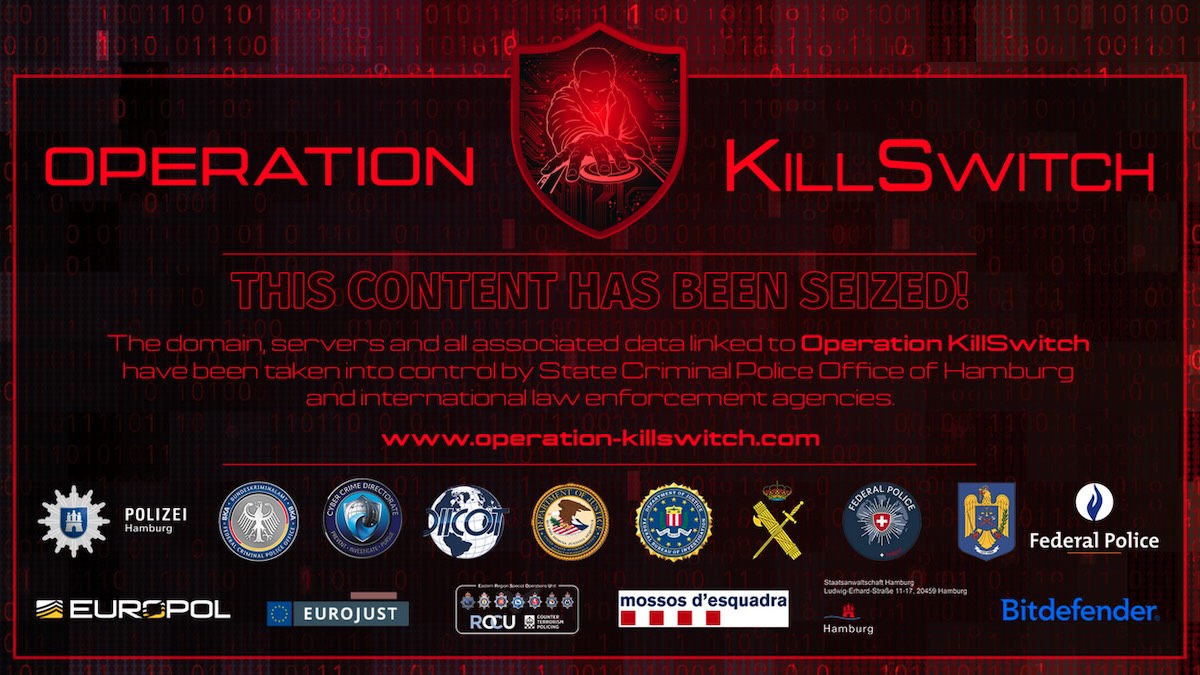
EUROPOL says a 16-year-old is believed to be the administrator and main operator of KillSec, a ransomware group linked to roughly 1,000 suspected attacks worldwide. The teenager was identified in Operation KillSwitch, an international investigation led by police and prosecutors in Germany, with provisional arrests in three cases and searches conducted at eight homes across Greece, Romania, Spain, and the United Kingdom.
Investigators also named a suspected developer who turned 18 in August, plus a suspected negotiator and an affiliate, with further members still being hunted.
On 1 October 2026, police took control of KillSec’s dark Web leak site and blocked further unauthorised access to at least 110 terabytes of data reportedly stolen from victims. Europol indicated the group used the site to threaten organisations with publication of stolen files unless a ransom was paid; victims who refused could see their data offered as free downloads.
Authorities also seized five core servers used to manage operations and store stolen data, with KillSec’s domains redirecting to a law enforcement seizure notice. Prior to the takedown, KillSec was active since around 2024, compromising organisations by exploiting software flaws and weak entry points—especially into cloud storage—and exfiltrating internal data to its own infrastructure, sometimes prompting substantial ransoms. Investigators are analysing seized devices and tracing criminal proceeds, hoping to identify additional victims and suspects.