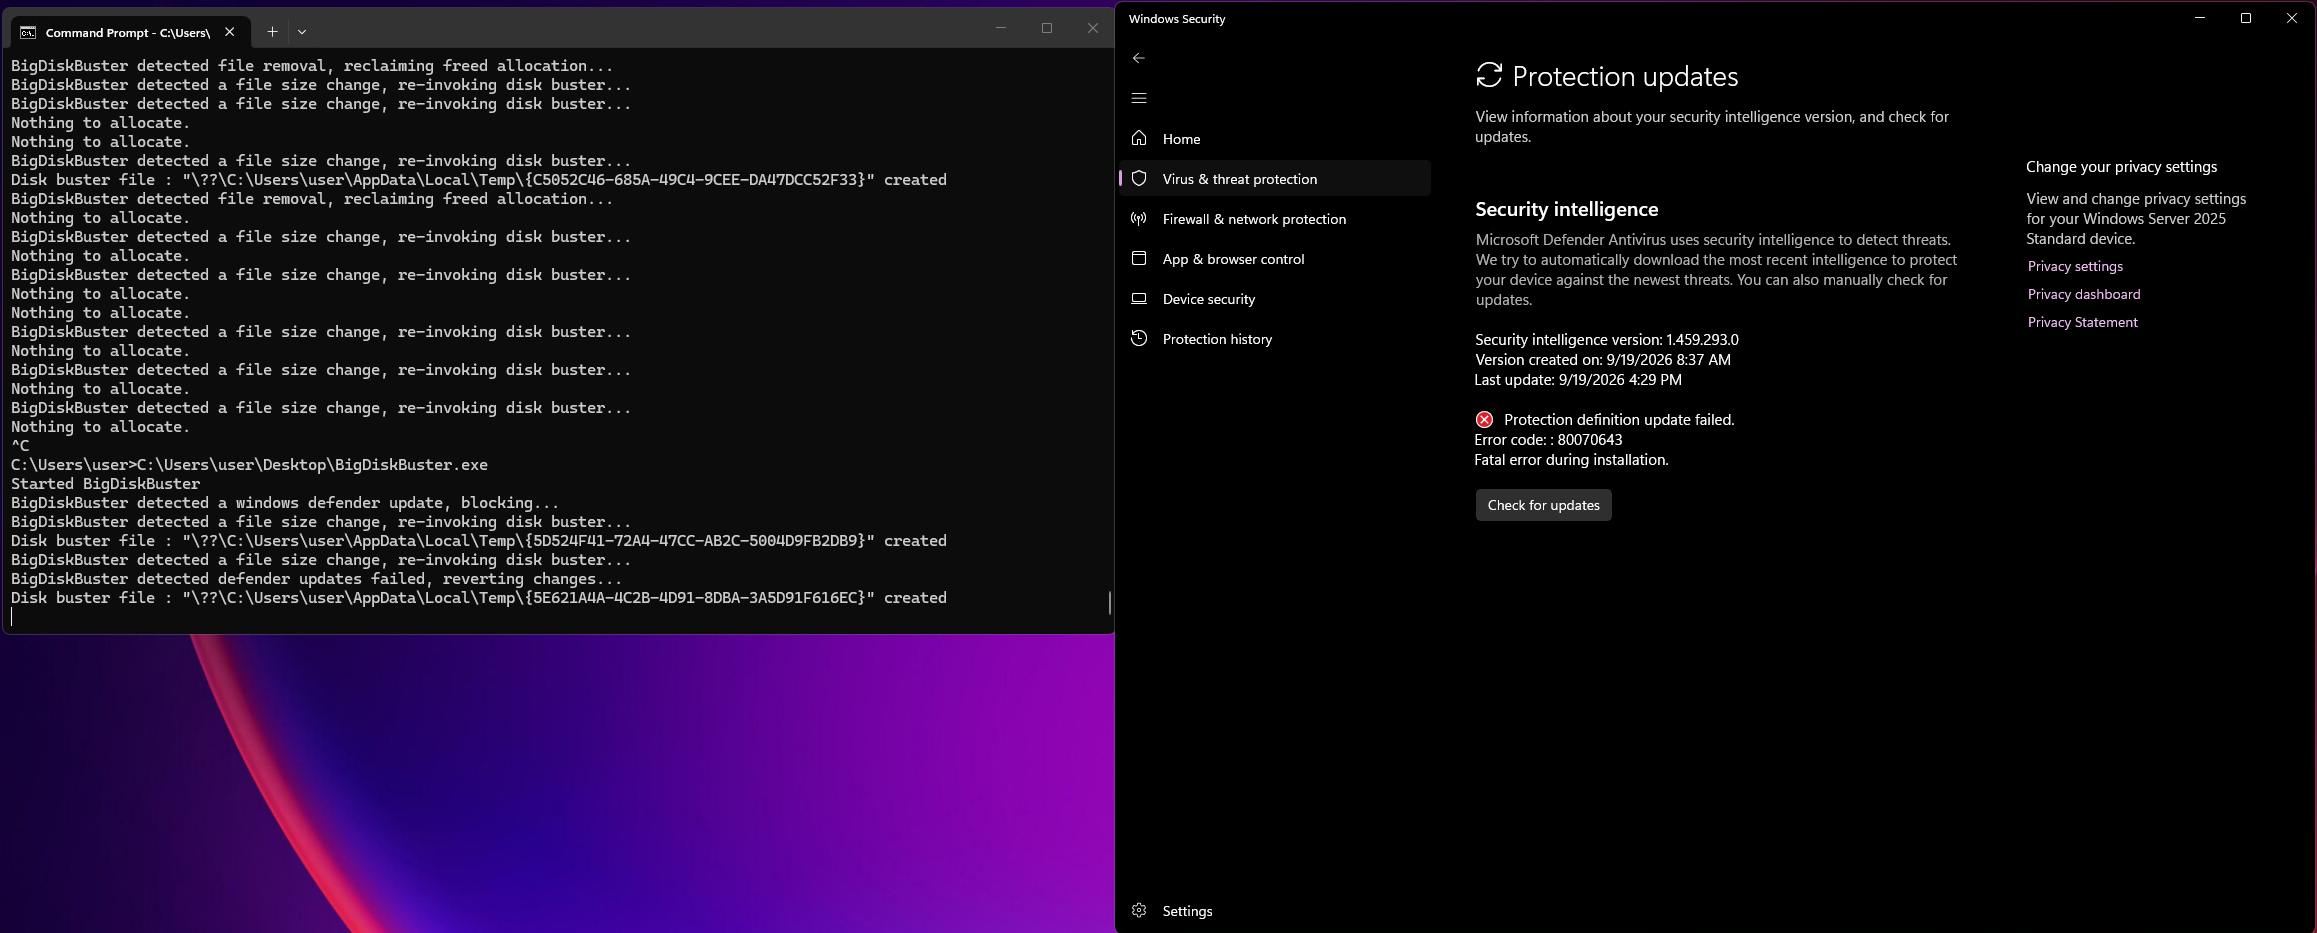
SECURITY researcher Chaotic Eclipse has released BigDiskBuster, a proof-of-concept exploit targeting a claimed zero-day denial-of-service vulnerability in Microsoft Defender’s update process. According to the researcher, the tool can prevent Defender from receiving platform and signature updates, potentially leaving its protections without the latest security intelligence.
Chaotic Eclipse says the technique works on all supported Windows versions, but also describes the publicly released PoC as buggy and in need of rewriting.
The report does not identify a CVE, provide technical details of the underlying flaw, or confirm exploitation in attacks. It also contains no indication that Microsoft has acknowledged the vulnerability or issued a fix. The practical information currently available is therefore limited to the researcher’s claims and the published PoC; users and organisations should treat BigDiskBuster’s reported impact as potential rather than confirmed.
The release follows other alleged zero-day PoCs from Chaotic Eclipse targeting security products, but those separate claims are not evidence that BigDiskBuster has been used in the wild.