BLACKPOINT’S Adversary Pursuit Group has identified ChainScript, a previously undocumented Node.js remote access trojan (RAT) distributed through ClickFix campaigns. Victims are persuaded to paste and run a command that launches `msiexec.exe`, downloading a malicious Windows Installer disguised as Spotify software.
The installer deploys a bundled Node.js runtime and JavaScript agent through hidden PowerShell and VBScript stages, placing components in folders with Microsoft-style names and running entirely within the user profile, without requiring administrator privileges. Samples were also disguised as Zoom Workplace and Microsoft Teams packages.
ChainScript’s main code resides in `app\src\index.js`. It gathers host information, maintains WebSocket connections, executes commands, transfers files, captures screenshots, downloads further payloads, runs arbitrary JavaScript, updates itself and can remove traces. It also checks for installed cryptocurrency wallets, although Blackpoint found no dedicated code to steal seed phrases or private keys.
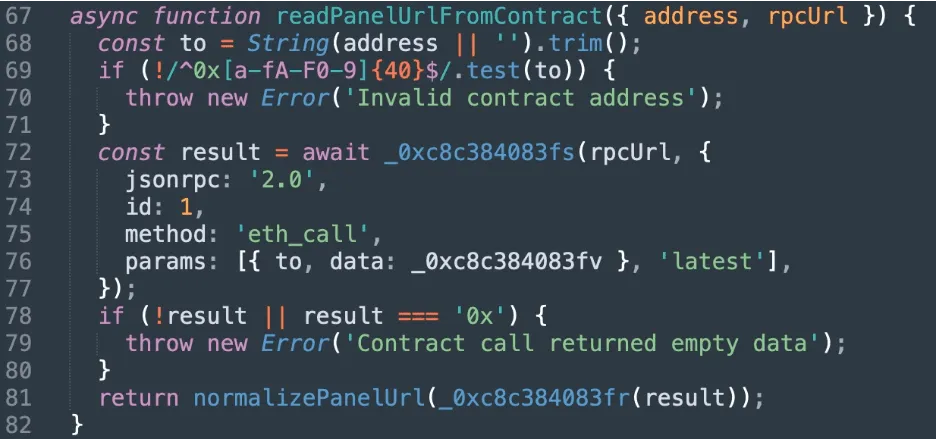
Rather than using a fixed command-and-control address, the RAT queries a Polygon smart contract using an EtherHiding-style technique. The analysed sample targeted contract `0xf9099d0d747368cce8C10226CC9AF2bFD4DDbCF4` on chain ID `137`, using selector `0x4ab787e4`; it accepts returned strings beginning `ws://` or `wss://`, caches them for five minutes and connects to the resulting server.
Blackpoint observed the contract redirecting the malware to a different server, allowing infrastructure rotation without changing the malware. The report recommends examining process chains such as `msiexec` to `wscript` and `node.exe` running `app\src\index.js`, as well as Node.js processes making blockchain RPC requests before opening WebSocket connections.