SECURITYONLINE [.]info reports that a critical vulnerability in the WordPress plugin WebRehab Super Forms – Drag & Drop Form Builder (vulnerable up to and including 6.3.313) is being exploited in the wild. The flaw, CVE-2026-14894, allows unauthenticated users to perform an arbitrary file upload via the data parameter, bypassing file type checks and capability checks.
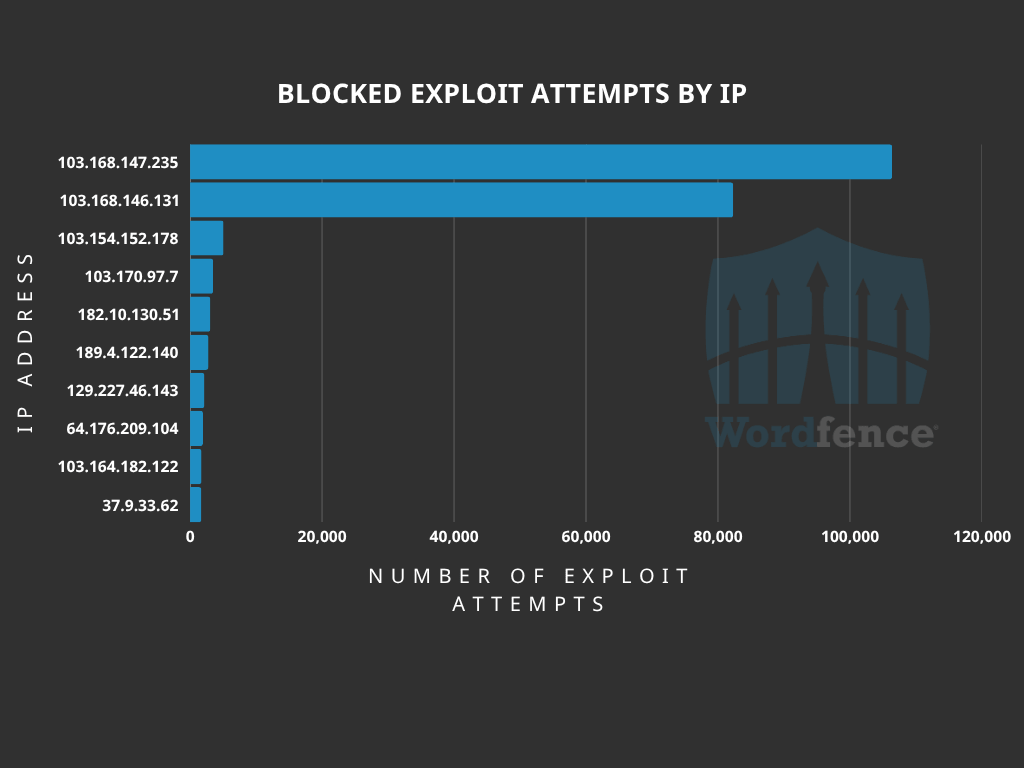
A publicly obtainable session nonce makes the protection ineffective, enabling attackers to upload a PHP payload and write a web shell to disk, leading to remote code execution and full site takeover. Wordfence estimates the CVSS score at 9.8 and notes that around 13,000 active installations are affected, with exploitation starting on or around 14 July 2026; a firewall rule shipped the same day, and more than 250,000 exploit attempts have since been blocked. The report also mentions a Mushr00w-labeled web shell previously associated with a government-site defacement, though attribution may be unreliable.
In response, the vendor released a patched build as version 6.3.314 on 8 July 2026. Administrators are urged to update immediately to 6.3.314 or later. To detect compromises, sites should scan for unexpected or recently modified PHP files dated on or after 8 July 2026 and look for a file named Mushr00w_upl.php; review access logs for admin-ajax[.]php requests using the super_submit_form action. If compromised, remove planted files, delete unknown admin accounts, and hunt for backdoors.
The article notes that exploitation is unauthenticated and requires no user interaction beyond the initial upload, meaning thousands of sites could be at risk until patched.