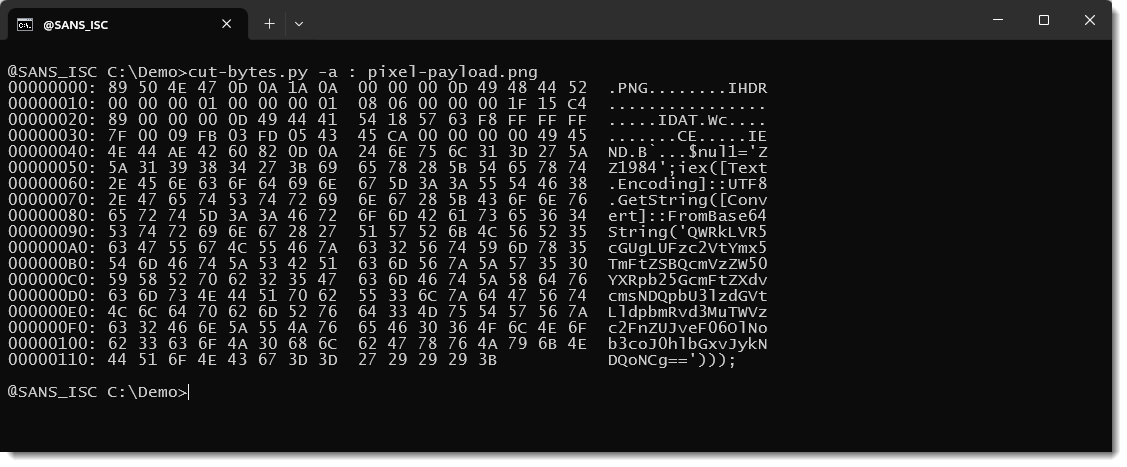
THE article discusses a new malware identified as DOUBLECUP, which employs a PNG file for its payload. Although initially intriguing for its use of steganography, the author, Didier Stevens, notes that the malware does not actually conceal its PowerShell script within the PNG image. Instead, the script is appended after the PNG file. Stevens highlights a clever method through which the script can be extracted using the FINDSTR command in Windows, which leverages a specific line break format in the script. The blog post was published and last updated on August 24, 2026.
Malware DOUBLECUP exploits PNG file to sneak PowerShell payload
CyberSIXT Evidence Panel
Source marked as original reporting
Article by CyberSIXT
Timeline Coverage
Swipe to explore timeline
-
BraZetsu Malware Framework Powers Initial Access Sales
securityonline.info
-
Malware DOUBLECUP exploits PNG file to sneak PowerShell payload
isc.sans.edu
-
DoubleCup RAT Leverages ClickFix and PNG Cache to Evade Defences
thehackernews.com