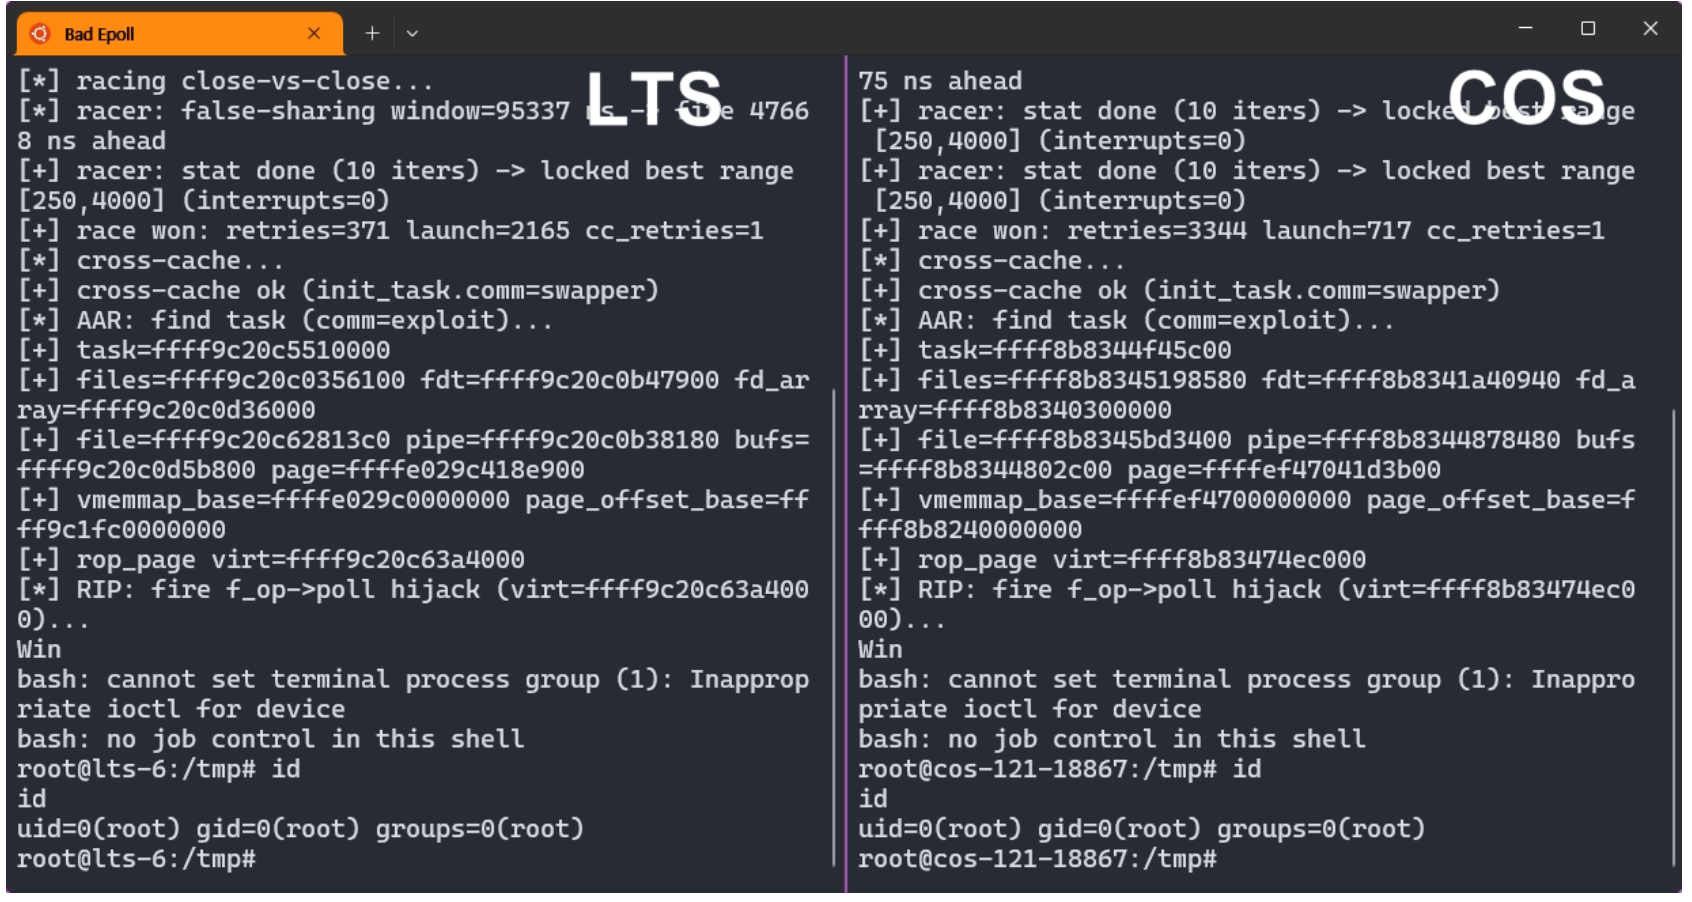
THE content discusses a critical vulnerability in the Linux kernel identified as CVE-2026-46242, which allows unprivileged users to escalate their privileges to root. The vulnerability, referred to as 'Bad Epoll', affects various Linux kernels (v6.4 and newer) and can even affect Android systems. There is no confirmed exploitation yet, but a publicly available proof-of-concept exploit code has been released, with a high success rate. The flaw arises from a race condition during file release operations in the epoll feature. A fix is essential as there is no workaround available.
Public Exploit and Details Released for Bad Epoll Root Flaw (CVE-2026-46242)
CyberSIXT Evidence Panel
Article by CyberSIXT