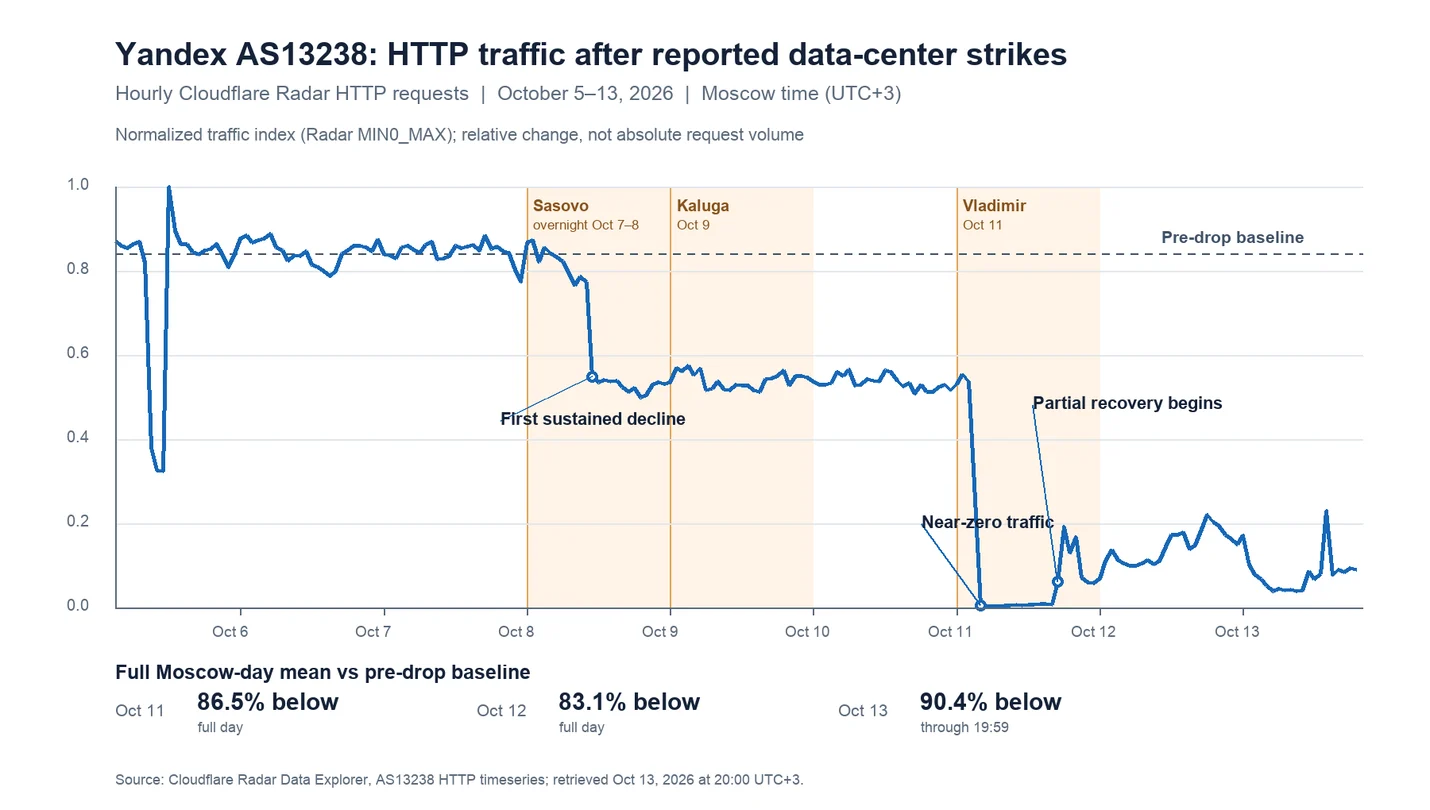
INDEPENDENT telemetry and Cloudflare’s analysis contest claims that Russian bot activity was crippled by strikes on data centre infrastructure. The article notes that Ukrainian President Volodymyr Zelenskyy asserted precision drone strikes degraded hostile automated tools, but observers say the opposite: threat actors rapidly shifted to alternative cloud environments to keep operations running.
Cloudflare’s assessment of the Yandex outage shows the immediate impact was concentrated on Yandex search indexing, with YandexBot traffic plummeting by 99% on 11 October compared with baseline levels. Telemetry indicated a three‑day recovery, with crawler activity returning to around 85% of previous levels. The observed traffic focuses on web crawling, image cataloguing, and news indexing rather than broader user engagement.
The report also highlights shifts in automated traffic: bot activity from AS200350 in Yandex Cloud fell by 40%, and probing for WordPress plugin vulnerabilities dropped by about 90%, while overall vulnerability scanning across diverse services declined by roughly 93%.
Crucially, the data do not show a permanent interruption. Forensic telemetry identified that traffic with matching TLS fingerprints, target paths, and User‑Agent headers reappeared quickly on alternative Russian hosting providers, signalling a fast reallocation of workloads and resumed automated activity with minimal long‑term disruption. The piece also emphasises the need to distinguish automated HTTP traffic from social media influence networks, noting that social media posting and engagement remained stable.