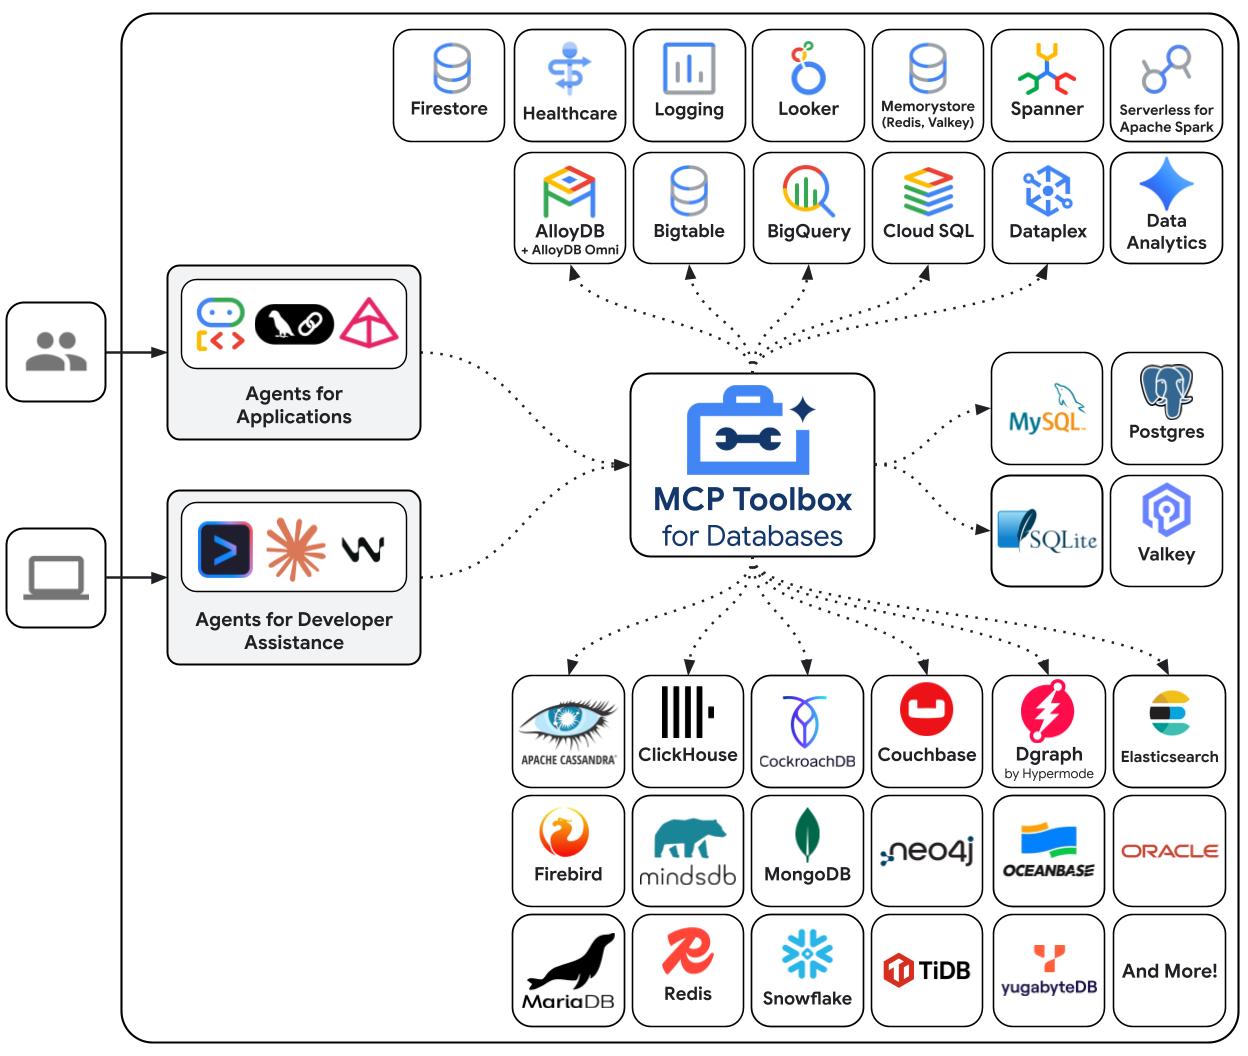
A critical vulnerability (CVE-2026-0257) has been identified in the MCP Toolbox, affecting its integration with enterprise database connectors. This flaw allows malicious websites to bypass security controls, exposing networks to session hijacking risks. The underlying issue stems from a hardcoded access control header that overrides CORS policies, enabling unauthorized access to local servers. The recommended fix involves removing the problematic header to restore secure origin permissions, thereby protecting sensitive infrastructure.
CVE-2026-0257 flaw in MCP Toolbox allows site based session hijack
CyberSIXT Evidence Panel
Article by CyberSIXT
Timeline Coverage
Swipe to explore timeline
-
Hackers Target Exposed Fortinet and Palo Alto Firewalls in Global Campaign
thehackernews.com
-
Hackers Steal 70,000 Credentials in Fortinet and Palo Alto Attacks
securityonline.info
-
Ransomware gangs exploit patched Palo Alto VPN security flaw
databreaches.net
-
Qilin and INC ransomware gangs exploit Palo Alto VPN flaw to bypass MFA
-
Ransomware gangs bypass MFA through PAN OS VPN flaw CVE-2026-0257
-
Attackers Exploit PAN-OS Flaw to Gain VPN Access and Move Laterally
-
Ransomware gangs exploit Palo Alto VPN flaw months after patch release
infosecurity-magazine.com
-
Hackers Exploited GlobalProtect Flaw to Fuel Brazilian Invoice Fraud
-
CVE-2026-0257 flaw in MCP Toolbox allows site based session hijack