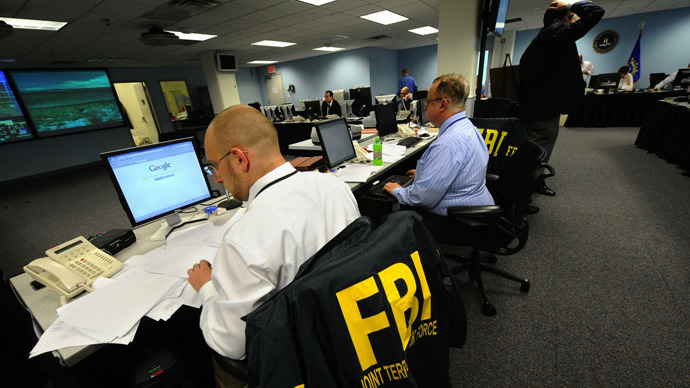
THE FBI removed an Accenture contractor from the bureau’s account after a data breach tied to a third‑party platform managed by Accenture. FBI cyber chief Brett Leatherman said the incident resulted from a security patch that the contractor failed to implement on a platform already patched, and the agency has taken steps to mitigate risk and protect its workforce.
The breach is described as arising from a known vulnerability in a third‑party system rather than a zero‑day, with Oracle PeopleSoft identified by Reuters as the platform involved in FBI[.]jobs‑related processes.
The attackers allegedly involved are linked to ShinyHunters, who claimed in September that they breached the FBI and stole sensitive information relating to employees and job applicants, including names, addresses, Social Security numbers, assignments, and even family details. Reuters partially verified some sample data against credit bureau records and dark‑web data.
The material reportedly exposed details such as counterintelligence roles, home addresses of intelligence personnel, and medical and psychiatric records. The FBI has not confirmed a systems compromise of its internal networks, and the agency is investigating, while continuing to assess the breach’s ramifications. The patching lapse occurred on a platform widely used for HR functions, underscoring operational security concerns beyond a single headline.