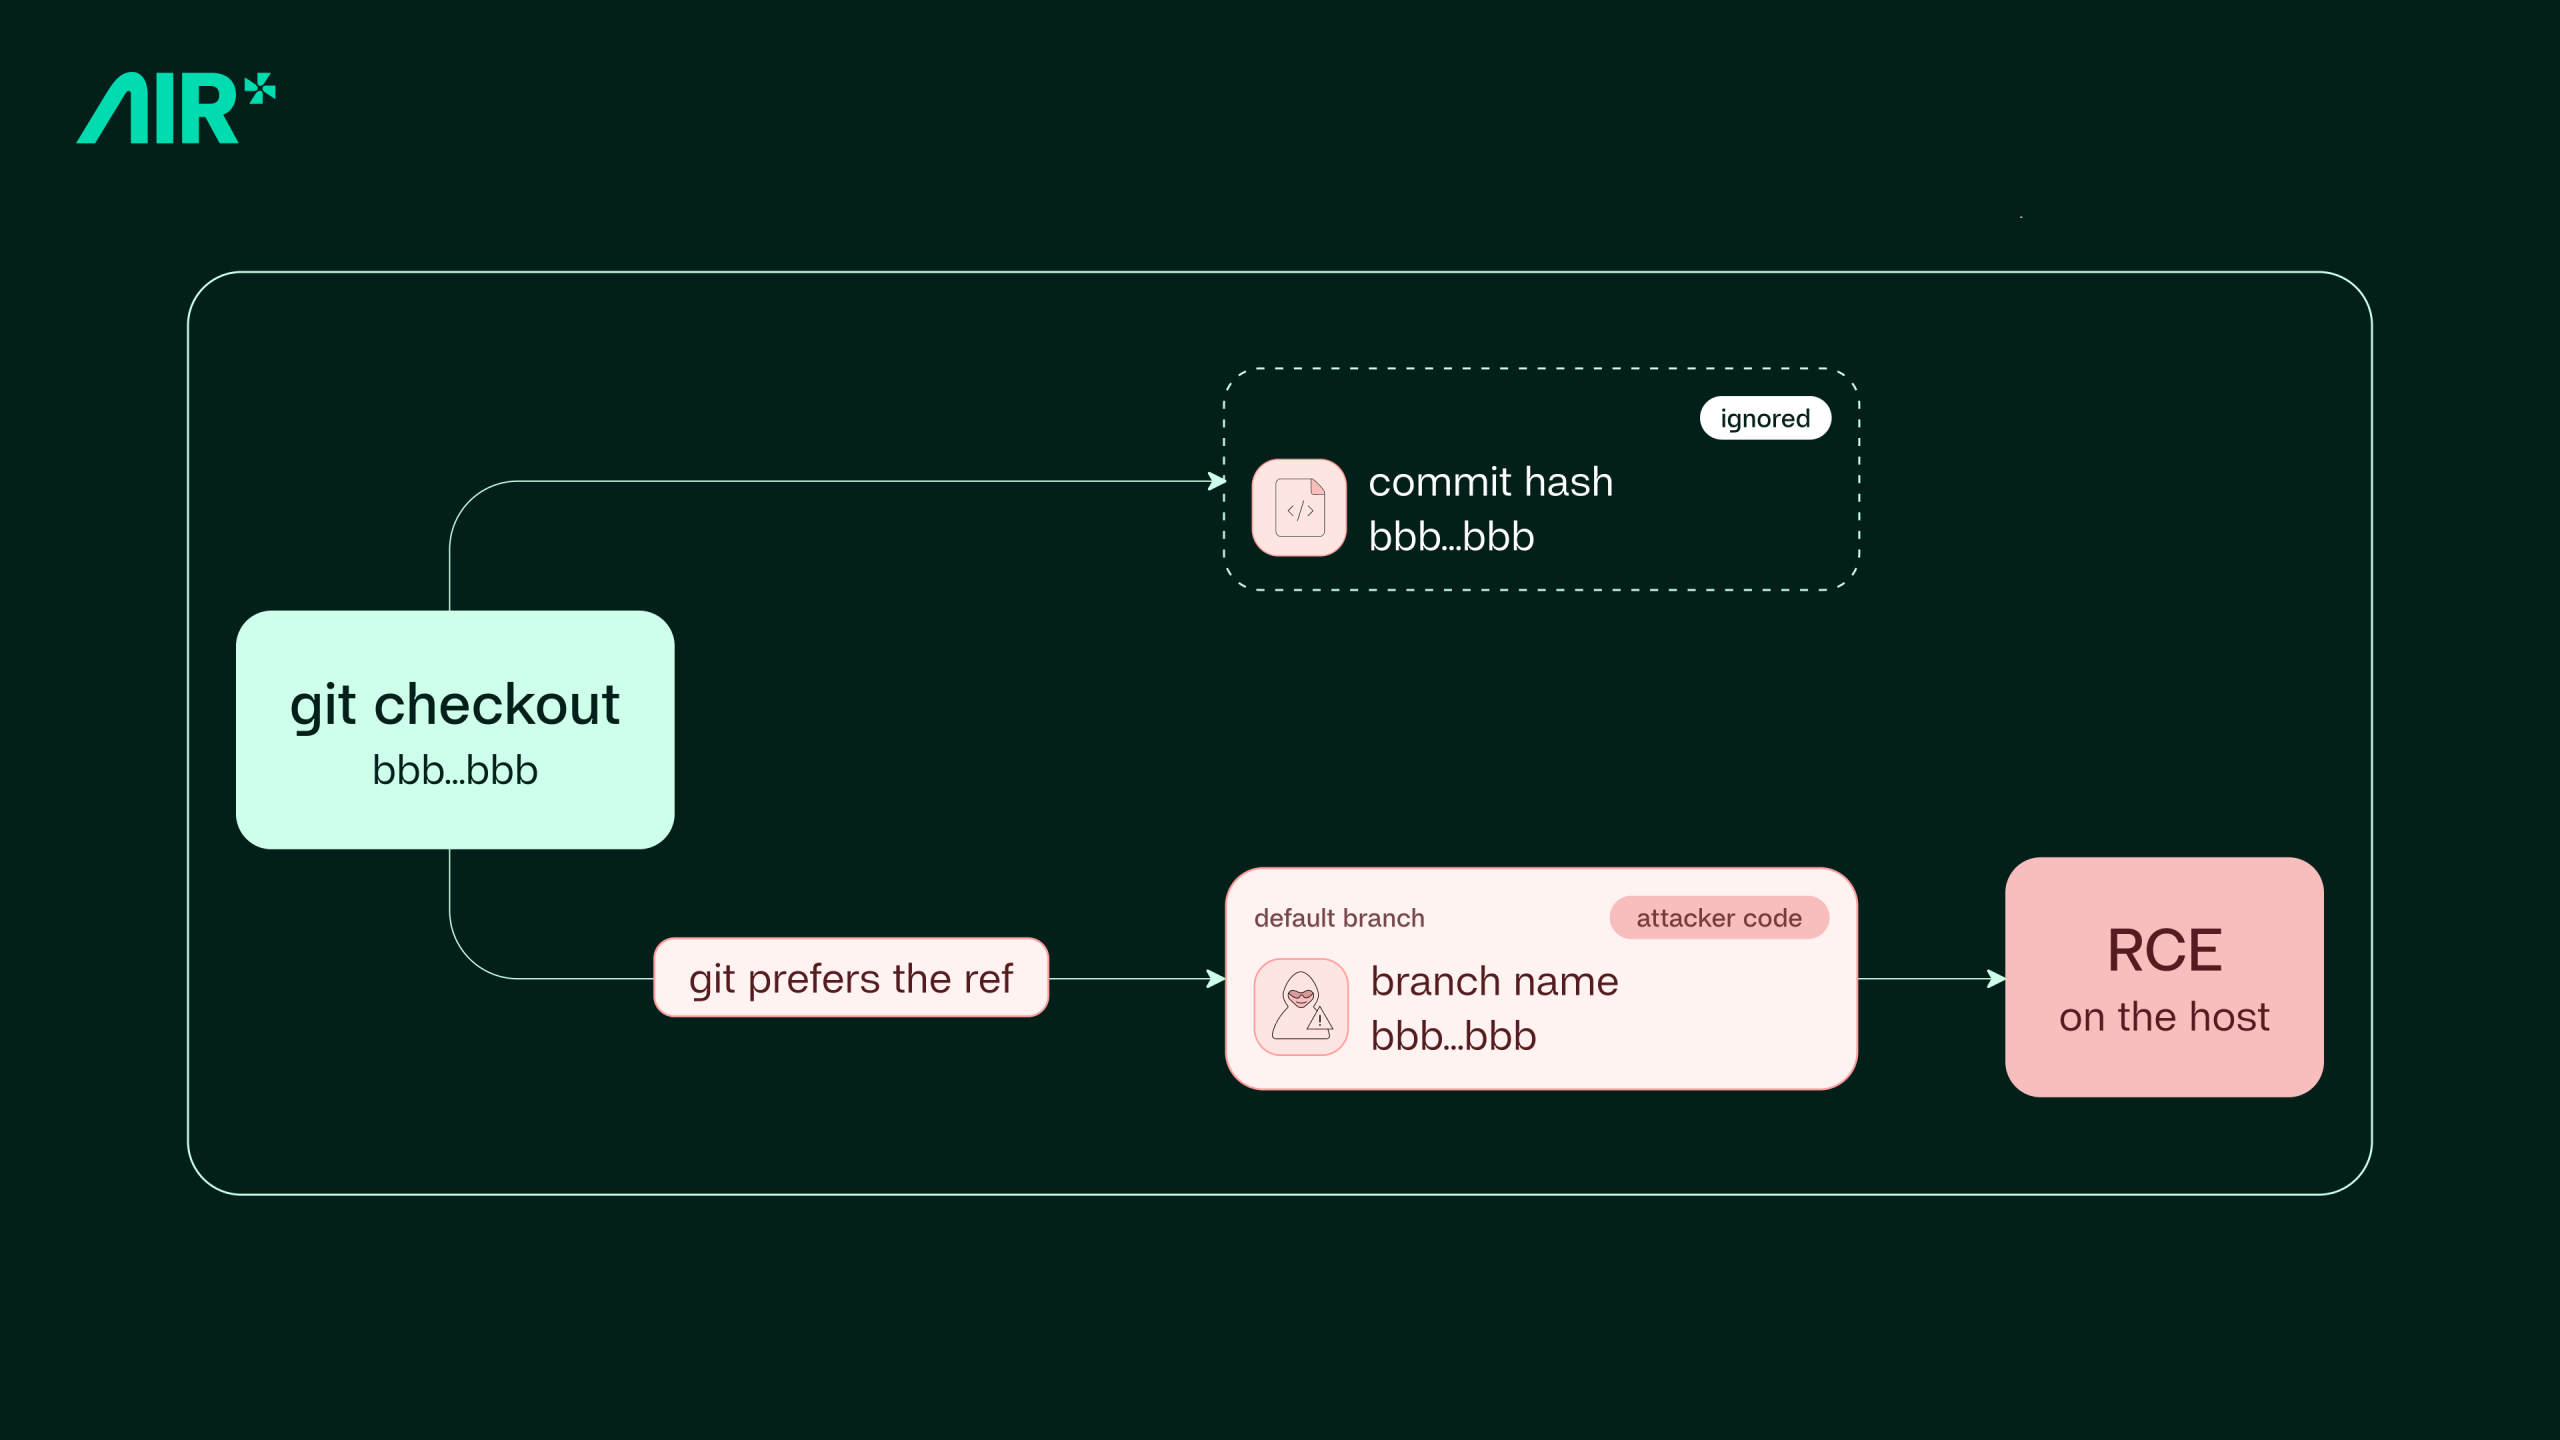
AIR Security has disclosed “Plugin4Shell”, a zero-click remote-code-execution flaw affecting four AI coding agents: Claude Code, OpenAI Codex, GitHub Copilot and Gemini CLI. The vulnerability bypasses SHA pinning, a safeguard intended to ensure that a plugin remains tied to a reviewed Git commit. AIR says a successful attack could give an attacker full control of the agent and its host, potentially exposing source code, API keys, CI/CD credentials and cloud environments. No CVE has been assigned, and exploitation in the wild has not been confirmed.
The attack abuses Git branch naming. For Claude Code, Codex and GitHub Copilot, an attacker controlling a plugin repository can create a branch named after the exact 40-character pinned hash and make it the default, causing the agent to run attacker-controlled code instead of the reviewed commit. Gemini CLI has a related issue involving a branch named `FETCH_HEAD`.
Background plugin updates make the attack zero-click for Claude Code and Codex: a trusted plugin already installed can become malicious without user interaction.
AIR reported proof-of-concept exploits to all four vendors in June 2026. Anthropic fixed Claude Code in version 2.1.179 and OpenAI fixed Codex in version 0.146.0. Microsoft has not released a Copilot fix. Google has deprecated Gemini CLI and will not patch it, advising users to migrate to Antigravity, which AIR says is not affected. Updating is therefore the complete mitigation where available; enterprises using Air Marketplace and Air Filter were not affected.