SECURITY researchers at Zimperium’s zLabs have identified Mantax Otax, an Android malware family that combines spyware with ransomware. The researchers observed about 210 infected devices, mainly in the Asia-Pacific region, and suspect Indonesian threat actors are behind the campaign. The malware is distributed as sideloaded APKs through third-party sharing sites and phishing or other targeted social-engineering messages, often posing as legitimate utilities or media applications.
After installation, Mantax Otax requests device administrator and accessibility privileges, alongside access to SMS messages, contacts, audio and images. It can record screen activity, capture screenshots and photographs, steal one-time passwords from SMS, and extract WhatsApp and Telegram chats through accessibility services. It also displays a fake lock screen designed to capture the victim’s PIN.
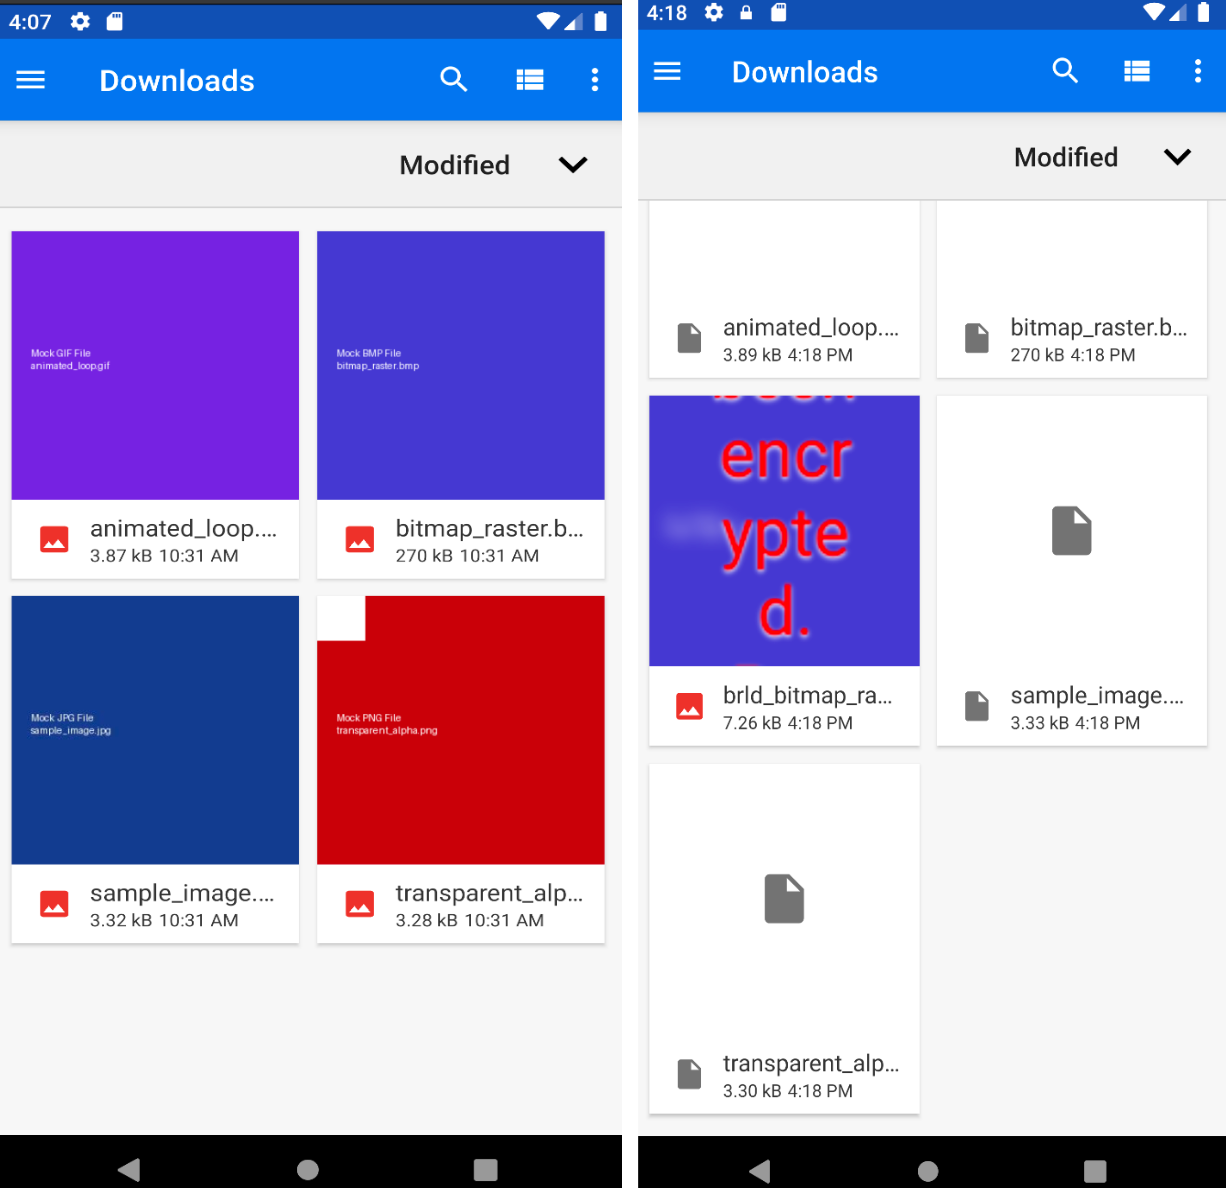
The malware obtains an AES encryption key from its command-and-control server and, on Android 9 and earlier, encrypts files on shared external storage, deletes the originals and adds a `.enc` extension. It avoids the `Android/data` and `Android/obb` directories. Android 10 and later’s Scoped Storage limits this encryption activity.
The malware uses HTTPS, Firebase-hosted extortion chat and Catbox for uploaded media, while Mantax v2 adds WebSockets and harassment features including repeated alerts, image flashes every 600 milliseconds and threatening text-to-speech audio. The report recommends blocking unapproved sideloading, refusing unverified accessibility or administrator requests, monitoring unusual Firebase and MediaProjection activity, and using Android 10 or later where possible. In a suspected infection, users should disconnect the device, change passwords from another device and enable multi-factor authentication.