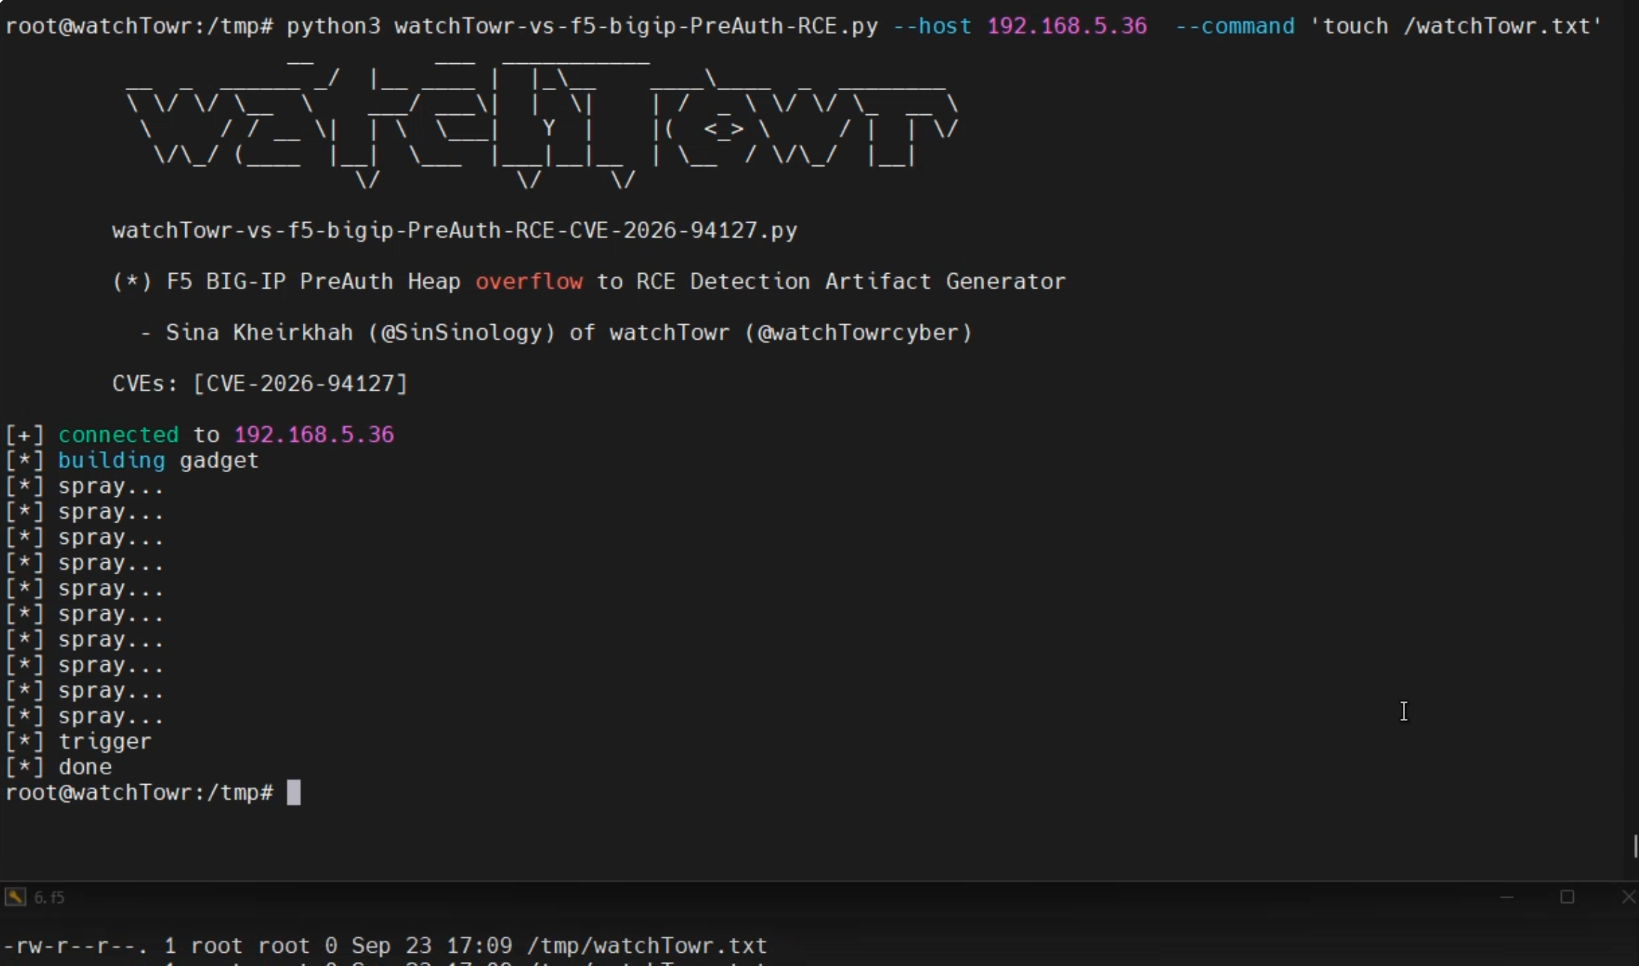
F 5 has patched a critical zero-day vulnerability in BIG-IP Access Policy Manager (APM), tracked as CVE-2026-94127, which the company says is being exploited in the wild. Rated 9.8 (Critical) under CVSSv3, the flaw affects BIG-IP 21.1.0, 17.5.0 and 17.1.0 deployments configured with OAuth Authorisation Server profiles on a virtual server. Researchers at watchTowr have published technical analysis and a working proof-of-concept exploit, increasing the risk to systems that have not been updated.
The vulnerability is a heap-based buffer overflow in BIG-IP’s handling of OAuth requests. An unauthenticated attacker can send an oversized Authorization header to the `/f5-oauth2/v1/userinfo` endpoint, potentially corrupting heap data and function pointers to achieve arbitrary command execution. The reported exploit uses return-oriented programming and modifies the `/etc/bigstart/scripts/tmm.finish` hook, which runs when the affected process crashes. Deployments acting only as OAuth Clients or Resource Servers are reported not to be affected.
F5’s fixes are Hotfix-BIGIP-21.1.0.2.0.30.22-ENG, Hotfix-BIGIP-17.5.1.9.0.160.12-ENG and Hotfix-BIGIP-17.1.3.5.0.41.14-ENG. For version 21.1.0, the article says administrators should apply hotfix build 0.30.22; F5 Support’s mitigating iRule is an alternative where immediate patching is not possible. Organisations should also review F5’s advisory and investigate repeated OAuth authentication failures followed by TMM SIGABRT crashes.