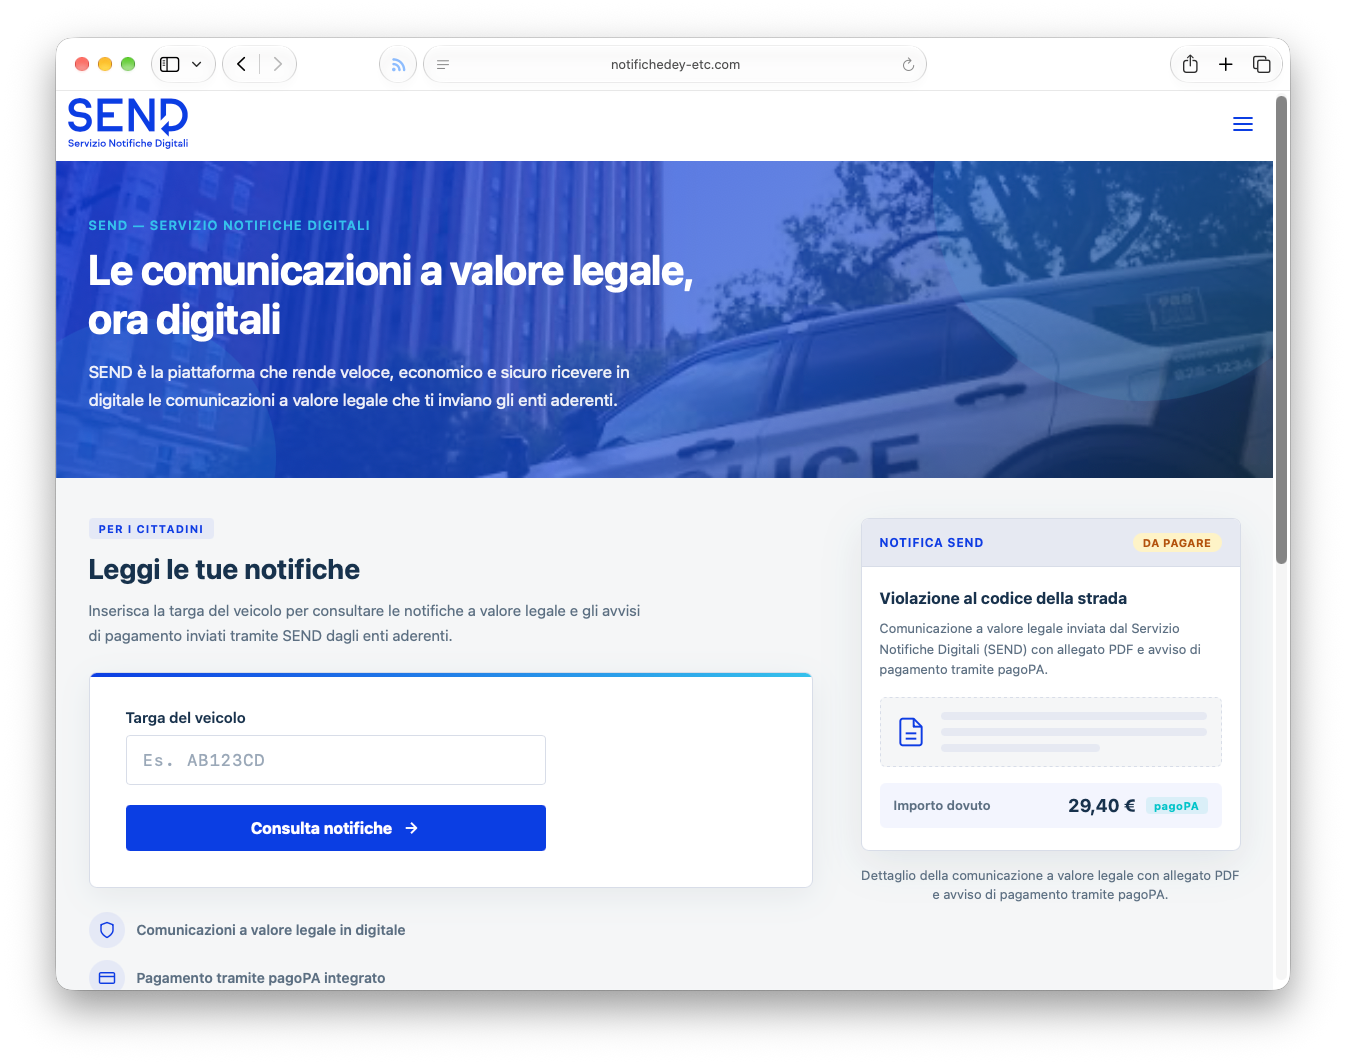
D 3Lab has reported an Italian phishing campaign that disguises malicious links as notifications from SEND, the country’s digital public-notice service. Messages claim that recipients have an outstanding legal or administrative document and direct them to a convincing copy of the pagoPA SEND portal. The fraudulent site presents a fake anti-bot check and uses Socket.IO to communicate with operators, who can change requests for payment-card details or verification codes based on victims’ replies.
The page also contains a hidden iframe connecting to an exploitation server. According to D3Lab, the browser itself is the entry point: no application installation or attachment opening is required. The server fingerprints the device and delivers a three-stage exploit chain against Safari’s WebKit engine, targeting iOS 13 through iOS 17.2.1. The stages attempt to obtain memory read/write access, bypass Pointer Authentication Code protections and escape the Safari sandbox.
If successful, a modified Coruna Pro V2 toolkit can collect SMS messages, call history, contacts, Safari bookmarks, location history and iOS Keychain data, then send it to command-and-control infrastructure.
The operators’ console, titled “Lü Technology Console API”, is written in Chinese and includes the Telegram handle “@ojishu”, but researchers could not attribute the campaign to a particular country or group. The reported response is to update iPhones beyond iOS 17.2.1, use the official portal at cittadini.notifichedigitali.it and consider Lockdown Mode for higher-risk users.