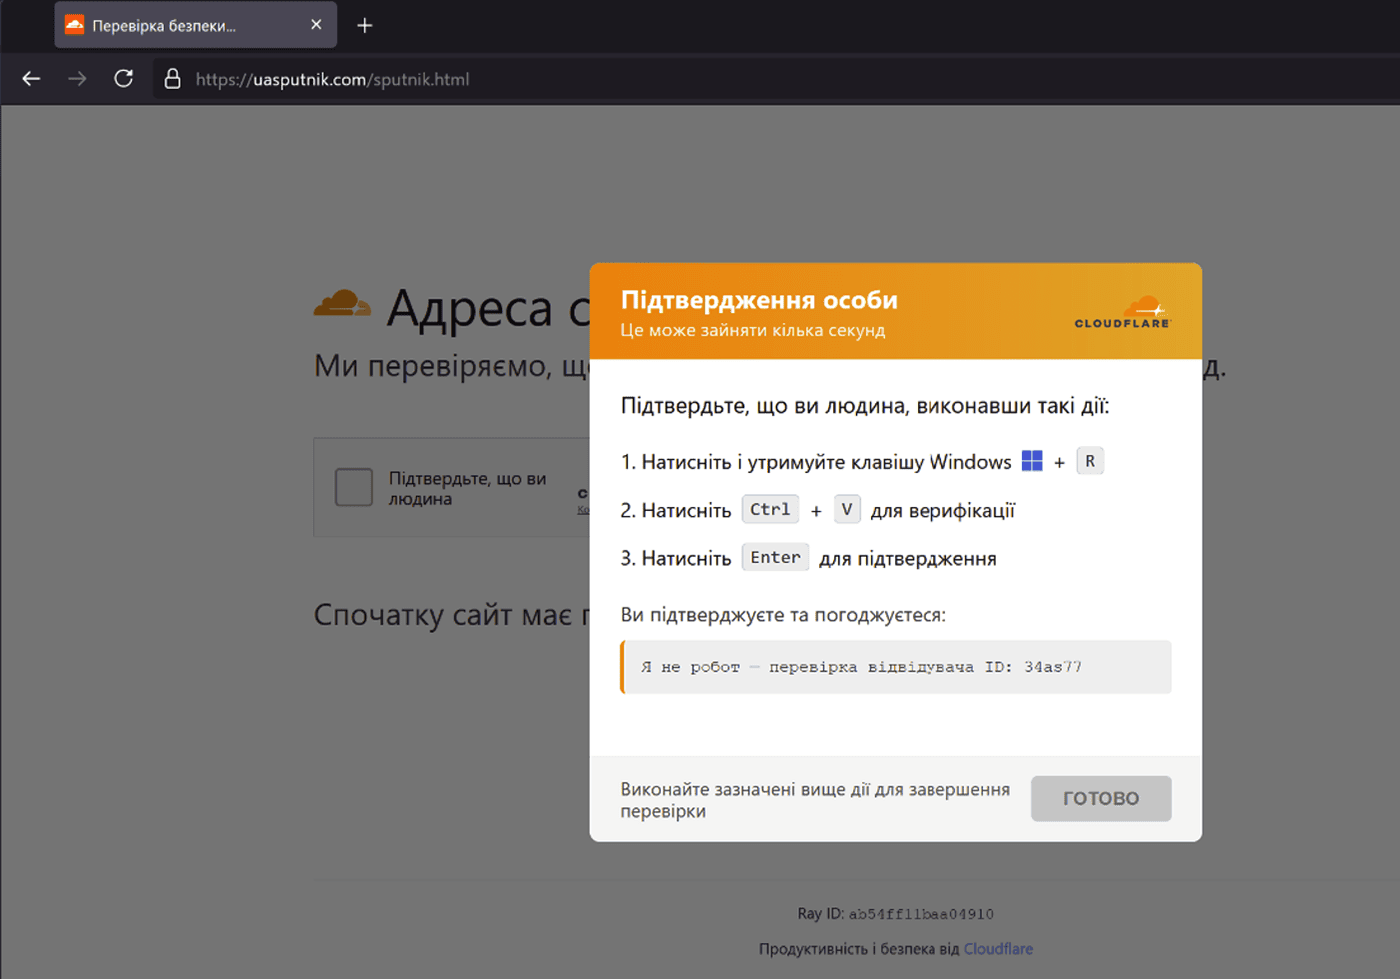
ATTACKERS compromised Ukrainian business websites to distribute Psychedelic Stealer through a ClickFix-style social-engineering campaign, according to Arctic Wolf Labs, whose report was cited by Security Affairs. The affected sites included businesses in sectors such as healthcare, retail, manufacturing and specialist bookselling. Visitors were shown a Ukrainian-language imitation of a Cloudflare CAPTCHA, including fabricated Ray ID and visitor-identifier values.
Clicking the CAPTCHA silently copied a Windows Installer command to the clipboard, after which victims were instructed to press Windows+R, paste it and run it. The command launches `msiexec.exe` rather than PowerShell, potentially avoiding controls focused on malicious PowerShell activity.
The downloaded MSI installs the 64-bit `psychedeliclove.exe`, tracked as Psychedelic Stealer. It targets saved passwords and account tokens from Chrome, Edge, Brave, Opera, Opera GX, Vivaldi and Yandex, as well as cryptocurrency wallets including Exodus, Atomic Wallet, Electrum, Bitcoin Core and Litecoin Core. The malware creates a scheduled task named `psychedelicloveUtils`, profiles the host, installs browser components and polls its command-and-control server for further instructions. Supported additional payloads include EXE, COM, BAT, CMD, MSI and PowerShell files, giving operators a route to extend the compromise.
The campaign used a control panel called “РУБЛЁВКА TDS” to change payload URLs and track visitor actions. At the time of collection it showed 557 views, 426 CAPTCHA clicks and 79 completed events across 32 countries, including 446 views and 351 clicks from Ukraine. Arctic Wolf cautioned that “complete” events do not confirm malware execution. Investigators can look for traffic to `uasputnik[.]com`, `admin777111777.php` and `193.178.159[.]128:8080`, alongside related file-creation and process-execution activity.