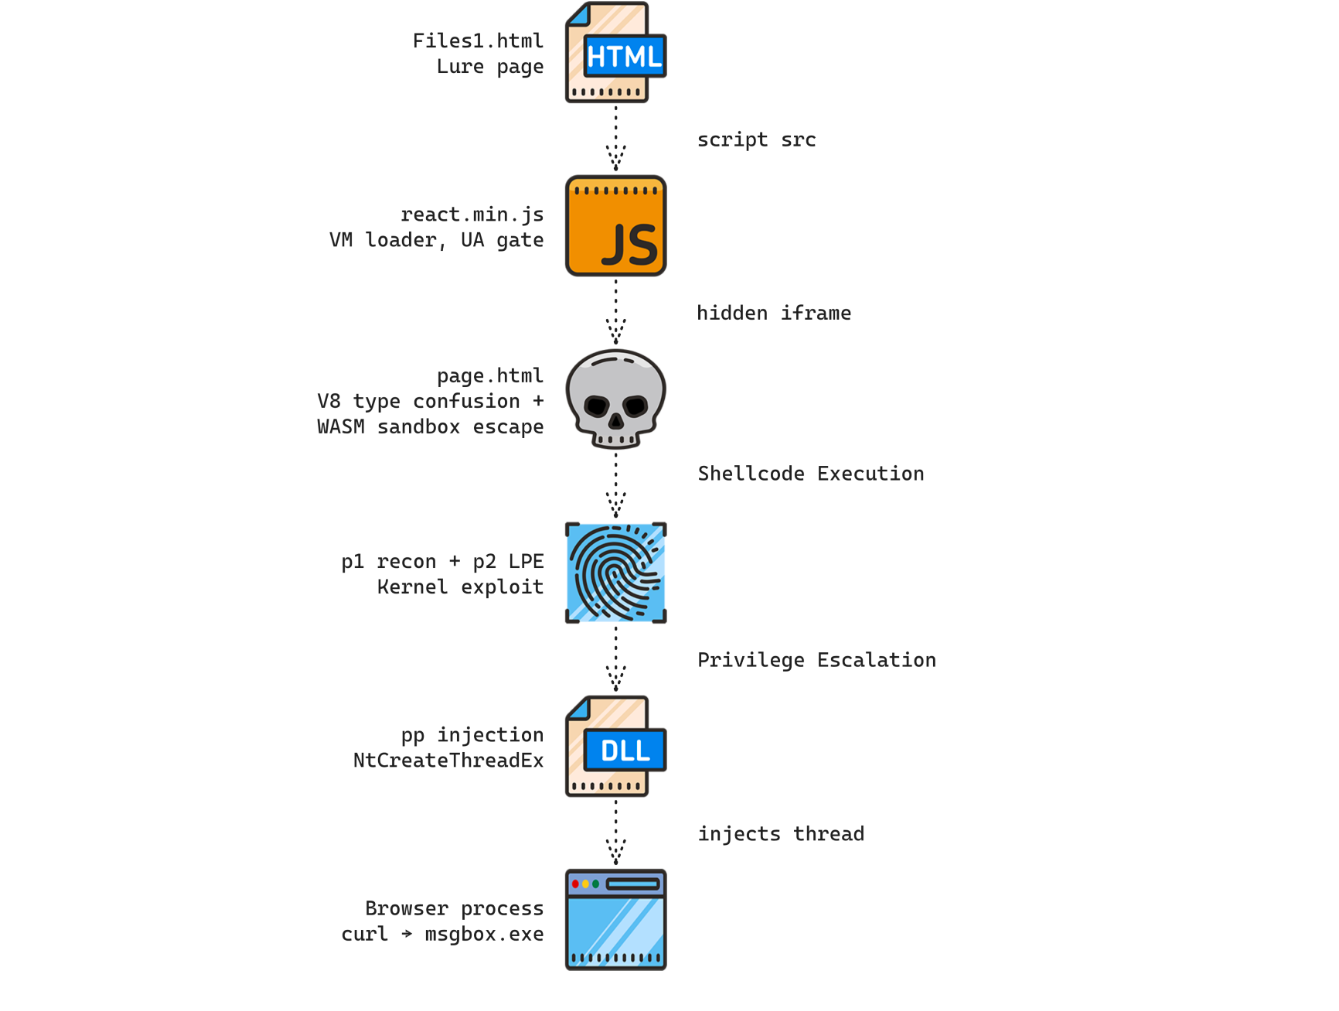
VOLEXITY says a suspected Chinese state-sponsored group, tracked as UTA0565, used targeted phishing and zero-day exploits against Asian government bodies, think tanks and policy researchers. The campaign began in early September 2026, with messages referring to Hong Kong activist Chow Hang-tung or impersonating the Center for American Progress. Links directed recipients to cloned websites hosted on attacker-controlled or typosquatted domains.
Volexity reported that the attacks were actively used on 3 and 4 September, before vendors issued patches, although the supplied report does not identify the affected Chrome or Windows versions.
Visiting a spoofed site triggered an invisible iframe that loaded an exploit configuration and chained Chrome vulnerabilities CVE-2026-85046 and CVE-2026-87491 with the Windows local privilege-escalation flaw CVE-2026-85880. The chain downloaded `chrome_cleanup.exe`, removed its Mark of the Web flag and executed it through Component Object Model interfaces. It then installed the CLEANGULP backdoor, which persists through a scheduled task named MicrosoftIME.
CLEANGULP can execute commands, list processes, transfer files and run beacon object files; it communicates over HTTP and encrypts traffic using AES-256-GCM.
Volexity assessed UTA0565’s Chinese state affiliation with moderate confidence, while Proofpoint found that multiple operators used the shared exploit kit. The report advises applying current Chrome and Windows updates, blocking typosquatted domains and checking for suspicious scheduled tasks and executables in user application or input-method-related directories.