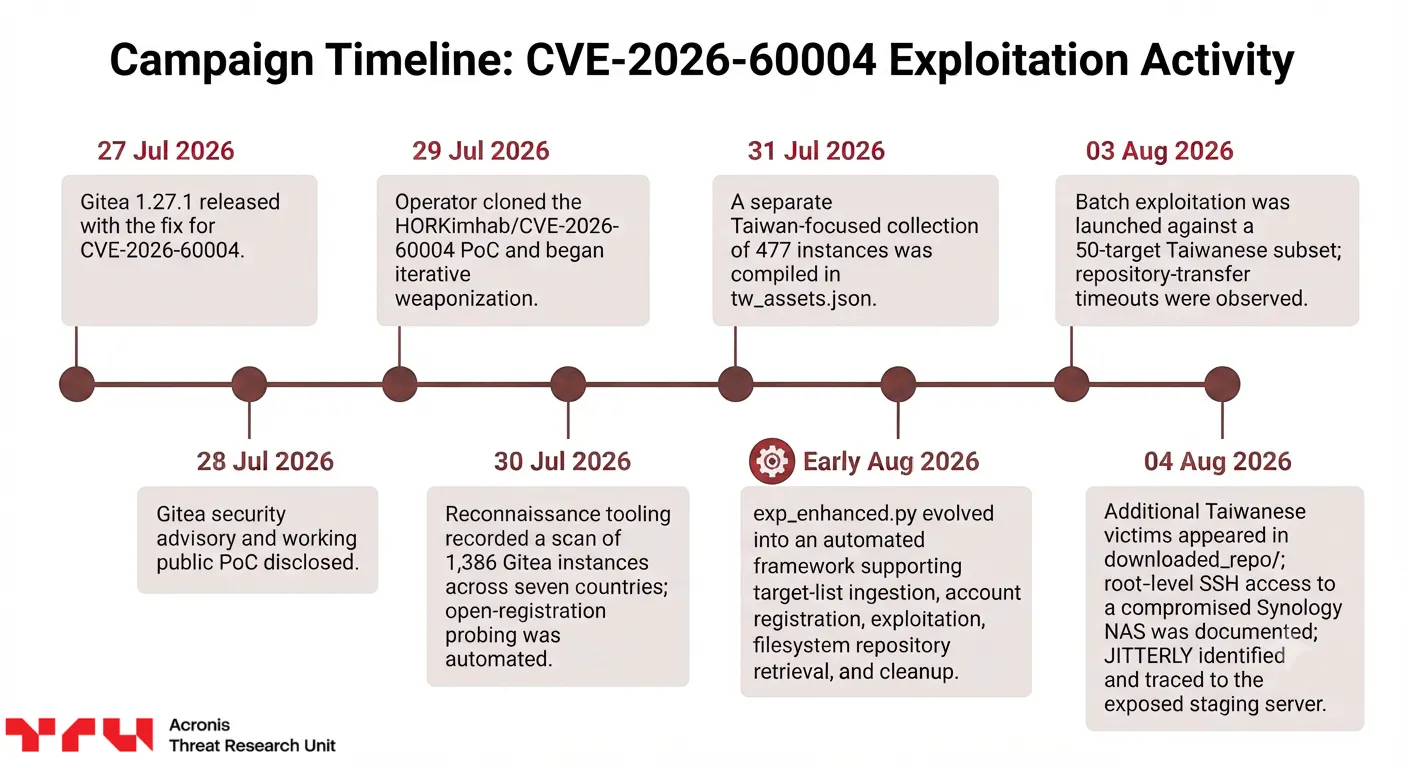
ACRONIS Threat Research Unit says a Chinese-speaking, state-linked actor tracked as Red Heron is exploiting a critical Gitea remote-code-execution flaw, CVE-2026-60004, in attacks against exposed self-hosted instances. The vulnerability affects Gitea versions 1.17.0 through 1.27.0 and has a CVSS v3 score of 9.8.
Acronis reportedly observed scanning of 1,386 servers across seven countries, with confirmed intrusions involving organisations in Canada, Argentina, Taiwan, the United States and Sri Lanka, including targets in defence, election infrastructure, aerospace and renewable energy.
The flaw is in Gitea’s diffpatch endpoint. By submitting the same crafted patch twice, an attacker can exploit Git’s merge handling to write a file into the active hook directory of a temporary bare repository. The hook then executes with the privileges of the Gitea service account. According to the report, attackers could register accounts on installations where public registration remained enabled, meaning authentication was not necessarily required beforehand.
The campaign allegedly involved repository theft, database and credential collection, and attempts to remove selected traces. In some environments, the attackers moved into virtualisation infrastructure and deployed the JITTERLY backdoor alongside the SIXZUT Linux rootkit, which hides processes, files and network connections.
Gitea fixed the issue in version 1.27.1 by changing temporary clones from bare to non-bare repositories. Administrators are urged to upgrade immediately, disable unnecessary public registration, examine repositories for recently created Git hooks, investigate suspicious processes and libraries, and rotate deploy keys, tokens and administrative credentials.