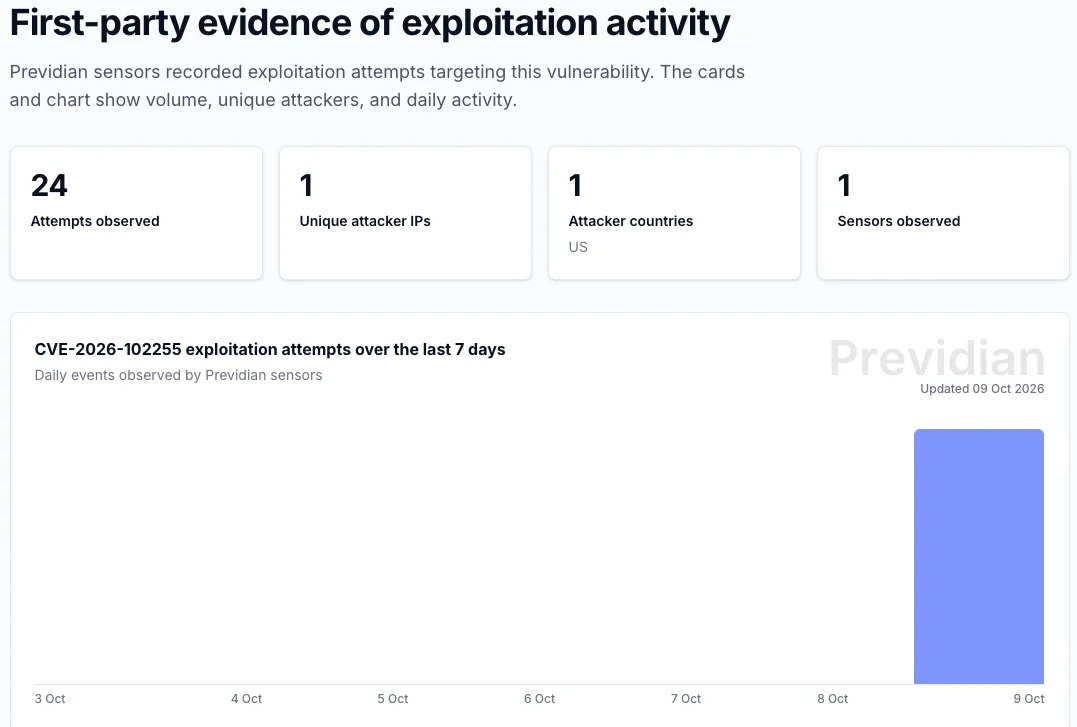
THREAT actors are actively exploiting a critical flaw in SonicWall SMA1000 appliances, with exploitation observed in the wild. The vulnerability, CVE-2026-102255, affects the SMA1000 line’s WorkPlace portal via an unintended access path in the Extraweb interface, allowing unauthenticated attackers to reach internal gateway functions and bypass normal perimeter authentication.
The attack chain involves an outside actor sending a crafted OPTIONS request that traverses a directory path into a design document rewrite function, ultimately forwarding unauthenticated traffic into an internal CouchDB database and enabling server-side request forgery. Official telemetry cited by Previdian indicates external traffic exploiting vulnerable systems, potentially giving intruders control over internal network resources. SonicWall itself assigned a maximum CVSS score of 10.0 for this flaw (CVSSv3).
Affected versions include physical SMA 6210 and 7210 models and virtual 8200v gateways, specifically platform branch 12.4.3 and earlier (12.4.3-03526 and older) and platform branch 12.5.0 and earlier (12.5.0-02952 and older). There is no documented workaround to stop exploitation, so patching is essential. SonicWall has released hotfixes and administrators should upgrade to 12.4.3-03670 or later on the 12.4.3 branch, and to 12.5.0-03082 or later on the 12.5.0 branch.
Note that appliances automatically reboot after hotfix installation. The advisory outlining these fixes underscores the need for immediate action to prevent unauthorised access.