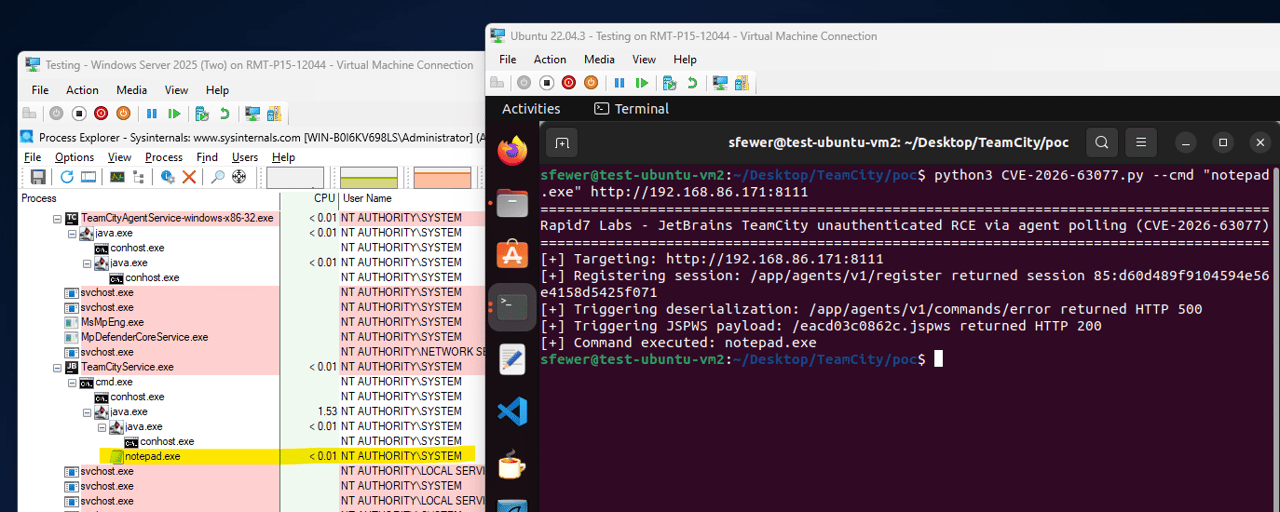
THE page discusses a critical vulnerability (CVE-2026-63077) in JetBrains TeamCity that allows unauthenticated remote code execution. Attackers are actively exploiting this flaw, confirmed by Australia's ACSC. The CVE has a CVSS score of 9.8, marking it as critical. Affected versions are those prior to 2026.1.3 and 2025.11.7. Rapid7 provides a detailed analysis and proof-of-concept. The vulnerability could compromise CI/CD pipelines, potentially exposing sensitive information and altering deployment processes. Users are advised to patch their systems immediately and review their security settings to mitigate risks.
CVE-2026-63077 lets attackers hijack JetBrains TeamCity servers
CyberSIXT Evidence Panel
Article by CyberSIXT
Timeline Coverage
Swipe to explore timeline
-
Hackers Exploit Citrix NetScaler Flaws as Forgotten Assets Fuel Attacks
thehackernews.com
-
JetBrains Urges Cadence Users to Rotate Credentials After Breach
-
JetBrains breach leaks AWS keys via unpatched TeamCity flaw
securityonline.info
-
CVE-2026-63077 lets attackers hijack JetBrains TeamCity servers