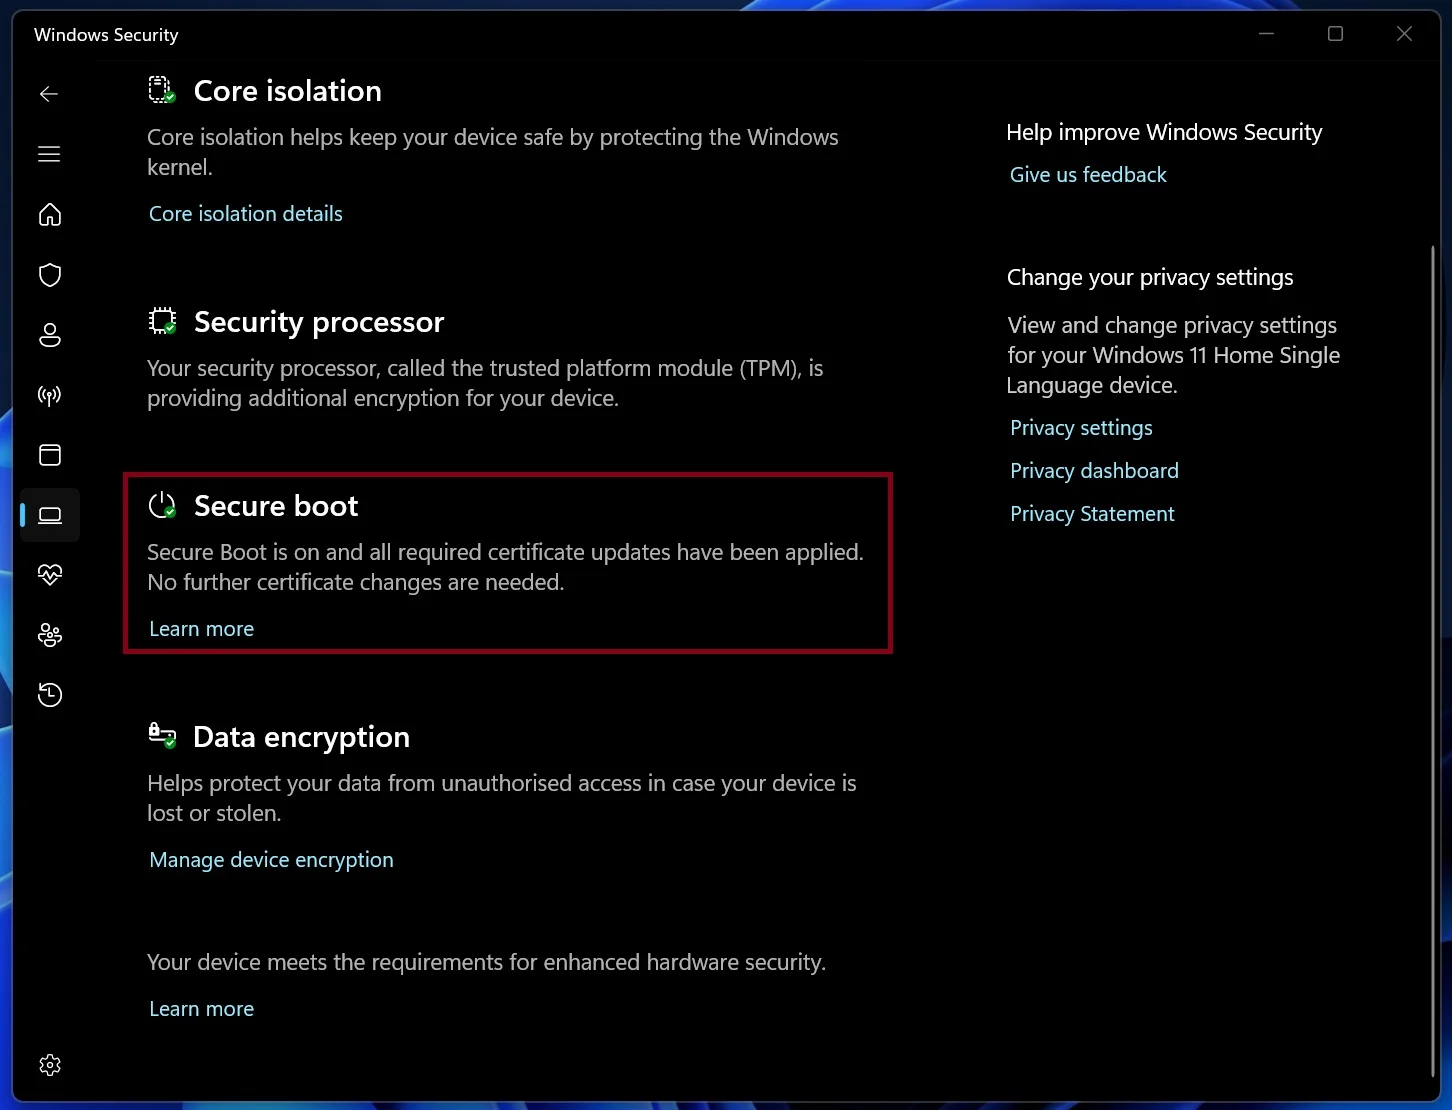
THE Windows Production PCA 2011 certificate has officially expired on 19 October 2026. This certificate long served to authenticate the integrity of the Windows Boot Manager during initial system startup. Microsoft states that devices still relying on the legacy certificate will boot normally and will receive routine cumulative security updates without disruption. However, systems that do not refresh their credentials may miss forthcoming bootloader mitigations as the transition to newer roots proceeds.
Secure Boot relies on cryptographic signatures across UEFI firmware, bootloaders, and kernel drivers to prevent untrusted software from running. The PCA 2011 root resided in the native UEFI signature database to validate Microsoft boot components, and its retirement marks the final phase of a 2026 certificate transition. Earlier, two companion 2011 certificates expired in June 2026, signing Secure Boot database updates, third‑party bootloaders, and external EFI utilities.
For those systems that have not updated, Microsoft guidance notes ongoing operational continuity, but they will not receive enhancements to the Secure Boot revocation database. In most cases, updates to the new Windows UEFI CA 2023 certificate are delivered via standard monthly patches, with some hardware configurations requiring firmware updates from the OEM.
Administrators are advised to verify Secure Boot status in Windows Security under Device Security and to back up BitLocker recovery keys before applying any BIOS/firmware updates, ensuring a safe transition to the updated certificate chain.