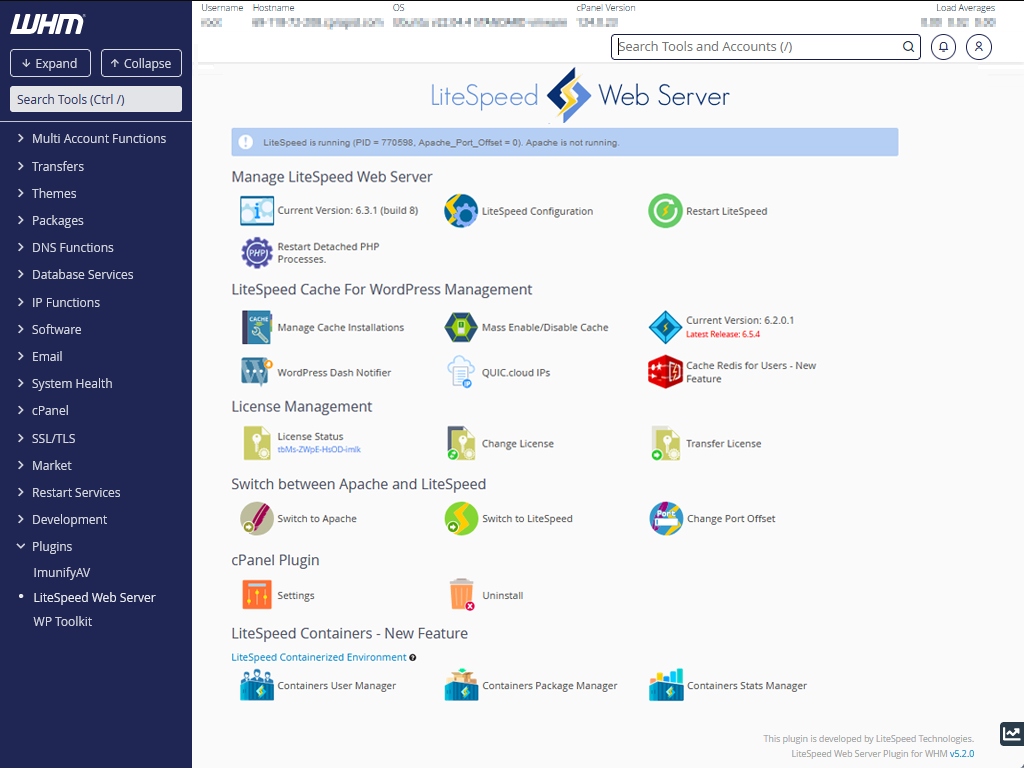
TWO critical vulnerabilities have been detected: CVE-2026-54420 affects the LiteSpeed cPanel Plugin, enabling privilege escalation for low-privileged users to gain root access, and CVE-2026-20262 pertains to Cisco Catalyst SD-WAN Manager allowing directory traversal. Administrators are urged to patch their systems urgently as these exploits are currently active. The LiteSpeed vulnerability, rated 8.5 on the CVSS scale, allows users on shared servers to escape their boundaries and threatens multiple accounts. LiteSpeed has addressed the issue in version 2.4.8; upgrading is advised to mitigate risks.
LiteSpeed flaw lets users gain root, Cisco SD WAN also exposed
CyberSIXT Evidence Panel
Article by CyberSIXT