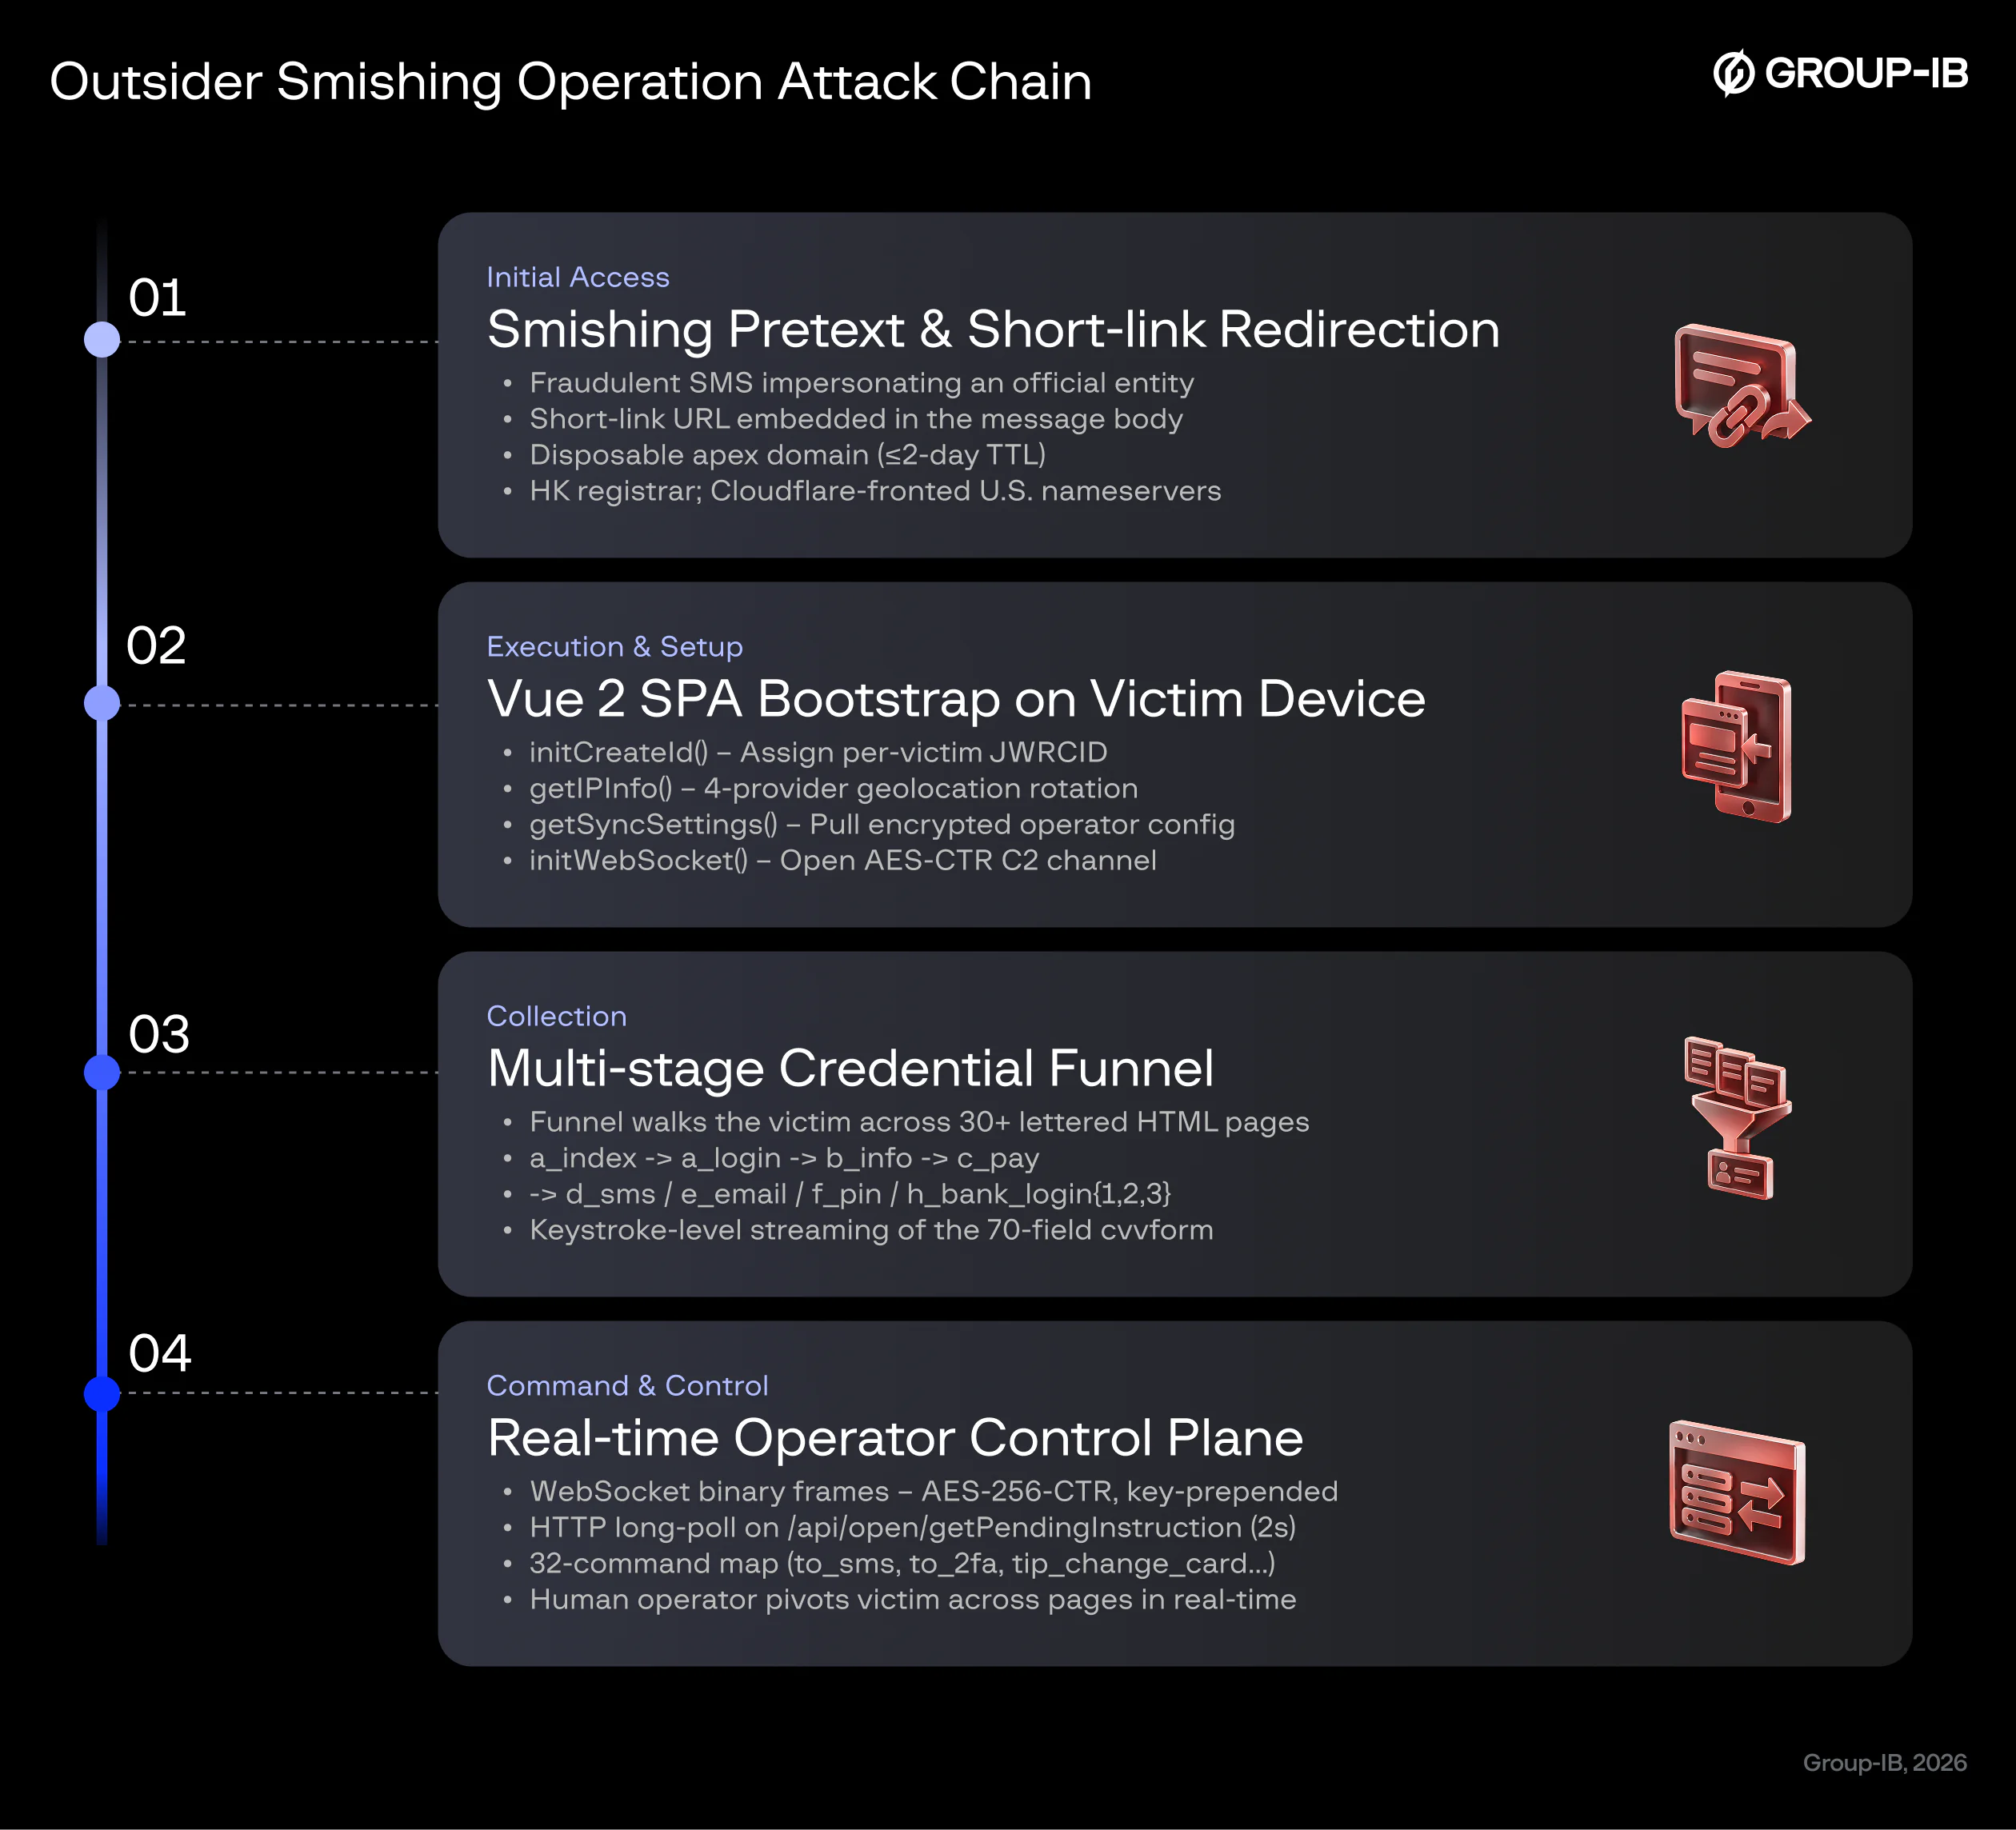
GROUP-IB has reported on a modular phishing-as-a-service platform known as JWR, which it attributes with moderate confidence to Outsider, a suspected affiliate of the wider Smishing Triad cybercrime marketplace. The operation sends SMS messages impersonating authorities or delivery companies, directing recipients through shortened links to temporary phishing sites.
Group-IB says the campaigns target mobile banking and postal customers in more than 121 countries, while industry reporting has linked the wider syndicate to over 194,000 malicious domains registered since 2024.
JWR uses a browser-based application and background worker to maintain real-time connections with operators through WebSockets and HTTP polling. It captures keystrokes as victims enter information and can collect identities, driving-licence and passport images, payment-card details and one-time passcodes. Operators can manually move victims through up to 32 stages, including simulated bank and PayPal pages.
The kit validates information for 12 jurisdictions and can support integrations targeting WordPress and Shopify checkout pages. Although stolen data is encrypted with AES, Group-IB found that the key is sent in clear text before each ciphertext, potentially allowing intercepted traffic to be decrypted.
The article says defenders can identify the kit through distinctive network request paths and static token suffixes. Telecoms providers are advised to filter deceptive SMS links, while financial institutions should monitor unusual account access and transactions. Consumers should avoid entering information after following unsolicited text-message links and instead visit official services directly through trusted bookmarks.