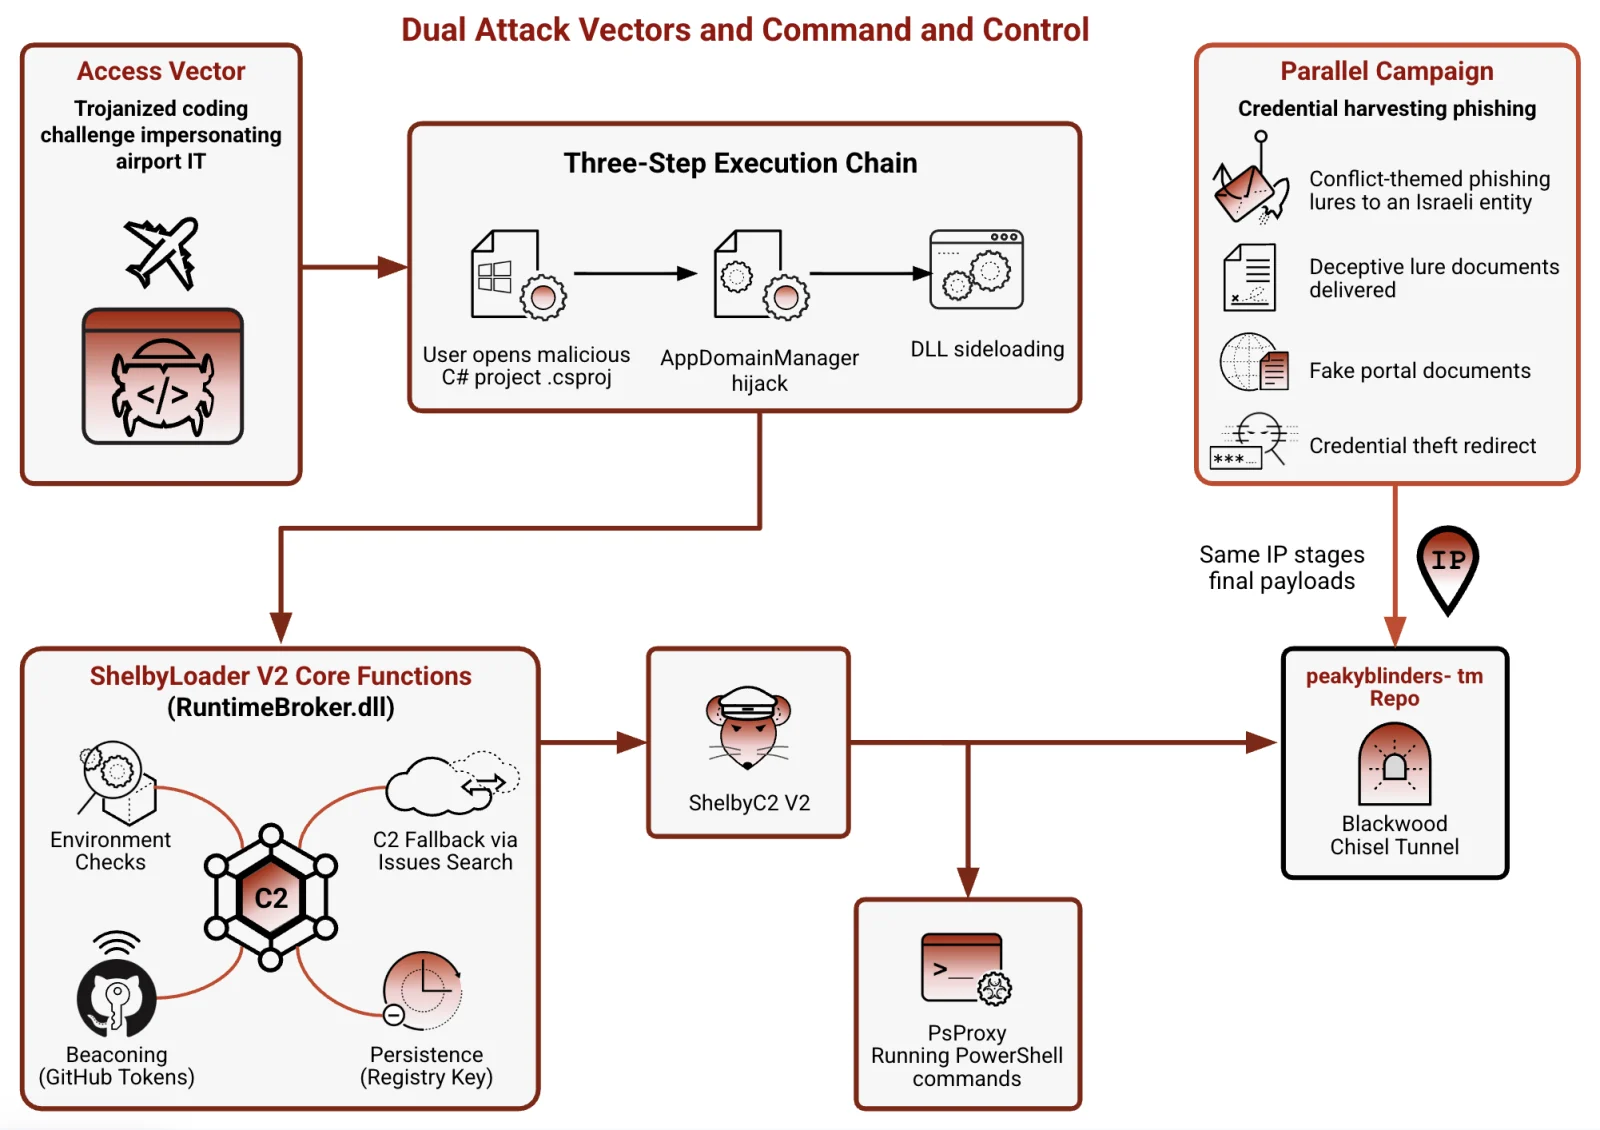
IRAN-LINKED threat actors, tracked by Unit 42 as CL-STA-1178, conducted a tightly targeted operation aimed at an Iraqi engineer involved in critical infrastructure. The campaign began with a fake Dubai Airports careers portal in March 2026, followed by a “coding assessment” in April that contained a tainted C# project. The readme file on the project addressed the target by full name, but Unit 42 notes there was no breach of Dubai Airports itself.
The malicious chain was triggered when the target opened the project in Visual Studio; a hijacked build step caused malware to run as soon as the project loaded, long before any compilation. The attack then used a renamed Microsoft binary to load a tampered config file via AppDomainManager hijacking, disabling Event Tracing for Windows, and finally loading ShelbyLoader V2 through DLL sideloading.
ShelbyLoader V2 establishes contact with a GitHub-based command-and-control node, periodically reporting a machine fingerprint and pulling instructions every 63 seconds. If GitHub channels fail, the loader searches for encrypted notes in issues that point to alternate repositories. The actor group subsequently decrypted ShelbyC2 V2 and executed PowerShell commands via a module that does not launch PowerShell[.]exe.
A later addition, Blackwood, injects the Chisel tunneling utility into memory to create a reverse proxy into the compromised network. The group’s activity appears Iranian-aligned, with evidence including Persian-language domains and an Iranian ISP server, and is believed to have a narrow footprint focused on Iraq, Israel, and the UAE. Unit 42 warns that the operation emphasised stealth and relied on authentic-looking recruitment and coding tests to elicit execution of the loader. Respondents are advised to secure developer environments, monitor cloud traffic, and treat unsolicited coding tests as untrustworthy.