SECURITY researchers have published a full technical analysis and proof-of-concept (PoC) exploit for a critical Drupal remote‑code‑execution flaw in the Field UI module, tracked as CVE-2026-108097. Drupal addressed the vulnerability in advisory SA-CORE-2026-014 on 14 October 2026. As of the report, patches are available: update to Drupal 11.4.10, 11.3.19 or 10.6.19. If updating is not possible, the Field UI module can be uninstalled as a mitigation.
The flaw’s impact is described as severe, with Drupal rating it Critical (19/25) and warning that “multiple serious exploit paths exist with contributed modules”; at least one known exploit path does not require authentication.
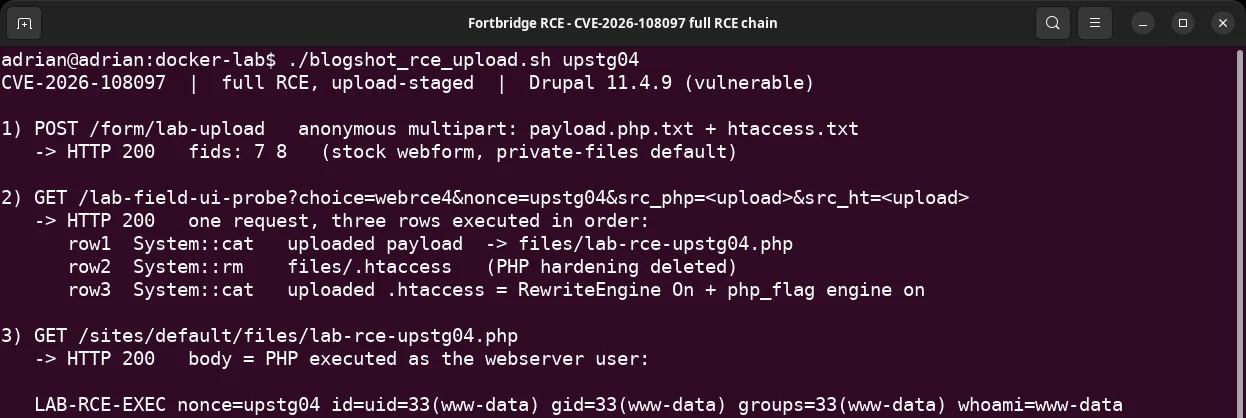
Exploitation details, according to FORTBRIDGE, show that a single line in Field UI can execute whatever PHP callable a table row names, effectively treating one field of data as code. However, outside access to that line requires a module to pass request data into the affected Field UI rows. In the researchers’ lab, they used a bridge module to fill this gap and demonstrated a complete chain from file disclosure to full command execution without logging in.
A publicly available PoC chain exists but relies on a synthetic module; no confirmed in‑the‑wild exploitation has been reported, and CISA KEV does not list the flaw. The advisory lists affected Drupal versions as 8.9.0 through 10.6.18, 11.0.0 through 11.3.18, 11.4.0 through 11.4.9, and 12.0.0 pre-releases before beta2. The recommended mitigation steps remain patching, auditing custom modules that feed request data into Field UI, and monitoring changes to the files directory and its .htaccess.