LUMEN’S Black Lotus Labs has detailed BambooToken, a previously undocumented malware family that has operated against Windows and Linux systems since at least February 2023 and possibly through July 2026. The researchers found it during a VirusTotal search and cannot link it to a known threat actor. BambooToken’s distinguishing feature is its use of MQTT, a publish-and-subscribe messaging protocol widely used by smart devices and industrial systems.
Infected machines communicate through an MQTT broker rather than connecting directly to the command-and-control server, which can obscure the operator’s infrastructure and supports asynchronous communication.
The earliest samples used HTTP, but variants from 2024 and 2025 adopted MQTT and Windows DLL sideloading. The malware was delivered alongside legitimate signed binaries associated with Tendyron’s OnKey hardware-token software and, in another case, Kingsoft Office. Lumen said neither company’s signing certificate or build environment appeared to have been compromised; instead, the attackers likely abused files vulnerable to sideloading.
A Linux version found in December 2025 can open a shell, transfer and delete files, and return system information. A Windows plugin checks installed antivirus software every five seconds. Researchers also found inactive code for keylogging, clipboard theft, audio recording and screen or webcam capture, although it is unclear whether those functions were completed.
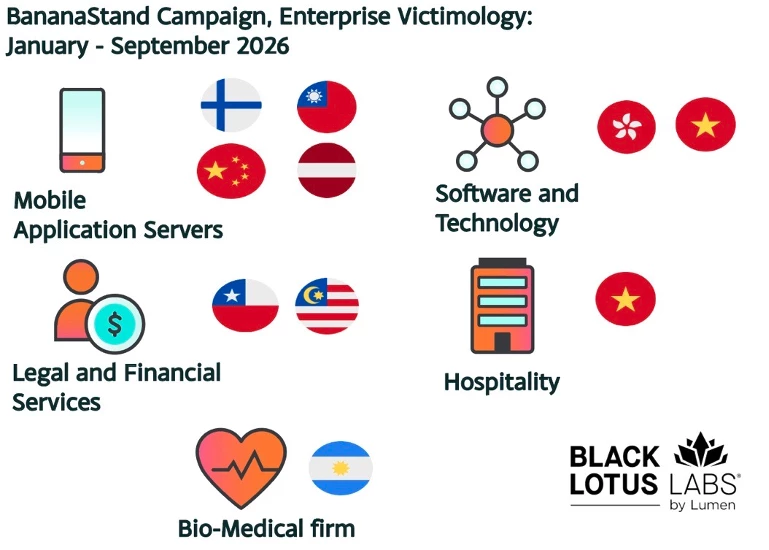
Victims included MikroTik and DrayTek routers in Singapore, Cambodia and Vietnam, as well as mobile-app servers, cryptocurrency-related systems, a Vietnamese hotel, a biomedical company in Argentina, a Chilean law firm, a Malaysian financial company and a GitLab instance in Hong Kong. Lumen recommends monitoring unexpected outbound MQTT traffic, restricting unsolicited SNMP access on routers, changing default community strings, mapping dependencies and investigating unusual data transfers.