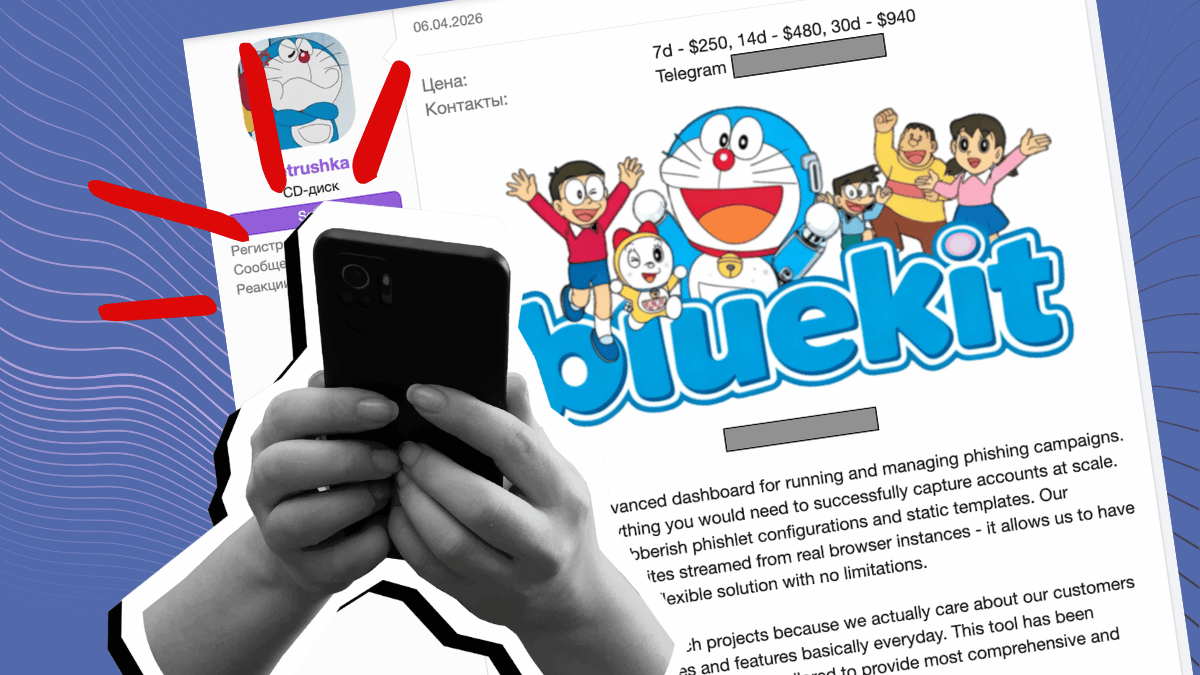
MALWAREBYTES researchers have detailed a rising phishing-as-a-service platform called BlueKit, which is designed to simplify and scale account hijacking for criminals. Since its appearance on a prominent cybercrime forum in April, BlueKit has evolved into a turnkey toolkit that lets operators manage phishing campaigns from a single dashboard, reducing the technical barriers to launching advanced scams. The service markets itself as “pixel-perfect and ready to deploy in one click,” and it now targets both consumer and business logins.
BlueKit offers a large template library that imitates 97 brands across 176 variants, including consumer services such as Amazon, Google, Apple and Booking[.]com, financial and crypto sites, social platforms, and even corporate systems like Salesforce, HubSpot, GitHub, Check Point, Citrix, Cloudflare and Cisco. Notably, the platform has expanded to include features such as an SMS sender for smishing campaigns and a built-in AI assistant that can draft phishing emails and fake texts without guardrails.
The operators claim over 1,000 customers as of August, with potential revenue calculations suggesting hundreds of thousands of dollars from subscriptions. In practice, BlueKit also captures device fingerprints and session cookies, enabling attackers to impersonate victims and bypass multi-factor protections, a combination that poses a significant risk to individuals and organisations alike.