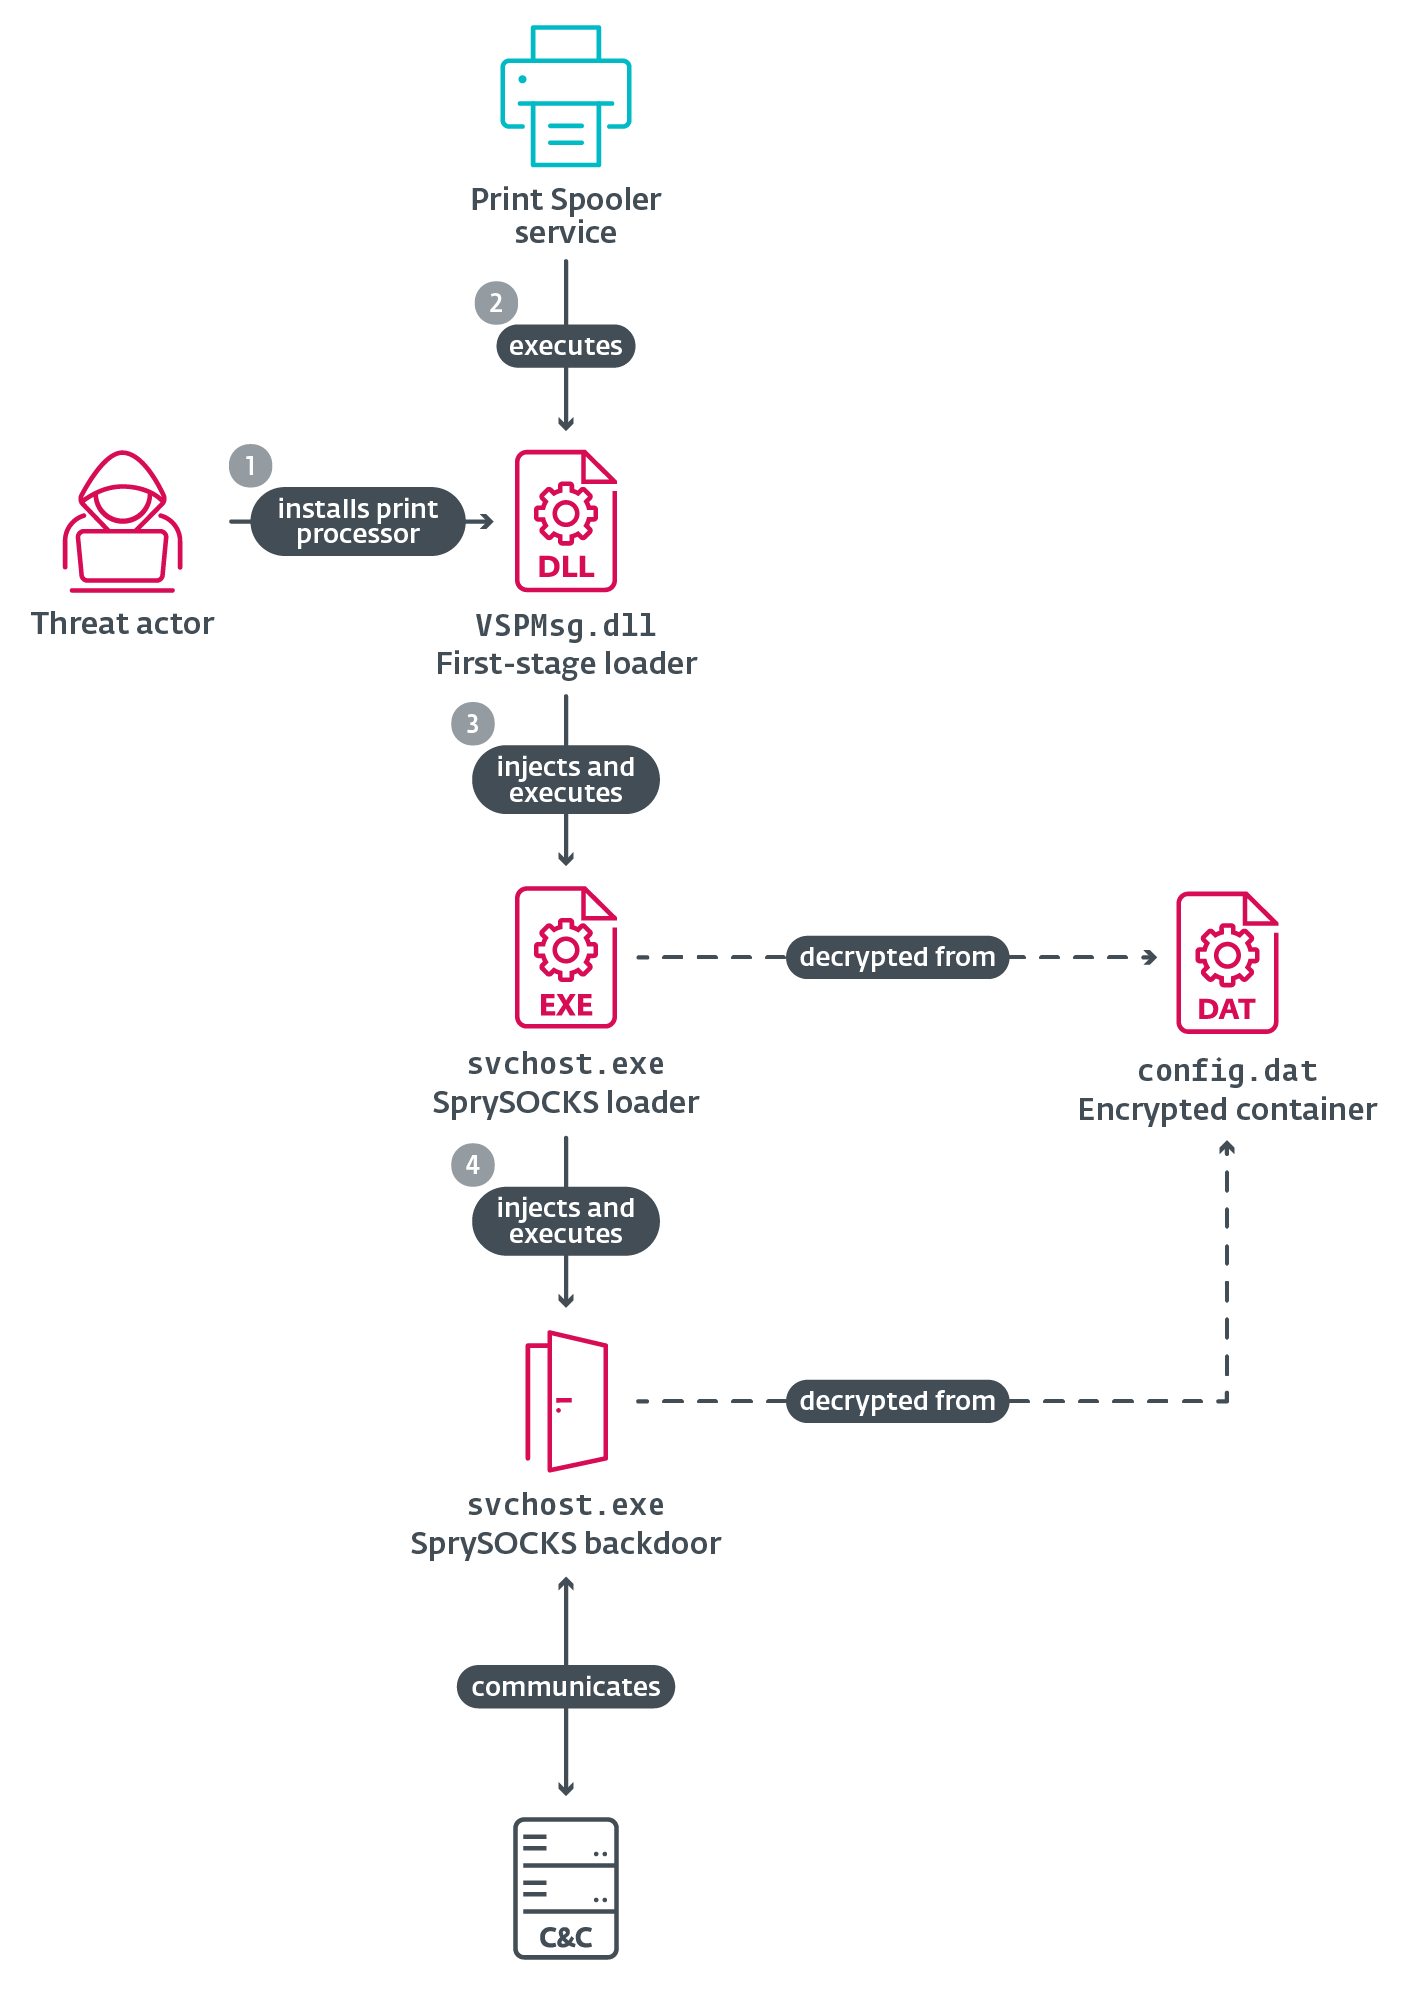
ESET researchers have identified two new Windows variants of the SprySOCKS backdoor, previously linked only to Linux, associated with the China-linked actor FishMonger. The variants, WIN_DRV and WIN_PLUS, leverage kernel drivers and the Print Spooler service to evade detection and target government organizations in Honduras, Taiwan, Thailand, and Pakistan. WIN_DRV employs a kernel driver to mask network connections, while WIN_PLUS uses the Print Spooler to inject malicious code.
Both variants enable commands such as system information collection and file manipulation. Additionally, there's speculation of a UEFI bootkit component exploiting a known Windows vulnerability, further complicating detection efforts for cybersecurity defenses.