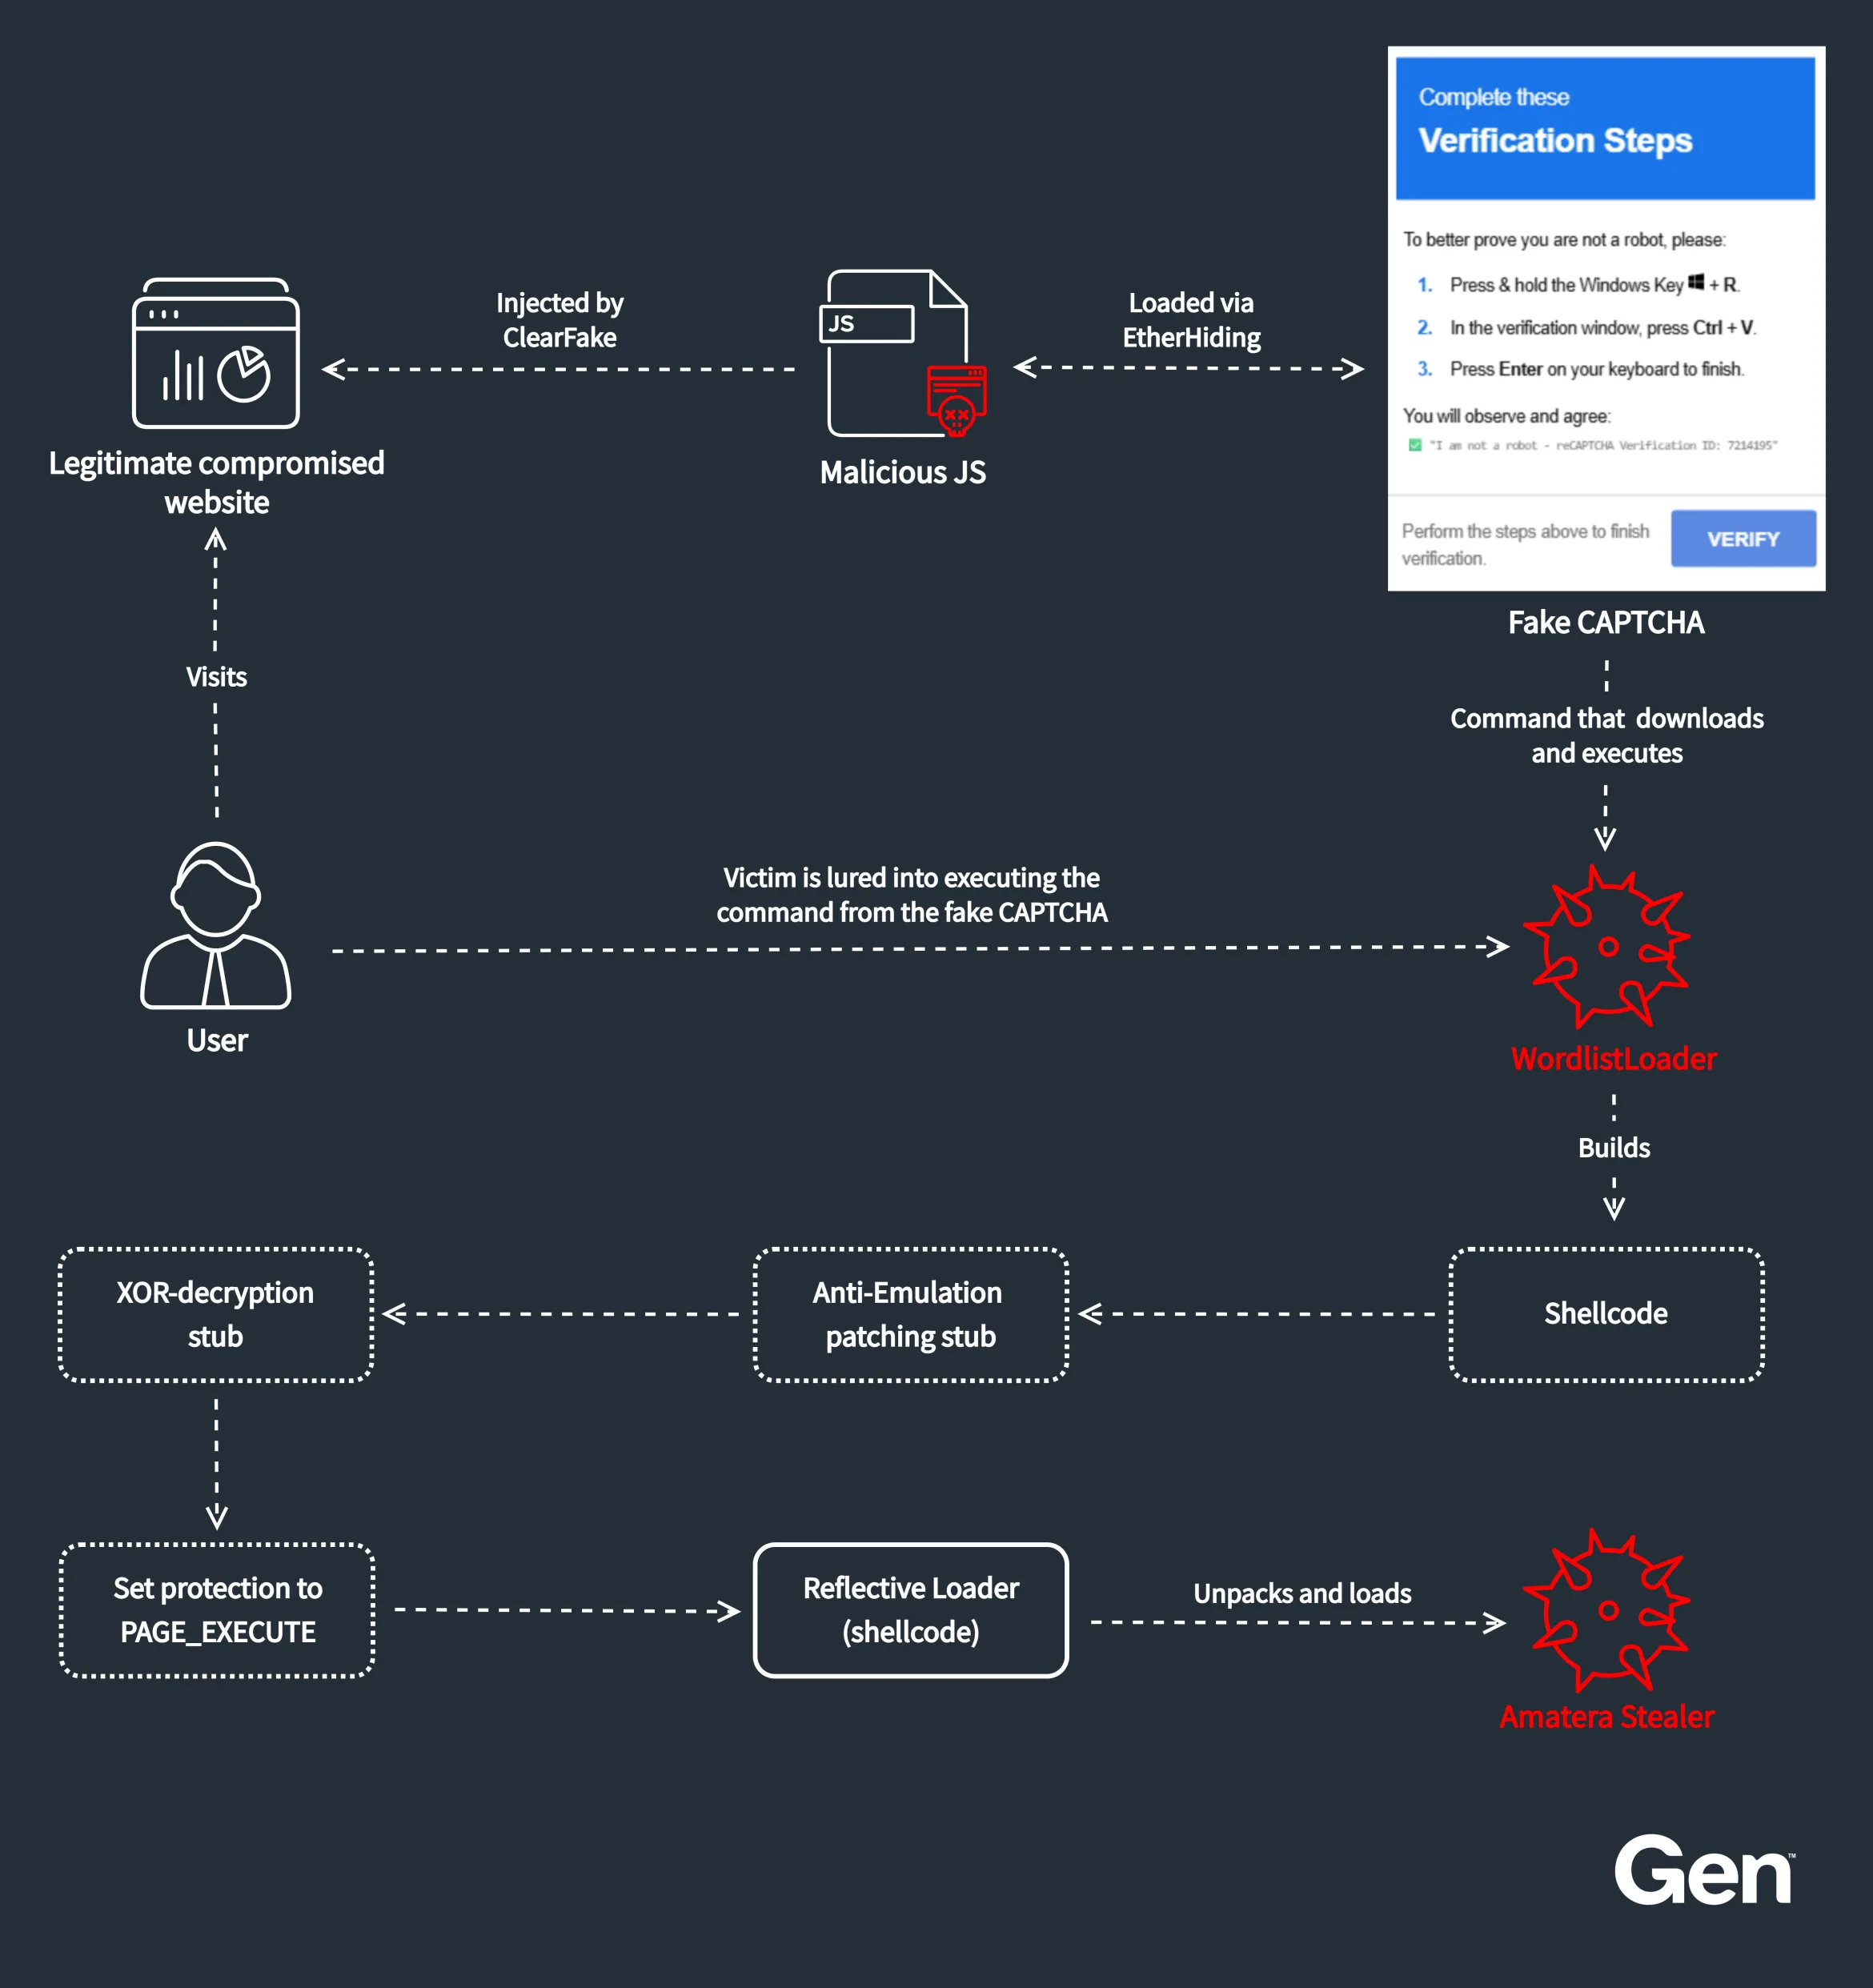
THE article discusses a newly identified malware called WordlistLoader, which delivers the Amatera Stealer through a fake CAPTCHA prompt known as ClearFake. The main points include:
1. **Malware Details**: WordlistLoader acts as a loader for Amatera Stealer, targeting Windows users by leveraging compromised websites.
2. **Infection Method**: Victims encounter a fake 'I’m not a robot' CAPTCHA that instructs them to execute a command, facilitating the malware's installation.
3. **Functionality**: The malware utilizes an innovative method of storing shellcode as plain English words, enhancing its stealth against security tools.
4. **Evasion Techniques**: It employs tactics like unhooking monitoring tools and bypassing Windows logging to evade detection.
5. **Payload Capability**: Amatera Stealer can extract sensitive data such as browser passwords and cryptocurrency wallet information.
6. **Preventive Measures**: Users are advised against executing commands from dubious websites, and defenders are encouraged to monitor specific unusual activities to thwart these attacks.