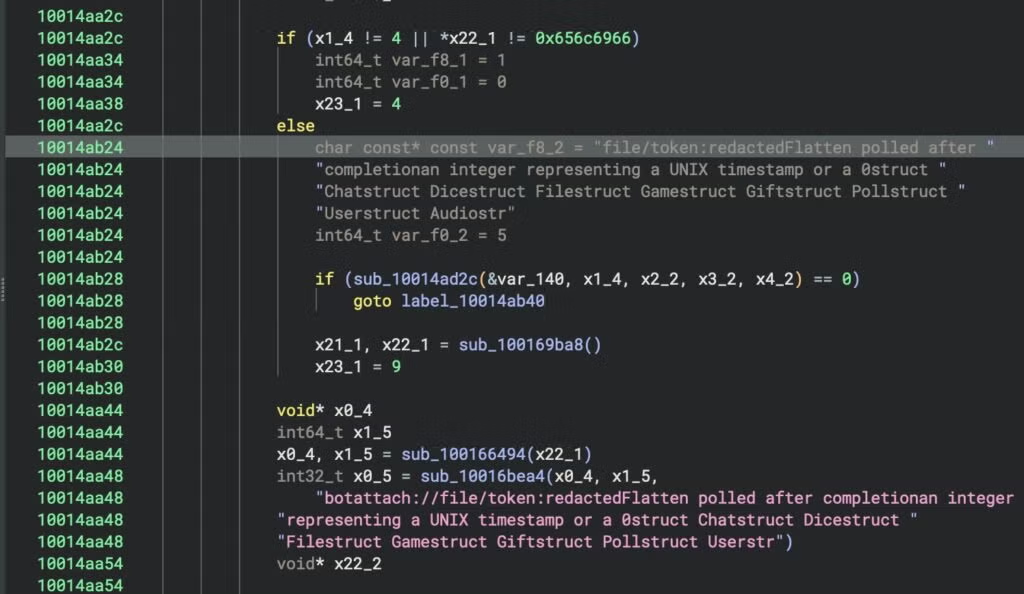
THE article discusses a new malware named macOS.Gaslight, attributed to North Korean hackers, which targets macOS systems. This Rust-based infostealer implants fabricated system messages designed to confuse AI-assisted malware analysts, ultimately manipulating their perception of the software's functionality. With 38 fake system messages, it aims to induce doubt in analysis, leading to potential misinterpretation or mishandling of the malware.
The malware features sophisticated controls, including encryption, self-redaction mechanisms, and a command system mimicking Apple's namespace for persistence. It is part of a broader toolset targeting multiple platforms, emphasizing the need for analysts to treat all sample data as potentially adversarial.