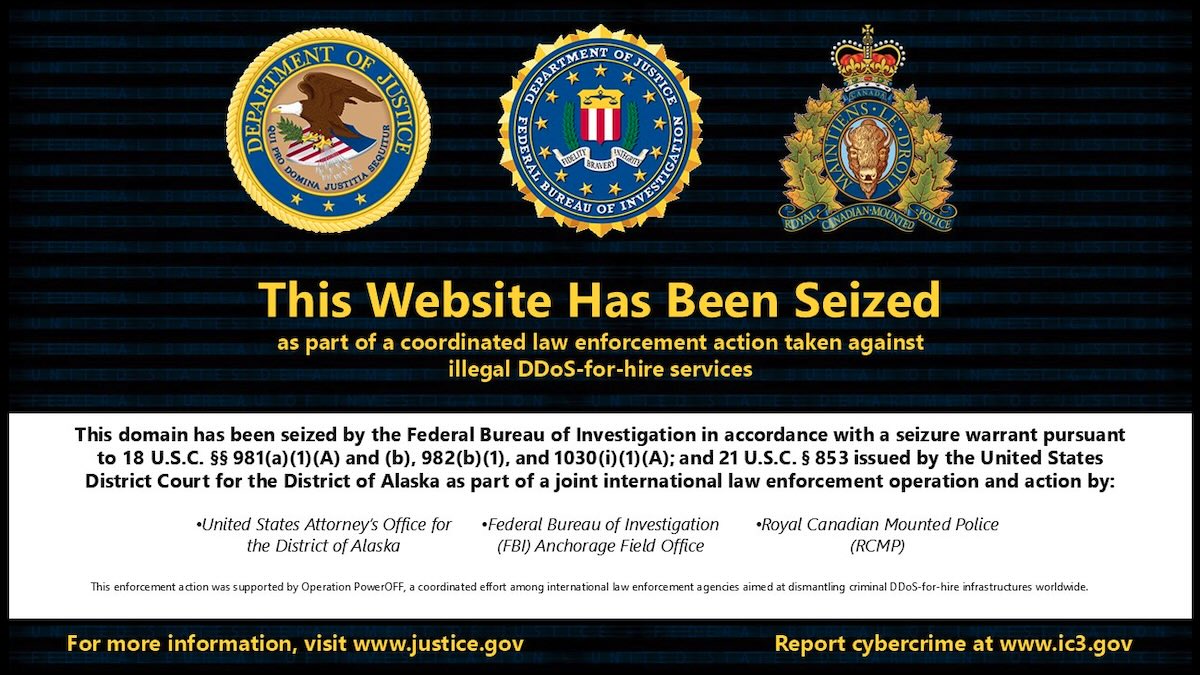
THE US Department of Justice says authorities have disrupted NightmareStresser, a long-running distributed denial-of-service (DDoS) “booter” service. The FBI seized the domains nightmare-stresser[.]com and nightmarestresser[.]org, which now display a law-enforcement seizure banner. The service was reportedly used to launch hundreds of thousands of DDoS attacks against victims worldwide.
The Justice Department said NightmareStresser had operated since at least 2022. However, security researcher Alex Carter reported last year that it may have been founded in 2016, became more widely used in 2018 and was the largest DDoS service in 2019. Carter’s research estimated that it had almost 1 million users by 2025 and could conduct between 3,000 and 4,000 attacks an hour. The service accepted cryptocurrency and reportedly excluded government, education and hospital domains from its targeting.
The seizure formed part of Operation PowerOFF, an international effort targeting DDoS-for-hire infrastructure and its operators and users. The US Department of Justice said it had charged 12 DDoS facilitators and seized more than 100 booter-related domains over the previous eight years. In April, authorities in 21 countries disrupted 53 related domains. The article does not report arrests or charges specifically linked to NightmareStresser.