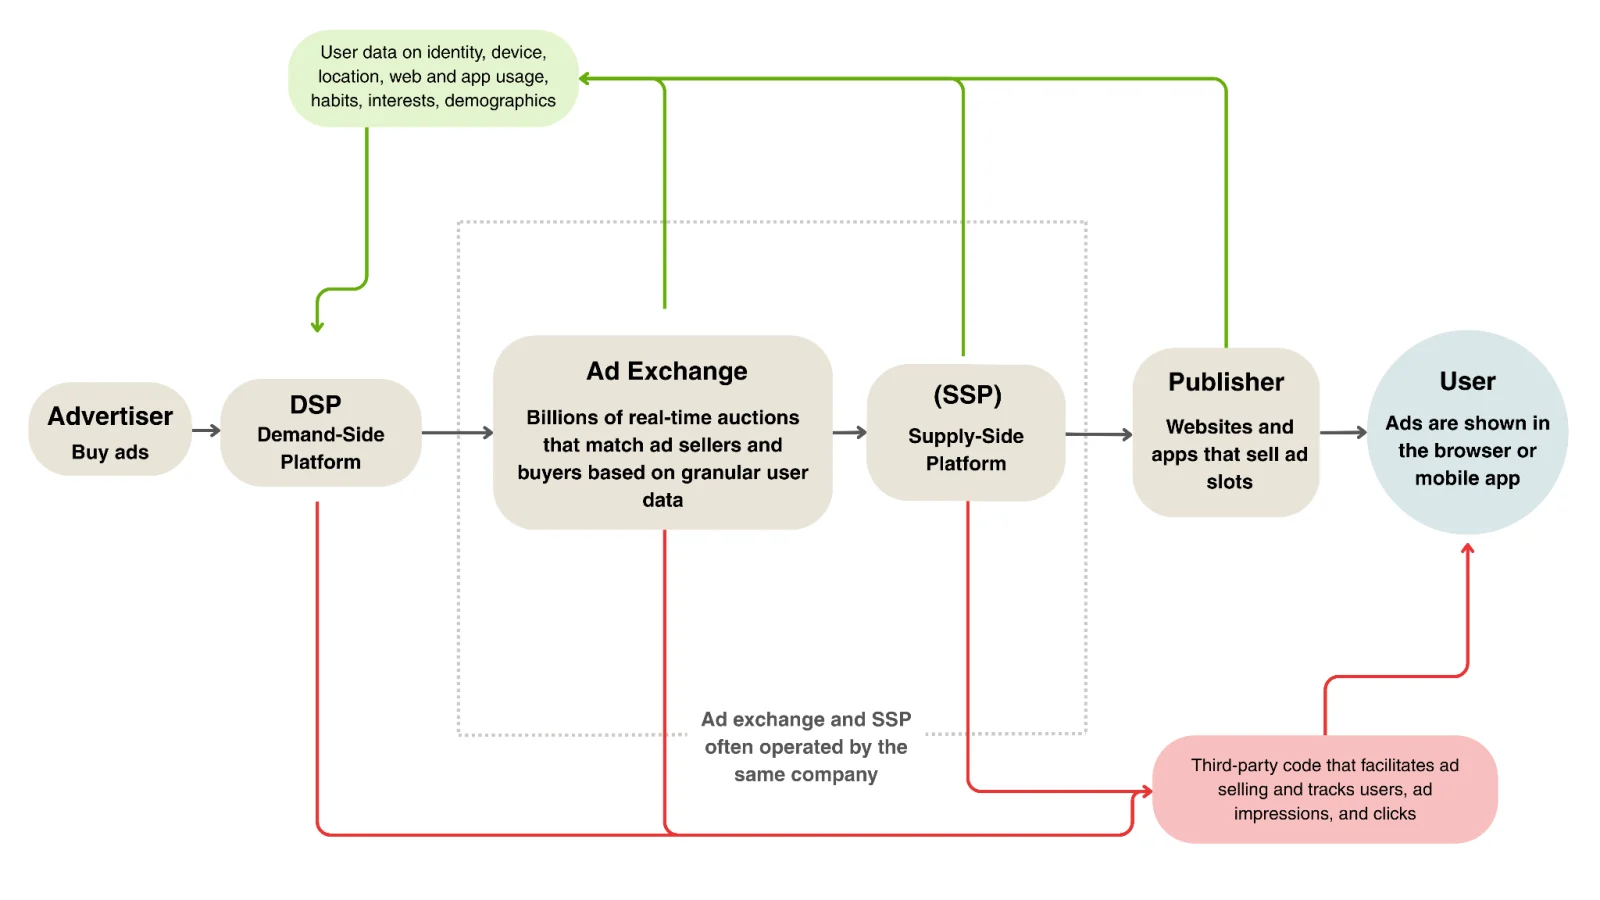
CITIZEN Lab has exposed a new AdFection spyware delivery chain that uses targeted advertising to plant information-stealing code on devices without any user interaction. The researchers describe how attackers leverage the real-time bidding (RTB) ecosystem to supply device and context data to an ad platform, then deploy a follow-up JavaScript inside an ad on a chosen device.
The technique allows a browser vulnerability to be exploited and the payload executed simply when an ad loads, without the user clicking anything. The Al Jazeera network was the targeted victim, with researchers saying the server decides when to return a malicious script based on signals such as device identifiers.
The investigation links the operation to Discover-Tech’s Controlium ad-delivery platform and the commercial spyware Candiru (also known as Sourgum). At least 45 Al Jazeera devices appeared on the target list between 2024 and 2025, according to network logs supplied by the broadcaster. A malware sample recovered from one infected device shows server-side details and code traits consistent with Candiru, reinforcing the connection with the Al Jazeera campaign.
The report emphasises that routine ad infrastructure can act as a pipeline for surveillance tools, illustrating a low-friction, zero-click vector that can bypass traditional user-initiated download steps. No broader campaign details are claimed beyond the Al Jazeera activity, though the researchers describe a high level of confidence in the Candiru attribution.