CVE-2024-26152: Label Studio vulnerable to Cross-site Scripting if `<Choices>` or `<Labels>` are used in labeling config
HumanSignal · label-studio
Affected: HumanSignal label-studio · Exploitation: possible (1 to 10%)
Not in CyberSIXT coverage yet: no article names this CVE. This page shows the public record.
Higher than 82% of scored CVEs
DescriptionCVE.org
Summary On all Label Studio versions prior to 1.11.0, data imported via file upload feature is not properly sanitized prior to being rendered within a [`Choices`](https://labelstud.io/tags/choices) or [`Labels`](https://labelstud.io/tags/labels) tag, resulting in an XSS vulnerability. ### Details Need permission to use the "data import" function. This was reproduced on Label Studio 1.10.1. ### PoC 1. Create a project. 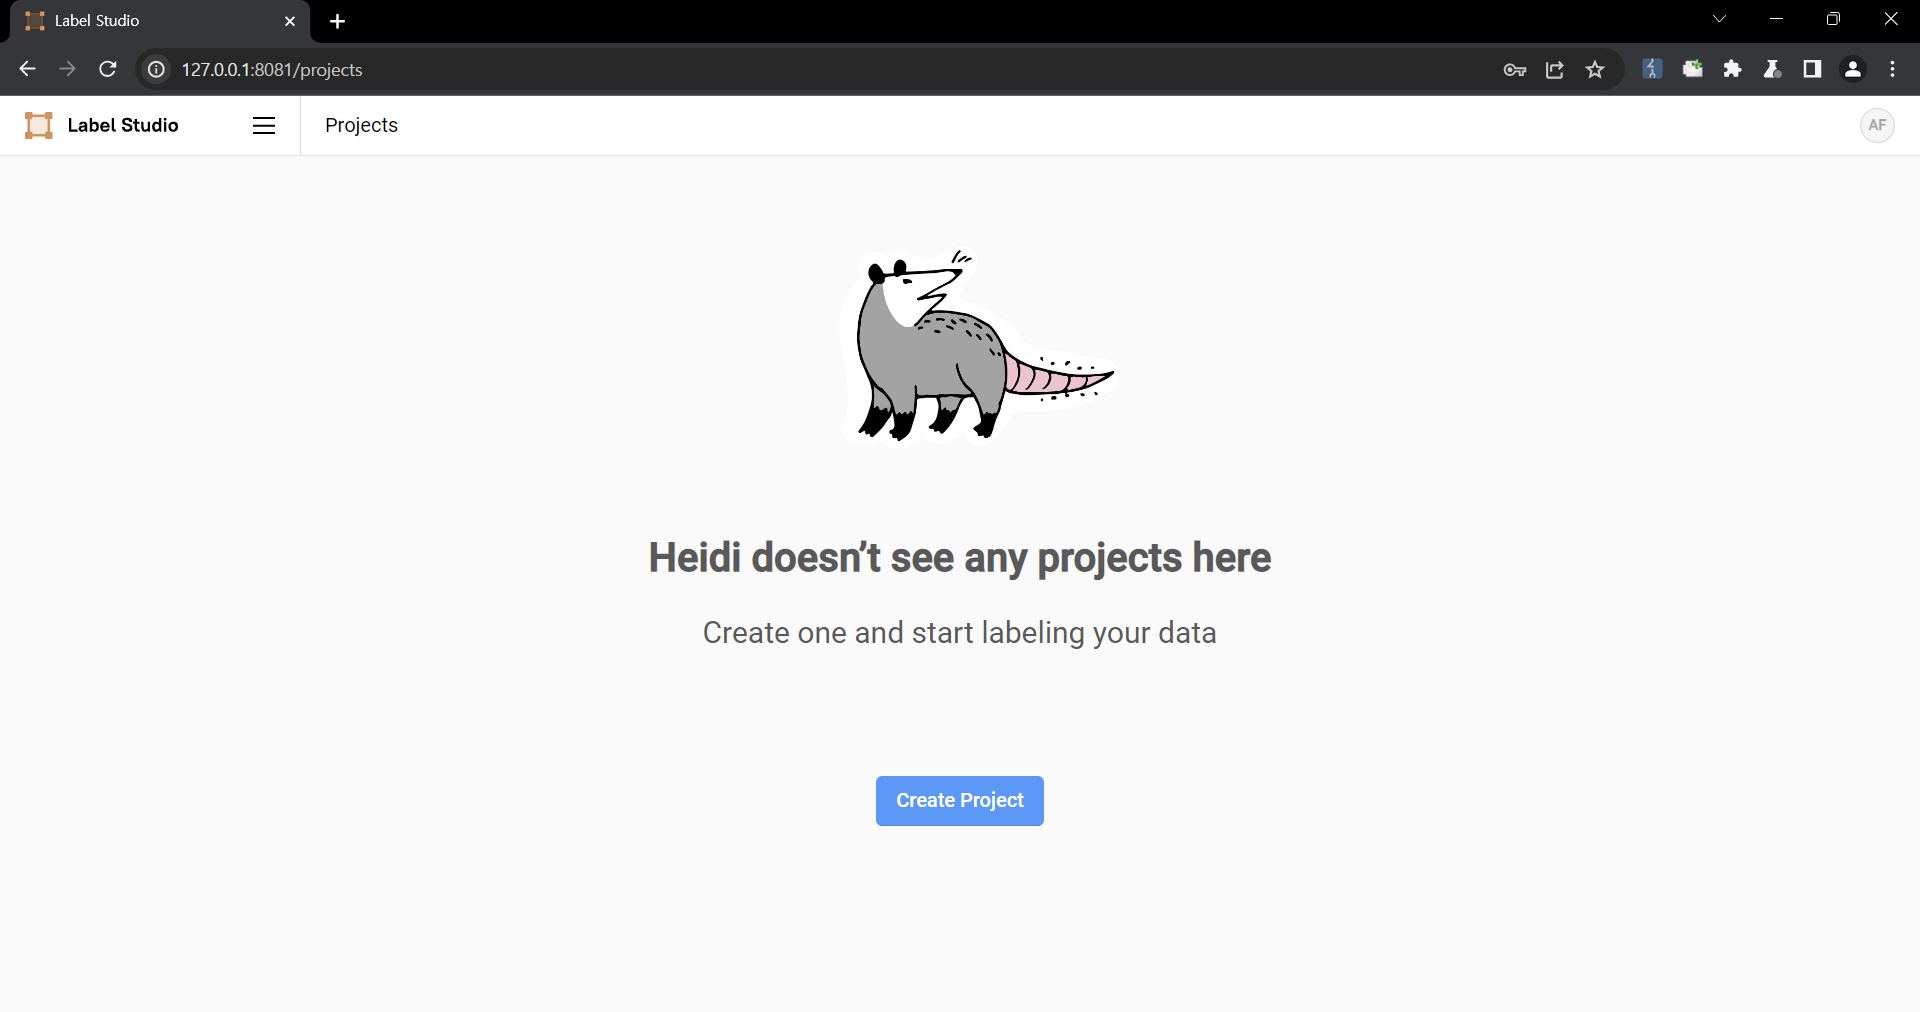 2. Upload a file containing the payload using the "Upload Files" function. 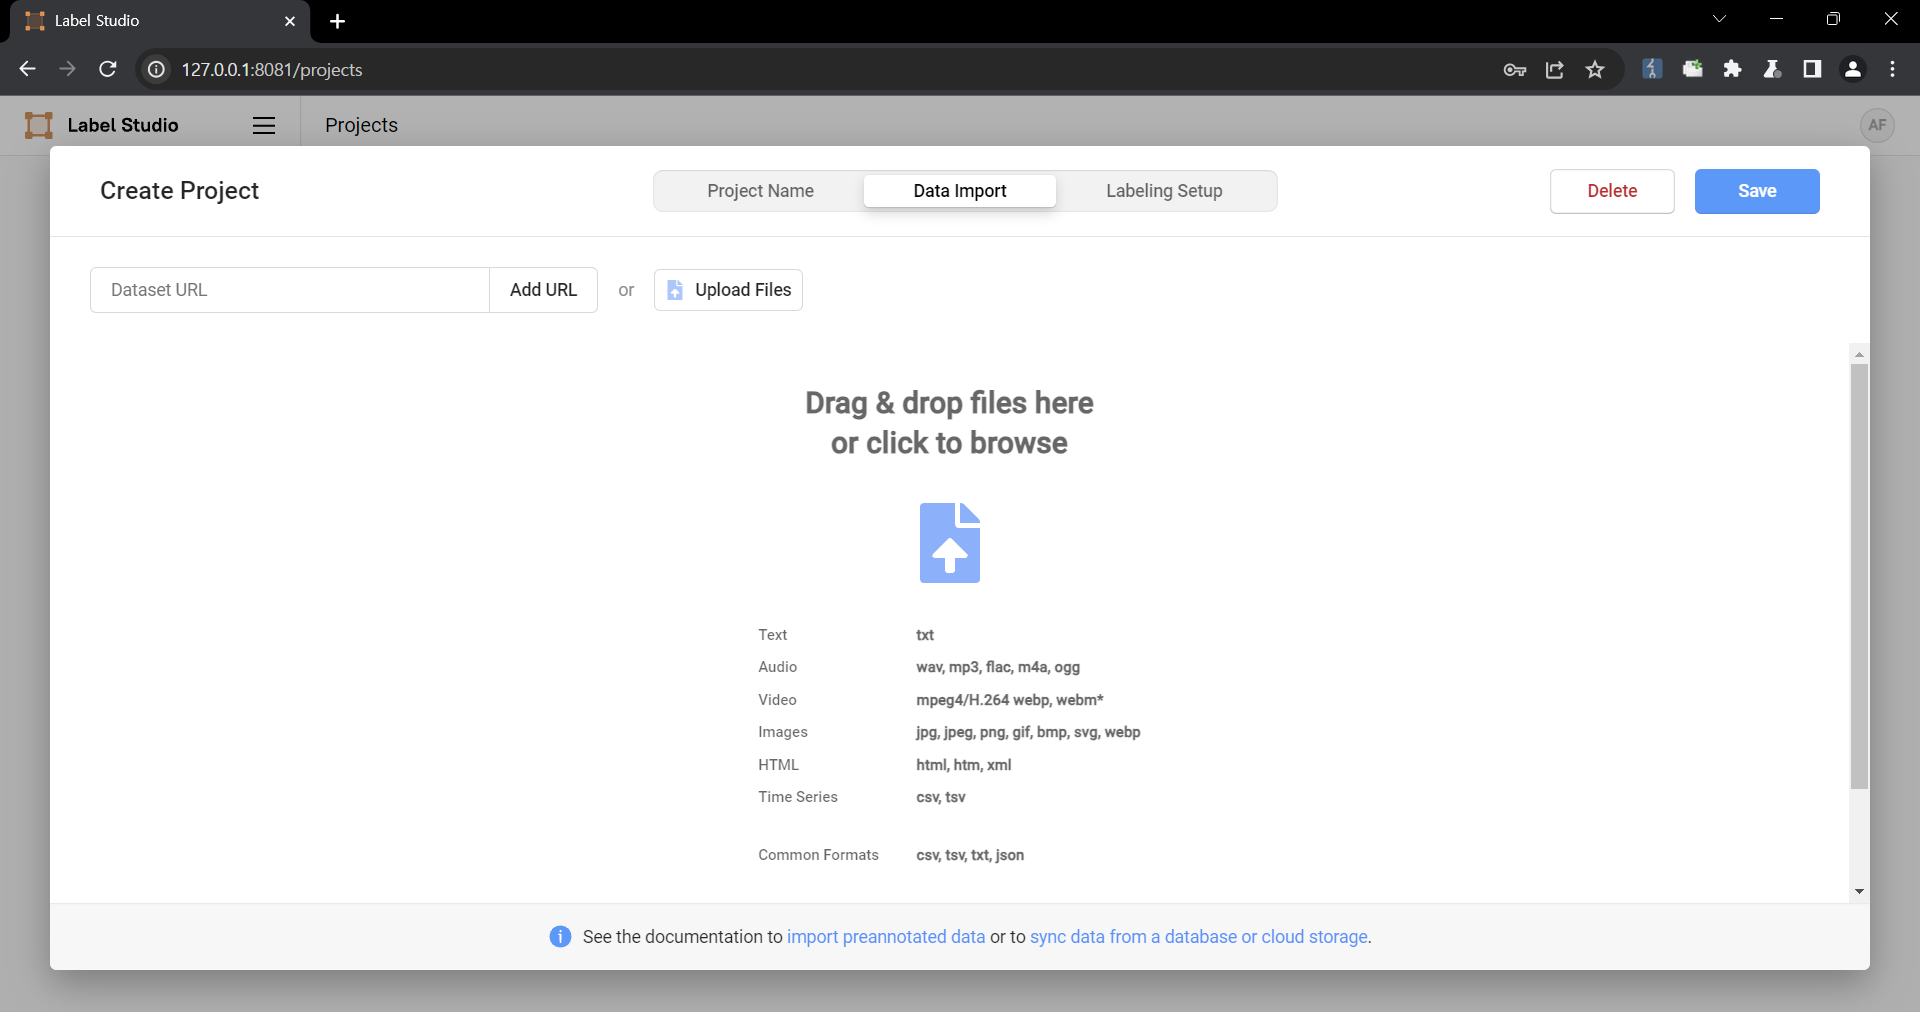 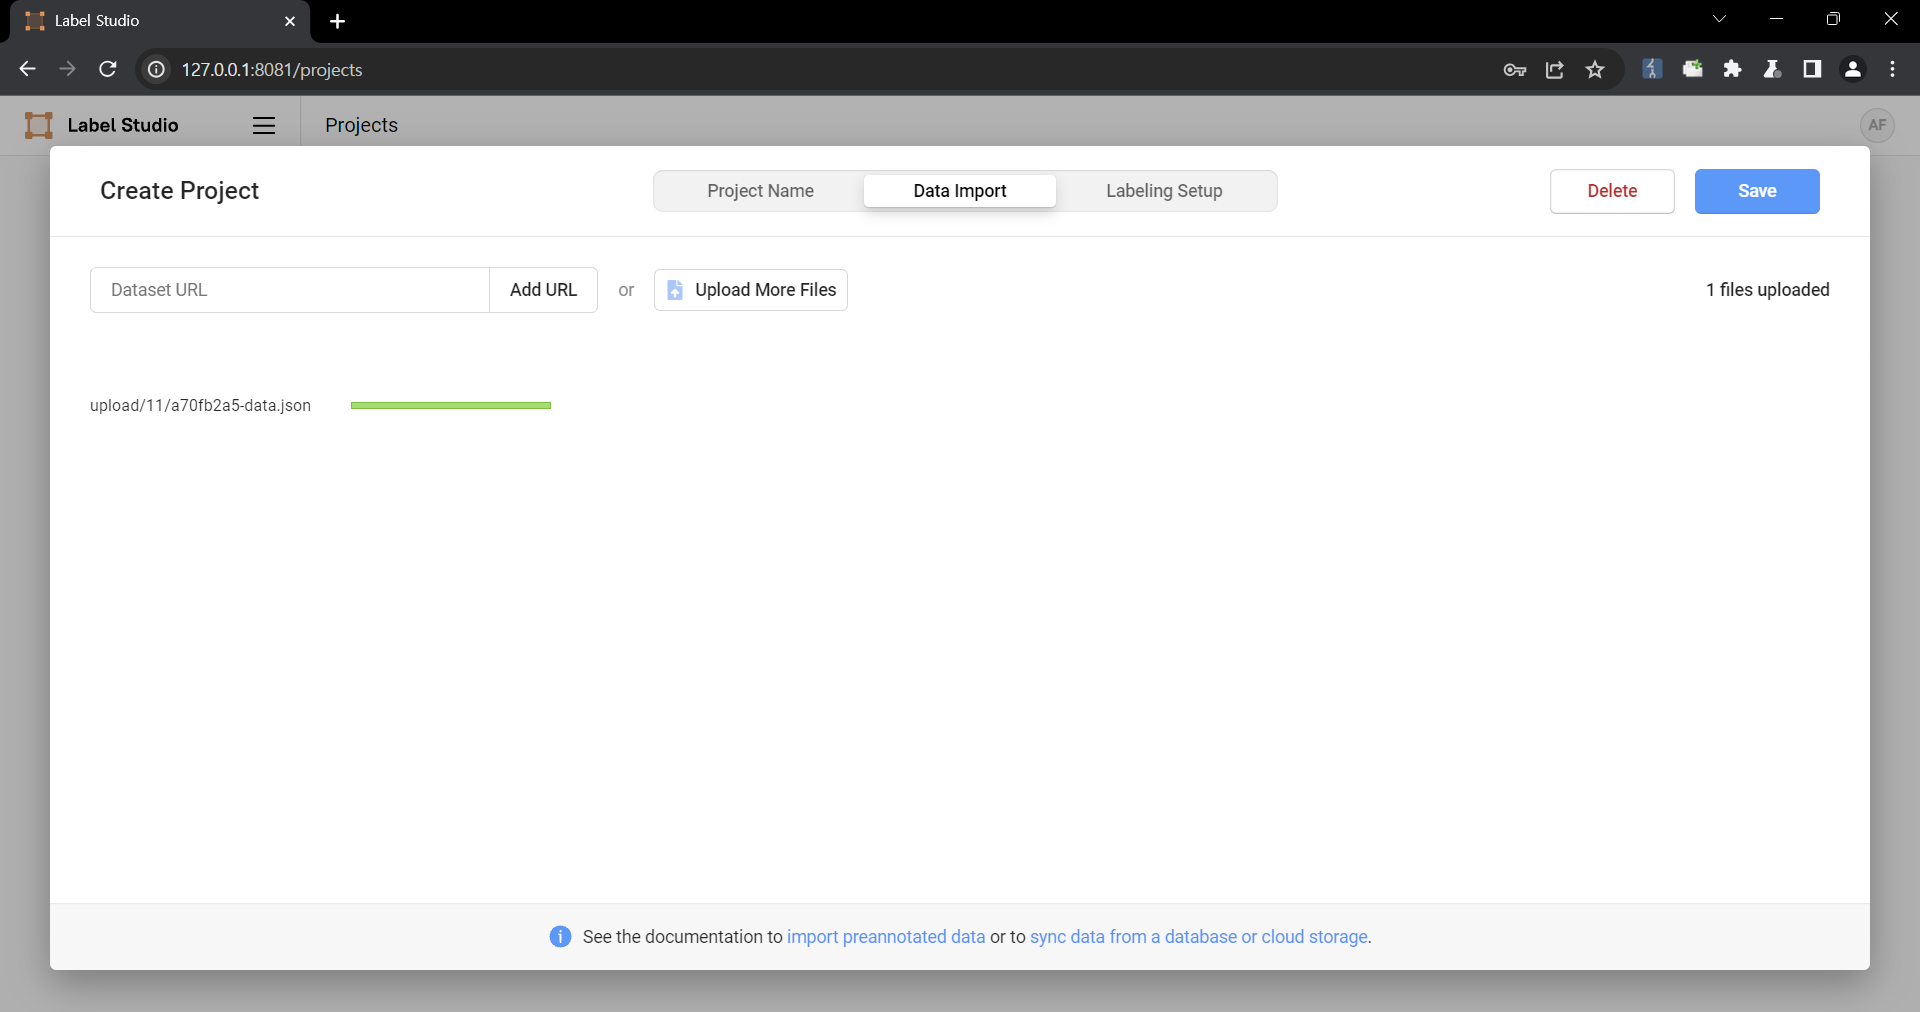 The following are the contents of the files used in the PoC ``` { "data": { "prompt": "labelstudio universe image", "images": [ { "value": "id123#0", "style": "margin: 5px", "html": "<img width='400' src='https://labelstud.io/_astro/images-tab.64279c16_ZaBSvC.avif' onload=alert(document.cookie)>" } ] } } ``` 3. Select the text-to-image generation labeling template of Ranking and scoring 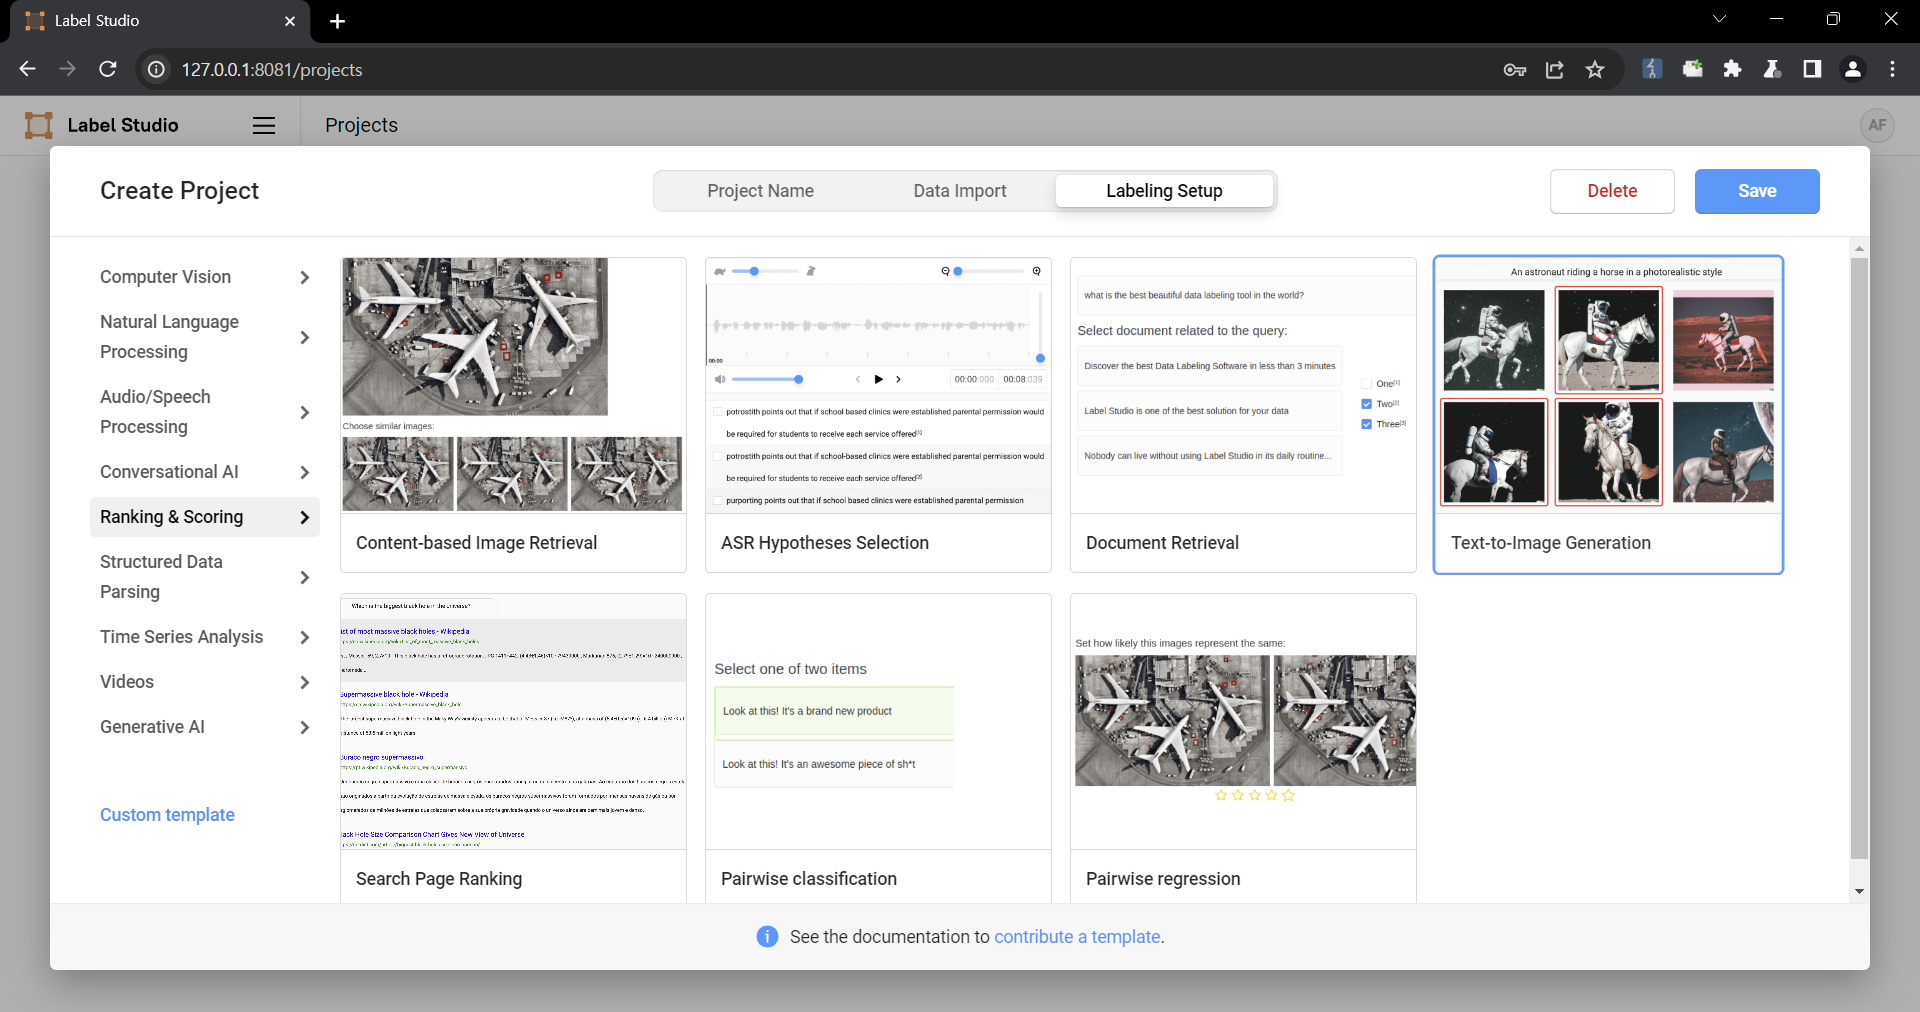 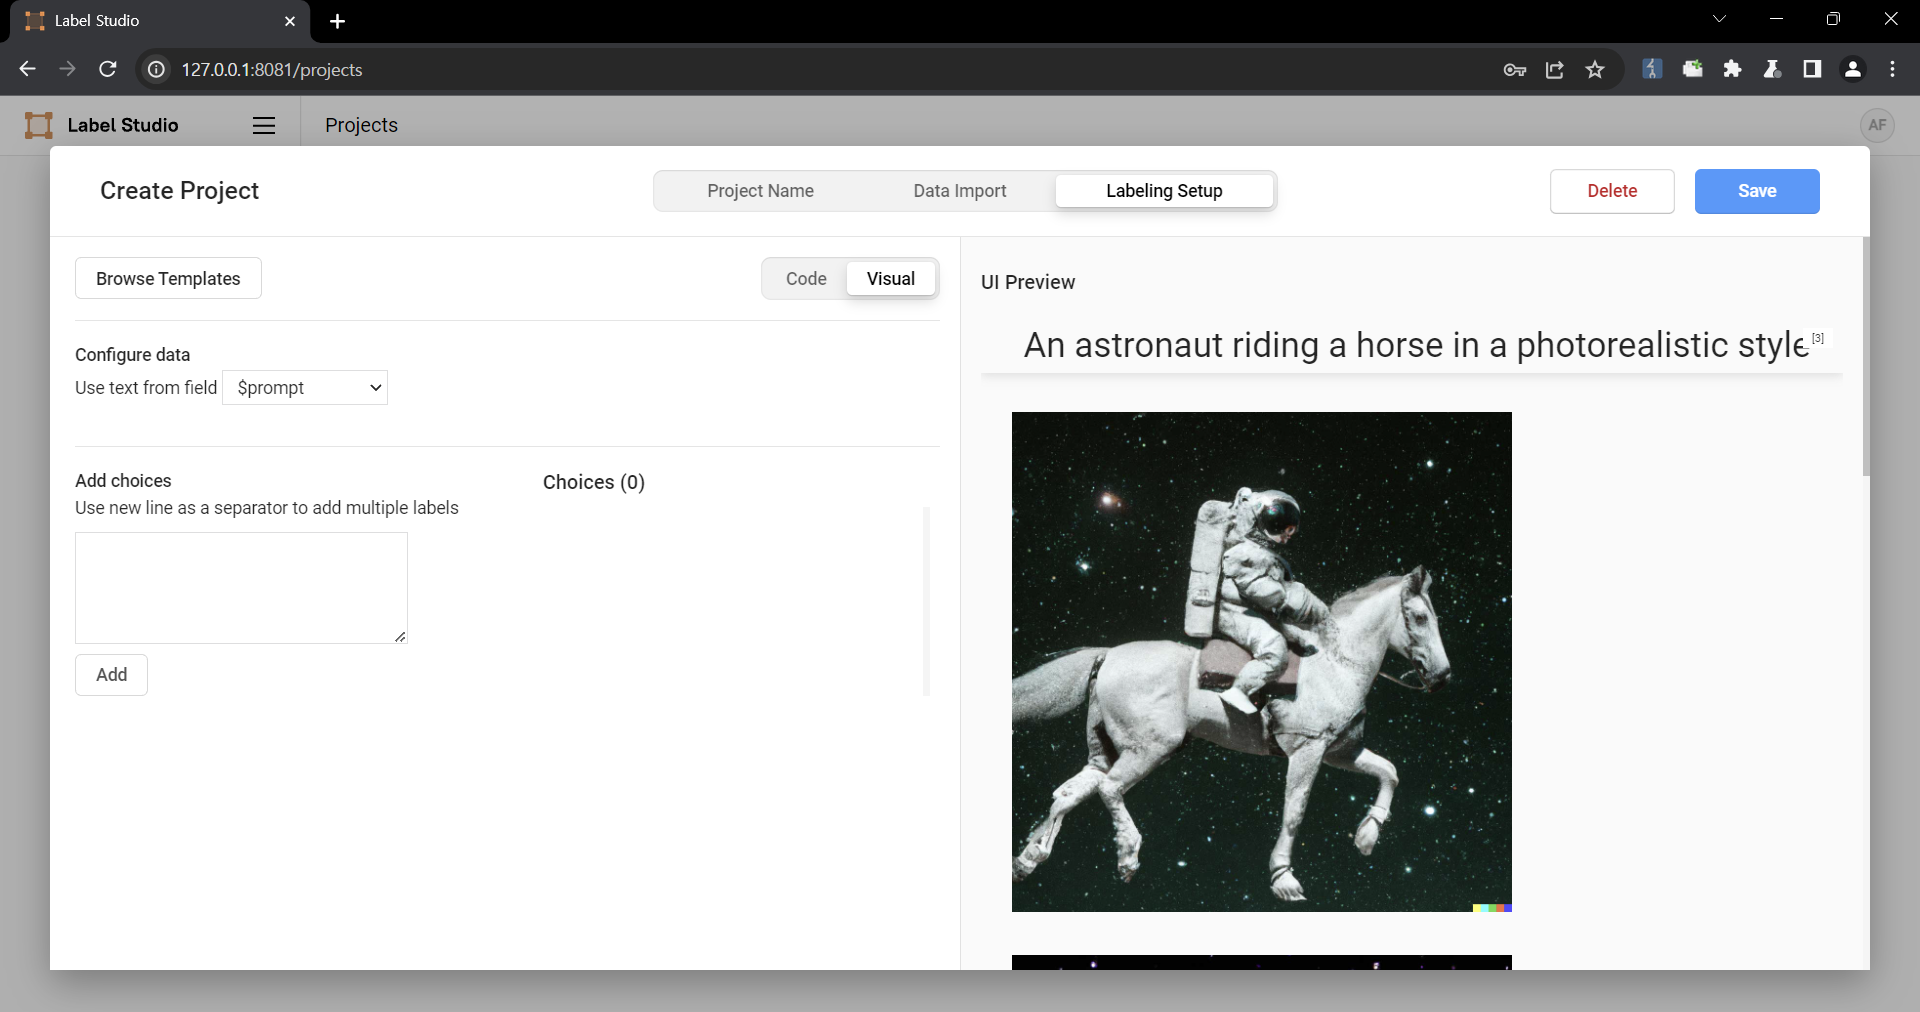 4. Select a task 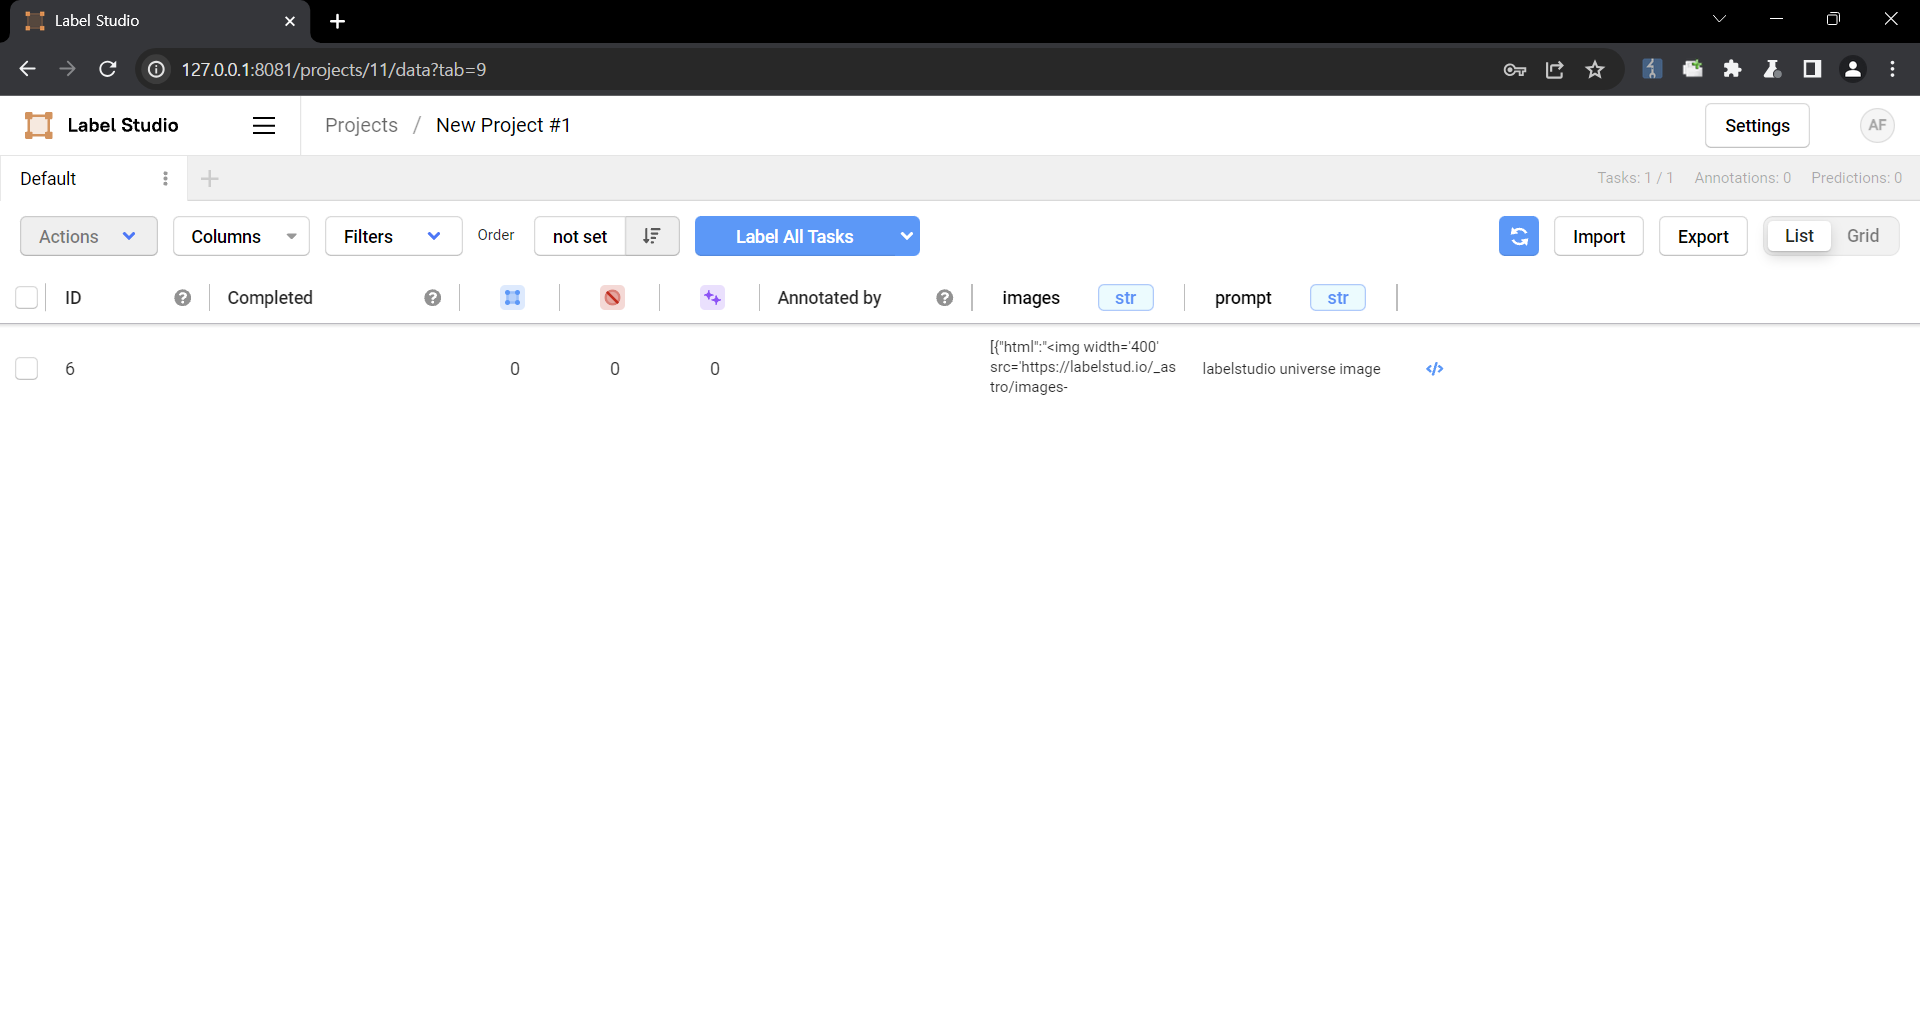 5.
Affected products1
From the CVE record. A product or version that is not listed is unknown, not unaffected.
- HumanSignal · label-studio< 1.11.0
On the Atlas
Every published CVE is on the CyberSIXT Atlas, grouped by weakness, vendor and month.
- Exploitation
- Possible (1 to 10%). EPSS between 1% and 10%.
- CISA KEV
- Not listed
- Public check
- No public nuclei template
- Weakness
- Cross-site Scripting
- Vendor
- HumanSignal
- Published
- February 2024
CoverageNo articles yet
No CyberSIXT article names CVE-2024-26152 yet, so there is no coverage timeline, action brief or change log for it. Everything on this page comes from the public CVE record, CISA KEV, EPSS and the nuclei template index. Search the archive or see the CVEs in the news.
References
- NVD entrynvd.nist.gov
- CVE recordcve.org
- Weakness CWE-79cwe.mitre.org
- github.com/HumanSignal/label-studio/security/advisories/GHSA-6xvgithub.com
- github.com/HumanSignal/label-studio/pull/5232github.com
- github.com/HumanSignal/label-studio/commit/5df9ae3828b98652e9fa2github.com
- github.com/HumanSignal/label-studio/releases/tag/1.11.0github.com