News
Every CyberSIXT summary, newest first, with a link to its story and to the original report.
Most articles on Wed 21 Oct (96); 9–13 on weekend days.
Show as table
| Day | Articles published |
|---|---|
| Sun 11 Oct | 9 |
| Mon 12 Oct | 56 |
| Tue 13 Oct | 85 |
| Wed 14 Oct | 86 |
| Thu 15 Oct | 78 |
| Fri 16 Oct | 61 |
| Sat 17 Oct | 10 |
| Sun 18 Oct | 10 |
| Mon 19 Oct | 60 |
| Tue 20 Oct | 86 |
| Wed 21 Oct | 96 |
| Thu 22 Oct | 84 |
| Fri 23 Oct | 68 |
| Sat 24 Oct | 13 |
| Today, Sun 25 Oct | 9 so far |
Thu 10 Sep· 18 articles
-
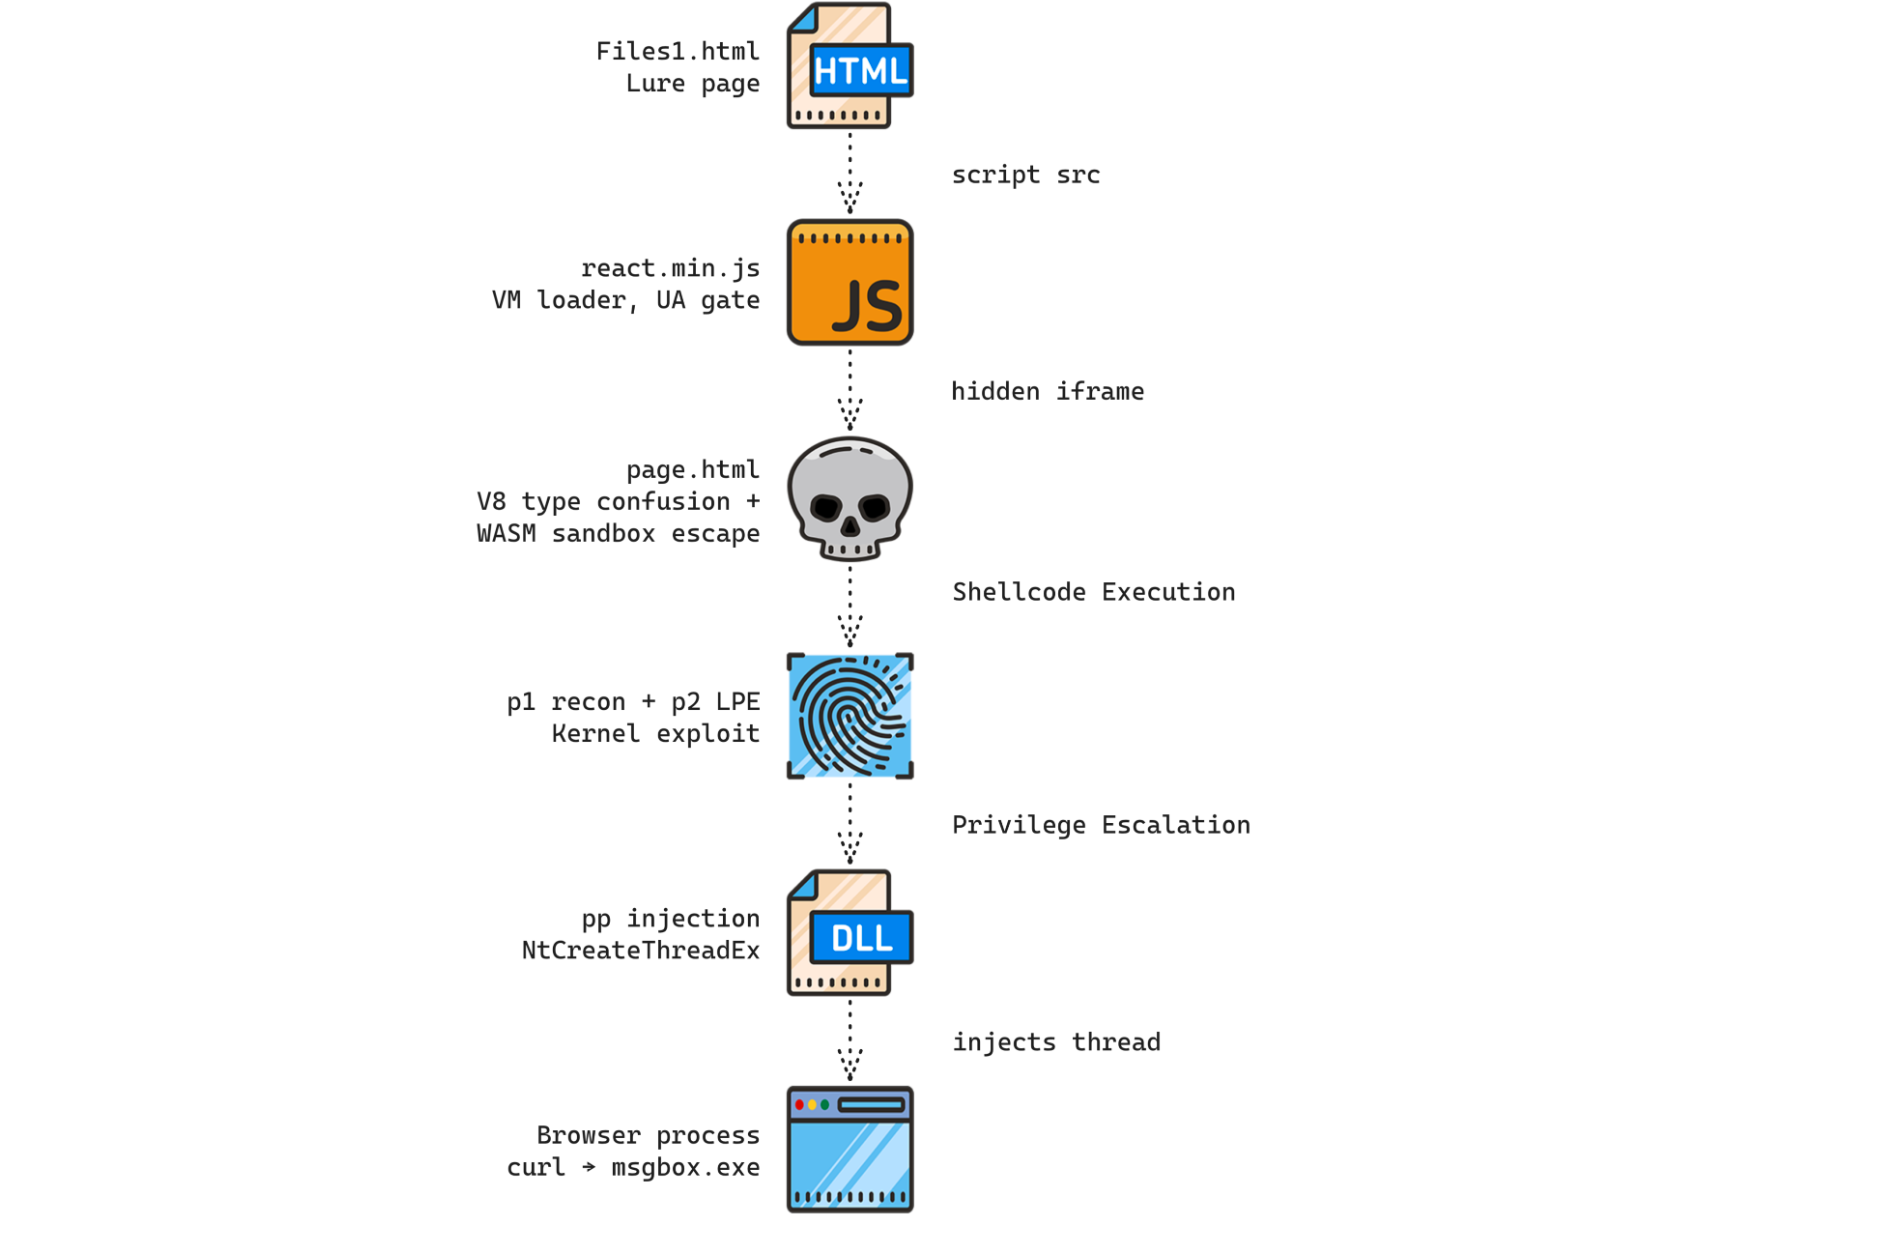
Chrome Zero Day Chain Targeted NGOs Before Google’s Patch Arrived
Security researchers have traced a Chrome-focused zero-day chain used by two Chinese espionage cohorts, UTA0560 and JungleBamboo (APT31), to target NGOs and public policy institutes across borders. The attackers carried out spear-phishing campaigns…
-
OpenMatter Names New CEO as It Shifts Focus to Global Growth
OpenMatter Network has announced a strategic realignment of its leadership as it moves from its initial platform launch into a phase of global commercial growth. The Melbourne, Florida-based company said that, effective 1 September, Mike Anderson has taken…
SecurityOnline
-
OnePlus 13R Flaw Lets Malicious Apps Hijack Cloud Sessions
Researchers have disclosed a severe OnePlus session takeover vulnerability that affects OnePlus 13R Android devices. The flaw resides in the device account management software, specifically the com.oneplus[.]account application and its exported content…
SecurityOnline
-
Apple May Add Security Chips to Gift Cards to Fight Fraud
Apple is stepping up efforts to curb gift-card fraud by reportedly embedding dedicated security chips into future physical Apple Gift Cards. The story, based on code discovered in the iOS 27 Release Candidate, suggests that these chips would be read by…
SecurityOnline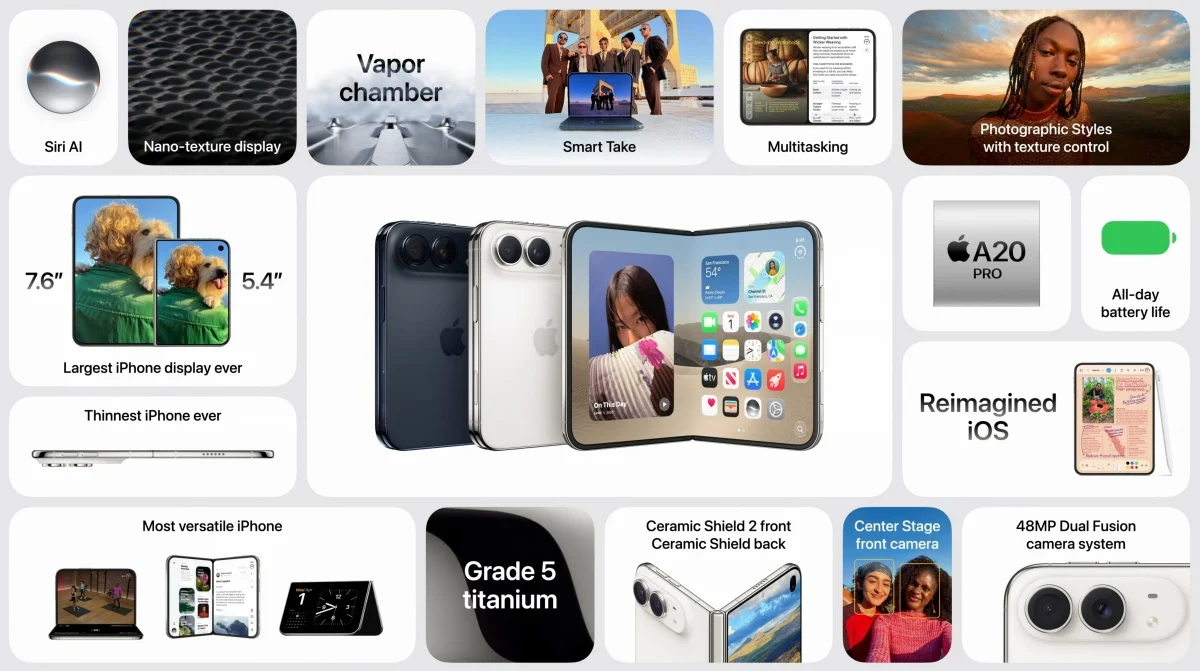
-
Google Photos Cuts Recovery Window as Trash Retention Drops to 30 Days
Google Photos has changed its trash retention policy. In the latest official guidance, items placed in the trash will remain there for 30 days before being permanently erased, after which they cannot be recovered via Google. This shortens the previous 60-day…
SecurityOnline
-
Microsoft Plans Windows 11 Age API to Limit Apps’ Data Collection
Microsoft is developing a Windows 11 age-awareness API to satisfy growing age-rating and age-verification obligations in several jurisdictions. The core idea is that Microsoft collects a user’s age signal at the OS level, then shares only a basic age bracket…
SecurityOnline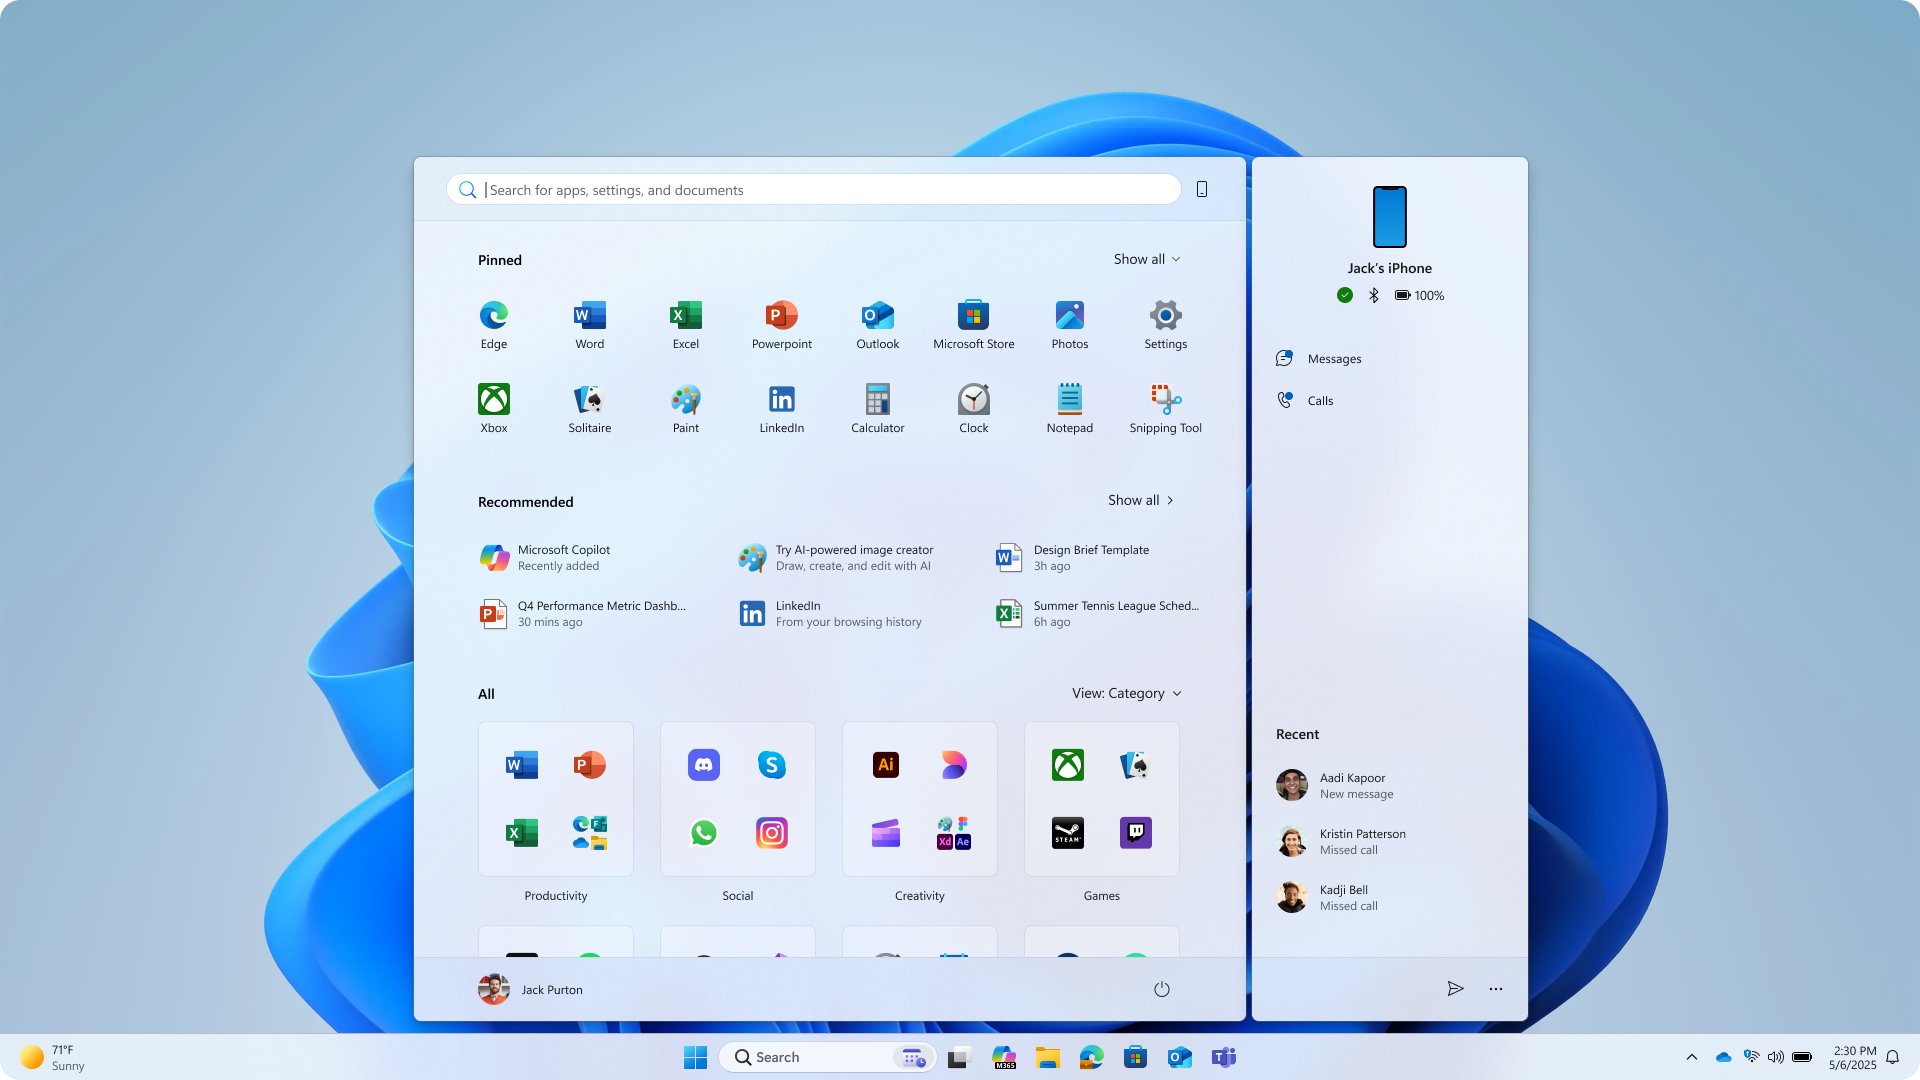
-
Brave Search API Keeps Free Searches as Billing Moves Prepaid
Brave has announced a shift in how its Brave Search API is billed, moving newly activated plans from a postpaid, pay‑as‑you‑go model to a prepaid, pay‑as‑you‑go model. Existing subscribers on a postpaid plan will remain unaffected, but if they cancel and…
SecurityOnline
-
Stealthy Ted Backdoor Hijacks HAProxy to Spy on South Korea
Rapid7 researchers have identified a stealthy Linux backdoor, dubbed the ted backdoor, that hides inside a modified HAProxy load balancer to spy on South Korean organisations. The tool is designed to run as a plugin for HAProxy version 2.8.12, allowing the…
SecurityOnline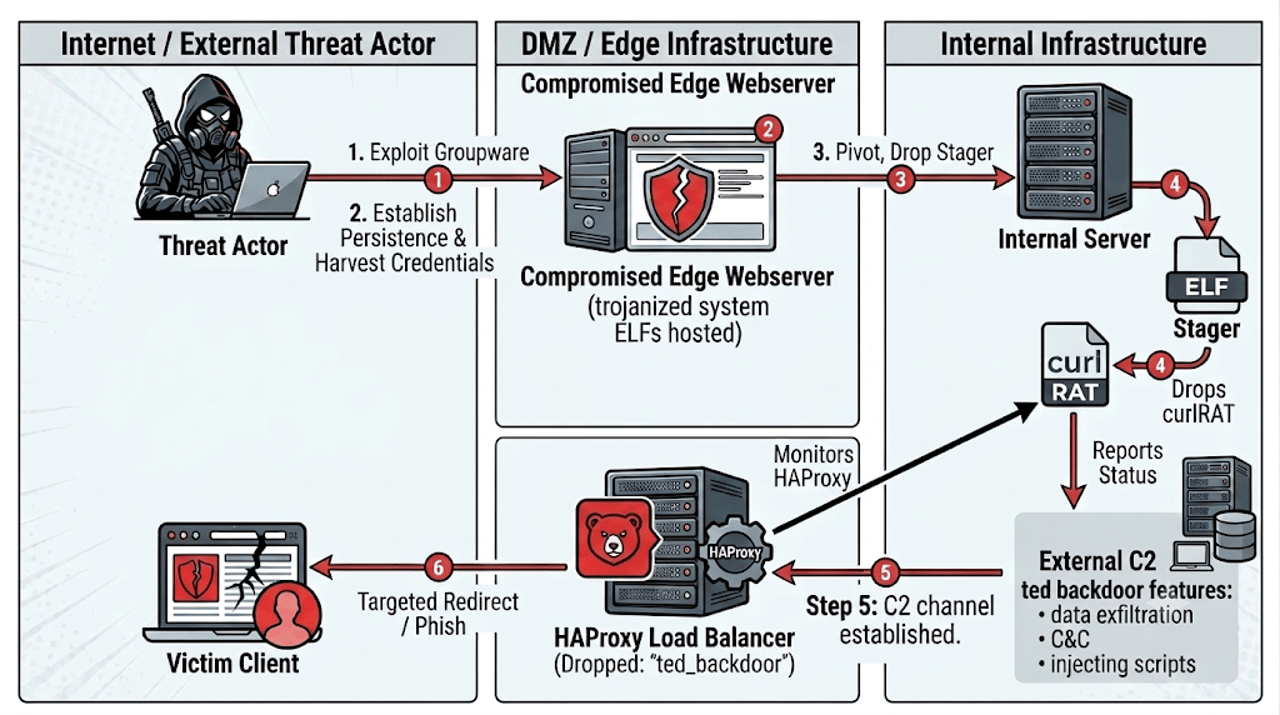
-
Microsoft Warns of AI-Inspired Phishing Campaign Hitting Millions
Microsoft threat researchers have disclosed a large-scale phishing campaign that uses AI-inspired ASCII smuggling to evade detection. Beginning around 8–9 February 2026, attackers deployed messages that insert invisible Unicode tag characters inside…
SecurityOnline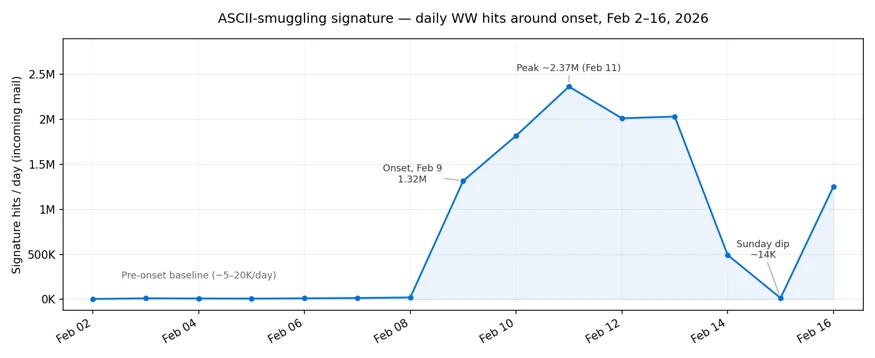
-
Kimsuky Uses AI Agent to Scale Phishing Against Finance Teams
North Korean state-sponsored threat group Kimsuky is alleged to be using an AI-powered agent, named opencode, to automate the creation of phishing decoys and scale its espionage campaigns. Researchers from Genians Security Center report intercepting 13…
SecurityOnlineKimsuky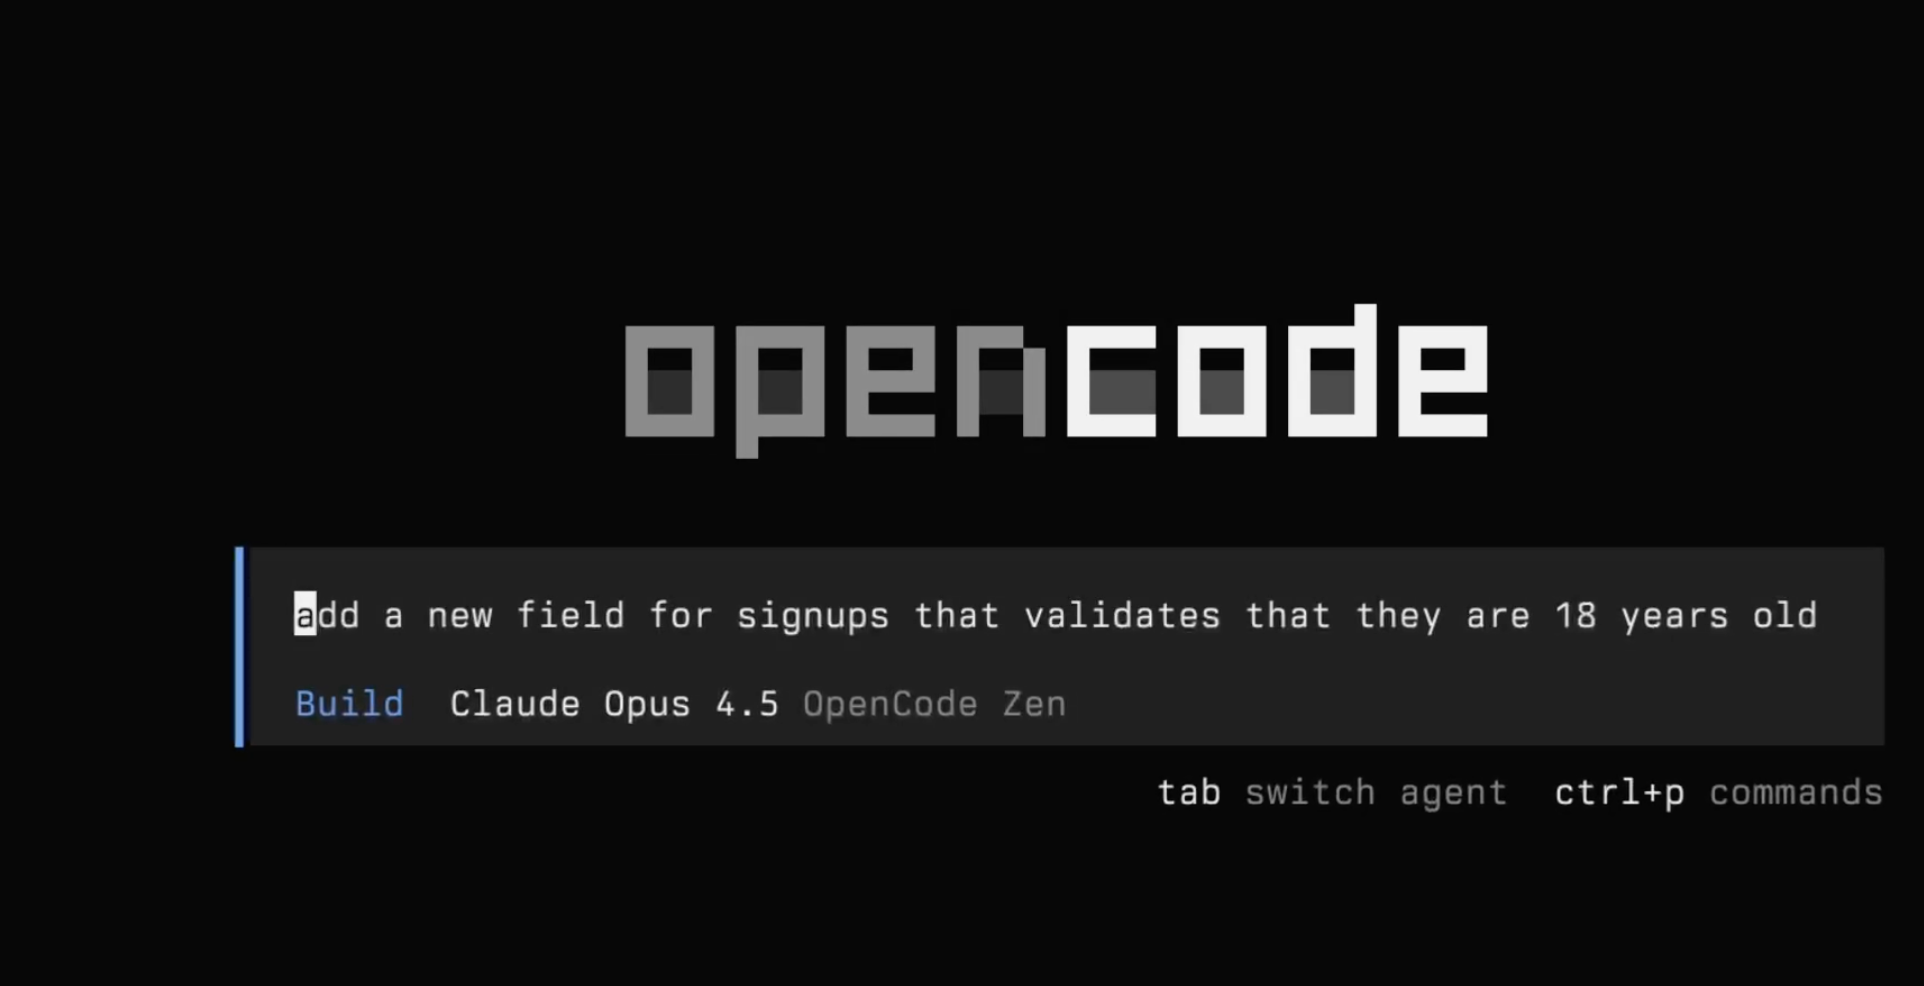
-
NVIDIA Patches Triton Flaws Exposing ML Servers to Remote Attacks
NVIDIA has released patches for two high-severity vulnerabilities in its Triton Inference Server, addressing security flaws that could allow unauthenticated remote attackers to cause a denial of service and access unauthorised data. The issues, tracked as…
-
Apache Artemis Flaws Let Attackers Steal Sessions and Expose Credentials
Five high‑severity flaws in Apache Artemis, encompassing the Core and protocol handling layers, require immediate attention. The vulnerabilities, linked to ActiveMQ Artemis, could enable unauthorised session theft, credential exposure and denial of service.…
-
Microsoft Warns Passkey Scams Are Breaching Cloud Tenants
Microsoft threat intelligence has flagged active cloud intrusions that abuse passkey social engineering to breach enterprise tenants, with observations dating to 9 September 2026. The campaigns, linked to Storm-3121 and Storm-3032 (Helix) and related…
SecurityOnlineStorm-3121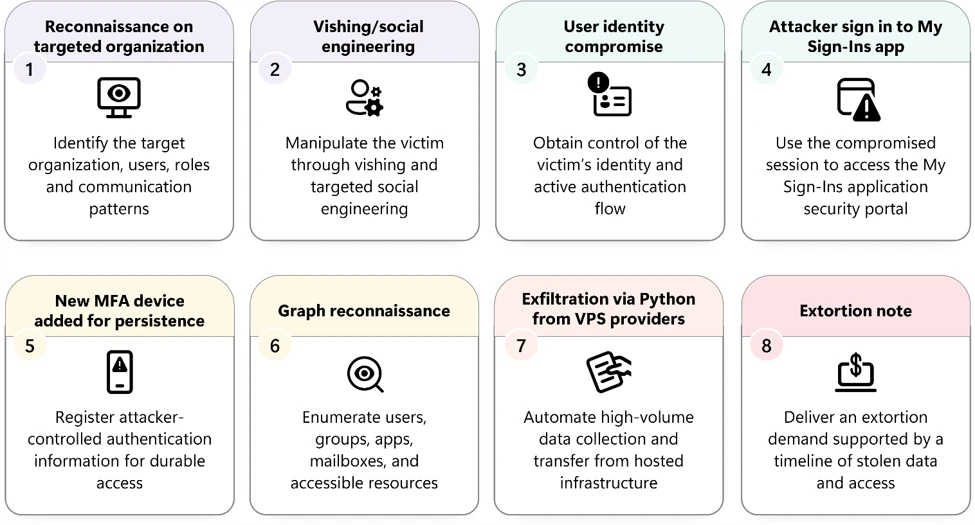
-
Arista Fixes Critical EOS Flaws Enabling Unauthenticated Code Execution
Arista Networks on 9 September 2026 published four security advisories addressing multiple critical flaws in Arista EOS and VeloCloud Edge software. The disclosures describe unauthenticated and authenticated paths to arbitrary code execution, potentially…
-
UEFI Shell Flaw Threatens Secure Boot on Millions of Devices
A vulnerability in the UEFI Shell module embedded in SPI flash memory has been disclosed that enables a Secure Boot bypass. Security researchers describe a critical flaw that could let an attacker execute unauthorised code during the early startup phase,…
-
MongoDB Patches Critical Flaw That Could Disable Authorisation
MongoDB has released patches addressing 24 server vulnerabilities across its recent releases, with six CVEs highlighted in the report. The most severe issue is CVE-2026-82067, rated 9.2 (CVSSv4), described as improper case sensitivity in configuration…
-
Okta Patches Six Flaws Enabling Access Bypass and Secret Theft
Okta has released security advisories addressing six vulnerabilities across its Auth0 AD/LDAP Connector, Okta Access Gateway, and the Hyperdrive Integration plugin. The issues, rated as 1 Critical and 5 High, were patched on 9 September 2026, with…
-
Android 17 Exploit Chain Gives Untrusted Apps Kernel Control
Researchers have disclosed the LSPromise exploit chain, which they say can take an untrusted local Android app through to full kernel control. The chain affects the initial official release of Android 17 and was successfully tested on a Pixel 10; it did not…