News
Every CyberSIXT summary, newest first, with a link to its story and to the original report.
Most articles on Wed 21 Oct (96); 9–13 on weekend days.
Show as table
| Day | Articles published |
|---|---|
| Sun 11 Oct | 9 |
| Mon 12 Oct | 56 |
| Tue 13 Oct | 85 |
| Wed 14 Oct | 86 |
| Thu 15 Oct | 78 |
| Fri 16 Oct | 61 |
| Sat 17 Oct | 10 |
| Sun 18 Oct | 10 |
| Mon 19 Oct | 60 |
| Tue 20 Oct | 86 |
| Wed 21 Oct | 96 |
| Thu 22 Oct | 84 |
| Fri 23 Oct | 68 |
| Sat 24 Oct | 13 |
| Today, Sun 25 Oct | 9 so far |
Mon 19 Oct· 1 article
-
Actively Exploited Flaws Hit Cisco, BeyondTrust and WordPress Plugin
Between 12 and 18 October 2026, CVE Watchtower logged 5,499 new vulnerabilities, with this weekly review tracking 12 exploited flaws. Six of those were flagged by Daily Cybersecurity’s intelligence sources, and three of the exploited flaws are not yet…
Fri 16 Oct· 1 article
-
China-linked hackers exploited BeyondTrust zero-day to steal credentials
Ivanti, Cisco, and Palo Alto Networks all had vulnerabilities in edge devices come under fire this week. Now BeyondTrust joins the group.
Thu 15 Oct· 4 articles
-
CISA Flags Exploited Firewall, Email Gateway and Backup Software Flaws
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has added four newly observed vulnerabilities to its Known Exploited Vulnerabilities (KEV) catalog. The list comprises CVE-2026-0322 (Palo Alto Networks PAN-OS code injection), CVE-2026-76519…

-
Cisco and Palo Alto Patch Exploited Flaws Enabling Root Access
Cisco and Palo Alto Networks have issued patches for two actively exploited zero-day vulnerabilities that can enable root-level code execution on security appliances. The flaws, CVE-2026-76519 and CVE-2026-0322, have been added to the US CISA Known Exploited…
-
Cisco Fixes Actively Exploited Secure Email Gateway Flaw Allowing Root Access
Cisco has disclosed a critical flaw in its Secure Email Gateway that threat actors have been actively exploiting, tracked as CVE-2026-76519 with a CVSS of 9.8. The vulnerability resides in the Advanced Malware Protection (AMP) feature and stems from improper…
-
Attackers Exploit Critical Cisco Email Gateway Flaw to Gain Root Access
Cisco has disclosed that attackers are actively exploiting a critical vulnerability in its Secure Email Gateway (SEG), tracked as CVE-2026-76519 with a CVSS of 9.8/10. The flaw affects the AMP (Advanced Malware Protection) component and arises when…
Wed 14 Oct· 3 articles
-
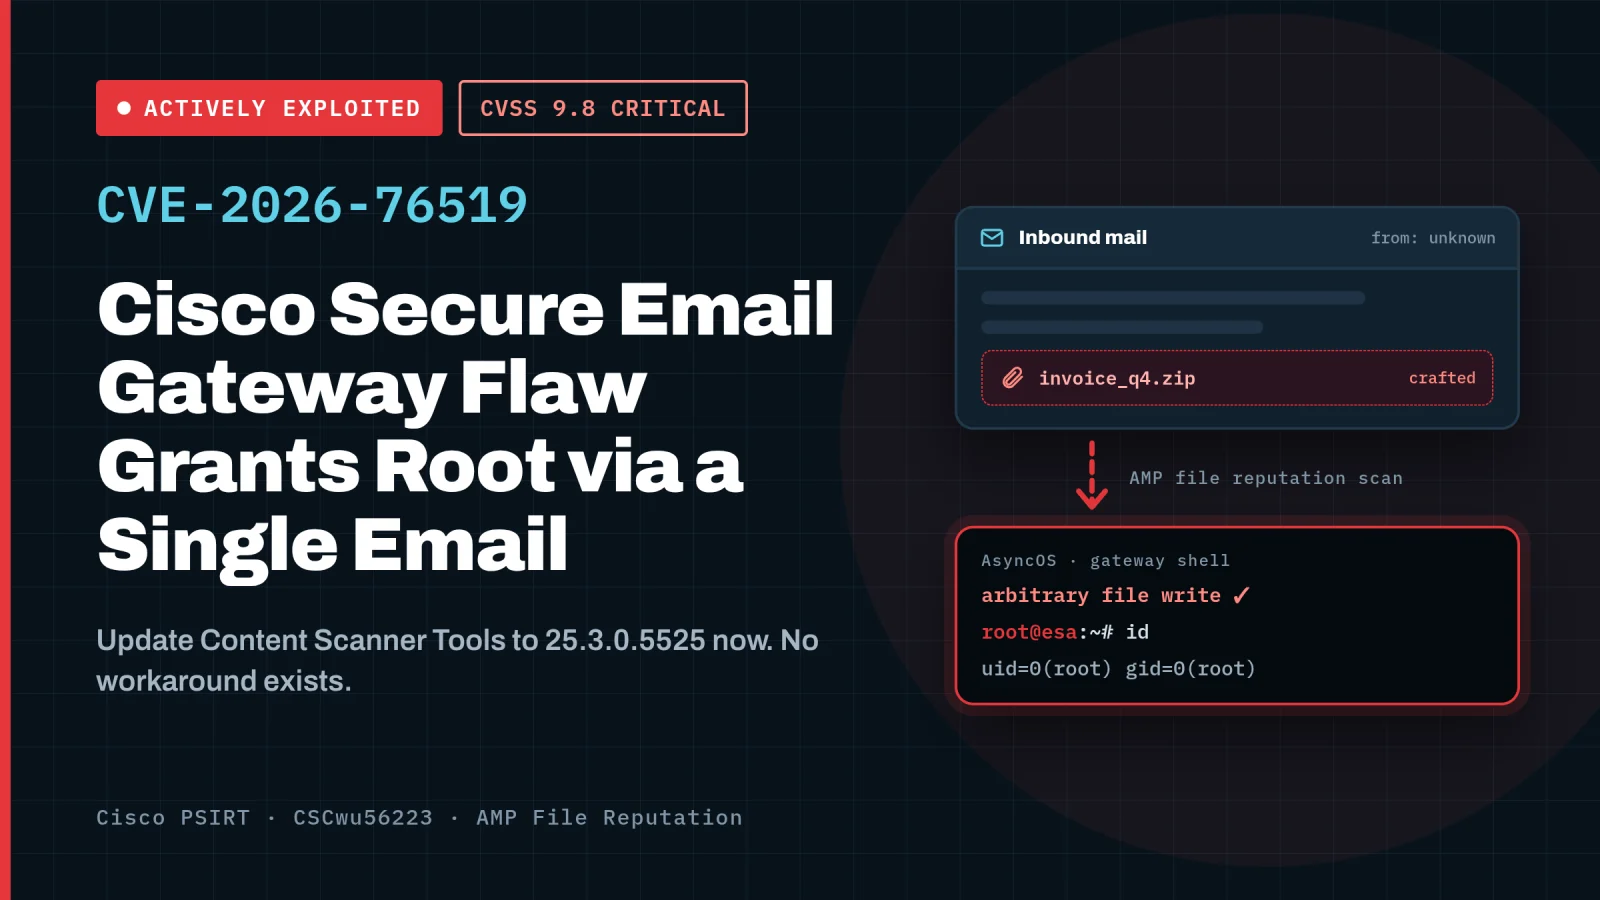
Cisco Email Gateways Face Active Attacks That Could Expose Cluster SSH Keys
Cisco’s Secure Email Gateway is being exploited in the wild for CVE-2026-76519, a critical arbitrary file write vulnerability rated CVSS 3.1 v3.1 9.8. The flaw lies in the AMP File Reputation feature, specifically in how the file reputation service handles…
-
CISA Flags Exploited Cisco Email Gateway Flaw With Critical Score
CISA added CVE-2026-76519 to its Known Exploited Vulnerabilities (KEV) catalogue on 14 October 2026. The Cisco Secure Email Gateway Relative Path Traversal Vulnerability affects Cisco Secure Email Gateway and could let an unauthenticated remote attacker…
-
Cisco Email Gateway Flaw Exploited to Run Commands as Root
Cisco has warned that active attacks are exploiting a critical vulnerability in its Secure Email Gateway. The flaw, tracked as CVE-2026-76519 (CVSS 9.8), can allow a sender with no login to write files to the appliance’s operating system and, if successful,…
No older articles match these filters.