THE content discusses a critical vulnerability (CVE-2026-8461) in FFmpeg's MagicYUV decoder that allows for heap out-of-bounds write, posing a high risk (CVSS score 8.8). This flaw can enable attackers to execute arbitrary code through specially crafted video files, leading to potential server compromises without user interaction. Affected versions are those prior to 8.1.2, which has a patch available. Administrators are urged to upgrade immediately or disable the decoder as mitigation. The vulnerability impacts numerous applications, including Jellyfin and Nextcloud, emphasizing its widespread risk.
FFmpeg MagicYUV flaw lets hackers run code via crafted files
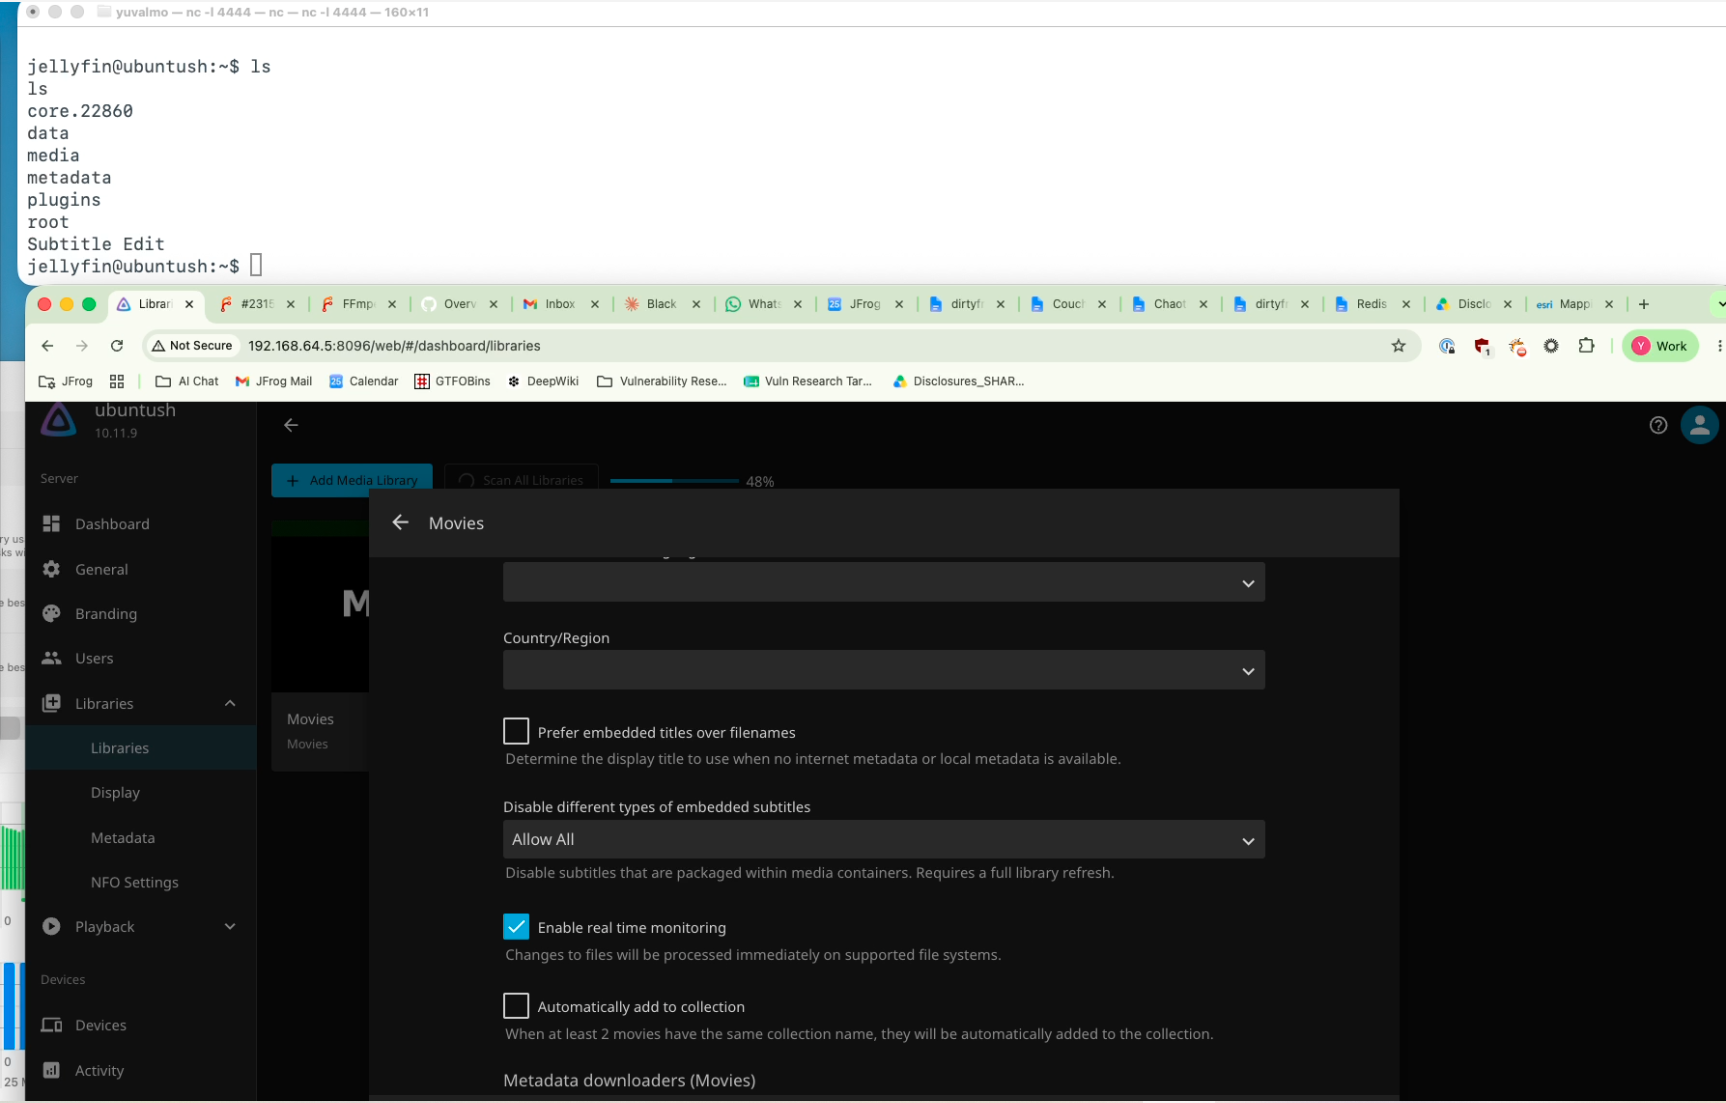
CyberSIXT Evidence Panel
Article by CyberSIXT