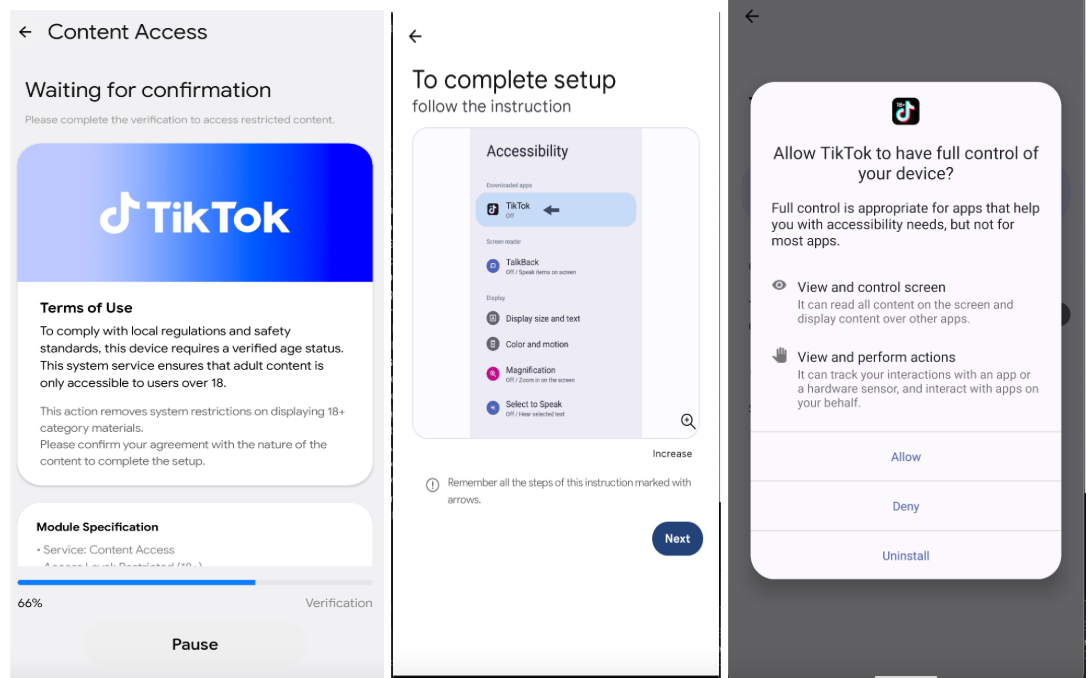
THE Rokarolla Android banking trojan is a malware that executes complete device takeovers, targeting 217 cryptocurrency and banking applications. It is spread through malicious websites impersonating legitimate apps, tricking users into installing a dropper application that delivers the trojan. After gaining Accessibility Services access, it conceals its icon, connects to a remote server, and downloads fake HTML phishing pages for banking apps to capture user credentials.
The malware employs tactics like disabling Google Play Protect, sending SMS messages impersonating the victim, and bypassing two-factor authentication. Users are advised to avoid unofficial app downloads and scrutinize app permissions to protect against this threat.