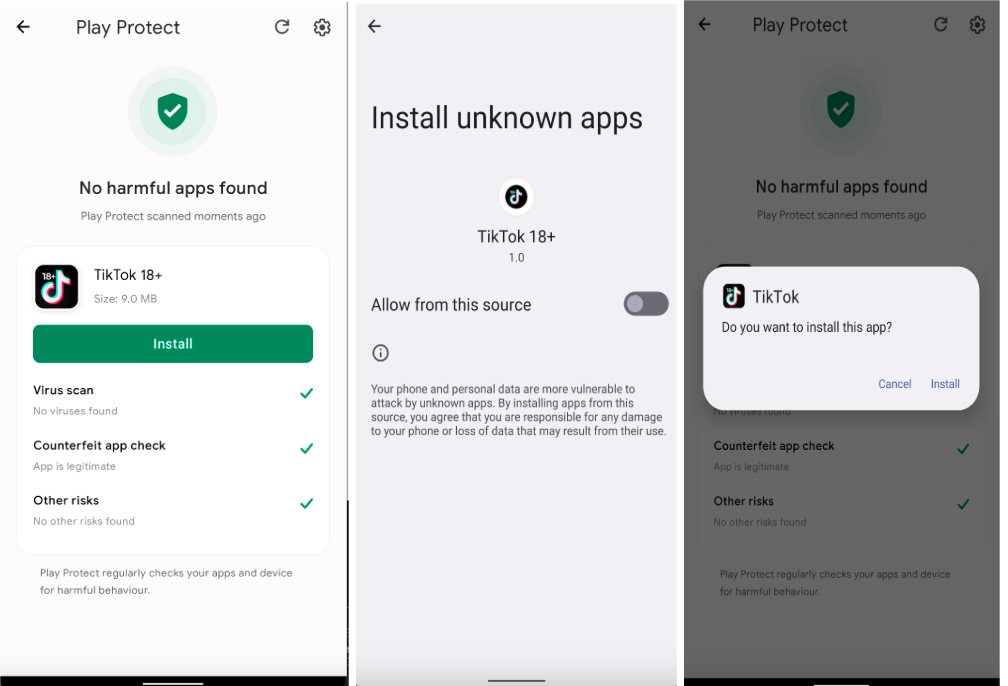
THE article discusses the Rokarolla Android Trojan, which targets 217 banking and crypto applications, stealing user credentials and interfering with device functionality. This malware spreads through malicious sites disguised as popular apps like TikTok and Google Chrome, using a dropper that masquerades as Google Play Protect to gain access. Once installed, it can simulate user taps, display fraudulent overlays to capture sensitive information, and intercept SMS messages.
Rokarolla can block incoming calls, mute device sounds, and silently rewrite clipboard data, making it highly evasive and persistent. Researchers from Zimperium advise against granting accessibility access to unknown apps and stress the importance of downloading apps only from trusted sources.