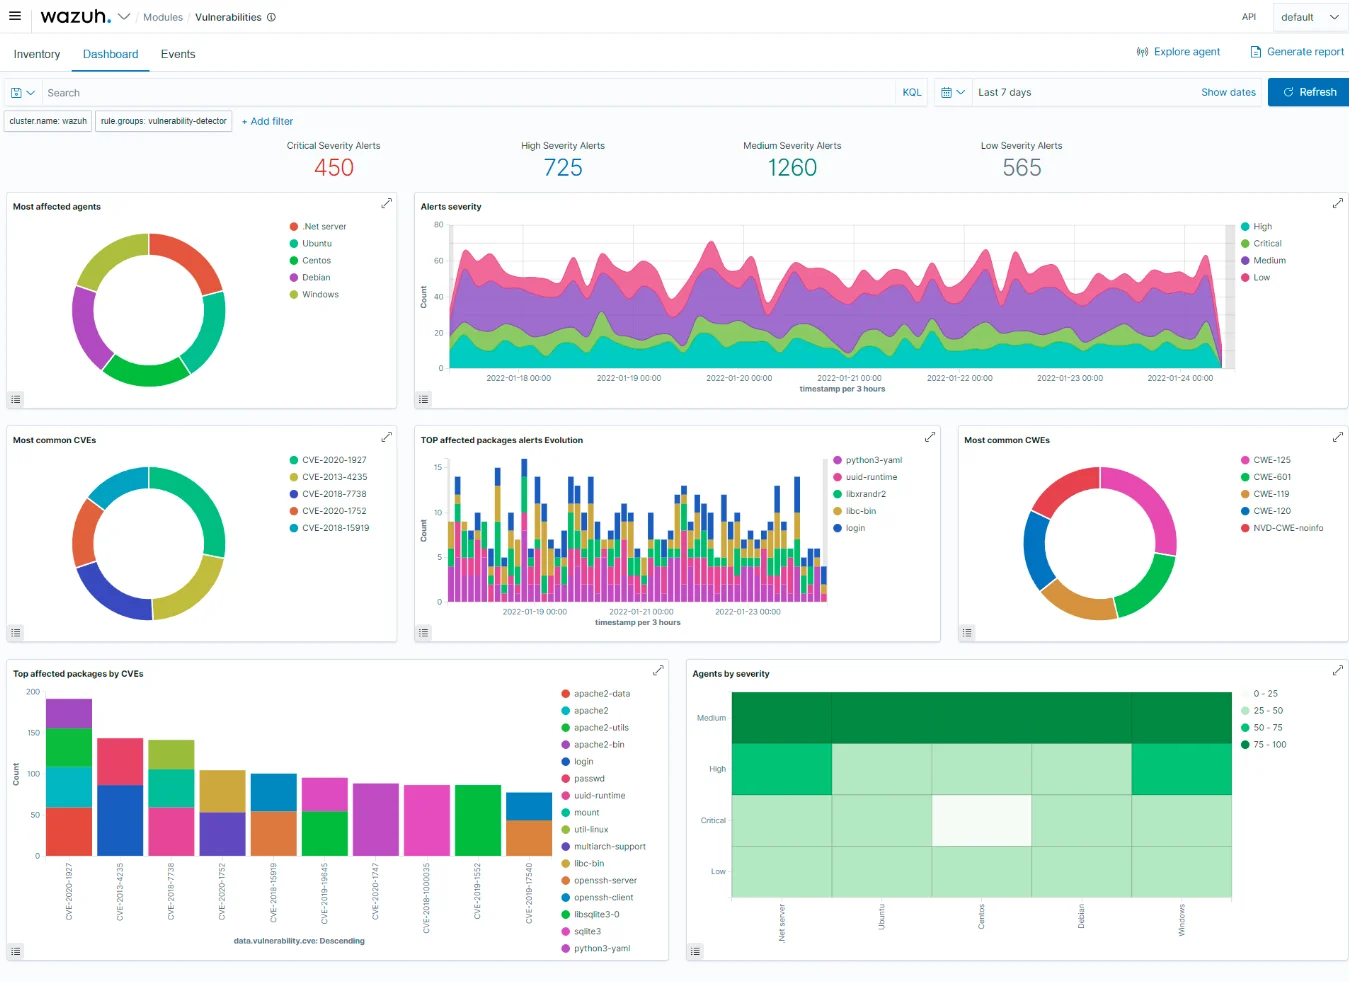
WAZUH has released version 4.14.8 to fix a set of 15 security vulnerabilities in the open‑source SIEM and XDR platform. The article notes that two of these flaws are high‑severity, with CVSS scores around 9.4, and can lead to remote code execution as root. It also states that several other vulnerabilities could allow an attacker who compromises one component to take control of other parts of a Wazuh deployment. The piece emphasises the potential impact on both the SIEM managers and the connected agents.
Details in the article are limited due to premium content restrictions, but the publicly visible material confirms that the fixes cover multiple issues across the Wazuh stack and underline the risk of full compromisation if exploited. It calls for applying the 4.14.8 update to mitigate the risks and to monitor deployments for indicators of compromise consistent with a broad, multi‑component compromise scenario.
The article also includes a list of related CVEs and security coverage, including CVE tags such as CVE-2026-74034, CVE-2026-74040 and CVE-2026-74041, though it does not provide the specific exploit details or mitigations for each CVE within the accessible portion.
For organisations relying on Wazuh, the practical response is to upgrade to 4.14.8 promptly and review access controls and monitoring across both managers and agents to detect any signs of unusual activity that might indicate exploitation of the affected components.