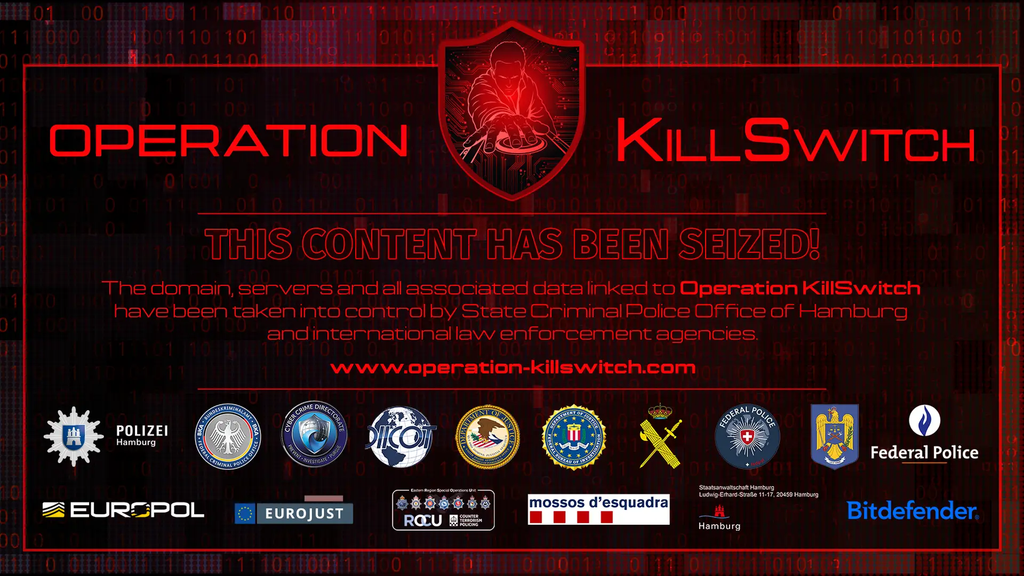
EUROPOL says the KillSec ransomware group has been dismantled as part of Operation KillSwitch, with law enforcement seizing control of the group’s dark web leak site and more than 110 terabytes of stolen data. The action, led by German authorities and supported by Europol and Eurojust, involved eight property searches across Spain, Greece, Romania and the United Kingdom and resulted in three provisional arrests.
Investigators are reviewing evidence seized from several servers and seized domains as they pursue up to around 1,000 suspected attacks linked to KillSec.
Europol’s release notes that KillSec infiltrated organisations by exploiting software flaws and weak access controls, frequently targeting cloud storage to steal data and then publish victims on the group’s leak site unless payment was made. About 500 of the suspected attacks have been identified as successful so far, though investigators caution that the figure may change as they analyse the seized evidence.
The takedown also disrupted the group’s operational infrastructure by bringing five central servers under police control and redirecting visitors to a law enforcement notice.
A noteworthy detail from the case is the claimed use of AI to build and maintain KillSec’s ransomware operations and to aid target selection. Authorities say the main operator is believed to be 16 years old, with another suspect who turned 18 in August 2026 and who was under 18 at the time of some alleged crimes. The investigation is ongoing, with ten countries involved and continued scrutiny of financial trails and additional victims.