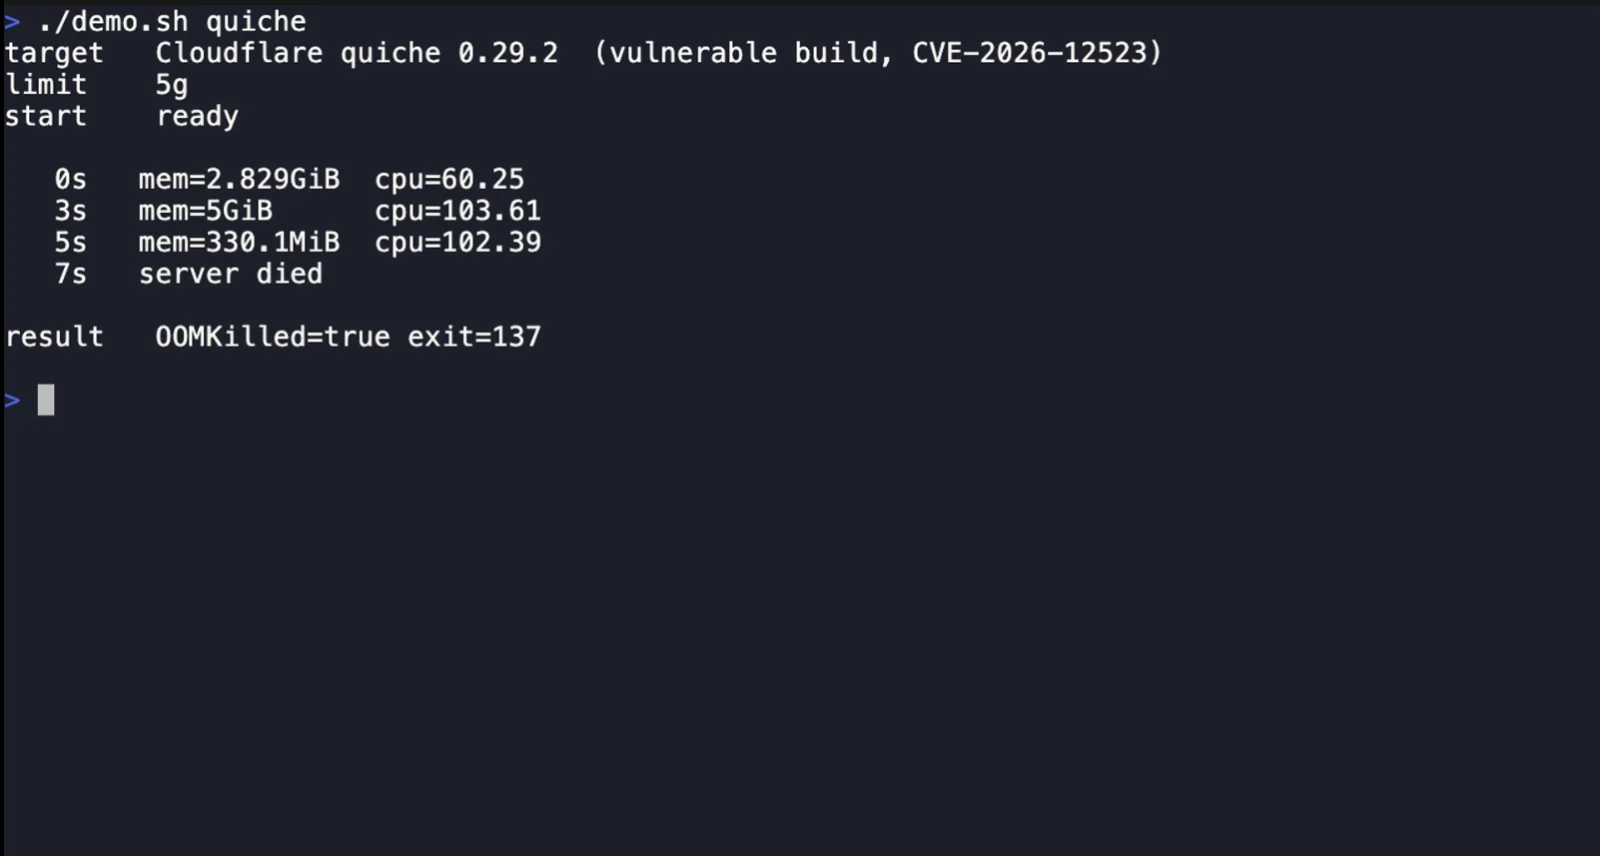
ON 20 October 2026, security researchers FoxIO published details and proof-of-concept code for “Header Accordions”, a denial-of-service attack targeting HTTP/3 implementations that use QPACK to compress headers. FoxIO found that a small request can make some servers allocate far more memory than the data sent: in Bun, amplification reached about 4,000 to 1. The researchers said seven of ten tested implementations were vulnerable. They reported no confirmed attacks in the wild, but warned that public exploit code makes the technique easier to test and use.
The attack exploits weak or missing checks on the size of headers after QPACK has expanded them. Some implementations limit only the compressed data; others fail to apply the required 32-byte overhead per header field or allocate memory before checking the limit. FoxIO identified issues affecting quic-go, Cloudflare quiche, lsquic, Bun, aioquic, mitmproxy, the h3 crate and Wireshark.
The article lists CVE-2025-64702, CVE-2026-12523 and CVE-2025-13945; it says CVE-2025-64702 has no fix listed, while the other two are fixed in quiche 0.29.3 and Wireshark 4.6.2 or 4.4.12. It also reports fixes for quic-go 0.57.0 and lsquic 4.9.0. Bun 1.4.3, h3, aioquic and mitmproxy are listed as still unpatched. FoxIO recommends keeping HTTP/3 disabled on Bun servers until a fix is available, disabling it in mitmproxy with `http3=false`, and setting a reasonable `max_field_section_size` for h3.