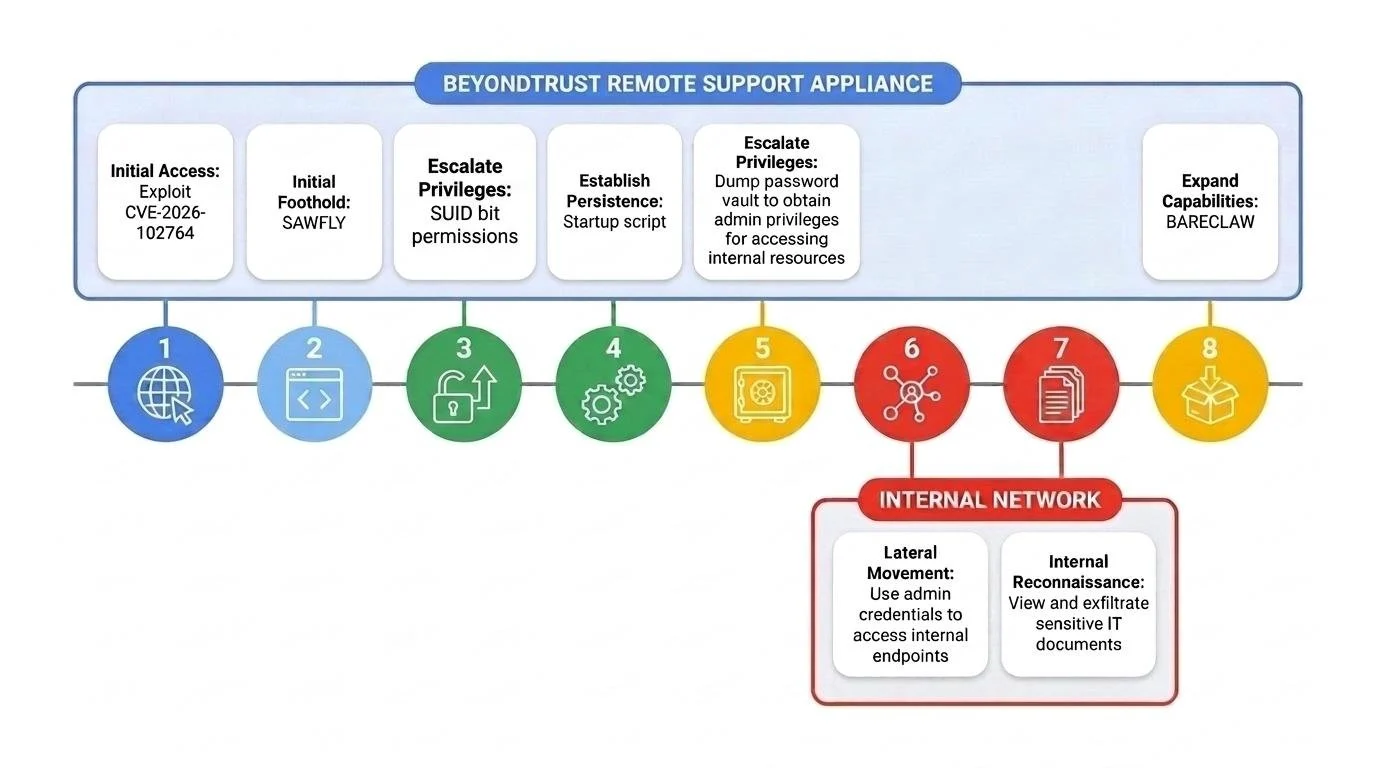
BEYONDTRUST disclosed a critical remote-access vulnerability in its BeyondTrust Remote Support product, tracked as CVE-2026-102764, with a CVSS of 9.3. The flaw allows unauthenticated remote attackers to bypass origin validation in internal messaging components, enabling arbitrary file operations and the upload of malicious files to the appliance.
The issue was observed being exploited in the wild by a threat group identified as ARMORY CASTLE (formerly UNC5221) from late August 2026, according to Mandiant and Google Threat Intelligence Group (GTIG). Evidence points to a zero‑day used to deploy custom malware and harvest credentials, with attackers achieving root access via a webshell and then escalating privileges to access all stored credentials and system files.
Affected versions include all supported BeyondTrust Remote Support releases up to and including 26.2.3. BeyondTrust issued a patch for SaaS tenants on 9 October 2026 (BT26-05) and advised self‑hosted customers on version 24.3.1 or later to apply BT26-05-RS via the appliance interface; those on older versions should upgrade to a supported release before patching.
Practical responses include capturing memory and disk snapshots, blocking perimeter traffic, redeploying from clean images, terminating active sessions, and rotating all credentials while exporting syslog data to an external SIEM. The GTIG note cautions that organisations reachable on the vulnerable version during the exploitation window should treat appliances as potentially compromised until reviewed.