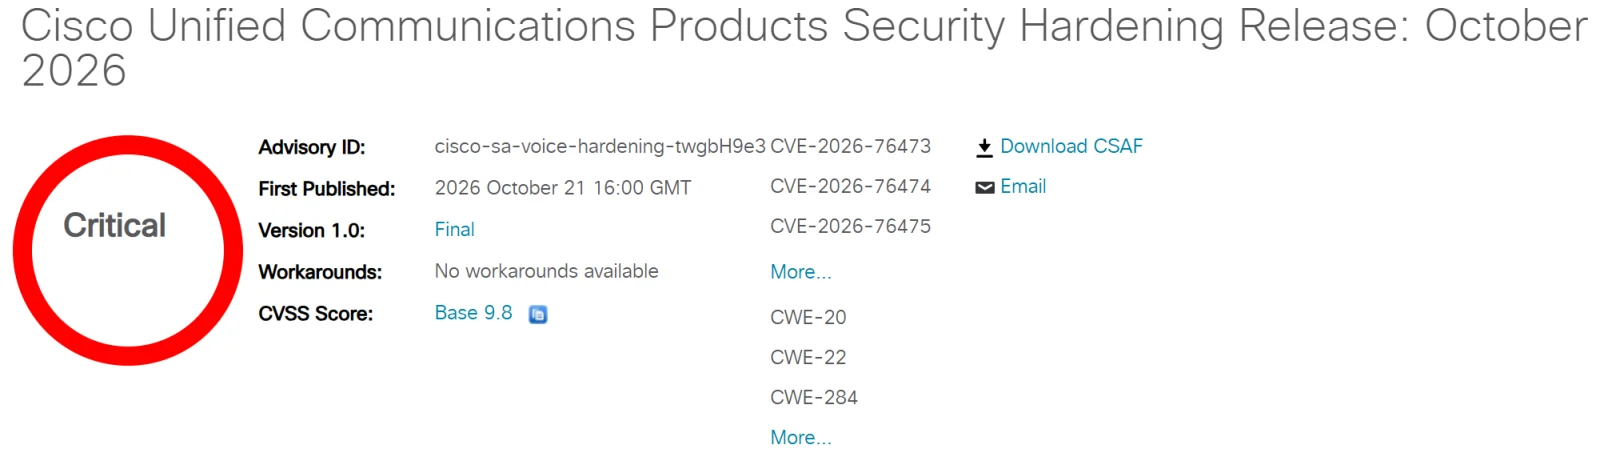
CISCO has released a security hardening update for Unified CM and related voice products, after internal testing uncovered a set of bugs that were grouped into nine CVEs. The advisories issued on 21 October 2026 flag three critical vulnerabilities (all CVSS v3 scores of 9.8) and several high and medium issues, with the highest seen in CVE-2026-76473 and CVE-2026-76474.
Cisco notes these flaws affect Unified CM, Unified CM IM&P, Unified CM SME, Unity Connection, Emergency Responder and Prime Collaboration Deployment, and that the vulnerabilities arise from weaknesses such as improper resource lifetime management, improper authentication, cross-site scripting, and various input validation and access-control problems.
Eight of the bugs were addressed within a single security hardening release, with the advisory explaining that the CVE scores capture the maximum potential severity of the most impactful underlying issue in each group.
In practice, Cisco states there is no workaround and that upgrading is the fix. Affected versions include releases 14 and 15, regardless of device configuration. Customers running release 15 should upgrade to 15SU5, while those on release 14 must migrate to a fixed release.
Separately, CVE-2026-76487 introduces an access-control bypass allowing an unauthenticated attacker to send crafted HTTP requests to access parts of the network beyond the intended scope; Cisco cautions this could expose additional network segments. As of the advisories, Cisco PSIRT is not aware of any public exploitation or malicious use. Administrators are urged to apply the updates promptly and monitor for follow-up advisories.