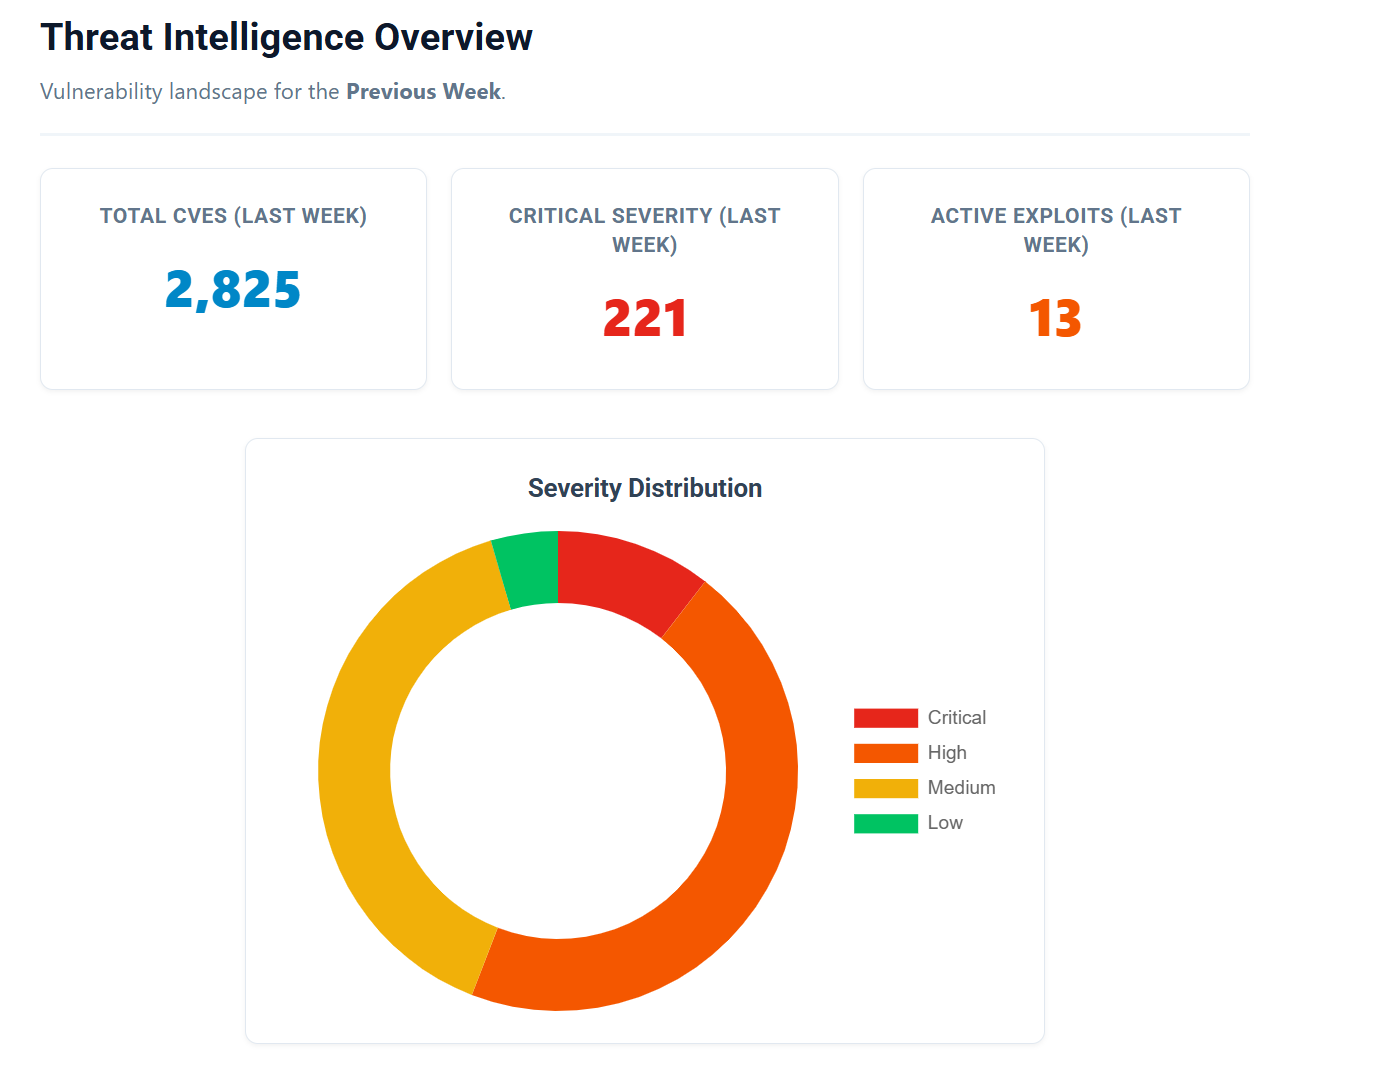
CVE WATCHTOWER recorded 2,825 new vulnerabilities between 21 and 27 September 2026, including 221 rated Critical and 218 scoring CVSS 9.0 or higher. Daily Cybersecurity identified nine flaws being exploited, eight of which were also added to CISA’s Known Exploited Vulnerabilities (KEV) catalogue. Four additional vulnerabilities appeared in KEV but not in Daily Cybersecurity’s list.
Most shared entries were recorded by both sources on the same day; Daily Cybersecurity identified the WordPress flaw, CVE-2026-87902, three days before CISA, while the exploited Roundcube issue, CVE-2026-48842, had not yet been added to KEV. The report notes that the two feeds measure different events, so the timing comparison is not a benchmark.
Several attacks targeted internet-facing edge products. CVE-2026-87902, a CVSS 9.2 WordPress Core path-traversal flaw, allows unauthenticated local PHP file inclusion under specific theme-folder conditions; Previdian recorded 68 attempts by 23 September. F5 confirmed exploitation of the CVSS 9.8 BIG-IP APM OAuth remote-code-execution zero-day, CVE-2026-94127. Check Point reported attacks against CVE-2026-85102, a VPN certificate flaw, from 12 September, while CVE-2026-93616 saw a handful of targeted attacks. Citrix confirmed exploitation of the CVSS 9.5 NetScaler flaws CVE-2026-88771 and CVE-2026-88772 on 27 September.
The report recommends prioritising patches for exposed NetScaler, F5 BIG-IP APM and Check Point systems, followed by WordPress, VeloCloud Orchestrator, SharePoint and Roundcube. NetScaler should be updated to 14.1-73.37 or 13.1-64.23, while Roundcube fixes are versions 1.6.16 and 1.7.1. Administrators are also urged to address the KEV-only flaws affecting Zyxel, WSO2, Adobe Commerce/Magento and MikroTik, and to investigate systems for compromise where exploitation occurred before patches were available.